
CVE-2026-67279
 hackspeak/cve-2026-67279
Python proof-of-concept scripts for the MikroTrick MikroTik RouterOS SSH takeover chain (CVE-2026-67279, CVE-2026-86060, CVE-2026-67276) for…
authenticationembedded-systems-securityexploitation+7
3
hackspeak/cve-2026-67279Python proof-of-concept scripts for the MikroTrick MikroTik RouterOS SSH takeover chain (CVE-2026-67279, CVE-2026-86060, CVE-2026-67276) for…
 poxsky/cve-2026-38577
Proof-of-concept demonstrating hardcoded root credentials (admin/system) in Tenda HG21 XPON modem firmware, enabling unauthorized root access via…
 amiraliuks/ip-camera-research
Security research on a consumer IP camera built on the Fullhan FH8626V100 SoC (model AJL30PG0803).
 mr-destroyer/cve-2025-55182
Exploit for CVE-2025-55182 enabling remote code execution via prototype pollution in Next.js React Server Components, with command execution and…
 darkflippers/unleashed-firmware
Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.
 ghostesp-revival/ghostesp
The open-source wireless research platform for ESP32.
 marginresearch/foisted
MikroTik remote jailbreak for v6.x.x
 jimilinuxguy/lrs-pager-systems-bruteforce
Long Range Pager Systems pagers and coasters URH and YS1 (yardstick one / cc11xx) information and brute force tool
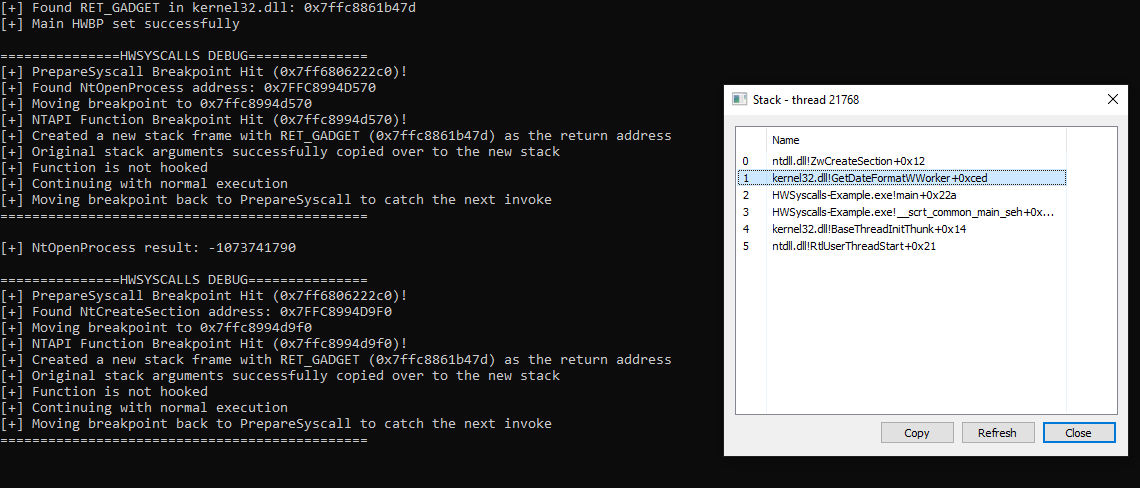 dec0ne/hwsyscalls
HWSyscalls is a new method to execute indirect syscalls using HWBP, HalosGate and a synthetic trampoline on kernel32 with HWBP.
 alteredsecurity/disable-tamperprotection
A POC to disable TamperProtection and other Defender / MDE components
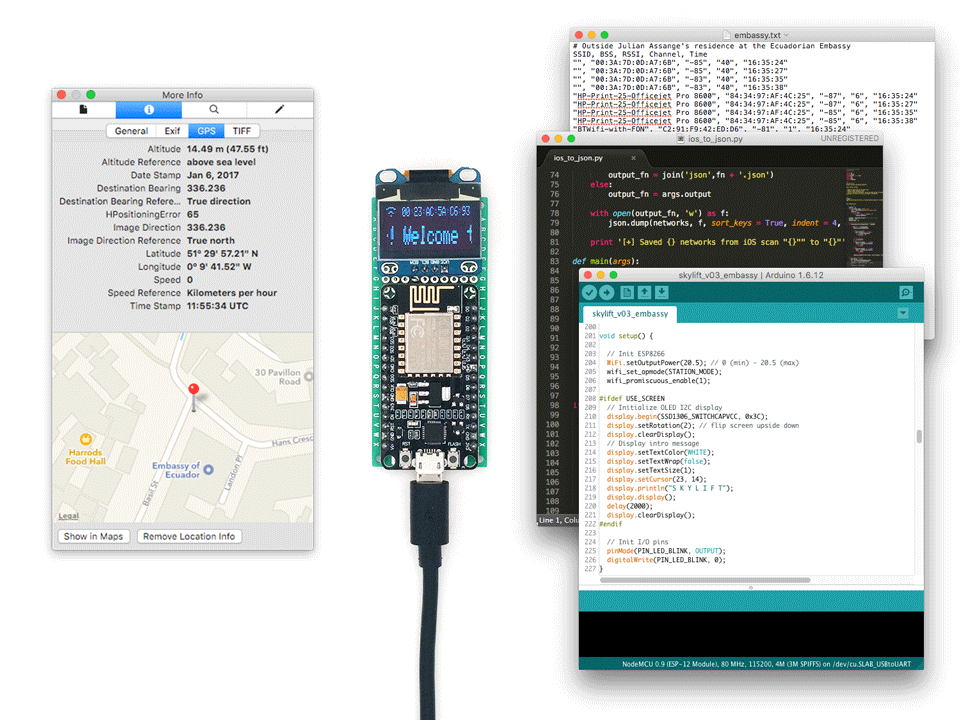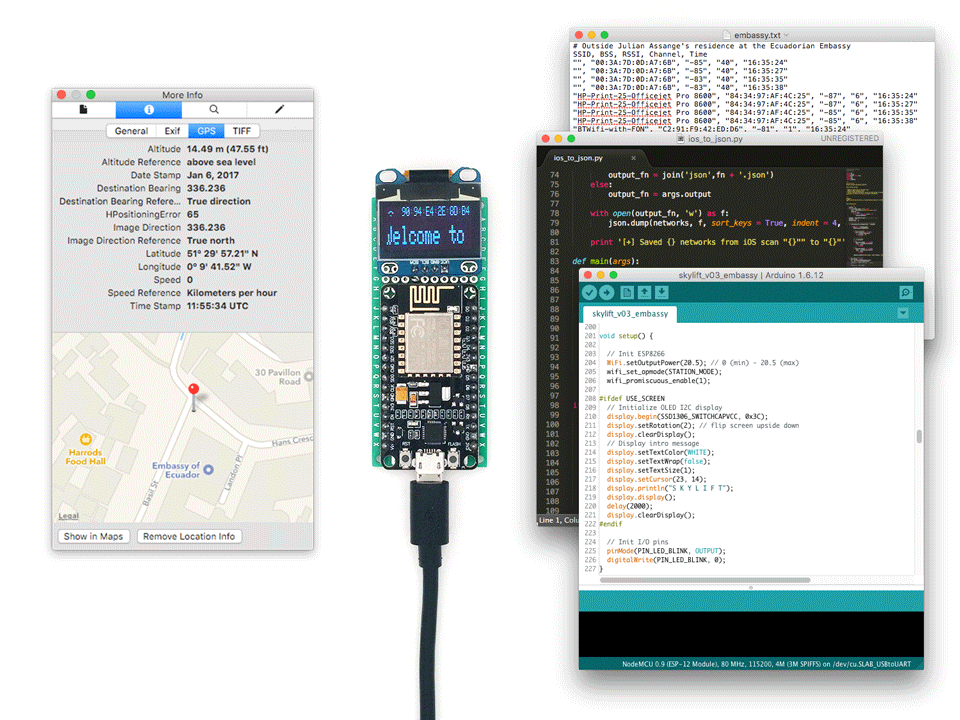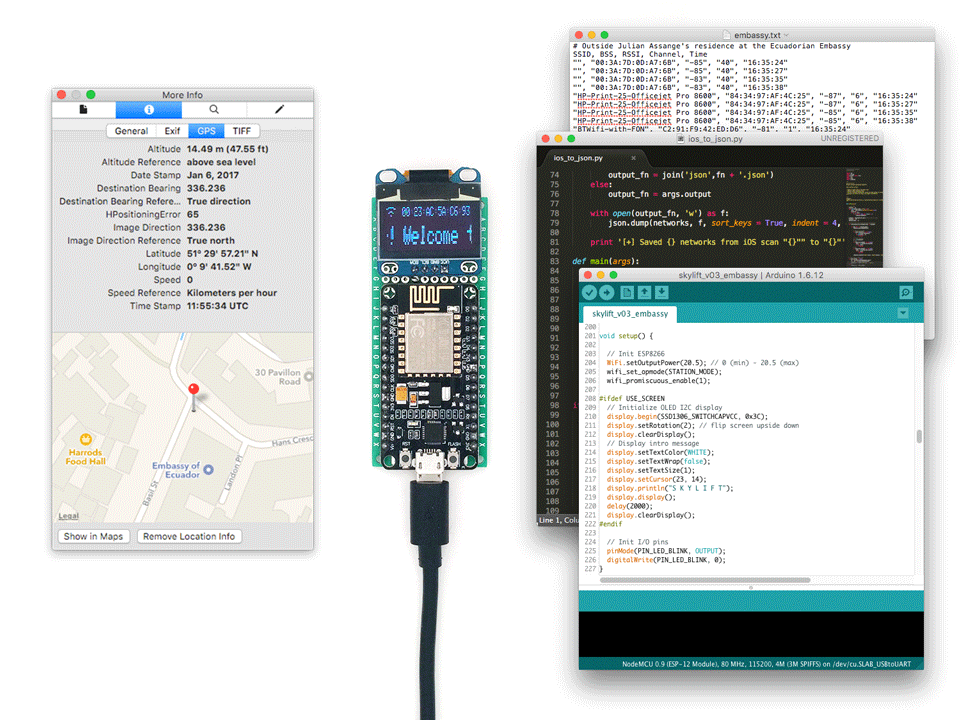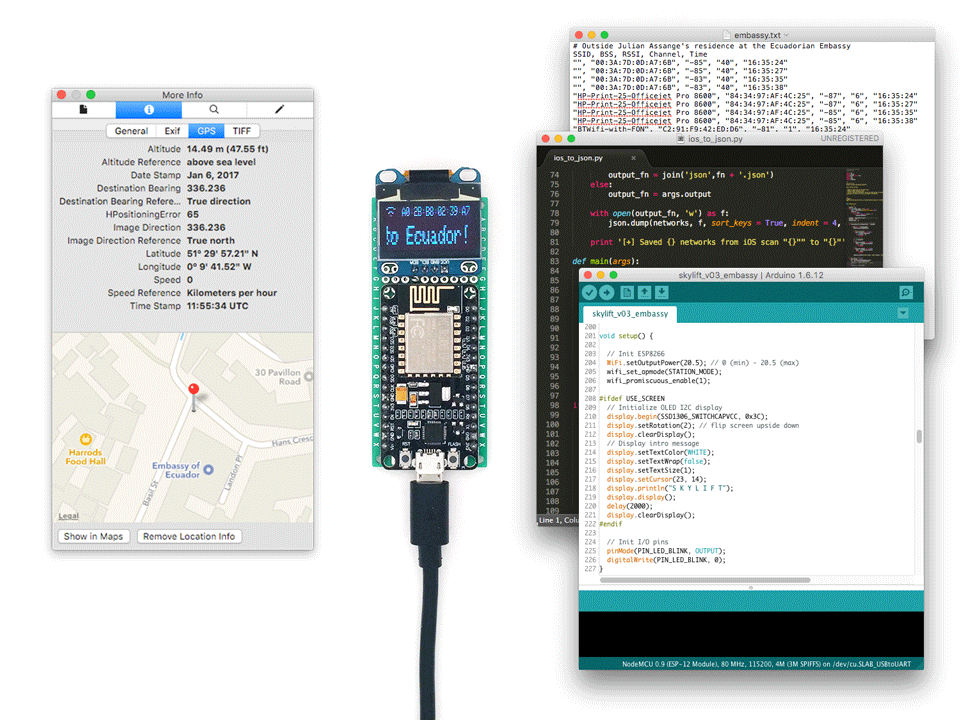 awesome-pentest-gadgets/skylift
WiFi Geolocation Spoofing with the ESP8266
 adamhrv/skylift
Wi-Fi Geolocation Spoofing with ESP8266 / ESP32
 xairy/lights-out
Tools for controlling webcam LED on ThinkPad X230
 lixmk/concierge
Concierge Toolkit: Physical Access Control Identification and Exploitation
 samyk/keysweeper
KeySweeper is a stealthy Arduino-based device, camouflaged as a functioning USB wall charger, that wirelessly and passively sniffs, decrypts, logs…
 elvanderb/tcp-32764
some codes and notes about the backdoor listening on TCP-32764 in linksys WAG200G.
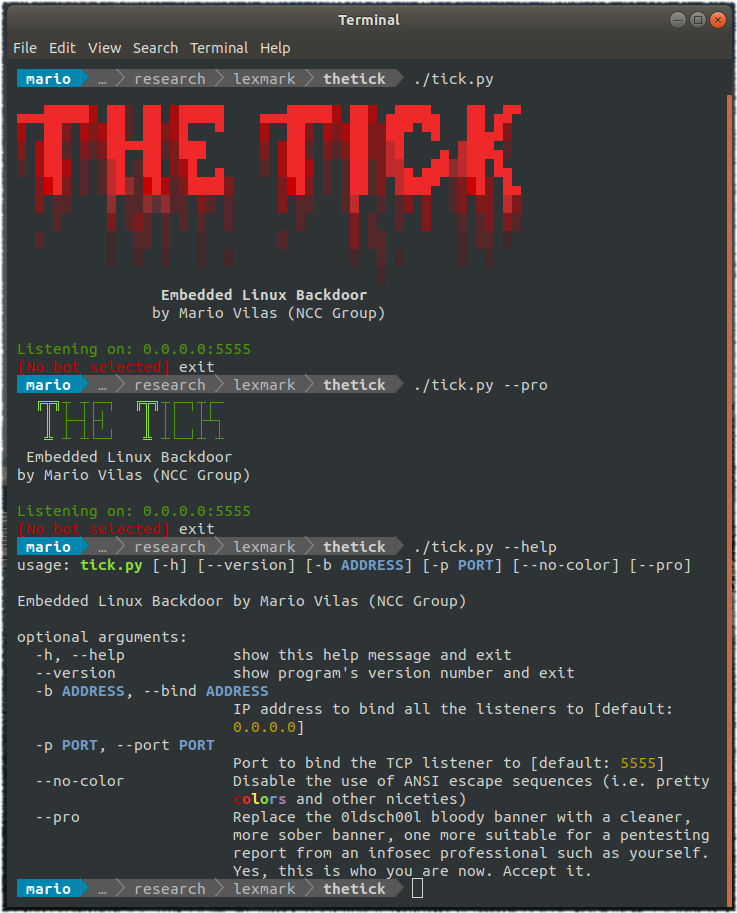 nccgroup/thetick
A simple embedded Linux backdoor.
 spiralbl0ck/bios-stuff-related-programming
Final OBJECTIVE:BIOS ROOTKIT AND RSHELL USING BIOS NETWORKING STACK