
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
25 results
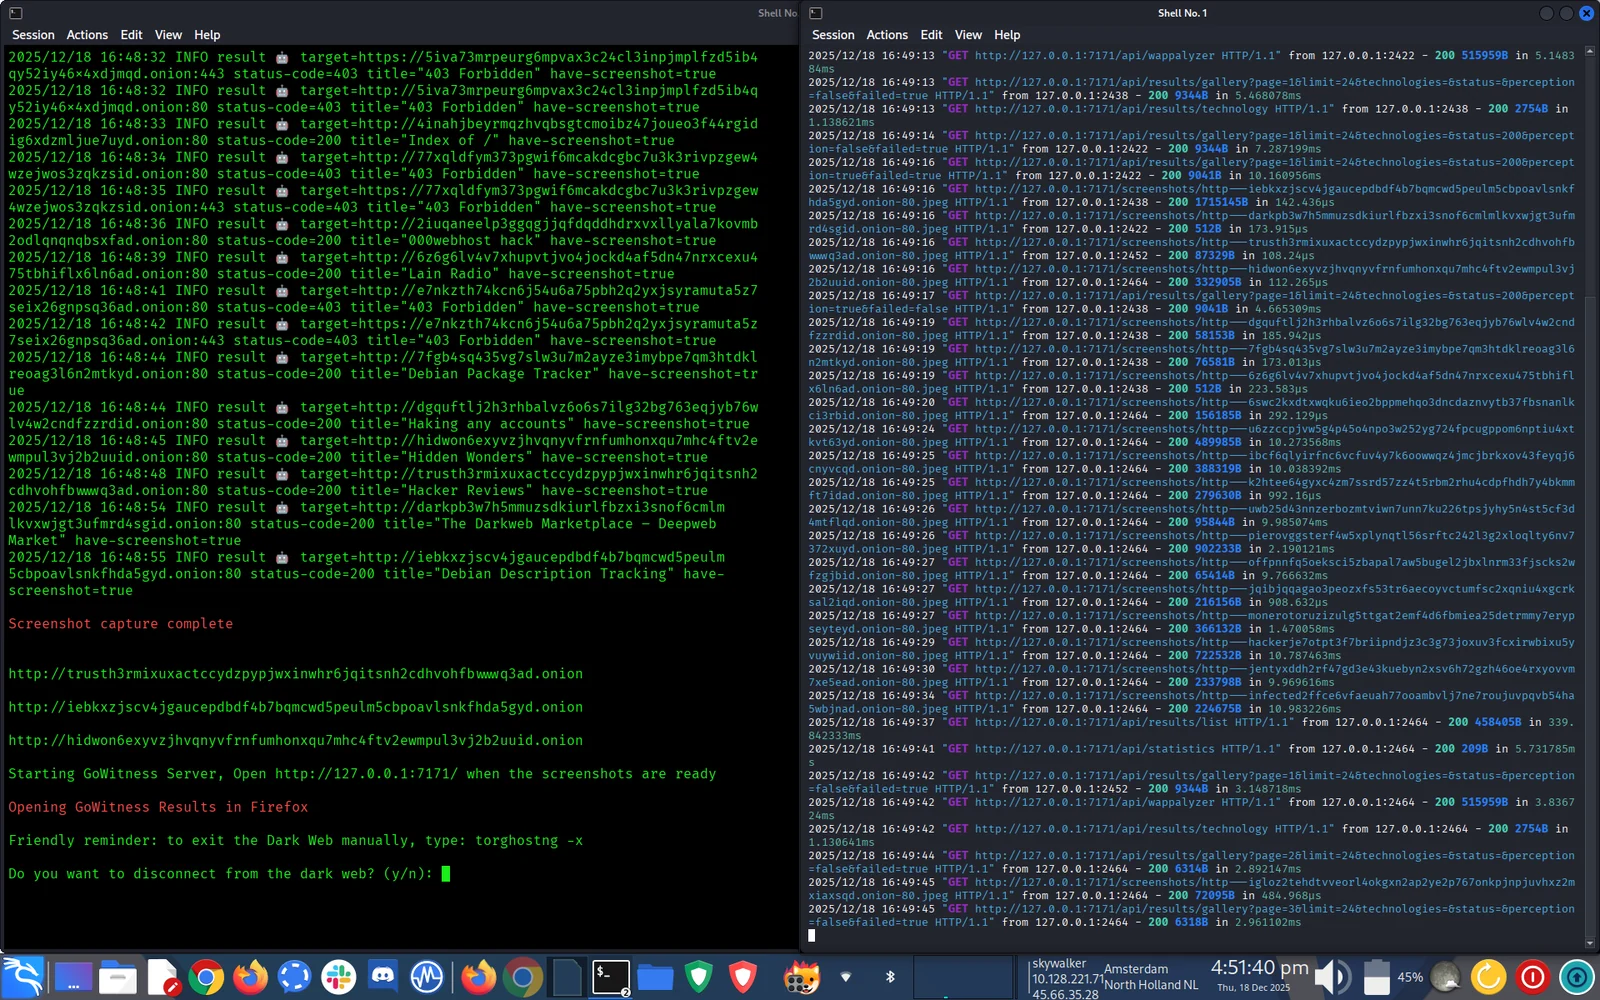
darkfox preview

darkfox

GitHubaryanguenthner/darkfox

CTI Cyber Threat Intelligence OSINT Dark Web Deep Web Research. Ransomware gang information gathering tool.
crawlerforensicsinformation-gathering+6
190
1 month ago
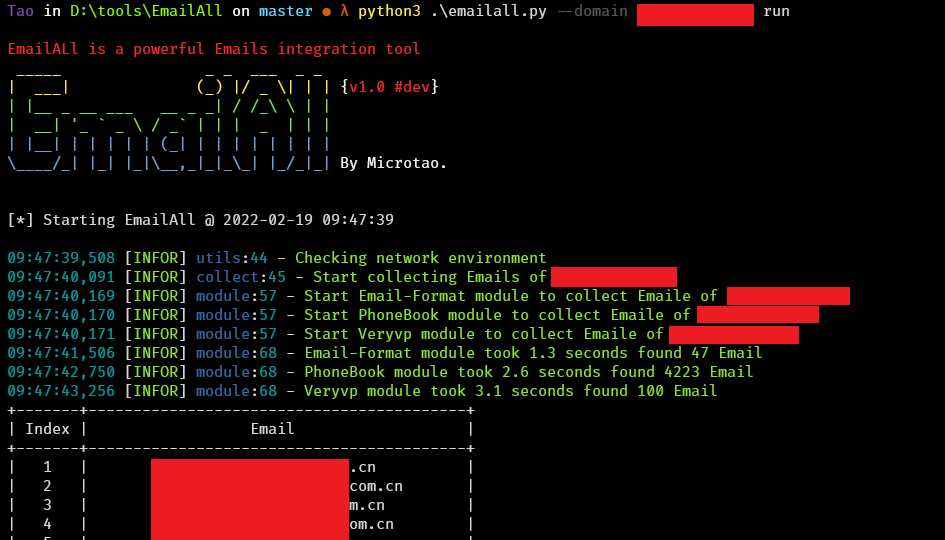
EmailAll preview

EmailAll

GitHubtaonn/emailall

Collects email addresses for a target domain by querying search engines, GitHub API, PhoneBook, Snov, Skymem and other OSINT sources, saving results…

crawleremail-harvestinginformation-gathering+4
7544 years ago
DeadMatter preview

DeadMatter

GitHubqsecure-labs/deadmatter

Offset Independent Credential Extraction Tool
data-recoverydigital-forensicsforensics+7
721 year ago
HiddenDesktop preview

HiddenDesktop

GitHubmalwaretech/hiddendesktop

Create and enumerate hidden desktops.
defensive-toolsforensicsincident-response+3
942 years ago
Credential-Hunting preview

Credential-Hunting

GitHubnecr00/credential-hunting

CredsHunter - Credential Hunting scripts for Windows and Linux OS
forensicsincident-responseinformation-gathering+7
1902 months ago
LogHound preview

LogHound

GitHubrnb-team/loghound

Post-Exploitation EVTX Analyzer for BloodHound Mapping
authenticationdigital-forensicsforensics+6
155 months ago
copyfail-rs preview

copyfail-rs

GitHubliverwortenuresis371/copyfail-rs

Exploit and detect CVE-2026-31431 vulnerabilities using a static binary that monitors system integrity and bypasses PAM authentication.

authenticationbinary-exploitationexploitation+7
16 days ago
sherlock preview

sherlock

GitHubsherlock-project/sherlock

Hunt down social media accounts by username across social networks

digital-forensicsemail-harvestingforensics+11
95.3k1 month ago
OffsetInspect preview

OffsetInspect

GitHubwarpedatom/offsetinspect

PowerShell toolkit for AMSI/Defender detection-boundary analysis and static malware triage maps byte offsets to detection triggers, plus YARA,…
binary-analysisdefensive-toolsexploitation+8
853 months ago
syd preview

syd

GitHubsydsec/syd

Offline AI Security Assistant for Air-Gapped Pentesting
ai-securityexploitationforensics+8
876 months ago
tricorne preview

tricorne

GitHubcrussella0129/tricorne

a Fedora remix focused on pentesting and purple hat tooling
defensive-toolsexploitationforensics+8
55 months ago
ShadowNet preview

ShadowNet

GitHubantisurveillanceagency/shadownet

ShadowNet is an anonymous routing protocol that forces all connections (system-wide) to go through Tor while implementing Mixnet-like…

anti-botdigital-forensicsforensics+9
161 month ago
VMkatz preview

VMkatz

GitHubnikaiw/vmkatz

Extract Windows credentials directly from VM memory snapshots and virtual disks
digital-forensicsexploitationforensics+7
1.6k3 days ago
USB Spy preview

USB Spy

GitLabchristophe.duvernois/usb-spy

Intercepts and analyzes USB Mass Storage traffic at the block and file level, emulates USB devices, and supports custom Python stubs for security…
digital-forensicsexploitationfirmware-analysis+6
33 months ago
Remote-Desktop-Caching- preview

Remote-Desktop-Caching-

GitHubviralmaniar/remote-desktop-caching-

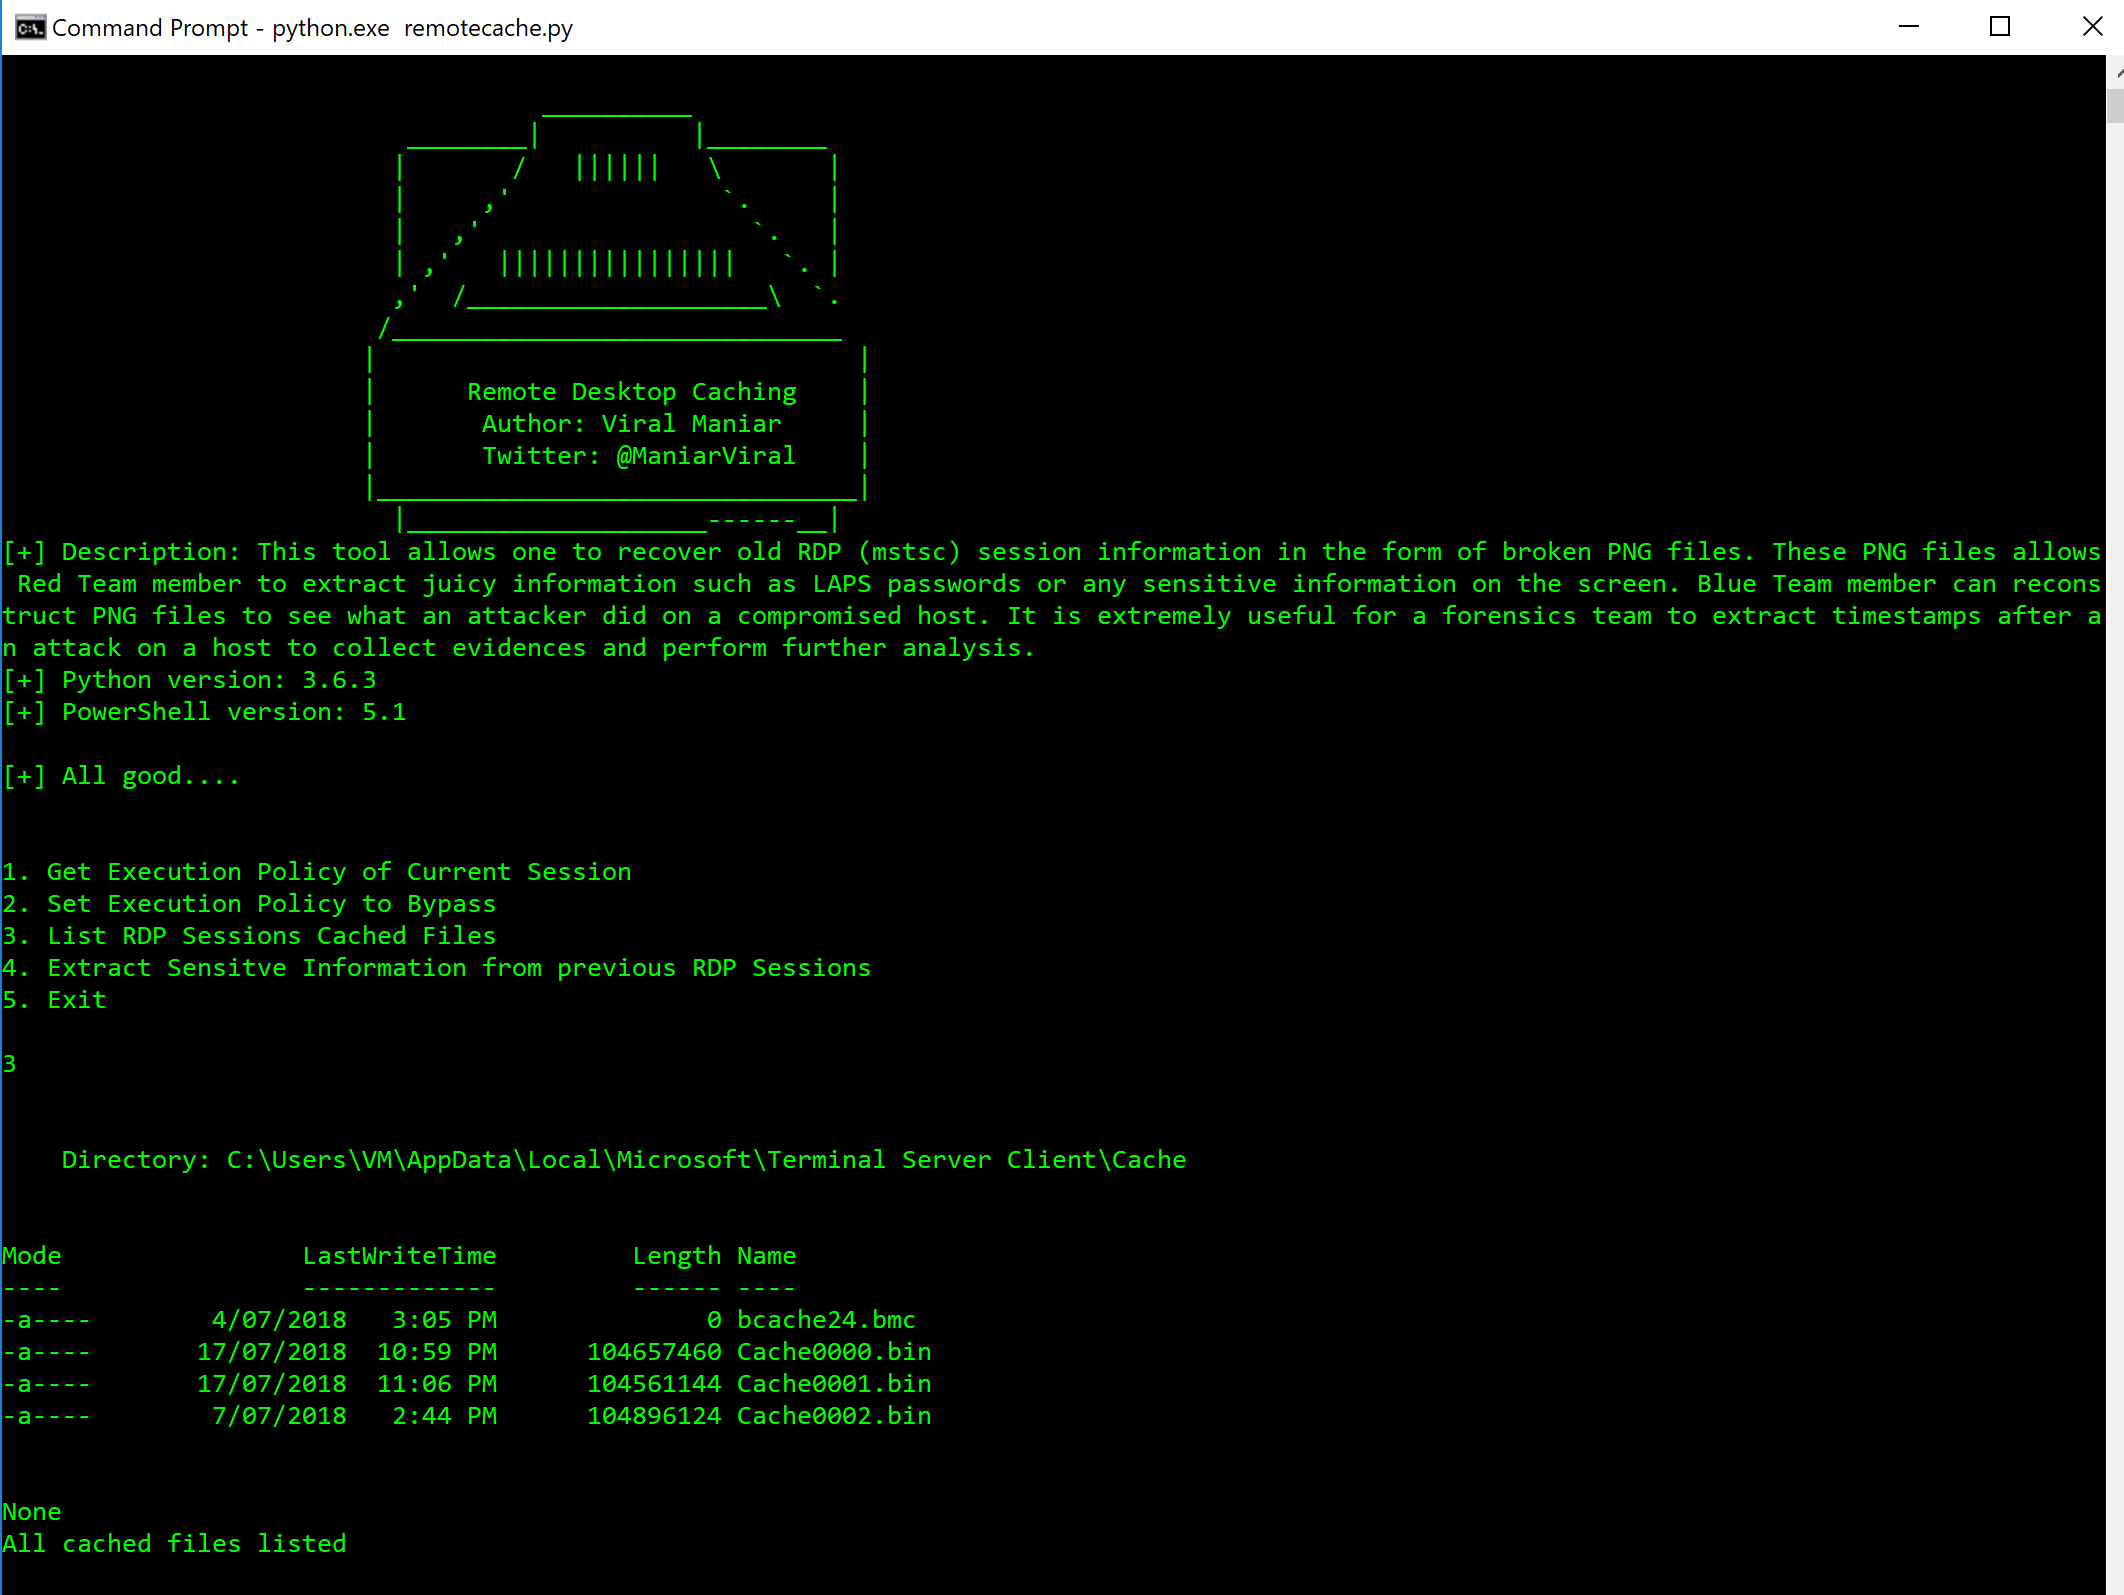
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
digital-forensicsforensicsincident-response+4
2188 years ago
proctools preview

proctools

GitHubmlcsec/proctools

Small toolkit for extracting information and dumping sensitive strings from Windows processes
digital-forensicsforensicsinformation-gathering+2
1162 years ago
artifacts-kit preview

artifacts-kit

GitHubforrest-orr/artifacts-kit

Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
exploitationforensicsmalware-analysis+5
2292 years ago
powerglot preview

powerglot

GitHubmindcrypt/powerglot

Powerglot encodes offensive powershell scripts using polyglots . Offensive security tool useful for stego-malware, privilege escalation, lateral…

defensive-toolsforensicslateral-movement+4
1836 years ago
Previous12Next
