

kube-reaper
 stillbigjosh/kube-reaper
Scans Kubernetes clusters from any identity, flags dangerous permissions, and chains them into multi-step escalation paths to cluster compromise.
cloud-securityconfiguration-auditingcontainer-security+9
3
stillbigjosh/kube-reaperScans Kubernetes clusters from any identity, flags dangerous permissions, and chains them into multi-step escalation paths to cluster compromise.
 w4r10ck423/envvisualizer
Parse and visualize /proc/self/environ on compromised Linux boxes — categorizes env vars by tech stack (AWS, Django, Rails, NodeJS, MySQL, K8s,…
 trustedsec/rage
Vendor-neutral NDJSON attack-graph format with node/edge taxonomy, AWS/GCP/Azure mappings, derivation rules, and an exposure DB for offensive…
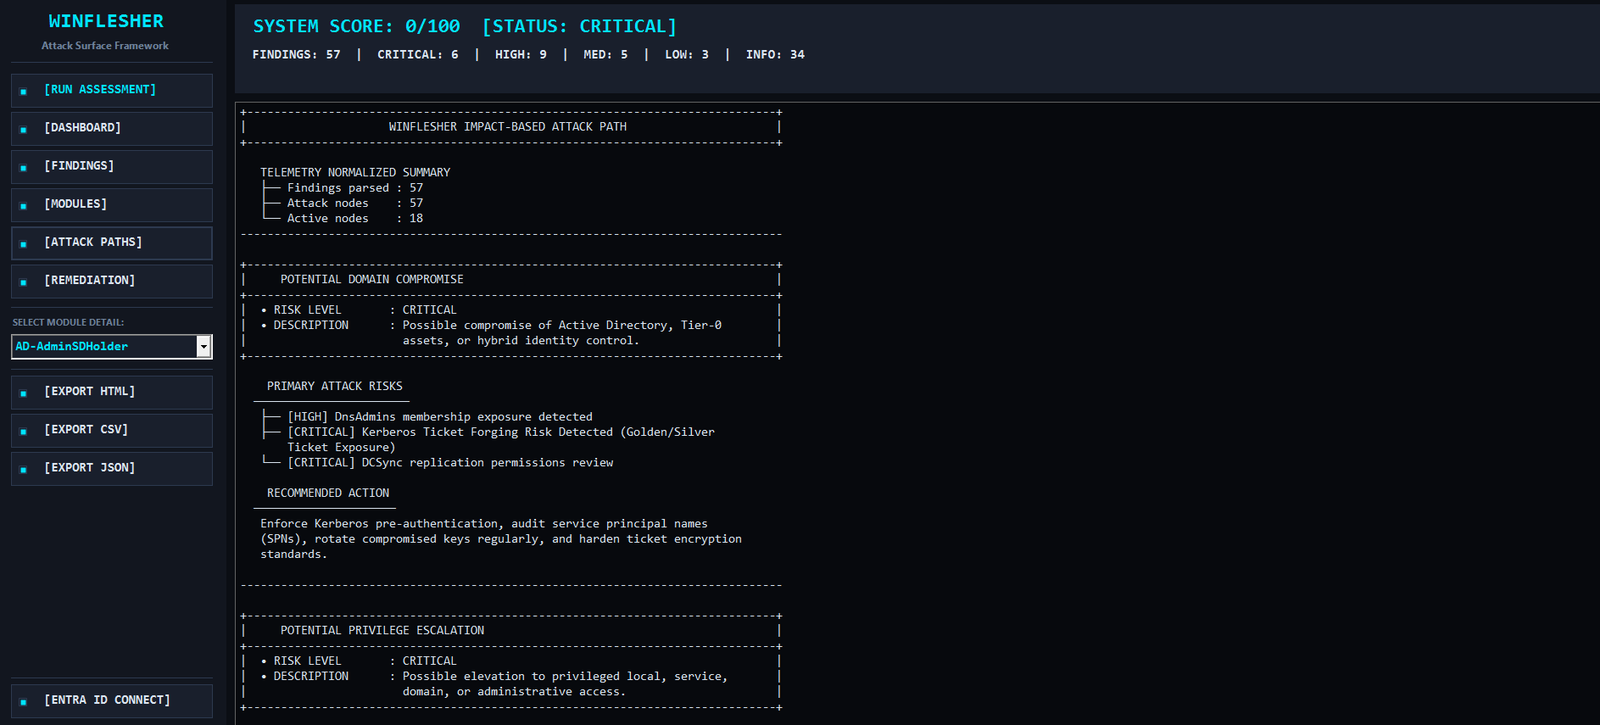 mindsflee/winflesher
Automated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…
 indoushka/context-aware-offensive-intelligence
Research framework redefining post-exploitation through decision intelligence.
 squidsec/bloodbash
Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…
 zyn3rgy/ldaprelayscan
Check for LDAP protections regarding the relay of NTLM authentication
 espressocake/defender_exclusions-bof
A BOF to determine Windows Defender exclusions.
 subat0mik/misconfiguration-manager
Misconfiguration Manager is a central knowledge base for all known Microsoft Configuration Manager tradecraft and associated defensive and hardening…
 bohops/ultimatewdacbypasslist
A centralized resource for previously documented WDAC bypass techniques
 p0dalirius/sharehound
A python tool to map the access rights of network shares into a BloodHound OpenGraphs easily
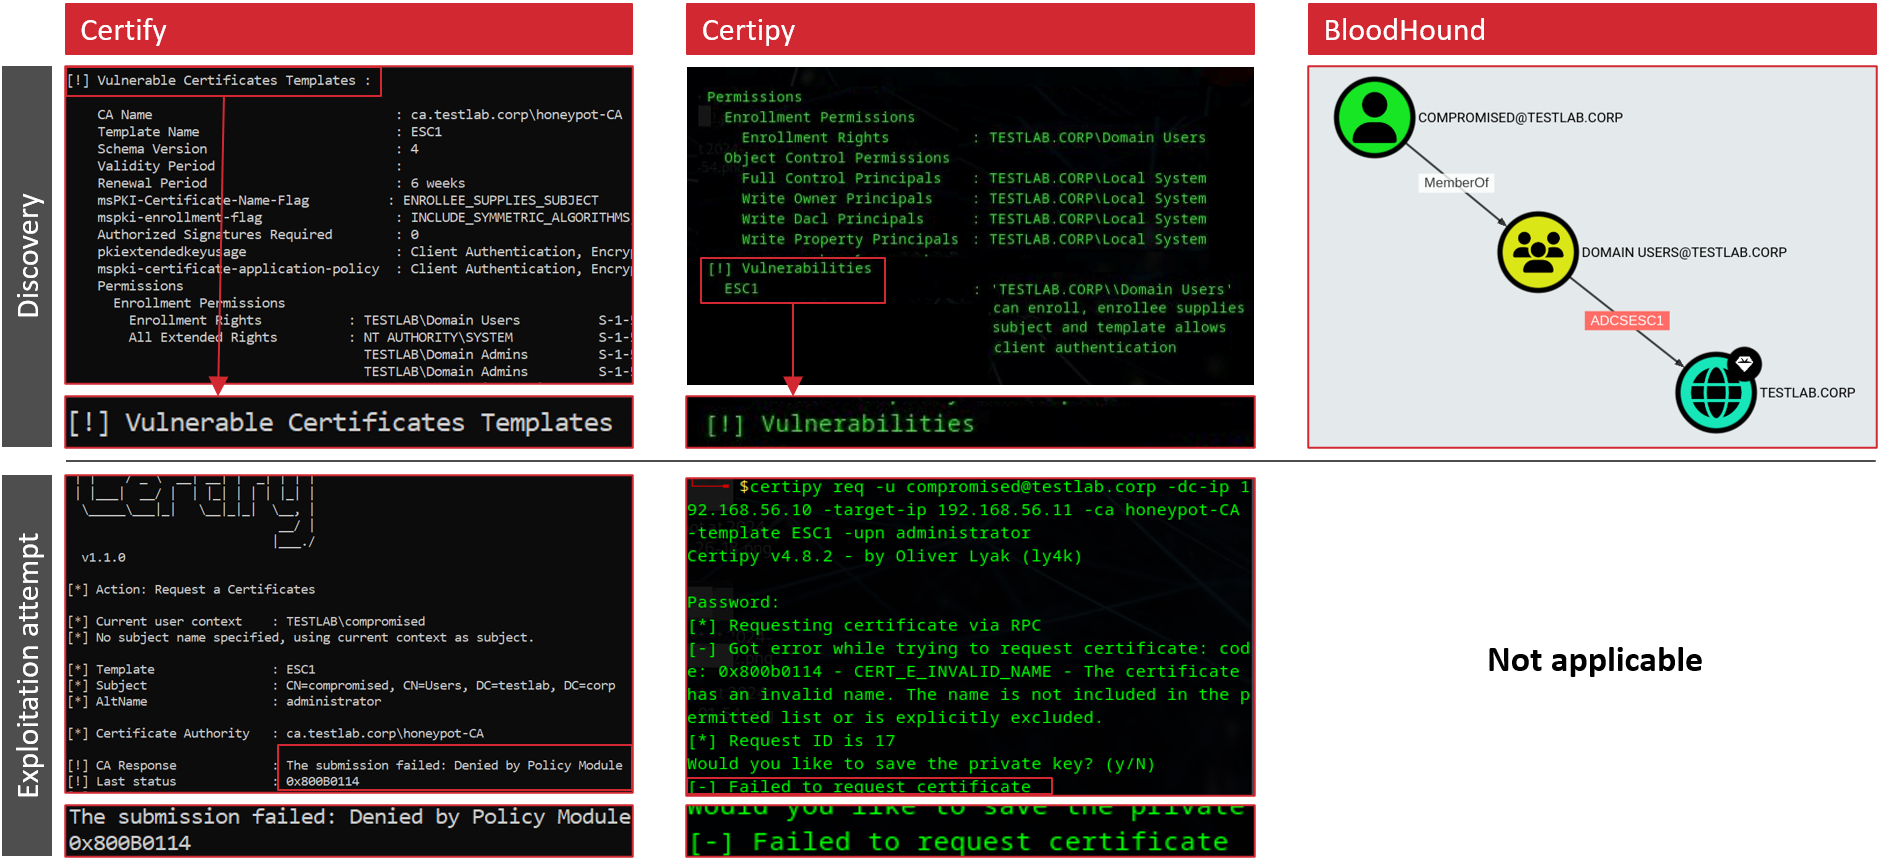 srlabs/certiception
An ADCS honeypot to catch attackers in your internal network.
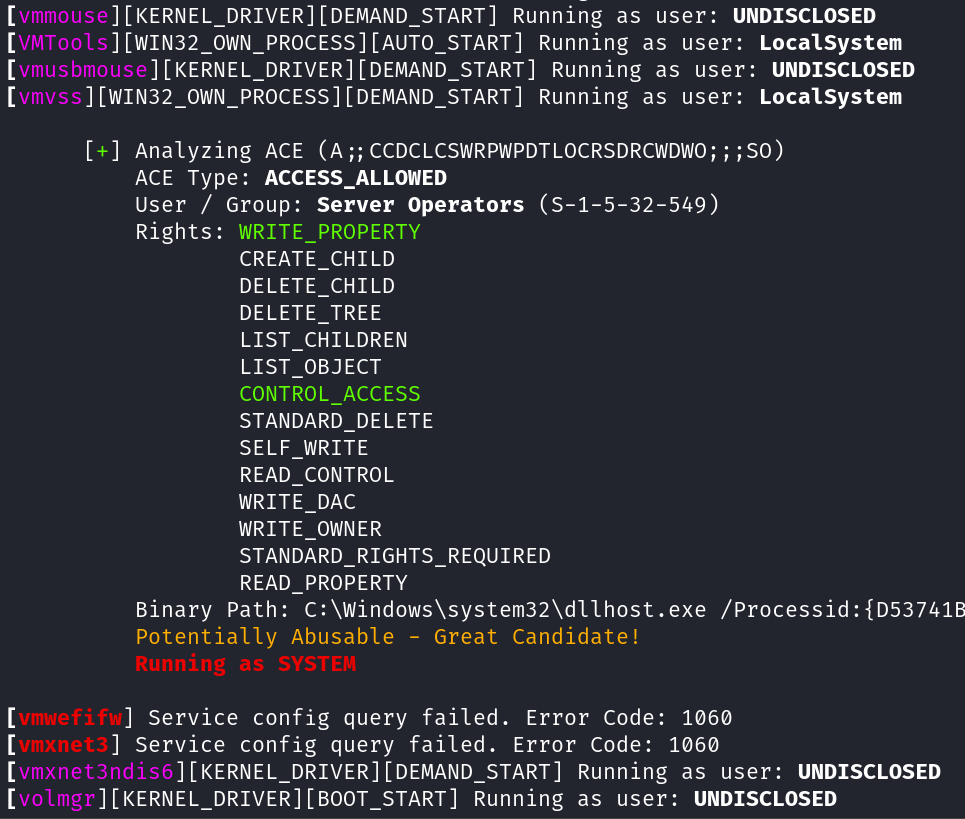 t3l3machus/aceshark
ACEshark is a utility designed for rapid extraction and analysis of Windows service configurations and Access Control Entries, eliminating the need…
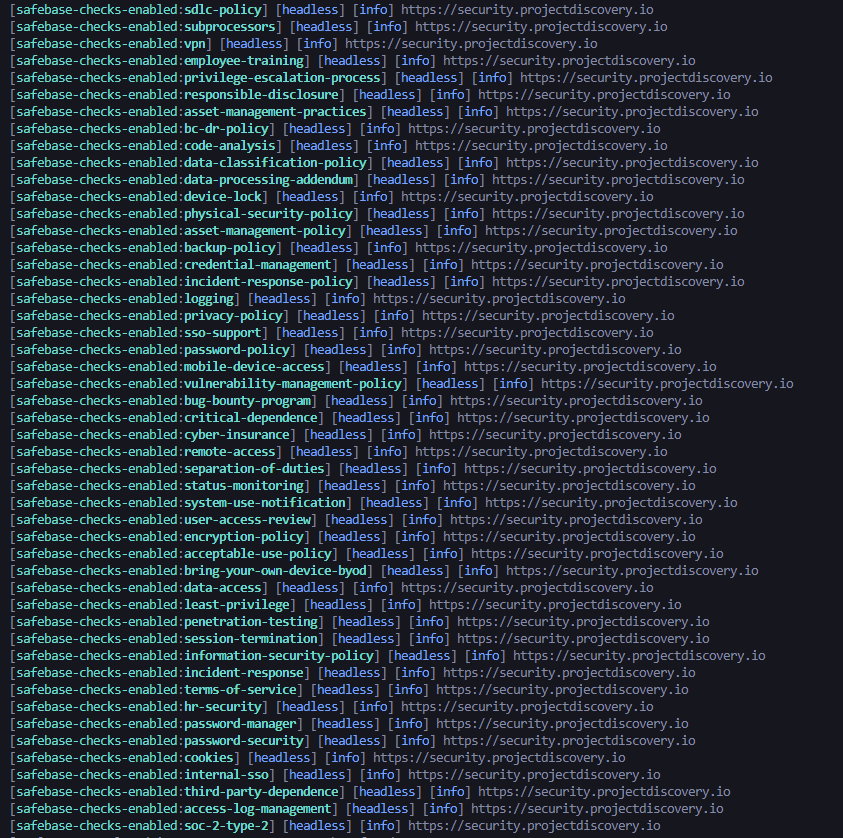 rxerium/internal-security-detect
The detection of internal security controls at a company
 synacktiv/gpoparser
gpoParser is a tool designed to extract and analyze configurations applied through Group Policy Objects (GPOs) in an Active Directory environment.
 blue0x1/sqlwinds
SQLWinds - SQL Server Security Assessment & Post-Exploitation Toolkit
 cerberusmrxi/cve-2026-57588-nessus-xml-import-sql-injection-poc
PoC for CVE-2026-57588 - SQL injection in Nessus 10.12.0 XML import. Generates malicious .nessus files to enumerate databases, exfiltrate…
 roo7break/serialator
Python script to exploit CVE-2015-4852.