archlive
 p3ng0s/archlive
Physical access red team live ISO built on Arch Linux
password-crackingpenetration-testingpost-exploitation+2
p3ng0s/archlivePhysical access red team live ISO built on Arch Linux
 elnerd/get-netntlm
Powershell module to get the NetNTLMv2 hash of the current user
 golem445/corporate_masks
8-14 character Hashcat masks based on analysis of 3.2 million NTLM hashes cracked while pentesting
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
 lkarlslund/hashmuncher
Grab NetNTLMv2 hashes using ETW with administrative rights on Windows 8.1 / Windows Server 2016 and later
 leftp/dpapisnoop
A C# tool to output crackable DPAPI hashes from user MasterKeys
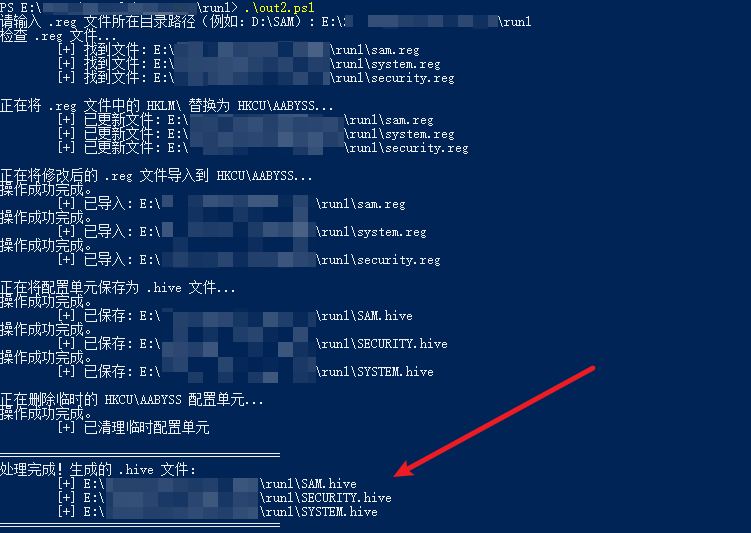 aabysszg/hashdump-bypassedr
Windows绕过EDR实现DumpHash
 kaihaochen04/monikerlinktest
cve-2024-21413
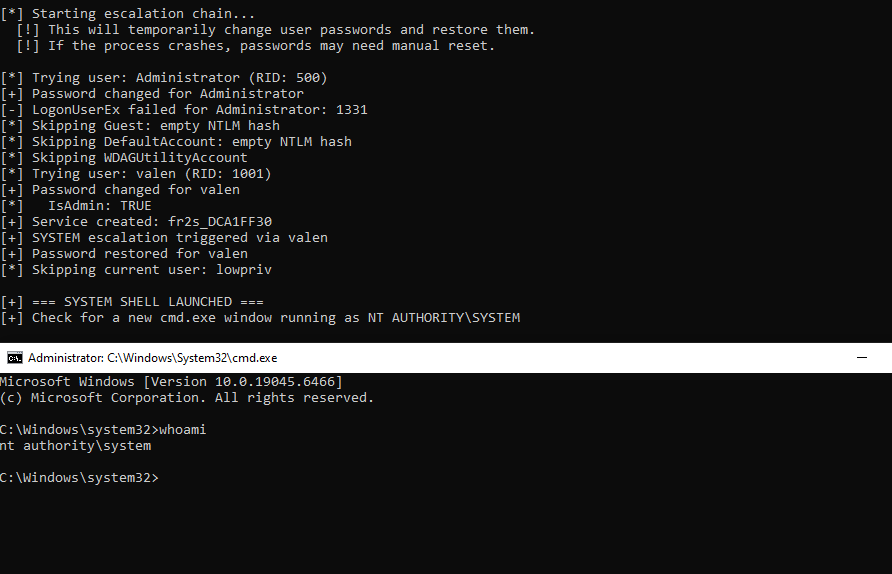
 danmcinerney/icebreaker
Gets plaintext Active Directory credentials if you're on the internal network but outside the AD environment
 them4hd1/vayne-rat
An Advanced C# .NET Rat, It’s Stable and Contains Many Features.
 cyberark/riskyspn
Detect and abuse risky SPNs
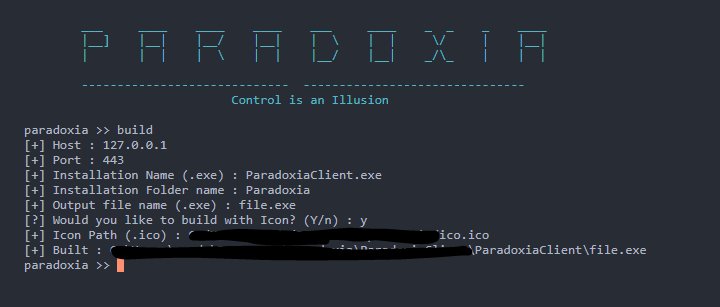 quantumcore/paradoxiarat
ParadoxiaRat : Native Windows Remote access Tool.
 orange-cyberdefense/keepwn
A python tool to automate KeePass discovery and secret extraction.