
Get-NetNTLM
 elnerd/get-netntlm
Powershell module to get the NetNTLMv2 hash of the current user
hash-analysisinformation-gatheringpassword-attacks+4
974 years ago
elnerd/get-netntlmPowershell module to get the NetNTLMv2 hash of the current user
 ajnik/joomla-bruteforce
Python script that brute-forces Joomla administrator login credentials using wordlists, with proxy and verbose options for penetration testing.
 golem445/corporate_masks
8-14 character Hashcat masks based on analysis of 3.2 million NTLM hashes cracked while pentesting
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
 n0isegat3/regpwnbrc4bof
Brute Ratel C4 BOF that exploits a registry symlink race condition in Windows Accessibility ATConfig to escalate privileges to SYSTEM by writing…
 paranoidninja/brute-ratel-c4-community-kit
This repository contains scripts, configurations and deprecated payload loaders for Brute Ratel C4 (https://bruteratel.com/)
 mr-un1k0d3r/windows-signedbinary
Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…
 jimilinuxguy/lrs-pager-systems-bruteforce
Long Range Pager Systems pagers and coasters URH and YS1 (yardstick one / cc11xx) information and brute force tool
 tw1sm/badger-builder
badger-builder is an AI-assisted tool for generating dynamic Brute Ratel C4 profiles
 lkarlslund/hashmuncher
Grab NetNTLMv2 hashes using ETW with administrative rights on Windows 8.1 / Windows Server 2016 and later
 leftp/dpapisnoop
A C# tool to output crackable DPAPI hashes from user MasterKeys
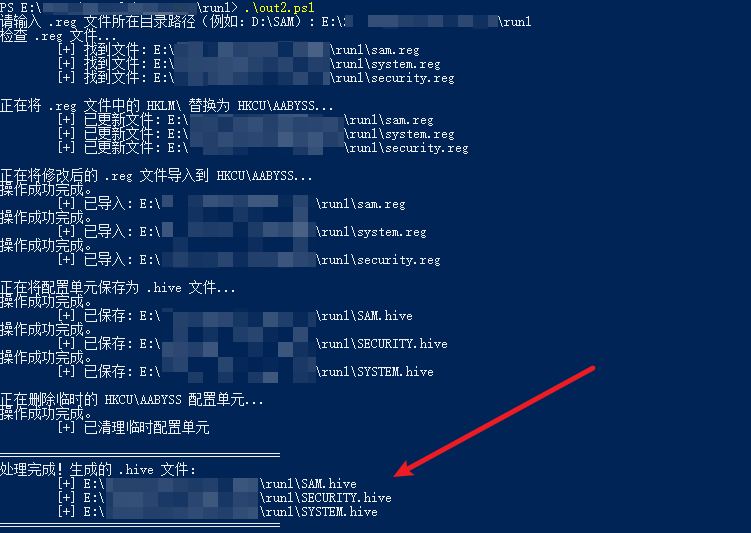 aabysszg/hashdump-bypassedr
Windows绕过EDR实现DumpHash
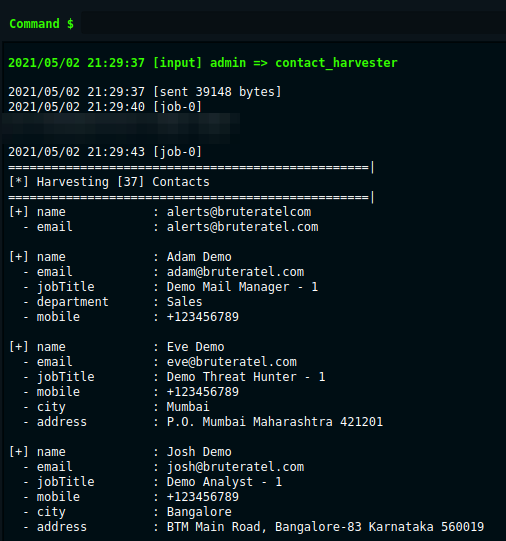 paranoidninja/brc4-bof-artillery
Collection of Brute Ratel C4 BOFs for Windows post-exploitation: process memory access, NetNTLMv2 hash retrieval, contact harvesting, and…
 iqbalx7/wp2shell
unauthenticated RCE in WordPress core (CVE-2026-63030 + CVE-2026-60137)
 averagesecurityguy/crack
XMLRPC server for password cracking
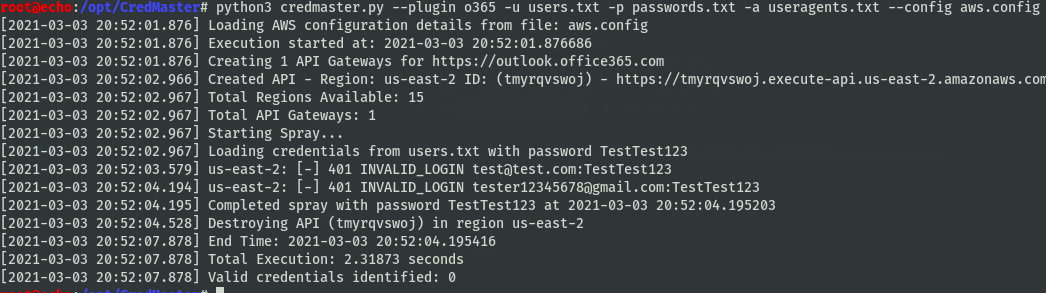 knavesec/credmaster
Refactored & improved CredKing password spraying tool, uses FireProx APIs to rotate IP addresses, stay anonymous, and beat throttling
 kaihaochen04/monikerlinktest
cve-2024-21413