

wraith
 arcanum-sec/wraith
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
command-and-controleducationexploitation+6
146
arcanum-sec/wraithBrowser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
 tarpeg007/cve-2026-19490
NetScaler ADC/Gateway SAML unsigned-assertion bypass via HTTP-Redirect binding (CTX696939) - root cause analysis + PoC
 samsayen/jqueryingu
Valid JQuery that profiles the system and returns info to the server in a fake analytics GET request
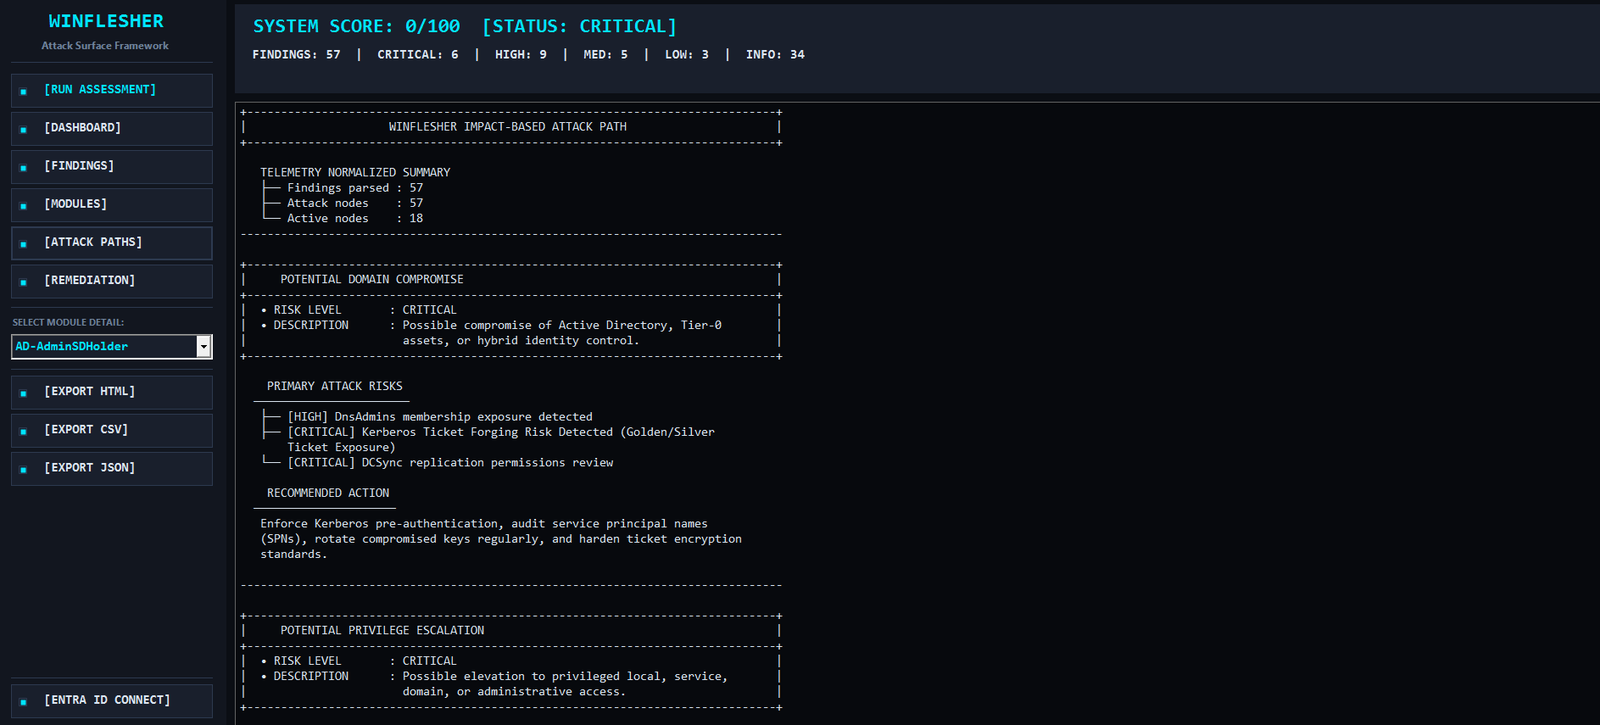 mindsflee/winflesher
Automated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…
 koadt/poc-cve-2026-32255
This repository contains a proof of concept (POC) for CVE-2026-32255, a high-severity Server-Side Request Forgery (SSRF) vulnerability in Kan, an…
 wh04m1001/diagtrackeop
Windows privilege-escalation exploit abusing SeImpersonate via DiagTrack RPC, using Secondary Logon to get an INTERACTIVE token and gain SYSTEM.
 fransr/hot-jar-swapping-urlclassloader
Demo of the URLClassLoader JAR-swapping showing the ability to replace and exploit an already loaded JAR with inner classes
 binderlabs/dircreate2system
Weaponizing to get NT SYSTEM for Privileged Directory Creation Bugs with Windows Error Reporting
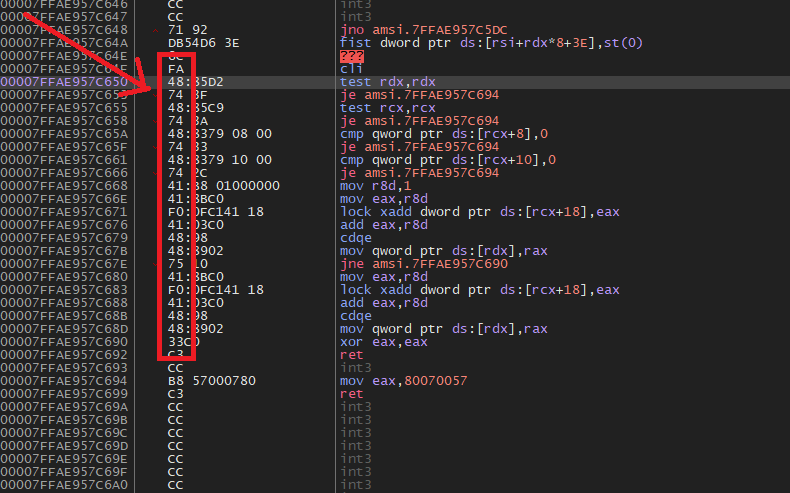 zeromemoryex/amsi-killer
Lifetime AMSI bypass
 lkarlslund/hashmuncher
Grab NetNTLMv2 hashes using ETW with administrative rights on Windows 8.1 / Windows Server 2016 and later
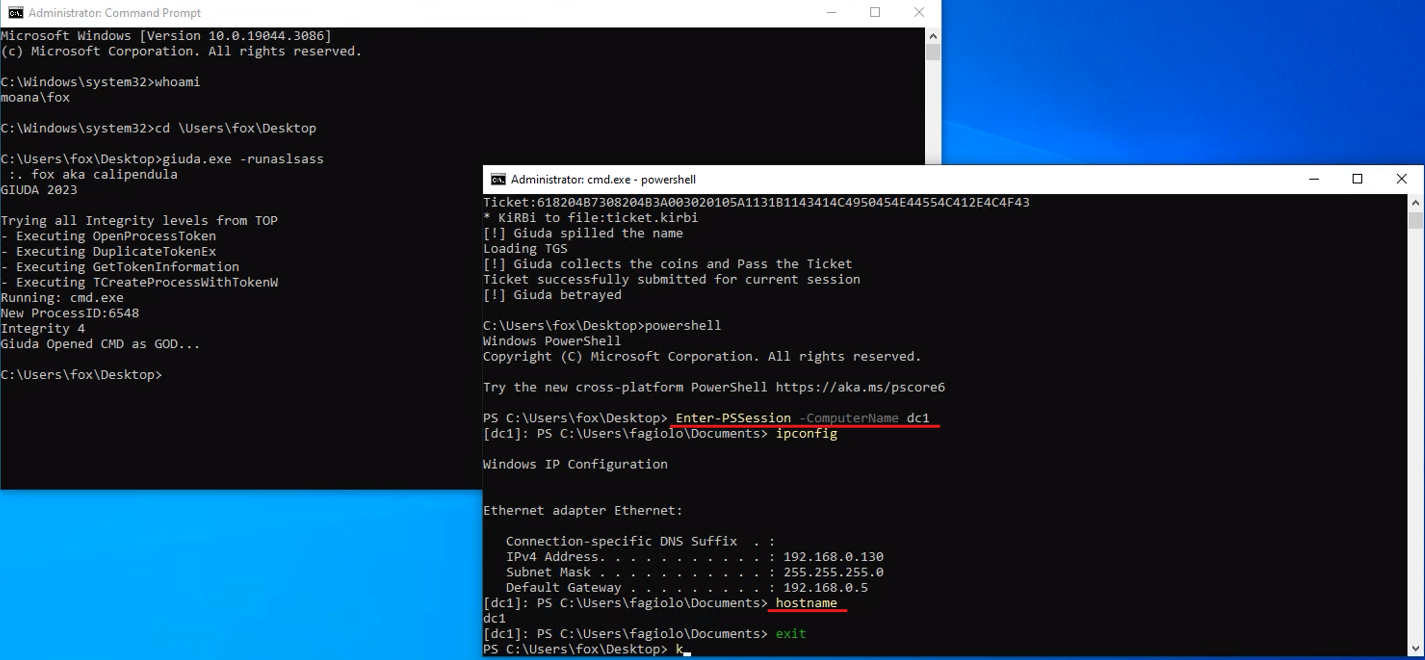 foxlox/giuda
Ask a TGS on behalf of another user without password
 wavvs/nanorobeus
COFF file (BOF) for managing Kerberos tickets.
 nul0x4c/manualrsrcdatafetching
Get your data from the resource section manually, with no need for windows apis
 scratchappy/cve-2025-68937
Automated PoC exploit for CVE-2025-68937 — Gitea/Forgejo Template Symlink RCE. Any authenticated user can get a shell as the git service user.
 nxploited/cve-2026-13714
Realtyna Organic IDX plugin + WPL Real Estate < 5.3.0 - Unauthenticated Arbitrary File Upload to Remote Code Execution
 3gstudent/homework-of-python
Python codes of my blog.
 randomrobbiebf/kong-pwn
Use Exposed KongAPI to act like a proxy and get metadata urls or internal urls
 k3ystr0k3r/httpstrike
DDoS script meant to flood websites.