
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
137 results
pwndrop preview

pwndrop

GitHubkgretzky/pwndrop

Self-deployable file hosting service for red teamers, allowing to easily upload and share payloads over HTTP and WebDAV.
phishing-toolsred-teamingweb-security
2.3k5 years ago
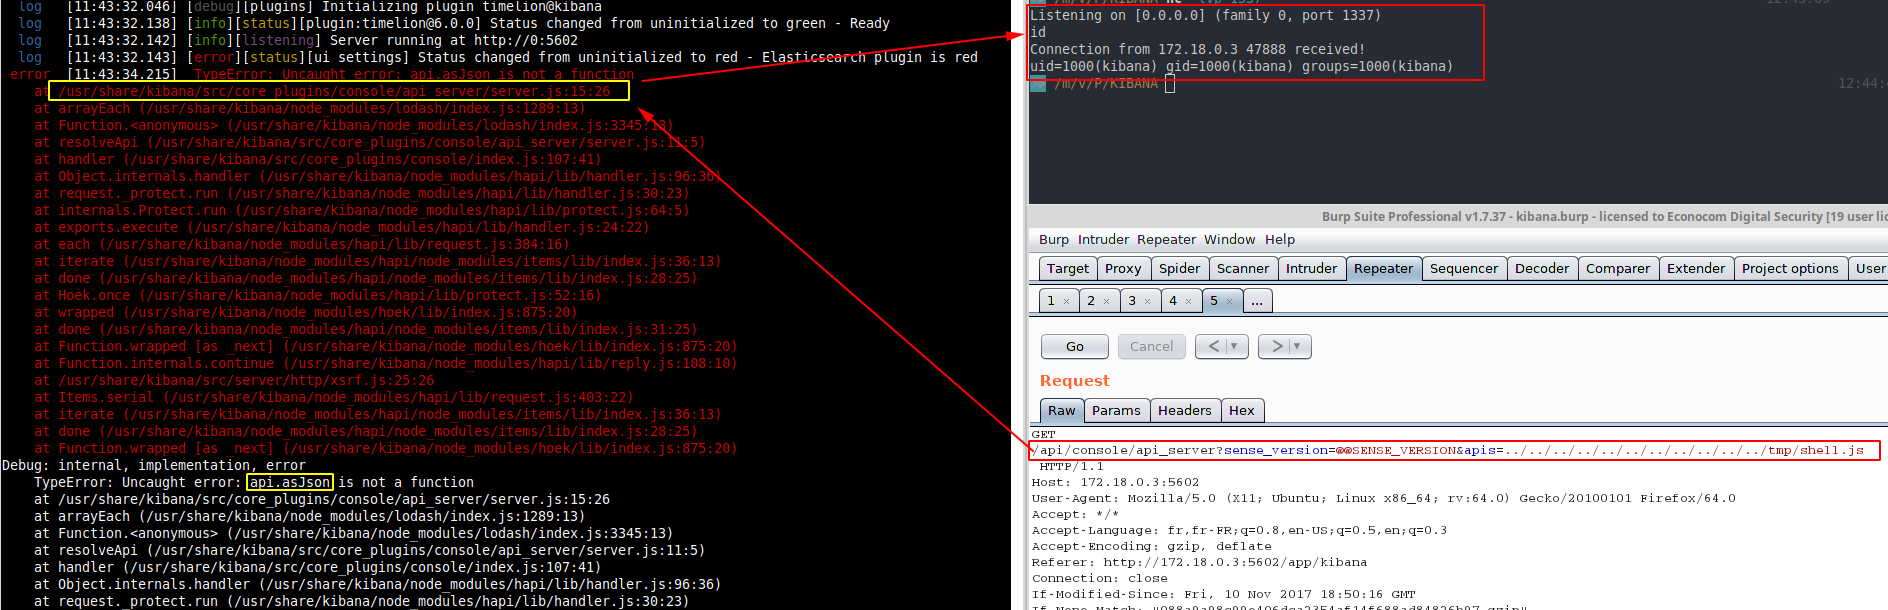
CVE-2018-17246 preview

CVE-2018-17246

GitHubmpgn/cve-2018-17246

CVE-2018-17246 - Kibana LFI < 6.4.3 & 5.6.13
exploitationpayload-developmentpenetration-testing+3
656 years ago
CVE-2024-51793 preview

CVE-2024-51793

GitHub0axz-tools/cve-2024-51793

Exploits CVE-2024-51793 unauthenticated arbitrary file upload in WordPress Computer Repair Shop plugin, scans target lists, uploads PHP webshells,…
exploitationpayload-developmentpenetration-testing+3
11 months ago
Better-CVE-2022-29464 preview

Better-CVE-2022-29464

GitHubjimidk/better-cve-2022-29464

Proof-of-concept exploit for CVE-2022-29464 enabling unrestricted file upload and remote code execution on vulnerable WSO2 products, with a custom…
exploitationpayload-generationpenetration-testing+3
54 years ago
shepard preview

shepard

GitHubd3adzo/shepard

In progress persistent download/upload/execution tool using Windows BITS.
command-and-controldata-exfiltrationpersistence-mechanisms+3
415 years ago
Flowise-CVE-2026-58057-exploit preview

Flowise-CVE-2026-58057-exploit

GitHubcerberusmrxi/flowise-cve-2026-58057-exploit

Flowise Windows RCE exploit for CVE-2026-58057. Bypasses environment variable validation via case-sensitive flaw. Uses node_options to inject…

command-and-controlexploitationinformation-gathering+7
12 months ago
Ghost-5.58-Arbitrary-File-Read-CVE-2023-40028 preview

Ghost-5.58-Arbitrary-File-Read-CVE-2023-40028

GitHub0xdtc/ghost-5.58-arbitrary-file-read-cve-2023-40028

CVE-2023-40028 affects Ghost, an open source content management system, where versions prior to 5.59.1 allow authenticated users to upload files that…
educationexploitationpenetration-testing+3
131 year ago
KrayinCRM-RCE-Exploit-CVE-2026-38526 preview

KrayinCRM-RCE-Exploit-CVE-2026-38526

GitHubcerberusmrxi/krayincrm-rce-exploit-cve-2026-38526

CVE-2026-38526 exploit for Krayin CRM v2.2.x - Authenticated RCE via TinyMCE file upload bypass. Features interactive shell, multi-type payloads,…

exploitationpayload-generationpenetration-testing+4
32 months ago
CVE-2025-52691-APT-PoC preview

CVE-2025-52691-APT-PoC

GitHubdeathshotxd/cve-2025-52691-apt-poc

An enhanced proof-of-concept exploit for CVE-2025-52691 (SmarterMail Arbitrary File Upload RCE) with APT-level features like stealth obfuscation,…
data-exfiltrationeducationexploitation+6
58 months ago
By-Poloss..-..CVE-2026-18080 preview

By-Poloss..-..CVE-2026-18080

GitHubpolosss/by-poloss..-..cve-2026-18080

Exploit for CVE-2026-18080, an unauthenticated arbitrary file upload leading to RCE in ERP Complete HR, Accounting & CRM Suite. Includes Python and…
exploitationpayload-developmentpenetration-testing+3
29 days ago
WSOB preview

WSOB

GitHubdsssssssm/wsob

Python exploit tool for CVE-2022-29464, enabling unrestricted file upload and remote code execution on vulnerable WSO2 products via directory…
exploitationpenetration-testingred-teaming+2
263 years ago
CVE-2026-57827 preview

CVE-2026-57827

GitHubshinthink/cve-2026-57827

CVE-2026-57827 — RSFiles! Joomla Component Unauthenticated File Upload RCE. Split-controller upload bypass. CVSS 9.8 | CWE-434 | com_rsfiles < 1.17.12
exploitationinformation-gatheringpayload-development+6
161 month ago
XSS2Shell preview

XSS2Shell

GitHubg0d150ne/xss2shell

Exploits WordPress pre-auth XSS (CVE-2026-64638) to achieve remote code execution, installing an AES-encrypted backdoor webshell with persistence,…
command-and-controlexploitationinformation-gathering+6
21 month ago
CVE-2026-56291 preview

CVE-2026-56291

GitHubshinthink/cve-2026-56291

Balbooa Forms (com_baforms) < 2.4.1 — Unauthenticated File Upload to RCE via form.uploadAttachmentFile | CVSS 9.8 | CISA KEV
exploitationpayload-generationpenetration-testing+3
22 months ago
CVE-2026-21627---Tassos-Novarain-Framework-plg_system_nrframework-Exploit---Joomla preview

CVE-2026-21627---Tassos-Novarain-Framework-plg_system_nrframework-Exploit---Joomla

GitHubyallasec/cve-2026-21627---tassos-novarain-framework-plg_system_nrframework-exploit---joomla

Python exploit for CVE-2026-21627, an unauthenticated arbitrary PHP file inclusion in Joomla's Novarain Framework, enabling file upload, delete, and…

exploitationpayload-developmentpenetration-testing+3
7 months ago
CVE-2025-6325_CVE-2025-6327 preview

CVE-2025-6325_CVE-2025-6327

GitHubjohenlastgen-jlg/cve-2025-6325_cve-2025-6327

Python PoC validating CVE-2025-6325 unauthenticated privilege escalation and CVE-2025-6327 arbitrary file upload RCE in King Addons for Elementor <=…

crawlerexploitationpayload-development+7
3 days ago
langflow-rce-exploit preview

langflow-rce-exploit

GitHub0-d3y/langflow-rce-exploit

Remote Code Execution Exploit for Langflow (CVE-2025-3248) - [ By S4Tech ]
command-and-controlexploitationpayload-development+8
71 year ago
CVE-2026-5524-PoC preview

CVE-2026-5524-PoC

GitHubiicaicai/cve-2026-5524-poc

Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…

exploitationinformation-gatheringpayload-development+8
2 months ago
Previous12…8Next