
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
56 results
OSRipper preview

OSRipper

GitHubnoahoksuz/osripper

AV evading cross platform Backdoor and Crypter Framework with a integrated lightweight webUI
command-and-controleducationexploit-frameworks+5
3337 months ago
ImpulsiveDLLHijack preview

ImpulsiveDLLHijack

GitHubknight0x07/impulsivedllhijack

C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be…

binary-exploitationexploitationpersistence-mechanisms+2
5565 years ago
TeamsImplant preview

TeamsImplant

GitHuballevon412/teamsimplant

Stealthy DLL proxying implant for Microsoft Teams that injects AES-encrypted shellcode via unhooking techniques, providing persistent backdoor access…
command-and-controlexploit-frameworkspayload-development+5
2074 years ago
bt2 preview

bt2

GitHubblazeinfosec/bt2

Blaze Telegram Backdoor Toolkit is a post-exploitation tool that leverages the infrastructure of Telegram as a C&C
command-and-controlpayload-developmentpenetration-testing+3
20610 years ago
ADOKit preview

ADOKit

GitHubh4wkst3r/adokit

Modular attack toolkit exploiting Azure DevOps REST API for reconnaissance, privilege escalation, and persistence using stolen cookies or PATs.
cloud-securitypenetration-testingpersistence-mechanisms+3
1541 month ago
CVE-2021-4034 preview

CVE-2021-4034

GitHubdevianntsec/cve-2021-4034

Master's thesis research on CVE-2021-4034 (PwnKit) local privilege escalation. Multi-payload Python exploit with 7 modes including interactive shell,…
binary-exploitationeducationexploitation+7
15 months ago
CVE-2011-2523-vsFTPd-2.3.4-Writeup preview

CVE-2011-2523-vsFTPd-2.3.4-Writeup

GitHubkn9annihilator/cve-2011-2523-vsftpd-2.3.4-writeup

Technical writeup and exploitation guide for CVE-2011-2523, a backdoor vulnerability in vsFTPd 2.3.4, detailing the exploit mechanism and manual…
binary-exploitationeducationexploitation+3
2 months ago
UACME preview

UACME

GitHubhfiref0x/uacme

Defeating Windows User Account Control
educationexploitationprivilege-escalation+1
7.8k2 months ago
reverse-ssh preview

reverse-ssh

GitHubfahrj/reverse-ssh

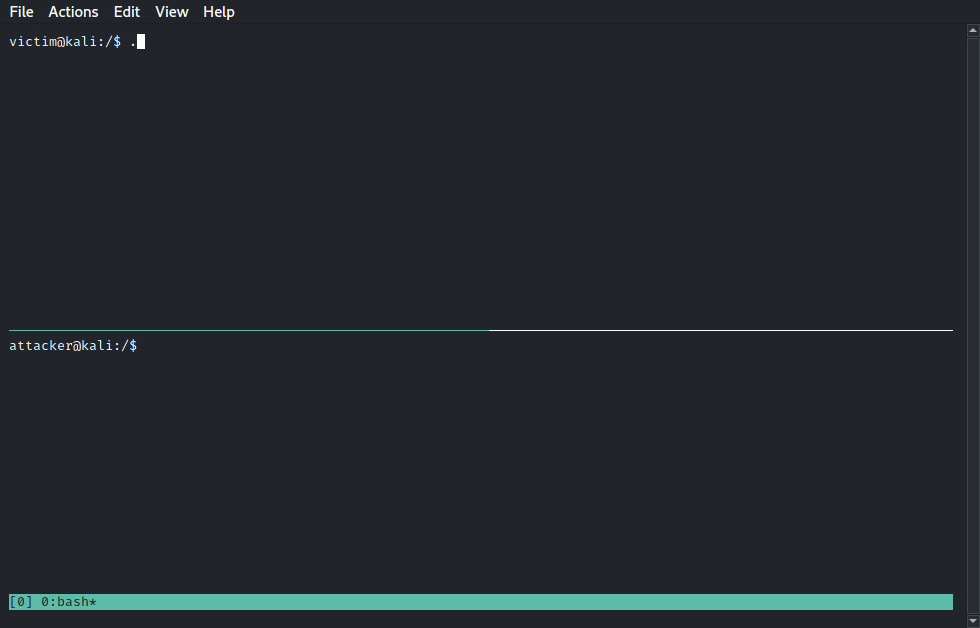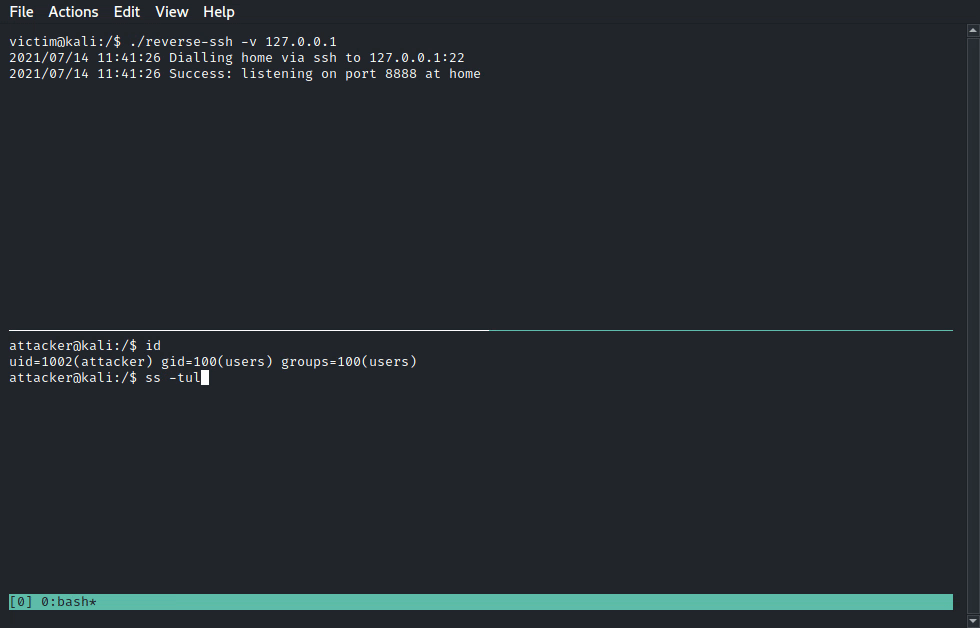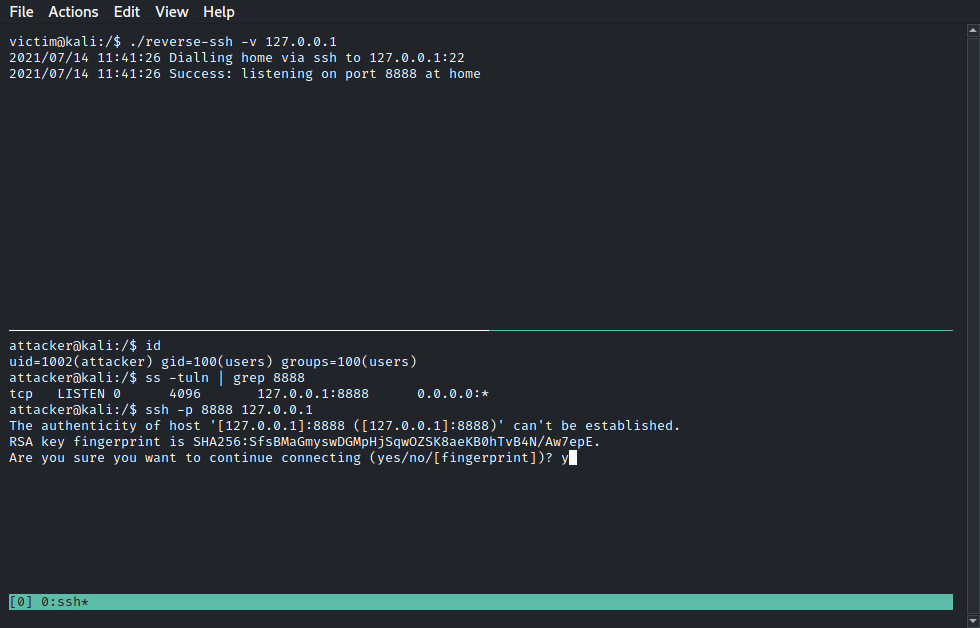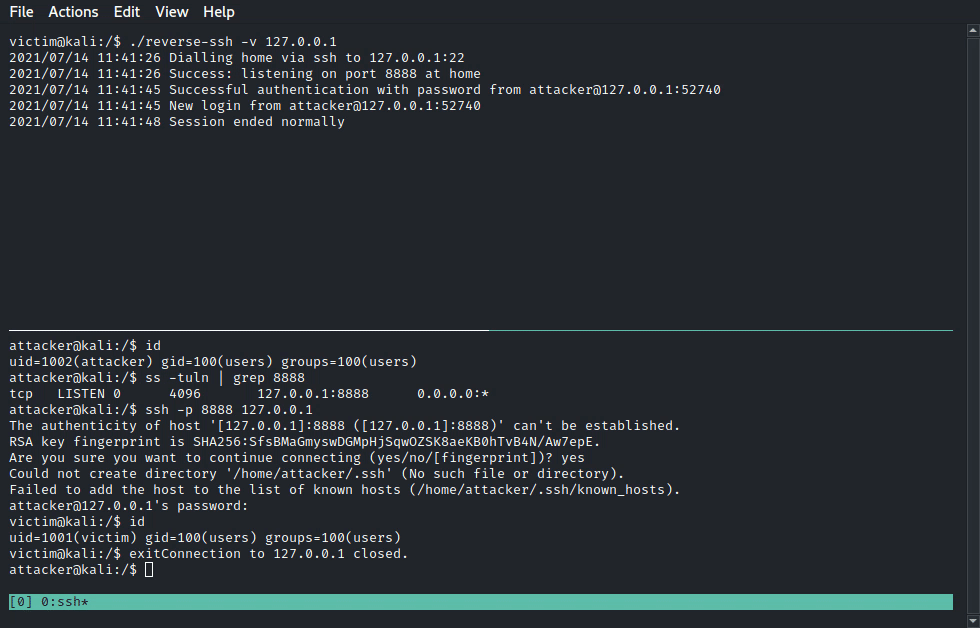
Statically-linked ssh server with reverse shell functionality for CTFs and such
ctfpenetration-testingpost-exploitation+2
1.1k3 years ago
Powershell-RAT preview

Powershell-RAT

GitHubviralmaniar/powershell-rat

Python based backdoor that uses Gmail to exfiltrate data through attachment. This RAT will help during red team engagements to backdoor any Windows…
data-exfiltrationeducationpayload-generation+4
1.2k7 years ago
Diamorphine preview

Diamorphine

GitHubm0nad/diamorphine

LKM rootkit for Linux Kernels 2.6.x/3.x/4.x/5.x/6.x (x86/x86_64 and ARM64)
malware-analysispersistence-mechanismsprivilege-escalation+1
2.5k5 months ago
ghost preview

ghost

GitHubahxr/ghost

Lightweight RAT providing silent remote command-line access, hidden file download/execution, and persistence mechanisms for Windows systems.…
command-and-controleducationmalware-analysis+5
1.1k8 years ago
nosferatu preview

nosferatu

GitHubkindtime/nosferatu

DLL that hooks NTLM and Kerberos authentication in lsass.exe to inject a backdoor hash, enabling persistent authenticated access on Windows systems.

authenticationlateral-movementpenetration-testing+2
2411 year ago
twittor preview

twittor

GitHubpaulsec/twittor

A fully featured backdoor that uses Twitter as a C&C server
command-and-controlexploitationpayload-development+4
81111 years ago
Kittysploit-framework preview

Kittysploit-framework

GitHubsia-iotechnology/kittysploit-framework

Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
ai-securitycommand-and-controldebuggers+8
62320 days ago
CVE-2026-Discord preview

CVE-2026-Discord

GitHubnicetop1027/cve-2026-discord

Critical vulnerability report detailing zero-day Remote Debugging Port exposure in Discord macOS client leading to account takeover, spyware, worm…
data-exfiltrationexploitationpenetration-testing+3
8 months ago
Powershell-C2 preview

Powershell-C2

GitHubal1ex/powershell-c2

Powershell-C2

command-and-controlpayload-developmentpersistence-mechanisms+2
16 years ago
sshimpanzee preview

sshimpanzee

GitHublexfo/sshimpanzee

SSHD Based implant supporting tunneling mecanisms to reach the C2 (DNS, ICMP, HTTP Encapsulation, HTTP/Socks Proxies, UDP...)

command-and-controldns-analysisnetwork-security+4
2931 year ago
Previous1234Next