
gitread
 plur1bu5/gitread
CVE-2026-85706 · GitLab CE/EE unauthenticated file read · research PoC with oracle mode, fd enumeration, and tiered loot targeting
data-exfiltrationexploitationinformation-gathering+7
1
plur1bu5/gitreadCVE-2026-85706 · GitLab CE/EE unauthenticated file read · research PoC with oracle mode, fd enumeration, and tiered loot targeting
 boroeurnprach/ashwesker-cve-2026-21962
Exploit PoC and Nuclei template for CVE-2026-21962, a critical unauthenticated remote code execution in Oracle HTTP Server and WebLogic Proxy…
 tc4dy/cve-2026-60206-poc-exploit
👾 CVE-2026-60206 - Oracle WebLogic SAML Auth Bypass Exploit Framework ⚡Bash & Python versions. Features: --detect safe check, --exploit…
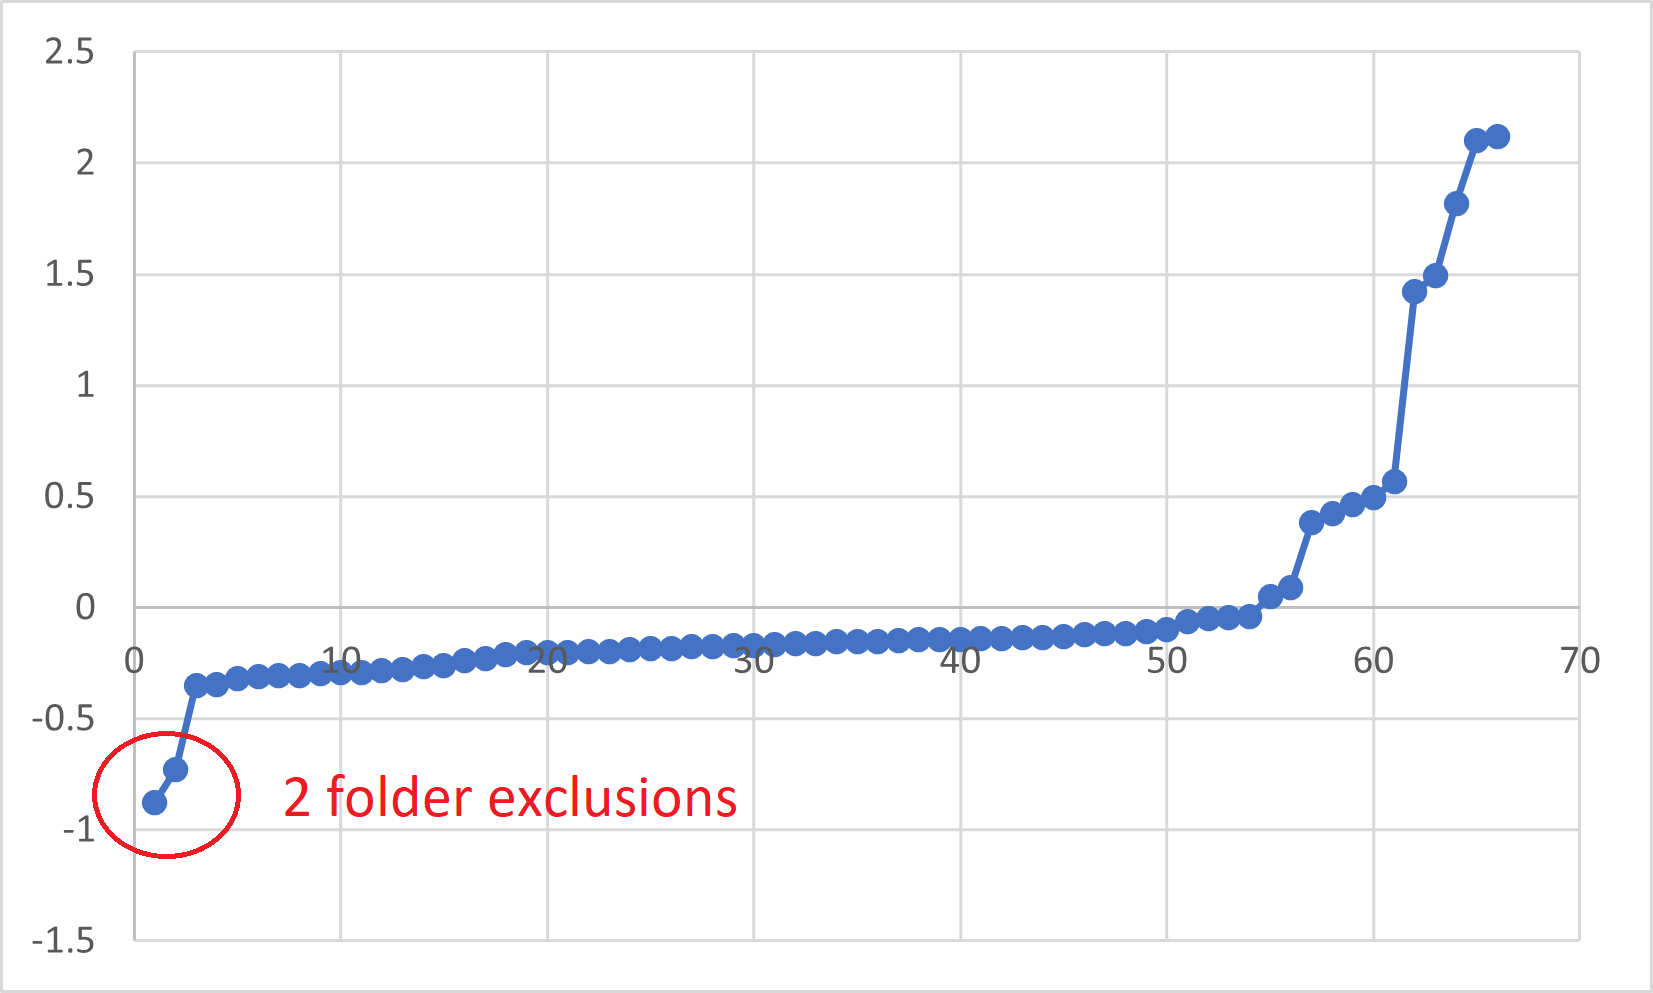 bananabr/timeexception
A tool to find folders excluded from AV real-time scanning using a time oracle
 abq0/rwsploit
Automated exploitation scanner for Oracle Reports Server (rwservlet) — CVE-2012-3152 / CVE-2012-3153. Detects, fingerprints, reads files via LFI,…
 wise-security/cve-2025-69600
Demonstrates command injection vulnerabilities in RayVentory Scan Engine's rvia tool, allowing arbitrary command execution via getconfig, upload,…
 dadvlingd/cve-2024-21006
Exploit for CVE-2024-21006 targeting Oracle WebLogic Server LDAP injection vulnerability. Requires JNDIExploit service and specific JDK version for…
 zeetee1235/cve-2026-21962
Verified PoC and analysis for CVE-2026-21962, an access-control bypass in Oracle HTTP Server/WebLogic Proxy Plug-in via URI normalization…
 loursha/oracle-weblogic-server-asyncresponseservice-deserialization-remote-code-execution-cve-2019-2725
Unauthenticated remote code execution exploit for Oracle WebLogic Server (CVE-2019-2725) via deserialization in AsyncResponseService, delivering a…
 gregk4sec/cve-2026-21962
Proof-of-concept exploit for CVE-2026-21962, a critical path traversal vulnerability in Oracle OHS and WebLogic Server proxy plugins leading to…
 mansk1es/cve-2024-21111
Oracle VirtualBox Elevation of Privilege (Local Privilege Escalation) Vulnerability
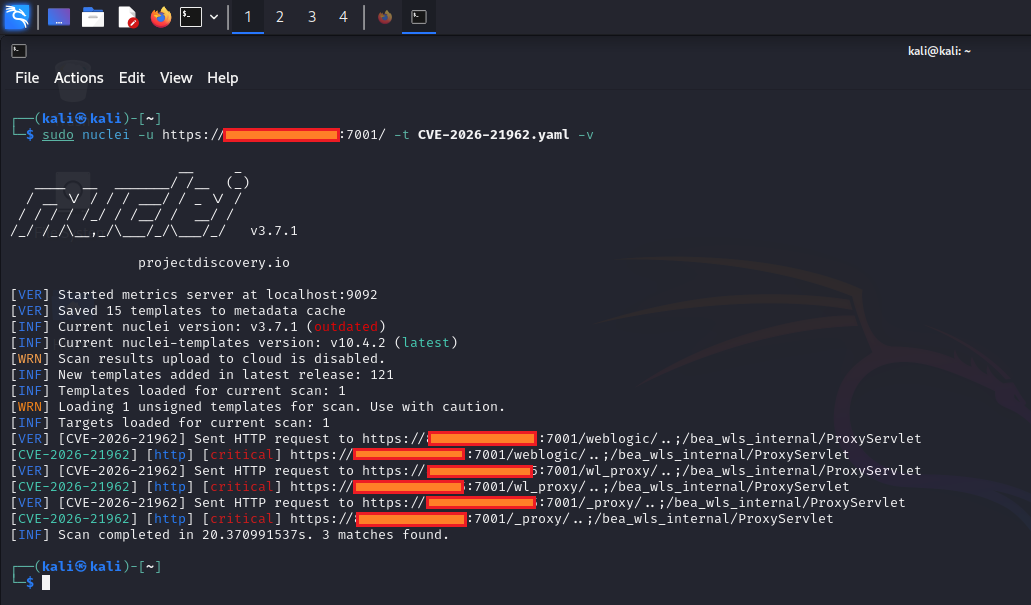 0xblackash/cve-2026-21962
CVE-2026-21962
 hyderpwn/weblogic
Unauthenticated authentication bypass and remote code execution exploit for Oracle WebLogic Server, targeting CVE-2020-14882 and CVE-2020-14750.
 razureink/cve-2025-61882-oracle_ebs_rce_reproduction
CVE Reproduction: cve-2025-61882-oracle_ebs_rce_reproduction
 mindflarex/cve-2025-61882-poc
Exploit for CVE-2025-61882, a critical pre-auth RCE in Oracle E-Business Suite. Combines SSRF, CRLF injection, HTTP smuggling, and XSLT injection for…

 watchtowrlabs/watchtowr-vs-oracle-e-business-suite-cve-2025-61882
Generates detection artifacts for Oracle E-Business Suite CVE-2025-61882 by serving a reverse shell payload to verify pre-auth RCE.
 dxask88ma/weblogic-cve-2023-21839
Java-based exploit for CVE-2023-21839 targeting Oracle WebLogic Server versions 12.2.1.3.0 and 12.2.1.4.0 via LDAP injection for remote code…