
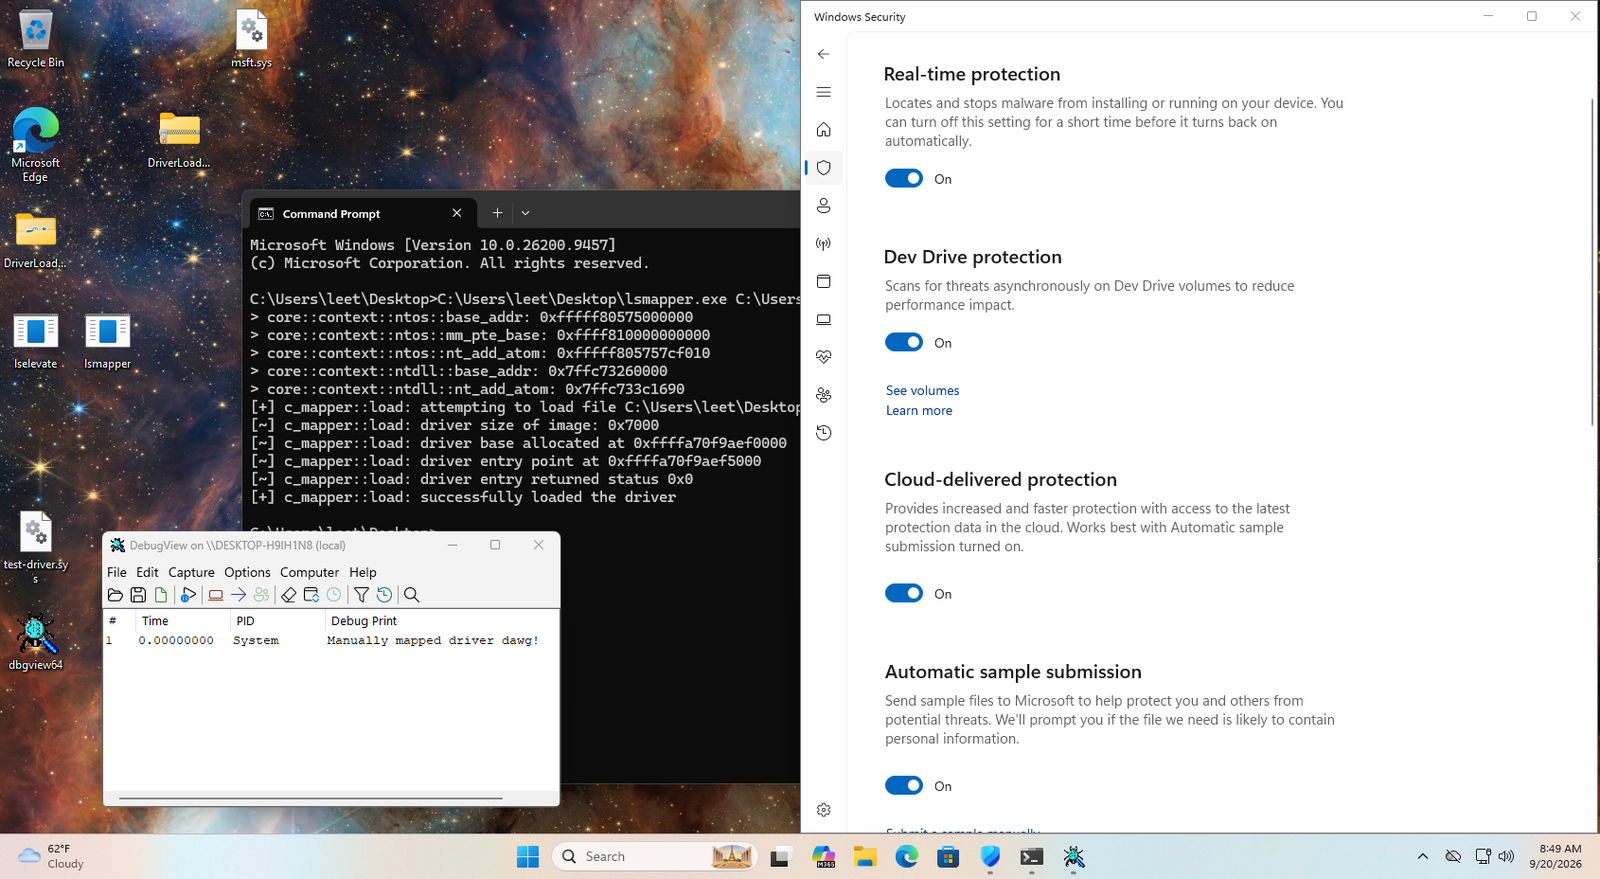
LocalStranger
 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
binary-exploitationexploit-frameworkspayload-development+3
42
nbs32k/localstrangerPoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
 antecursor/antecursor
Autonomous and modular system for network based information gathering and exploitation. WEB interface here: https://antecursor.fr/ More info…
 aircrack-ng/mdk4
IEEE 802.11 Wi-Fi testing tool for protocol weakness exploitation, including beacon flooding, deauthentication, packet fuzzing, and IDS evasion.…
 irsl/php-bypass-disable-functions
Demo project how to bypass the disable_functions security control of PHP on Linux
 beetlechunks/redsails
RedSails is a Python based post-exploitation project aimed at bypassing host based security monitoring and logging. DerbyCon 2017 Talk:…
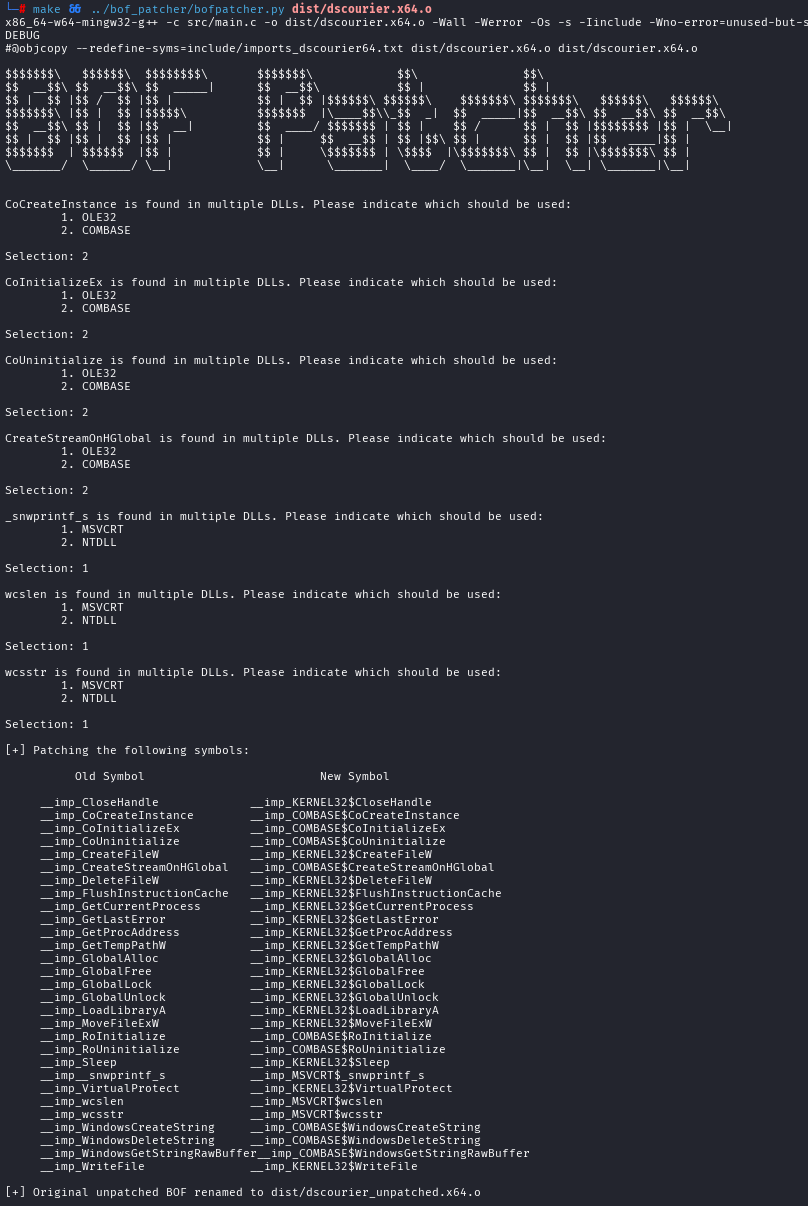 octoberfest7/dscourier_bof
BOF POC of the DSCourier project / invoking WinGet via COM
 tw1sm/pysqlrecon
Offensive MSSQL toolkit written in Python, based off SQLRecon
 yora1928/cve-2026-48908-by-yora
Passive security checker for CVE-2026-48908 affecting SP Page Builder.
 hackernese/sneakyexe
Automatic UAC-Bypassing for custom payloads during privilege escalation testing
 praneethnaidu1910-cmd/cve-2023-23397-purple-team
Purple team project exploiting CVE-2023-23397 Outlook NTLM leak with phishing delivery, plus Sigma/Wazuh detections mapped to MITRE ATT&CK for the…
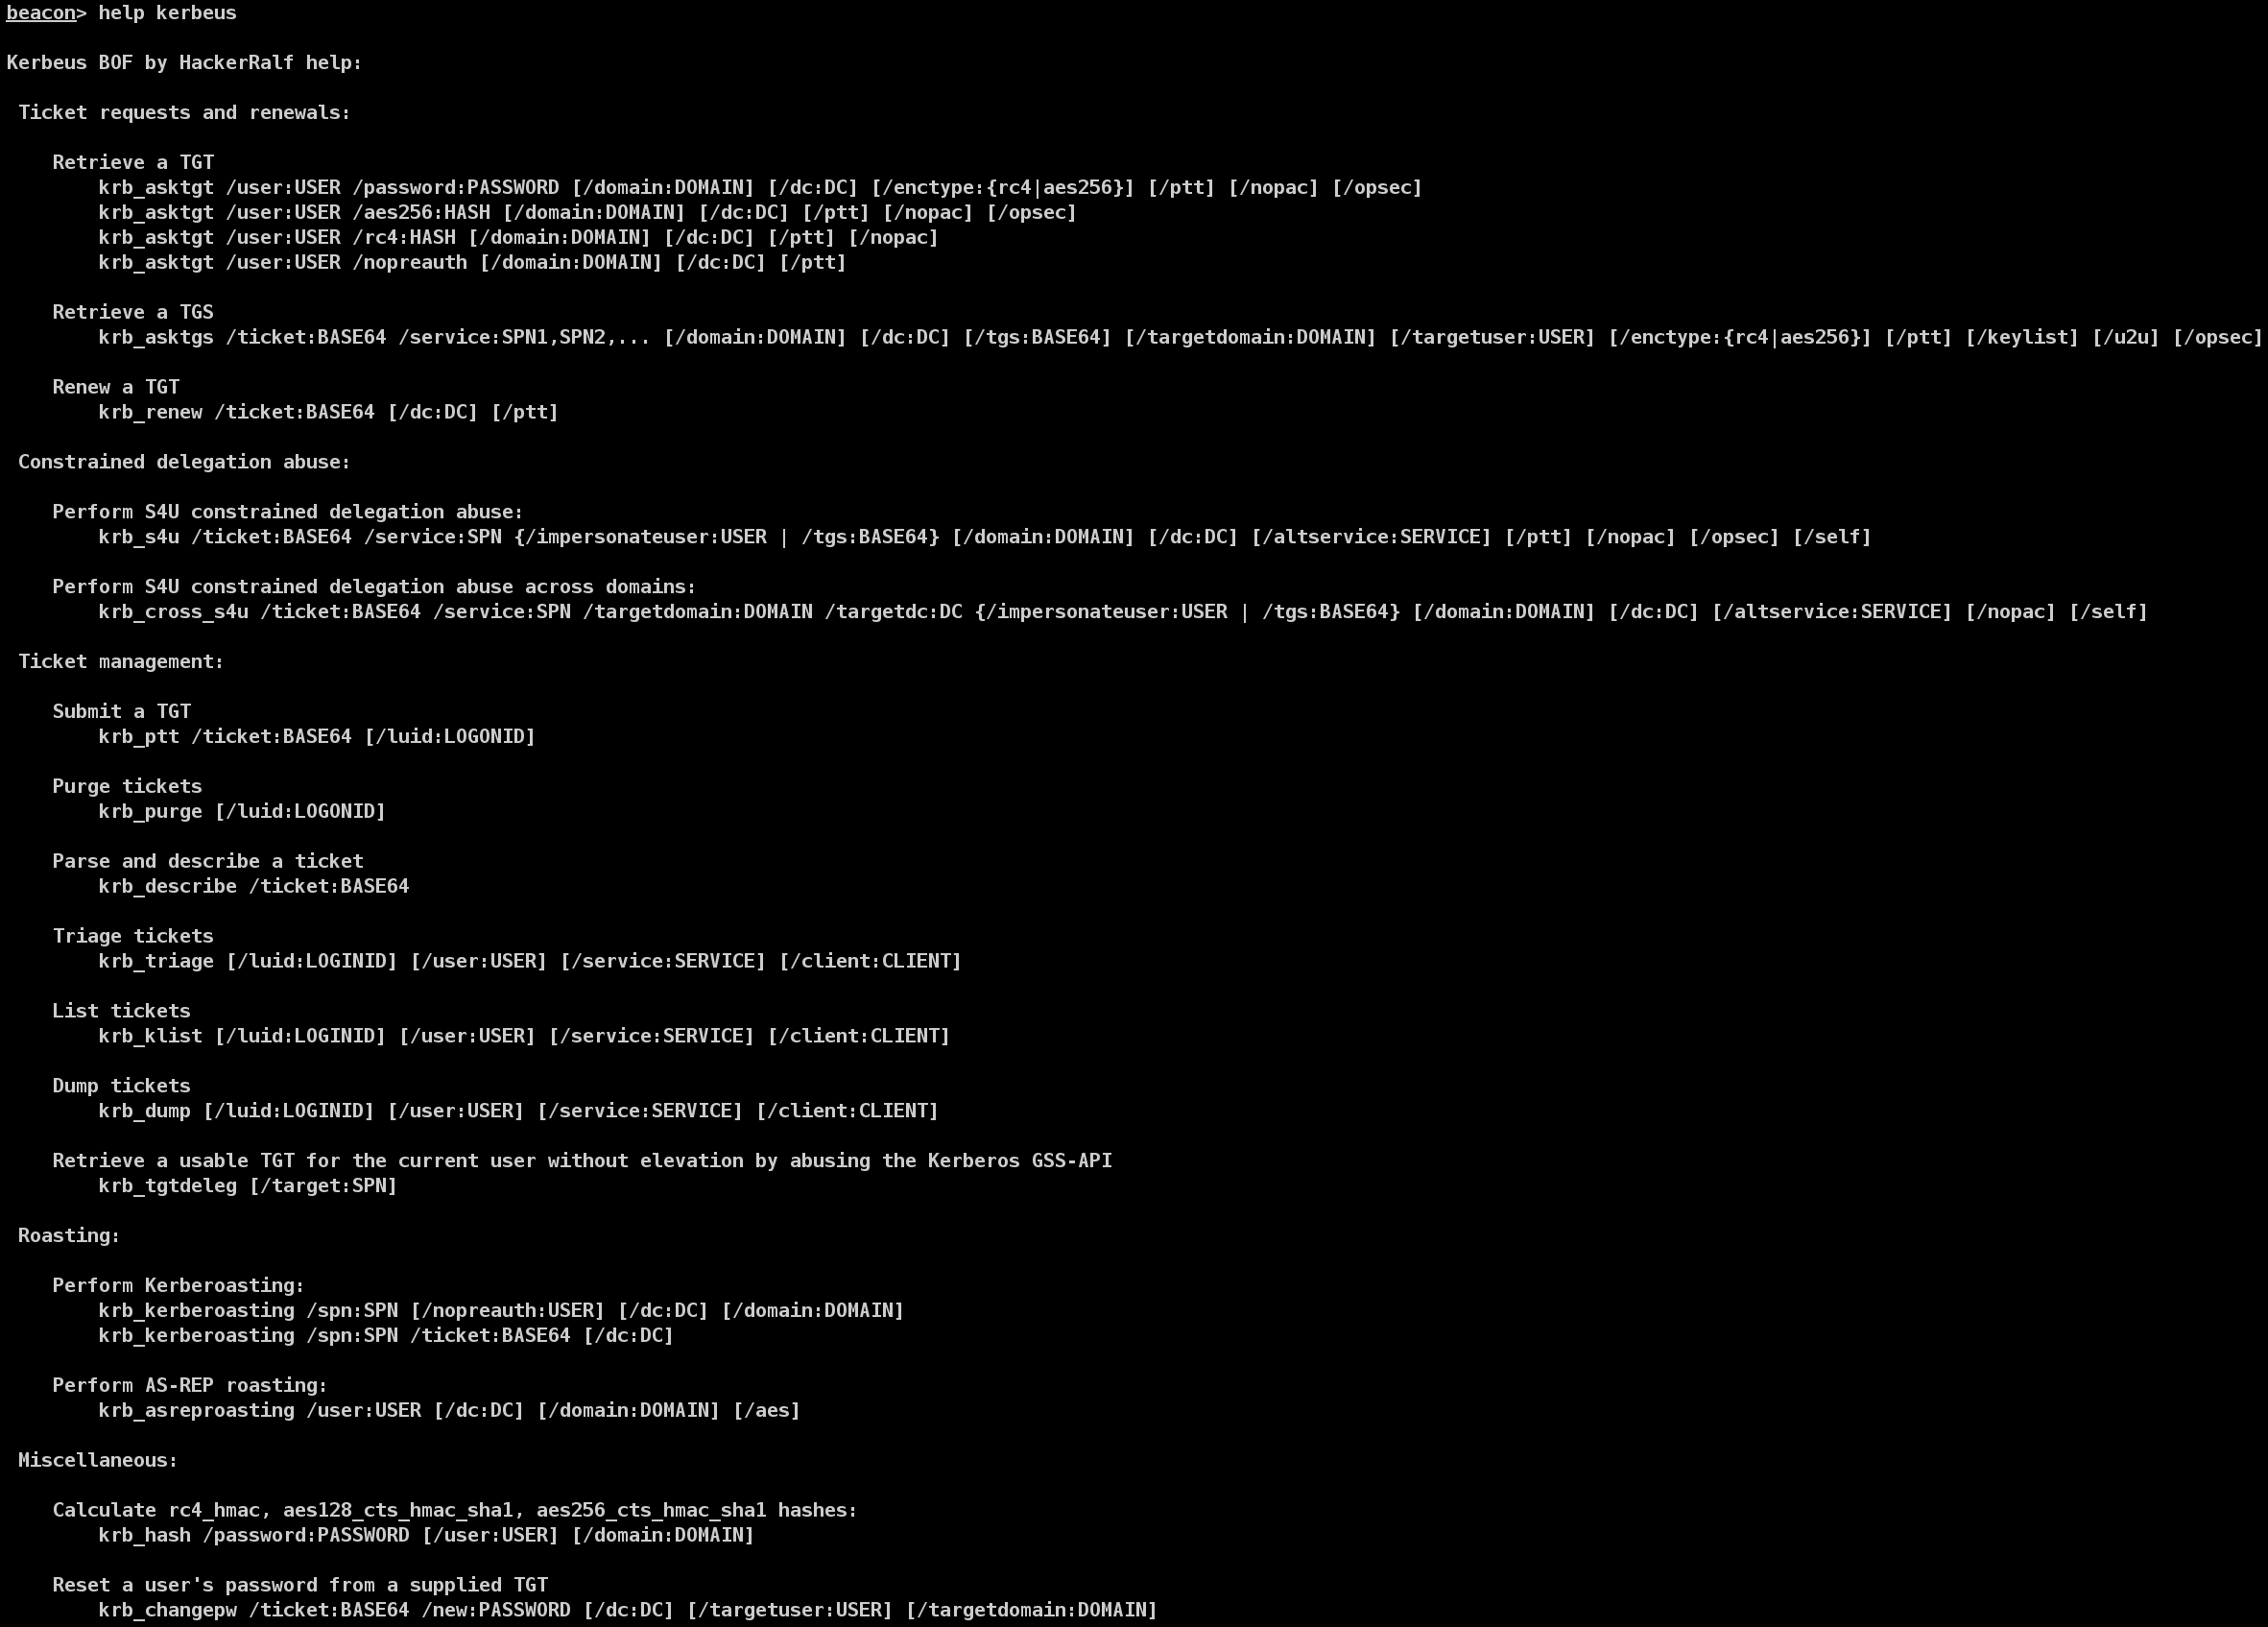 ralfhacker/kerbeus-bof
BOF for Kerberos abuse (an implementation of some important features of the Rubeus).
 zephrfish/autohoneypoc
AutoPoC Generator HoneyPoC
 monoxgas/koppeling
Adaptive DLL hijacking / dynamic export forwarding
 signorrayan/redteam_toolkit
Red Team Toolkit is an Open-Source Django Offensive Web-App which is keeping the useful offensive tools used in the red-teaming together.
 zux0x3a/0xsp-mongoose
a unique framework for cybersecurity simulation and red teaming operations, windows auditing for newer vulnerabilities, misconfigurations and…