
link
 postrequest/link
link is a command and control framework written in rust
command-and-controlexploit-frameworkspayload-development+2
postrequest/linklink is a command and control framework written in rust
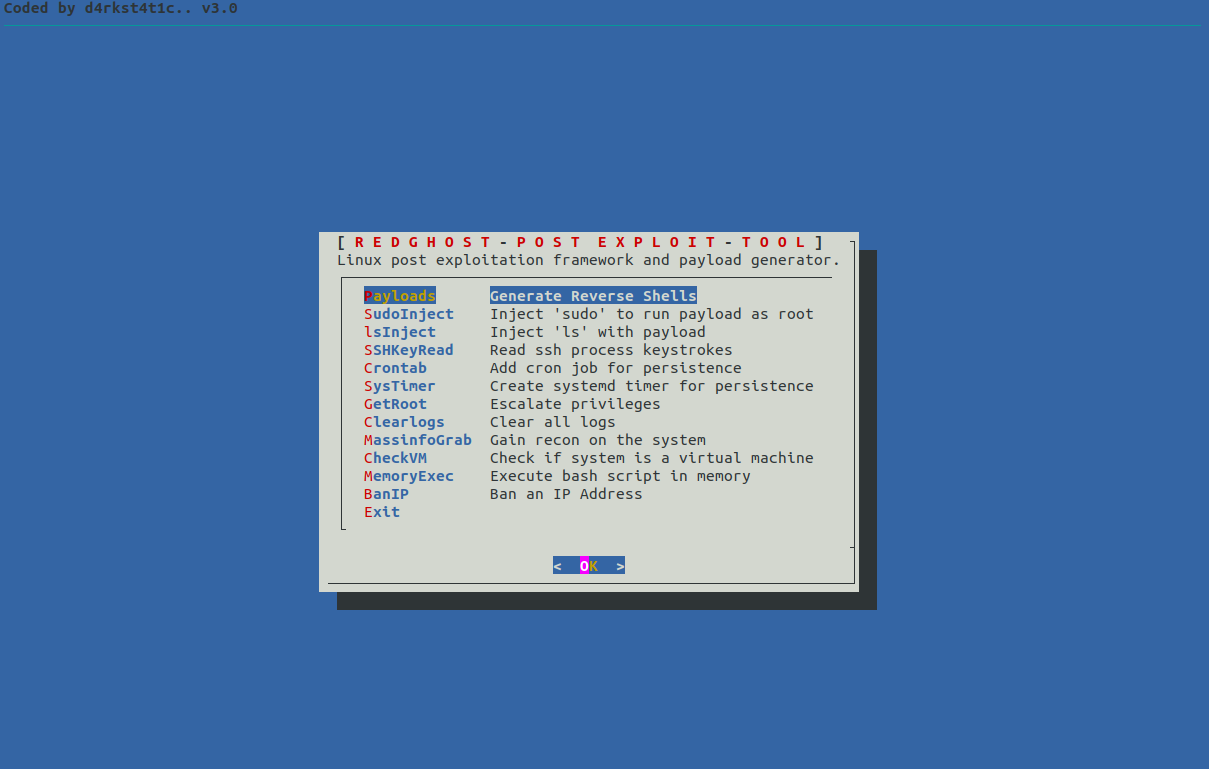 d4rk007/redghost
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 grines/scour
Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…
 erarnitox/malvexc2
A simple C2 Framework written in modern C++
 watersalesman/aura-botnet
A super portable botnet framework with a Django-based C2 server. The client is written in C++, with alternate clients written in Rust, Bash, and…
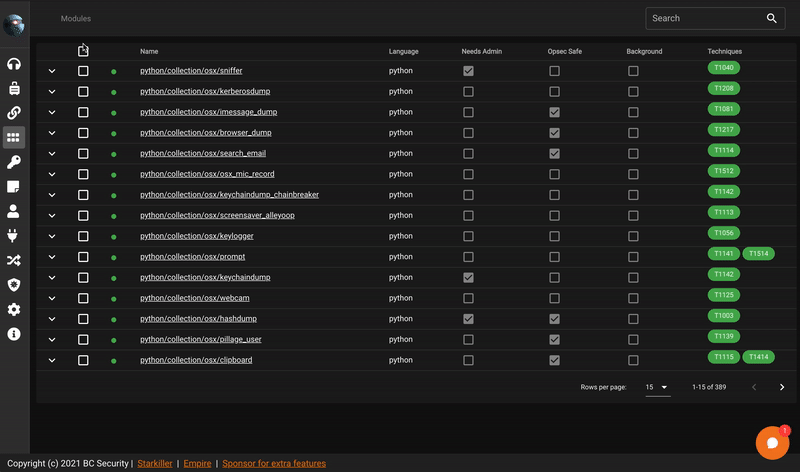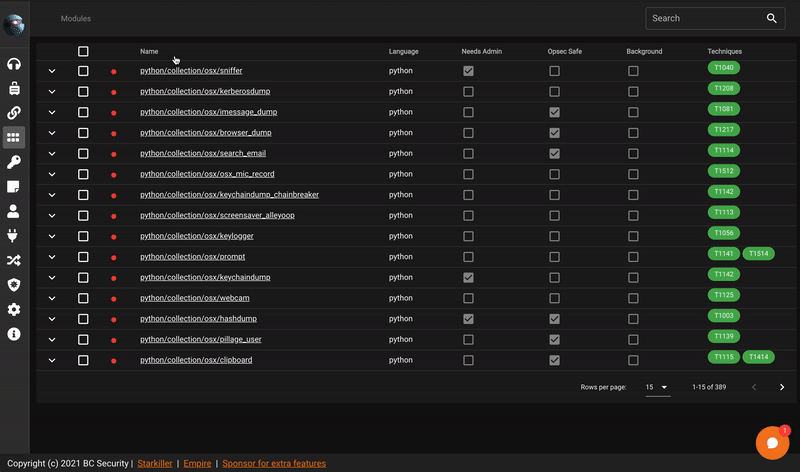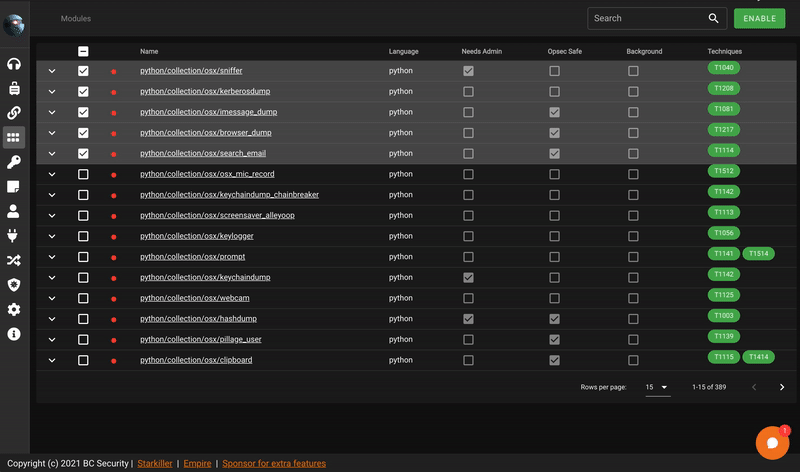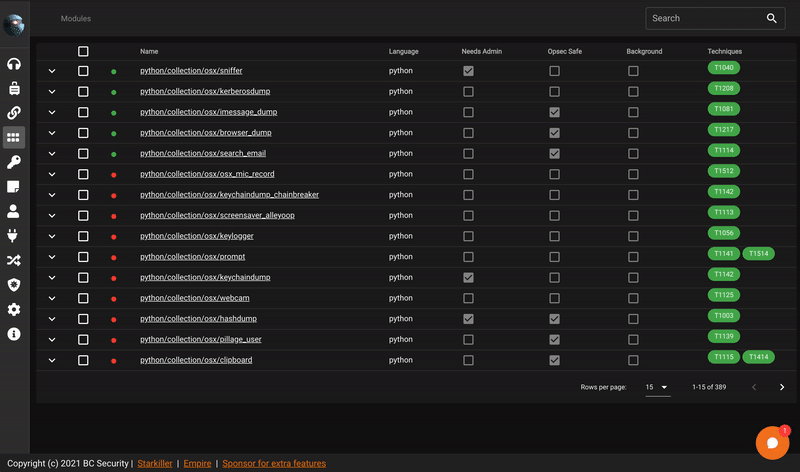 bc-security/starkiller
Starkiller is a Frontend for PowerShell Empire.
 p0cl4bs/wifipumpkin3
Powerful framework for rogue access point attack.
 dobin/antnium
A C2 framework for initial access in Go
 an00brektn/gopher47
A third-party Gopher Assassin for the Havoc Framework.
 cn33liz/p0wnedshell
PowerShell Runspace Post Exploitation Toolkit
 0xtriboulet/revenant
Revenant - A 3rd party agent for Havoc that demonstrates evasion techniques in the context of a C2 framework
 bashfuscator/bashfuscator
A fully configurable and extendable Bash obfuscation framework. This tool is intended to help both red team and blue team.
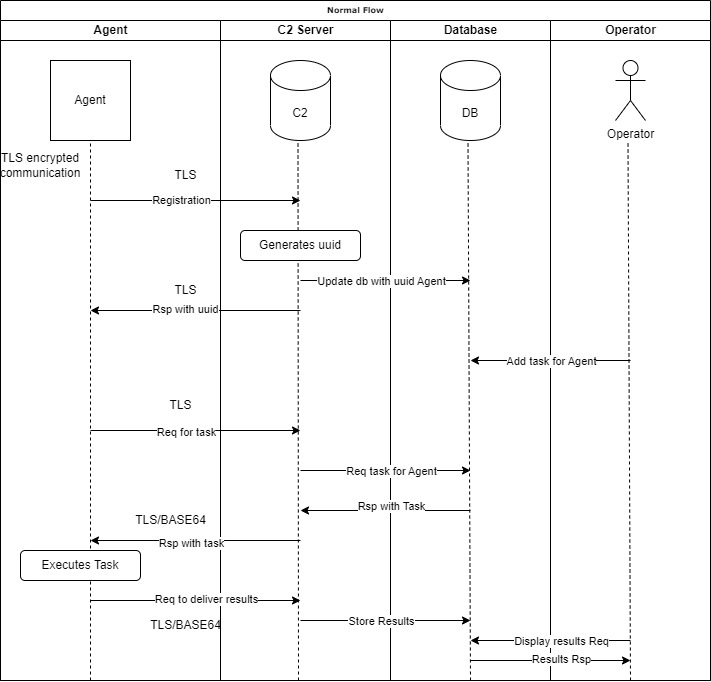 voukatas/commander
Python-based command and control framework with encrypted TLS communication, multiple agent support (Python/C), interactive sessions, file transfer,…
 trustedsec/tap
The TrustedSec Attack Platform is a reliable method for droppers on an infrastructure in order to ensure established connections to an organization.
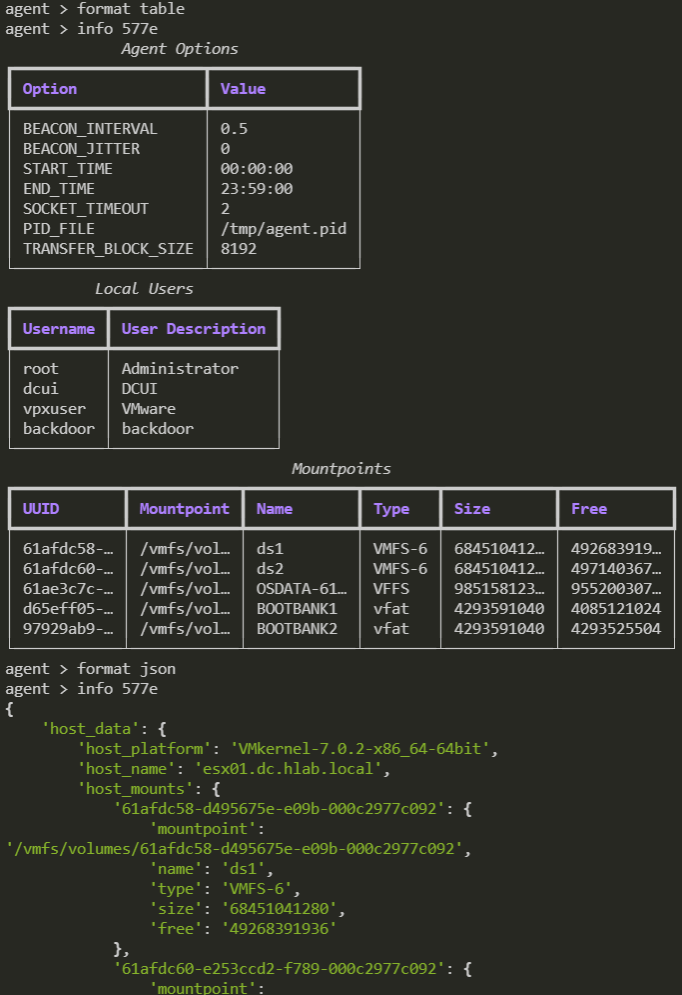 psmths/reave
WIP Post-exploitation framework tailored for hypervisors.
 mythicagents/thanatos
Mythic C2 agent targeting Linux and Windows hosts written in Rust