Purple-Team-Automation

Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.

Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.

Hunt down social media accounts by username across social networks

Intercepts and analyzes USB Mass Storage traffic at the block and file level, emulates USB devices, and supports custom Python stubs for security…

Offset Independent Credential Extraction Tool

AI harness for long-running code audits, web pentests, and bug bounty hunting, built around how real investigations fail: anchored hypotheses, false…

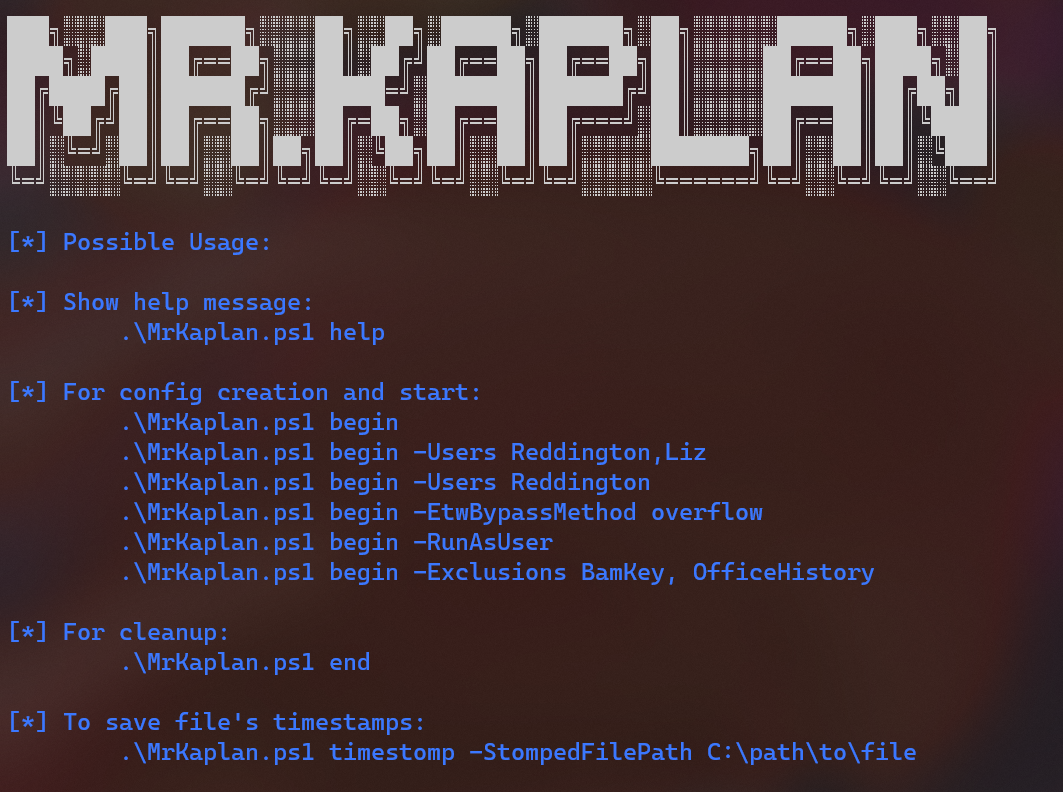
PowerShell tool for red teamers that clears execution evidence by stopping event logging, removing file and registry artifacts, and saving timestamps…

Powerglot encodes offensive powershell scripts using polyglots . Offensive security tool useful for stego-malware, privilege escalation, lateral…

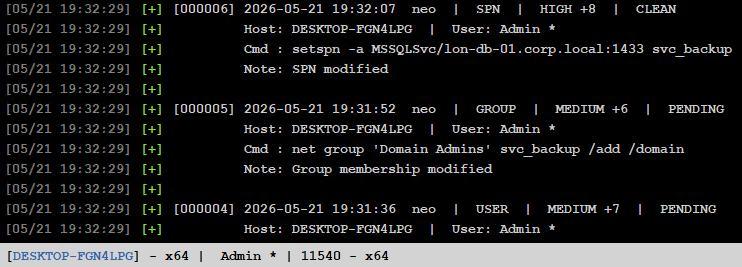
An aggressor script that tracks operational changes made during a red team engagement. Gives you a full audit trail of what was changed and what…

ShadowNet is an anonymous routing protocol that forces all connections (system-wide) to go through Tor while implementing Mixnet-like…

Anti Forensics Tool For Red Teamers, Used For Erasing Footprints In The Post Exploitation Phase.

This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…

Automated Adversary Emulation Platform

CredsHunter - Credential Hunting scripts for Windows and Linux OS

PowerShell toolkit for AMSI/Defender detection-boundary analysis and static malware triage maps byte offsets to detection triggers, plus YARA,…

Extract Windows credentials directly from VM memory snapshots and virtual disks

A network packet forensics tool for SSH

RedEye is a visual analytic tool supporting Red & Blue Team operations

Post-Exploitation EVTX Analyzer for BloodHound Mapping