
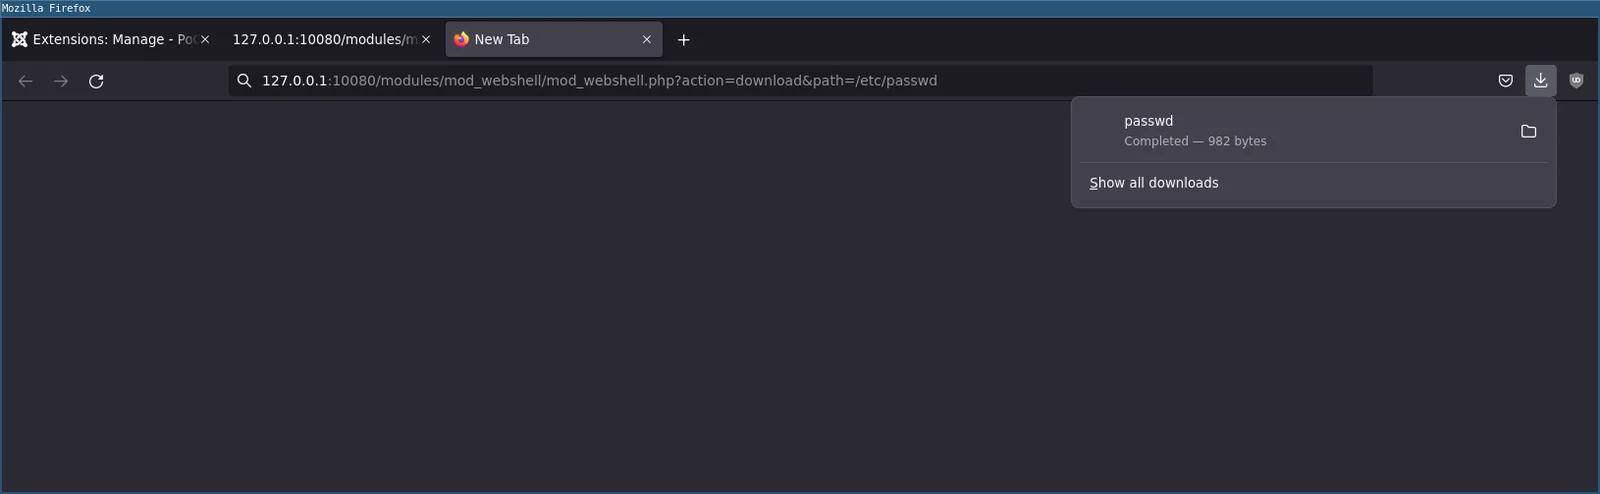
Joomla-webshell-plugin
 p0dalirius/joomla-webshell-plugin
A webshell plugin and interactive shell for pentesting a Joomla website.
command-and-controlexploitationpayload-development+6
62
p0dalirius/joomla-webshell-pluginA webshell plugin and interactive shell for pentesting a Joomla website.
 polosss/by-poloss..-..cve-2026-19125
Verified proof-of-concept exploiting the EthPress <= 2.3.5 unauthenticated authentication bypass, granting a WordPress administrator session via a…
 rajneeshkarya/cve-2025-32463
This is the exploit for the CVE-2025-32463
 ajnik/joomla-bruteforce
Python script that brute-forces Joomla administrator login credentials using wordlists, with proxy and verbose options for penetration testing.
 thoxy67/zig-pe
Reflective PE loader written in Zig. Loads and executes native and .NET PE files directly from memory.
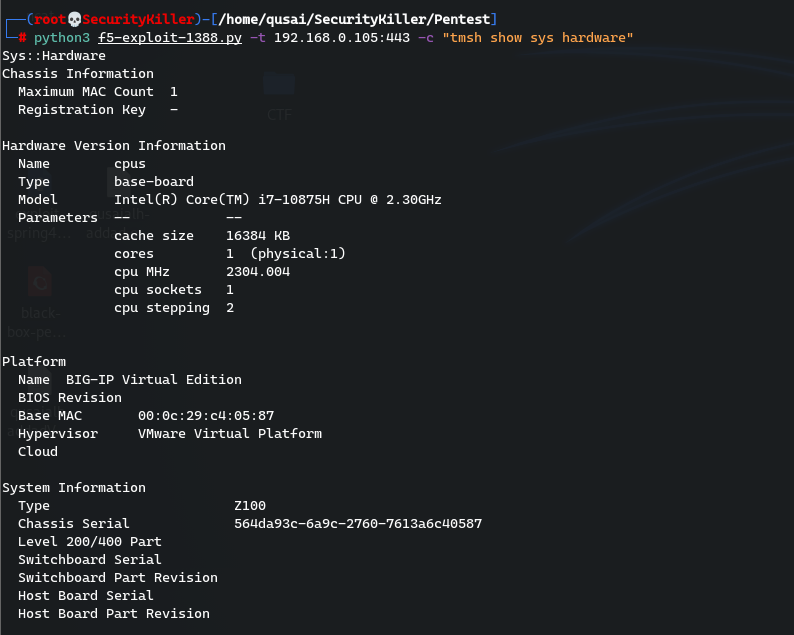 qusaialhaddad/f5-bigip-cve-2022-1388
Reverse Shell for CVE-2022-1388
 nmlz/cve-2023-35813_poc
Proof-of-concept exploit for CVE-2023-35813, a remote code execution vulnerability in Sitecore XP/XM via crafted XAML requests. Demonstrates…