
WinFlesher
 mindsflee/winflesher
Automated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…
configuration-auditinglateral-movementpenetration-testing+4
25
mindsflee/winflesherAutomated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…
 arcanum-sec/wraith
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
 nodauf/girsh
Automatically spawn a reverse shell fully interactive for Linux or Windows victim
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 xiaolichan/wmiexec-regout
Modify version of impacket wmiexec.py, get output(data,response) from registry, don't need SMB connection, also bypassing antivirus-software in…
 s4dp4nd4/frida-c2-mcp
Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
 neweracracker/loic
Deprecated - Low Orbit Ion Cannon - An open source network stress tool, written in C#. Based on Praetox's LOIC project. USE ON YOUR OWN RISK. WITHOUT…
 moscowchill/lstar-en
LSTAR - CobaltStrike Translated to EN
 aydinnyunus/keylogger
Get Keyboard,Mouse,ScreenShot,Microphone Inputs from Target Computer and Send to your Mail.
 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
 itm4n/pplcontrol
Windows tool to list, get, set, protect, and unprotect process protection levels (PP/L) for debugging, inspection, and privilege escalation.
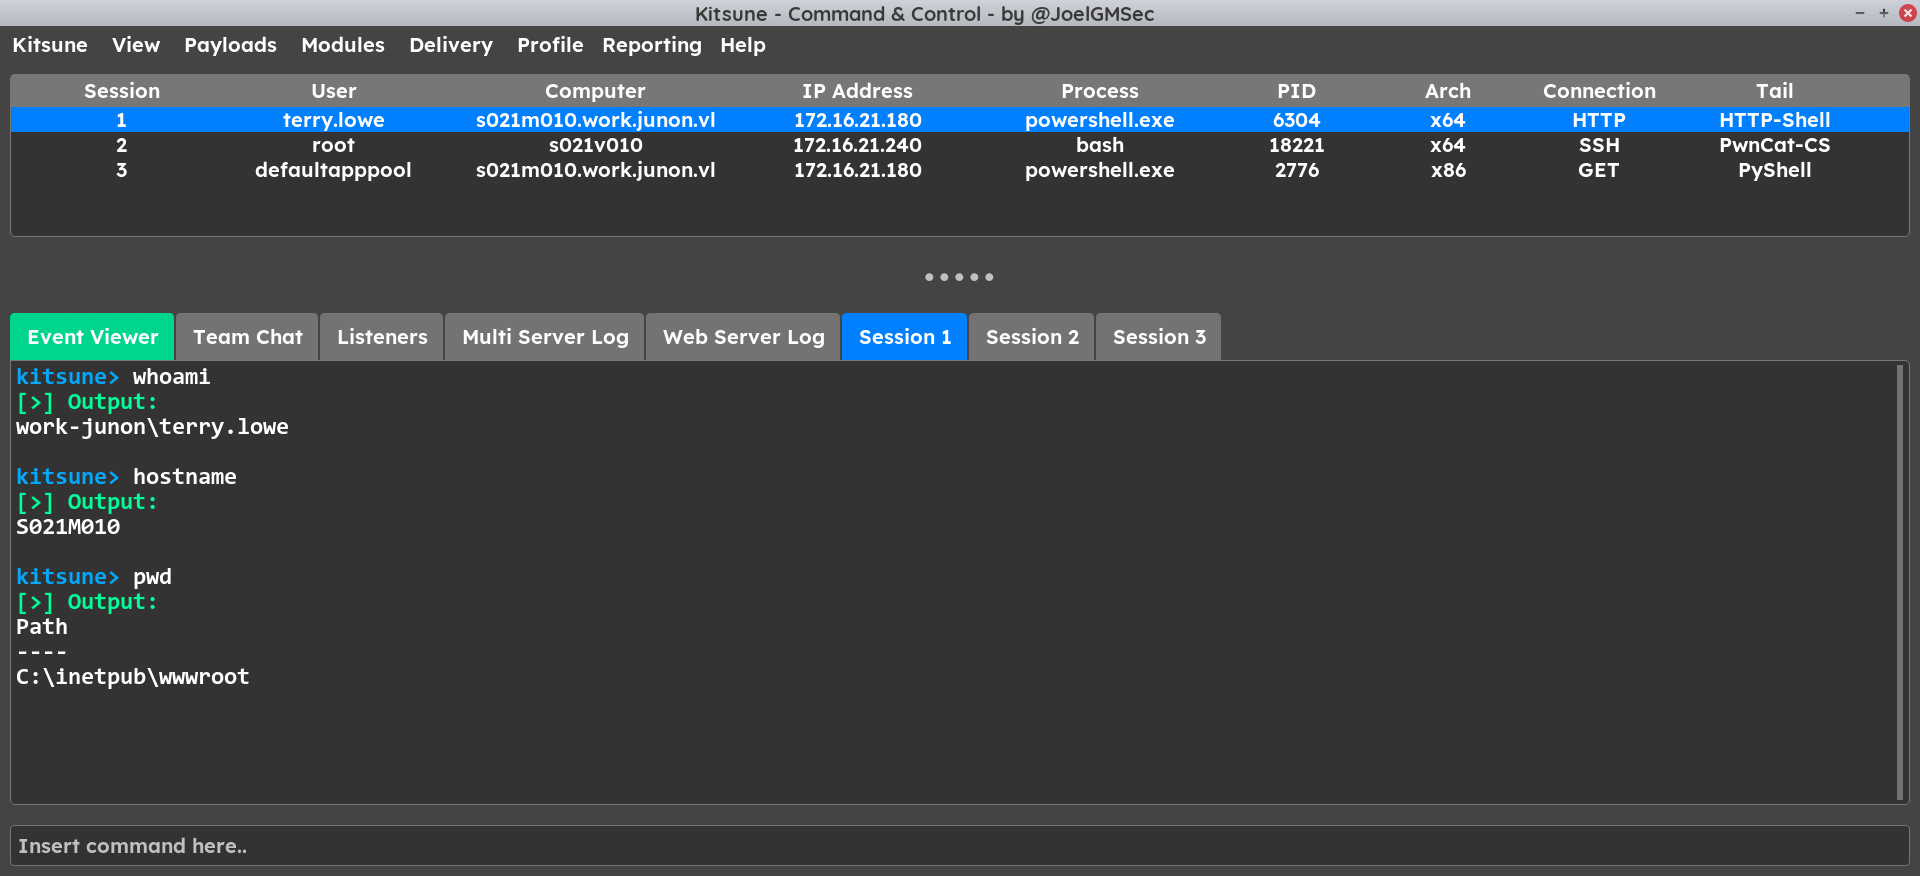 joelgmsec/kitsune
Polymorphic C2 framework with graphical interface, automatic reconnection, payload generation, and integrated hacking tools for red team operations…
 ixzodiak/cve-2025-8110
Gogs service Exploit and get the root user
 al-sultani/avideo3xploit
RCE exploit for AVideo < 8.9 (CVE-2020-23489 & CVE-2020-23490)
 sqldebugger/cve-2019-0708-tool
50 first stargazers will get get the tool via email
 ch4os1/cve-2024-4157-ssrf-rce-reverse-shell
Chaining Havoc C2 SSRF with RCE to get reverse shell on Havoc C2 Server.
 nate0634034090/nate158g-m-w-n-l-p-d-a-o-e
### This module requires Metasploit: https://metasploit.com/download# Current source: https://github.com/rapid7/metasploit-framework##class…
 0x00-0x00/cve-2015-3224
Modification of Metasploit module for RCE in Ruby-On-Rails Console CVE-2015-3224