Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
27 results
awesome-linux-attack-forensics-purplelabs preview

awesome-linux-attack-forensics-purplelabs

GitHubcr0nx/awesome-linux-attack-forensics-purplelabs

This page is a result of the ongoing hands-on research around advanced Linux attacks, detection and forensics techniques and tools.

container-securitycurated-resourcesdigital-forensics+8
342
3 years ago
emp3r0r preview

emp3r0r

GitHubjm33-m0/emp3r0r

Self‑healing Gossip Mesh C2 with Assisted Peer Discovery, Cross-Platform BOF Execution, and Scriptable Agents.

anti-botcommand-and-controlids-ips-evasion+10
1.8k2 days ago
Silverseal preview

Silverseal

GitHubidov31/silverseal

Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…

binary-exploitationexploitationmalware-analysis+4
1614 months ago
tor-rootkit preview

tor-rootkit

GitHubemcruise/tor-rootkit

A Python 3 standalone Windows 10 / Linux Rootkit using Tor.

command-and-controleducationpayload-generation+3
1843 years ago
azazel preview

azazel

GitHubchokepoint/azazel

Azazel is a userland rootkit based off of the original LD_PRELOAD technique from Jynx rootkit. It is more robust and has additional features, and…

educationpersistence-mechanismspost-exploitation+2
8106 years ago
Nidhogg preview

Nidhogg

GitHubidov31/nidhogg

Windows rootkit for Intel x64 with 25+ features, demonstrating rootkit techniques compatible with all Windows 10 and Windows 11 versions.

command-and-controlpayload-developmentprivilege-escalation+1
2.5k3 months ago
r77-rootkit preview

r77-rootkit

GitHubbytecode77/r77-rootkit

Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.

command-and-controldefensive-toolsids-ips-evasion+6
2.2k2 months ago
Diamorphine preview

Diamorphine

GitHubm0nad/diamorphine

LKM rootkit for Linux Kernels 2.6.x/3.x/4.x/5.x/6.x (x86/x86_64 and ARM64)

malware-analysispersistence-mechanismsprivilege-escalation+1
2.5k5 months ago
KSLDBYOVDARK preview

KSLDBYOVDARK

GitHubanylnk/ksldbyovdark

Exploits a KSLD anti-rootkit driver vulnerability (IOCTL 0x222044) to bypass PPL protection and access sensitive process memory, enabling local…

exploitationpenetration-testingpost-exploitation+3
415 months ago
project-rvbbit preview

project-rvbbit

GitHubbuter-chkalova/project-rvbbit

Educational Linux kernel rootkit PoC exploring DKOM, syscall hooking, stealth, observability and defensive detection

defensive-toolseducationmalware-analysis+3
334 days ago
talkingBen preview

talkingBen

GitHubm4rm0k/talkingben

UEFI rootkit under development focusing on privilege escalation, C2 integration, and anti-EDR/AV evasion for real-world malware deployment.

command-and-controlexploitationmalware-analysis+4
11 months ago
IIS-Backdoor preview

IIS-Backdoor

GitHubnu11secur1ty/iis-backdoor

Stealthy IIS backdoor using hidden ISAPI filter for persistent remote access, data exfiltration, and on-the-fly exploit injection via custom HTTP…

command-and-controlexploitationids-ips-evasion+4
346 years ago
CallMeWin32kDriver preview

CallMeWin32kDriver

GitHubgmh5225/callmewin32kdriver

Load your driver like win32k.sys

adversarial-attackids-ips-evasionpost-exploitation+1
2584 years ago
Kernel-Process-Hollowing preview
Archived

Kernel-Process-Hollowing

GitHubxaff-xaff/kernel-process-hollowing

Windows x64 kernel mode rootkit process hollowing POC.

ids-ips-evasionpayload-developmentpost-exploitation+1
1933 years ago
RootKit preview

RootKit

GitHubasekon/rootkit

A rootkit for ubuntu-16.04.6 (Linux 4.4). Can hide a process, give root access and hide itself

ids-ips-evasionpersistence-mechanismspost-exploitation+2
47 years ago
Cronos-Rootkit preview
Archived

Cronos-Rootkit

GitHubxaff-xaff/cronos-rootkit

Cronos is Windows 10/11 x64 ring 0 rootkit. Cronos is able to hide processes, protect and elevate them with token manipulation.

ids-ips-evasionpersistence-mechanismspost-exploitation+2
9444 years ago
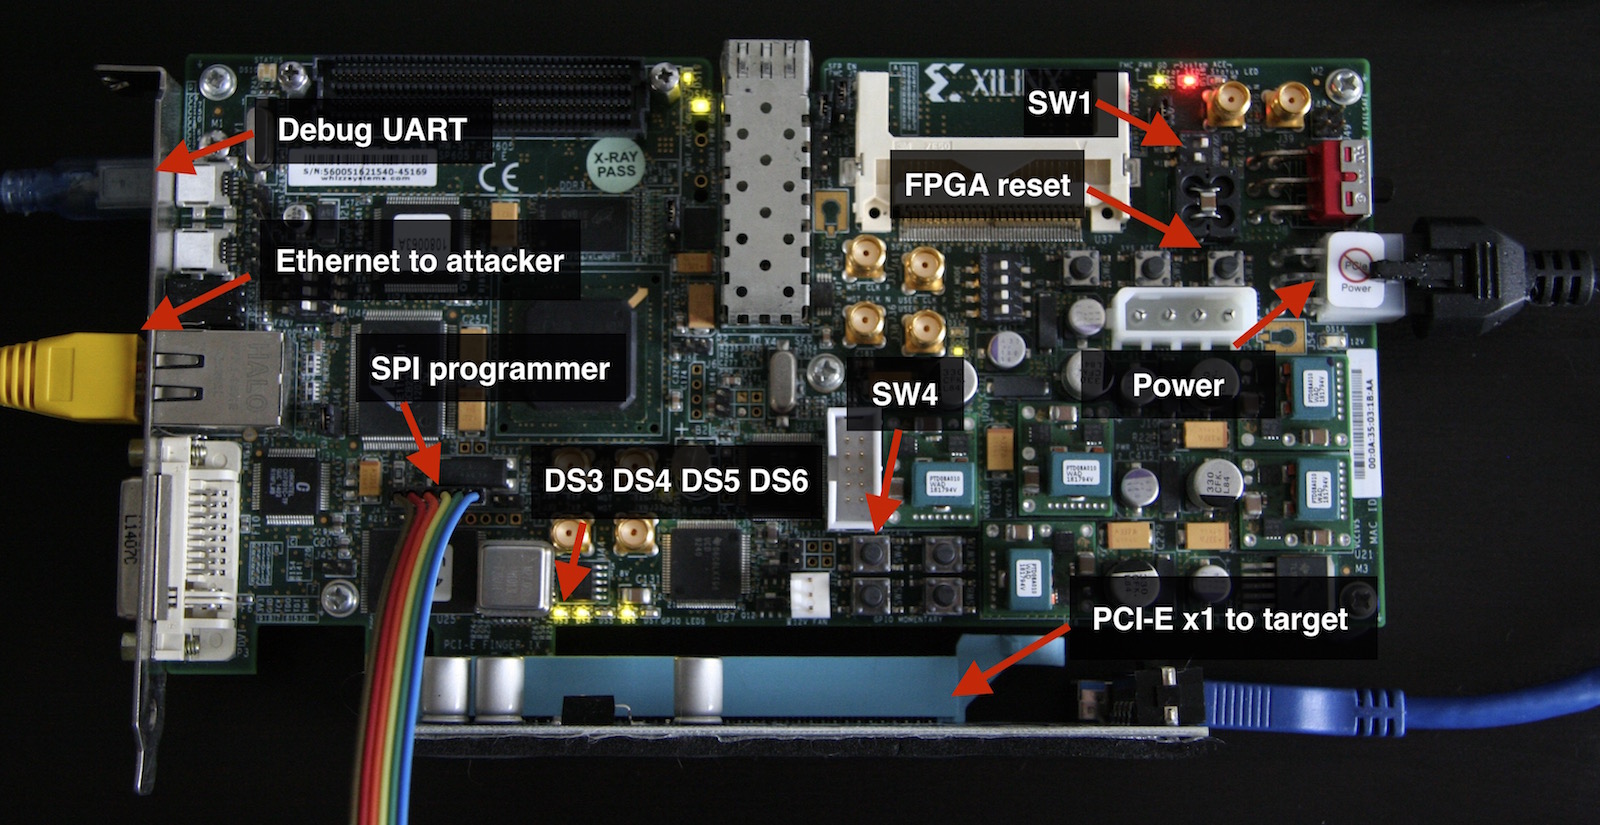
s6_pcie_microblaze preview

s6_pcie_microblaze

GitHubcr4sh/s6_pcie_microblaze

PCI Express DIY hacking toolkit for Xilinx SP605. This repository is also home of Hyper-V Backdoor and Boot Backdoor, check readme for links and info

command-and-controldata-exfiltrationexploitation+4
8886 months ago
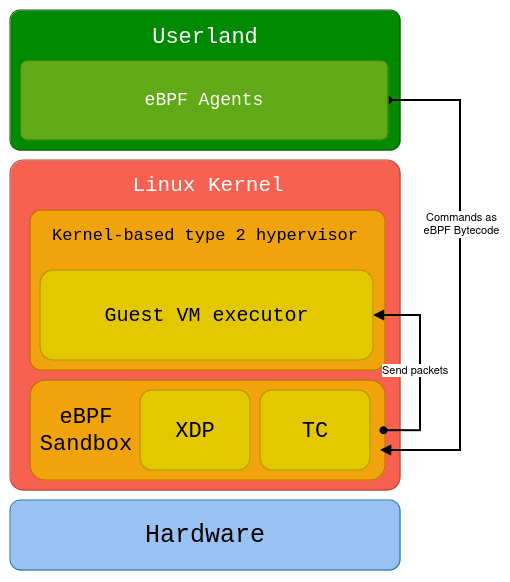
blackpill preview
Archived

blackpill

GitHubshard77/blackpill

A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs

binary-exploitationcommand-and-controlids-ips-evasion+7
3386 months ago
Previous12Next