
cve-2024-24919
 satchhacker/cve-2024-24919
Shell script that tests for CVE-2024-24919 by sending curl requests to specified IPs/domains, intended for educational vulnerability assessment.
educationexploitationreconnaissance+2
satchhacker/cve-2024-24919Shell script that tests for CVE-2024-24919 by sending curl requests to specified IPs/domains, intended for educational vulnerability assessment.
 graphite-org/cve-2024-4577
Shell script to scan domains for CVE-2024-4577 PHP remote code execution vulnerability via crafted POST requests, exporting vulnerable targets for…
 ashwani95/cve-2024-3094
Shell script to detect if the ssh binary is likely vulnerable to CVE-2024-3094, without requiring hexdump.
 kostas-pa/lfitester
Python3 tool that detects and exploits Local File Inclusion vulnerabilities, with crawling, path traversal and filter bypass payloads, and automated…
 blackmarketer/cve-2020-13942
Shell script to exploit CVE-2020-13942 on web targets, with pre-scanning via httpx or httprob and batch processing from a target list.
 epinna/weevely3
Weaponized web shell
 robotshell/magicrecon
MagicRecon is a powerful shell script to maximize the recon and data collection process of an objective and finding common vulnerabilities, all this…
 mr-rizwan-syed/chomtesh
CHOMTE.SH is a powerful shell script designed to automate reconnaissance tasks during penetration testing. It utilizes various Go-based tools to…
 lager1/cve-2023-35078
Shell script to check Ivanti EPMM (MobileIron Core) instances for CVE-2023-35078 remote unauthenticated API access vulnerability, with Shodan dorks…
 murrez/cve-2026-94132
Python check/exploit PoC for CVE-2026-94132: detects AcyMailing for Joomla versions, probes the media/com_acym/upload directory, and verifies…
 iveresk/cve-2022-1388-1veresk
Simple shell script for the exploit
 eagle-nett/react2shell-poc-cve-2025-55182
Proof-of-concept exploit for CVE-2025-55182 (React2Shell) RCE vulnerability in React Server Components. Includes a scanner for vulnerable hosts and a…
 prodrious/cve-2020-13942
Shell script to exploit CVE-2020-13942, a remote code execution vulnerability in Apache Unomi, with pre-scanning via httpx or httprob.
 j4f9s5d2q7/cve-2023-43208-mirthconnect
Shell script to identify and exploit CVE-2023-43208, an unauthenticated remote code execution vulnerability in NextGen Mirth Connect before version…
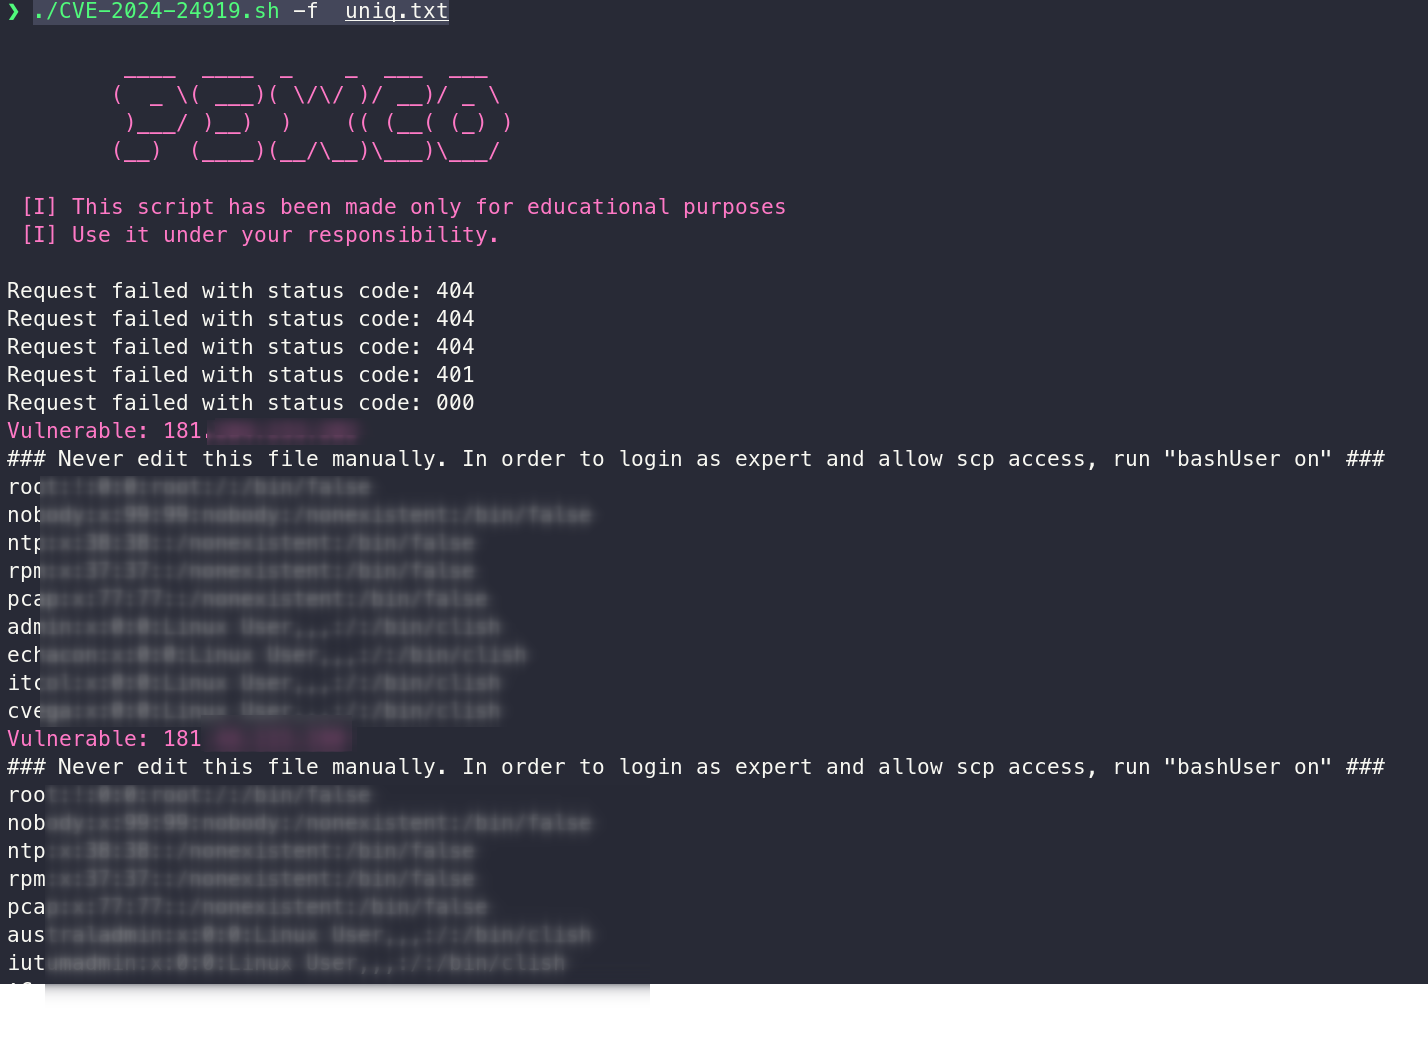 p3wc0/cve-2024-24919
Shell script to exploit CVE-2024-24919, enabling path traversal file retrieval from Check Point Security Gateways. Supports single IP and batch…
 phirojshah/cve-2024-4577
Proof-of-concept exploit for PHP CGI argument injection (CVE-2024-4577) enabling remote code execution on vulnerable Windows servers with scanning…
 stevemcilwain/quiver
Quiver is the tool to manage all of your tools for bug bounty hunting and penetration testing.
 nccgroup/autopwn
Specify targets and run sets of tools against them