
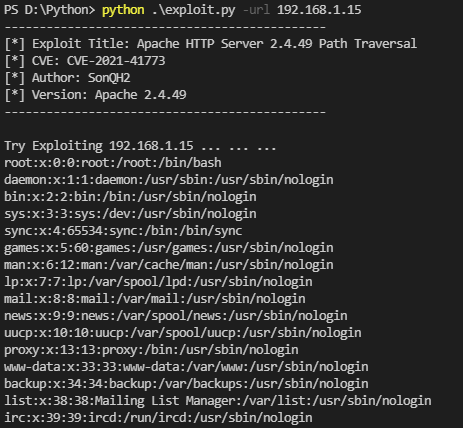
CVE-2021-41773
 zer0qs/cve-2021-41773
Exploit script for CVE-2021-41773 (Apache Path Traversal) with Docker setup and multi-target scanning via URL or list.
exploitationpenetration-testingreconnaissance+2
zer0qs/cve-2021-41773Exploit script for CVE-2021-41773 (Apache Path Traversal) with Docker setup and multi-target scanning via URL or list.
 foxvr-sudo/bug-bounty-arsenal-v.3
Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…

 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
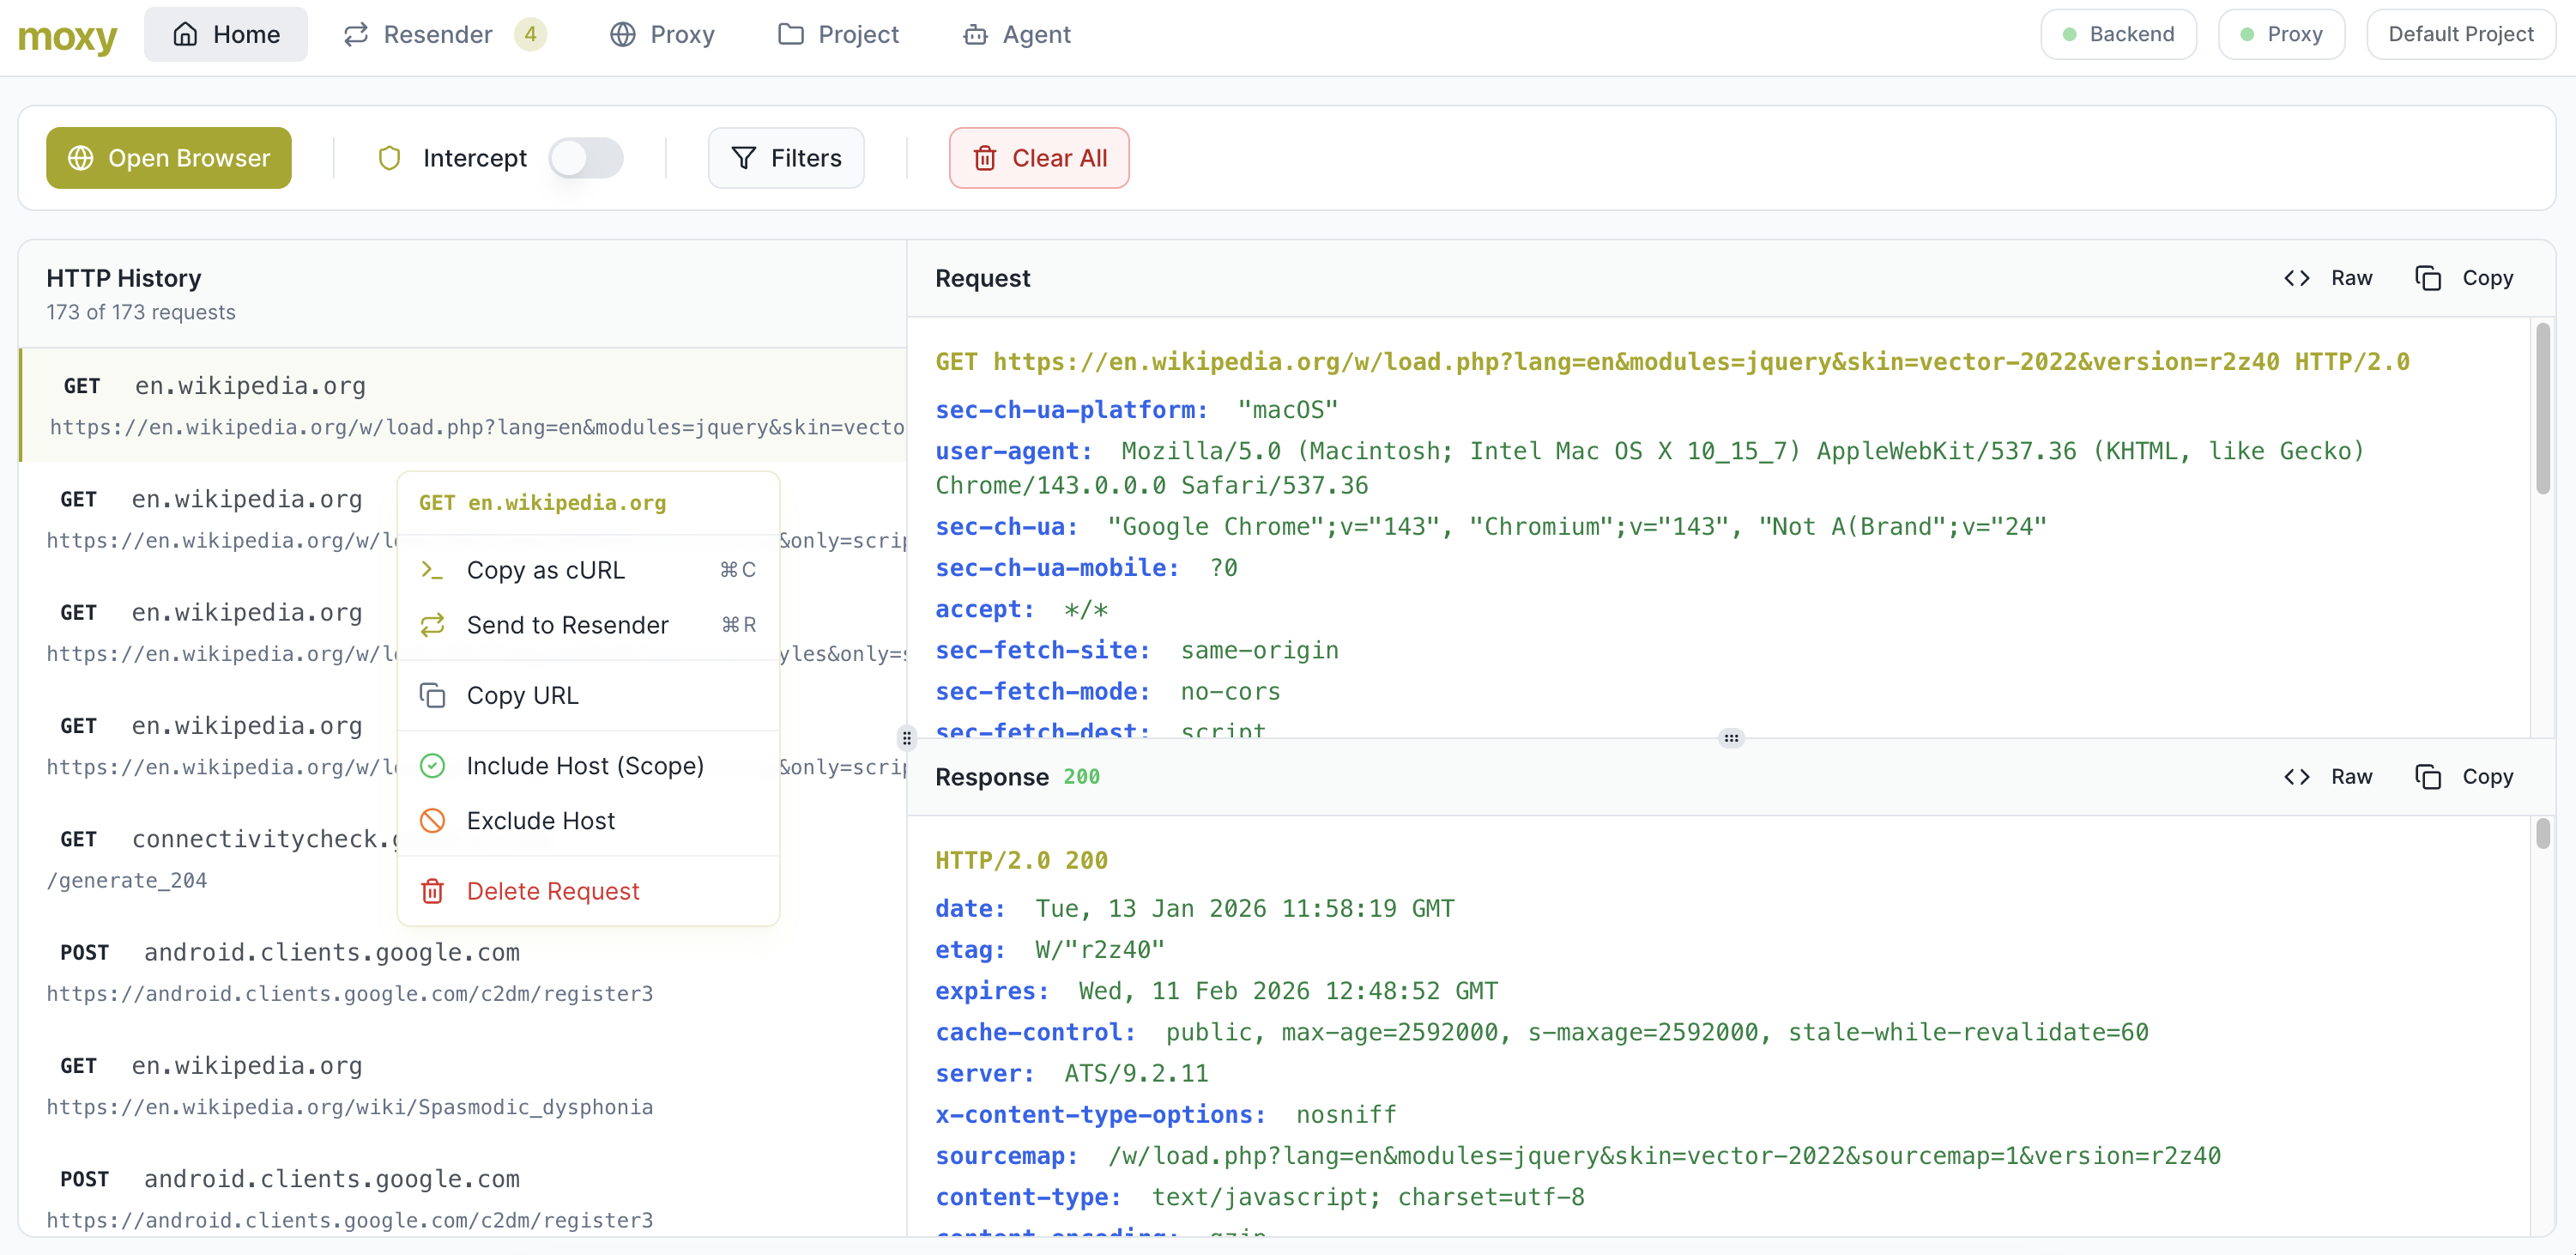 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
 dylvie/cve-2026-30824-flowise-nvidia-nim-authentication
A proof-of-concept exploit for **CVE-2026-30824**, a critical authentication bypass vulnerability in Flowise that exposes NVIDIA NIM API endpoints…
 gsmith257-cyber/graphcrawler
GraphQL automated security testing toolkit
 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.

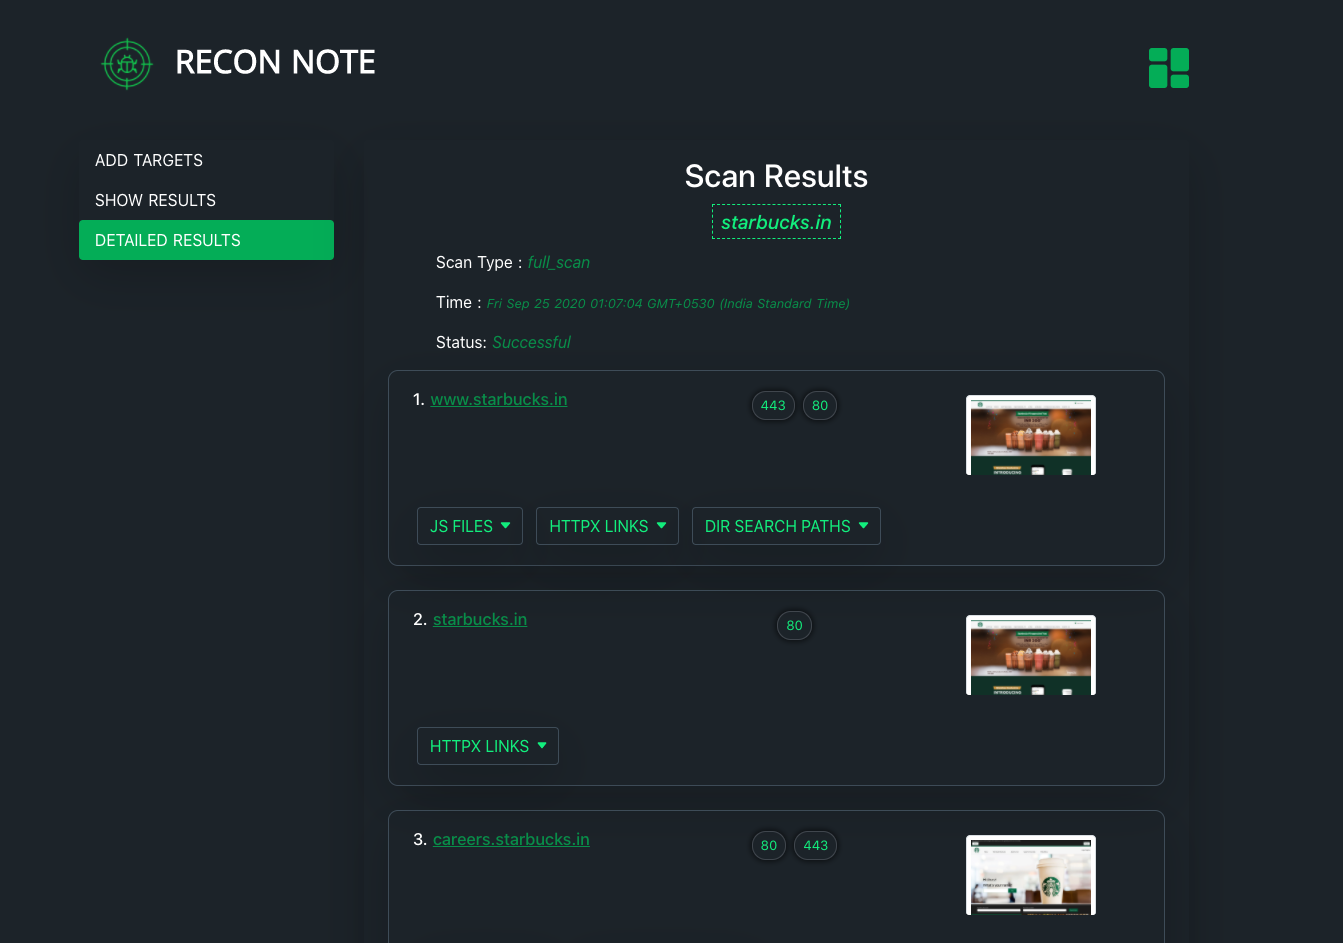 0xdekster/reconnote
Web Application Security Automation Framework which recons the target for various assets to maximize the attack surface for security professionals &…

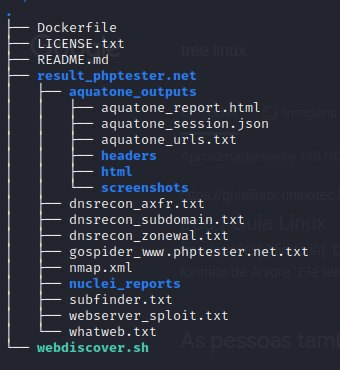 v1n1v131r4/webdiscover
The purpose of this script is to automate the web enumeration process and search for exploits
 gmh5225/disclosure-check
Tool to identify the best mechanisms for privately disclosing a security vulnerability for a package/project.
 nccgroup/go-pillage-registries
Pentester-focused Docker registry tool to enumerate and pull images
 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
 bishopfox/cve-2026-34908-check
Safely detect whether a UniFi OS Server is vulnerable to CVE-2026-34908
 oscerd/cve-2026-64640
Reproducer for CVE-2026-64640 — Apache Polaris Iceberg REST register/register-view vends storage credentials and reads an attacker-chosen metadata…