
RCE-CVE-2025-32710
 sincan2/rce-cve-2025-32710
Windows Remote Desktop Services Vulnerability Allows Remote Code Execution
exploitationpayload-generationpenetration-testing+6
5
sincan2/rce-cve-2025-32710Windows Remote Desktop Services Vulnerability Allows Remote Code Execution
 kienquoc102/cve-2017-8225
Exploit tool for CVE-2017-8225 targeting IP cameras. Scans for vulnerable devices and performs credential brute-forcing to gain unauthorized access.
 suriyaboon/hackthebox-facts
HTB Facts is a Easy Linux box featuring Camaleon CMS and MinIO. Gain admin access via open registration and a mass assignment vulnerability, then…
 nyxrecon/sudo-agent-ctf-
Write-up do Sudo Agent CTF (TryHackMe), com enumeração, exploração web, esteganografia, SSH e privilege escalation via CVE-2019-14287.
 adfortunato/metasploitable3-pentest-writeup
Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
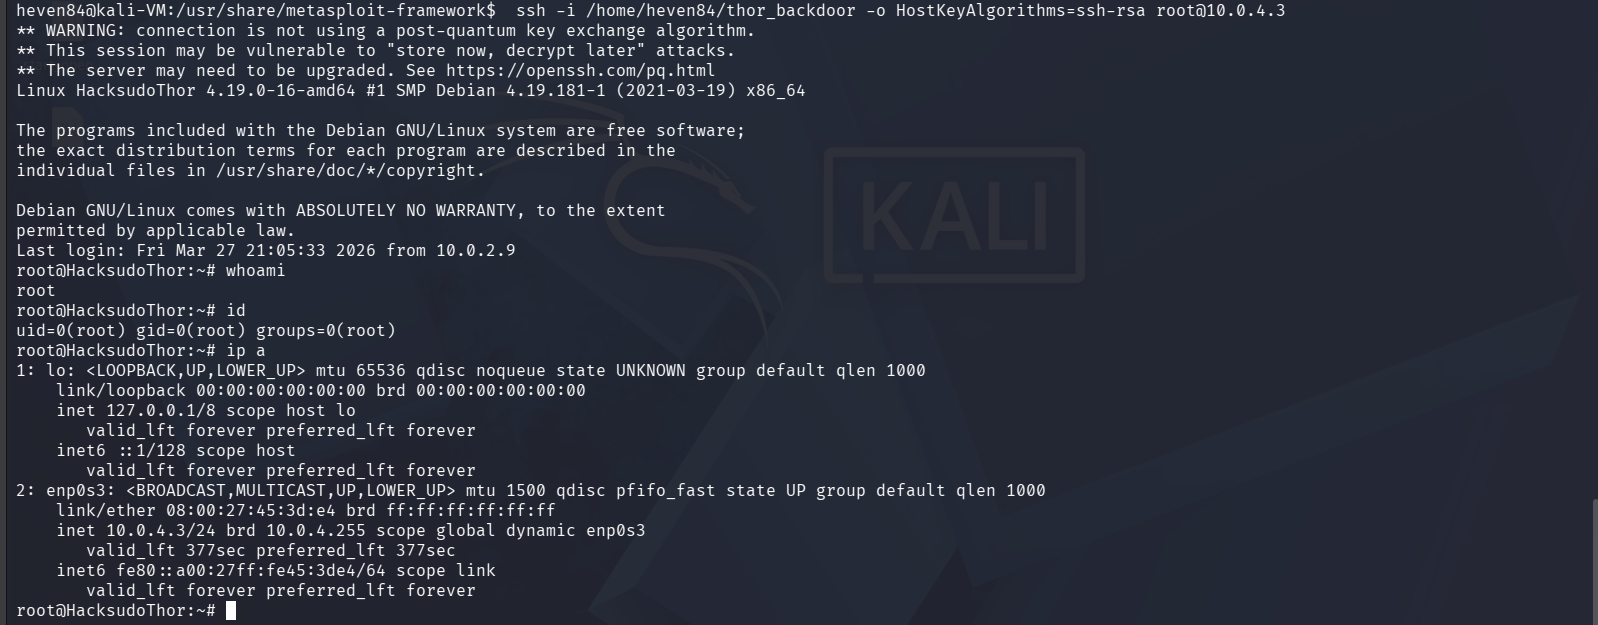 heventafese/penetration-testing-walkthrough-hacksudo-thor
Black-box penetration test against HackSudo Thor : CVE-2014-6271 Shellshock RCE through Apache mod_cgi, chained with sudo misconfiguration and bash…
 r3fr4kt/shocker-tjnull-oscp-
Structured HTB walkthrough demonstrating Shellshock (CVE-2014-6271) exploitation via CGI directory fuzzing and privilege escalation through…
 paulameg/simplectf-thm-walkthrough
First CTF successfully completed! This repo documents my walkthrough of TryHackMe's Simple CTF. It covers network reconnaissance (Nmap), web…
 rxerium/cve-2024-12084
A heap-based buffer overflow flaw was found in the rsync daemon. This issue is due to improper handling of attacker-controlled checksum lengths…
 edsonjt81/cve-2019-14287-
Shell script to detect and exploit CVE-2019-14287 sudo privilege bypass vulnerability, with standalone or scanner-integrated enumeration mode.
 te-k/harpoon
CLI tool for open source and threat intelligence
 franc-pentest/ldeep
In-depth ldap enumeration utility
 neffisback/wsuks
Automating the MITM attack on WSUS
 ginjachris/pentmenu
A bash script for recon and DOS attacks
 alienwhatever/admin-scanner
This tool is design to find admin panel of any website by using custom wordlist or default wordlist easily and allow you to find admin panel trough a…
 nccgroup/chuckle
An automated SMB relay exploitation script.
 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
 adityabhatt3010/room-walkthrough-billing
A detailed walkthrough of Billing room exploiting CVE-2023-30258 and escalating via fail2ban misconfig