
htb-ctf-walkthroughs
 rootsecnz/htb-ctf-walkthroughs
Walkthroughs for Capture the Flag challenges on the HTB Cybersecurity Platform.
ctfeducationexploitation+6
rootsecnz/htb-ctf-walkthroughsWalkthroughs for Capture the Flag challenges on the HTB Cybersecurity Platform.
 foxvr-sudo/bug-bounty-arsenal-v.3
Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…
 taksec/google-dorks-bug-bounty
A list of Google Dorks for Bug Bounty, Web Application Security, and Pentesting
 spinkham/skipfish
Web application security scanner created by lcamtuf for google - Unofficial Mirror
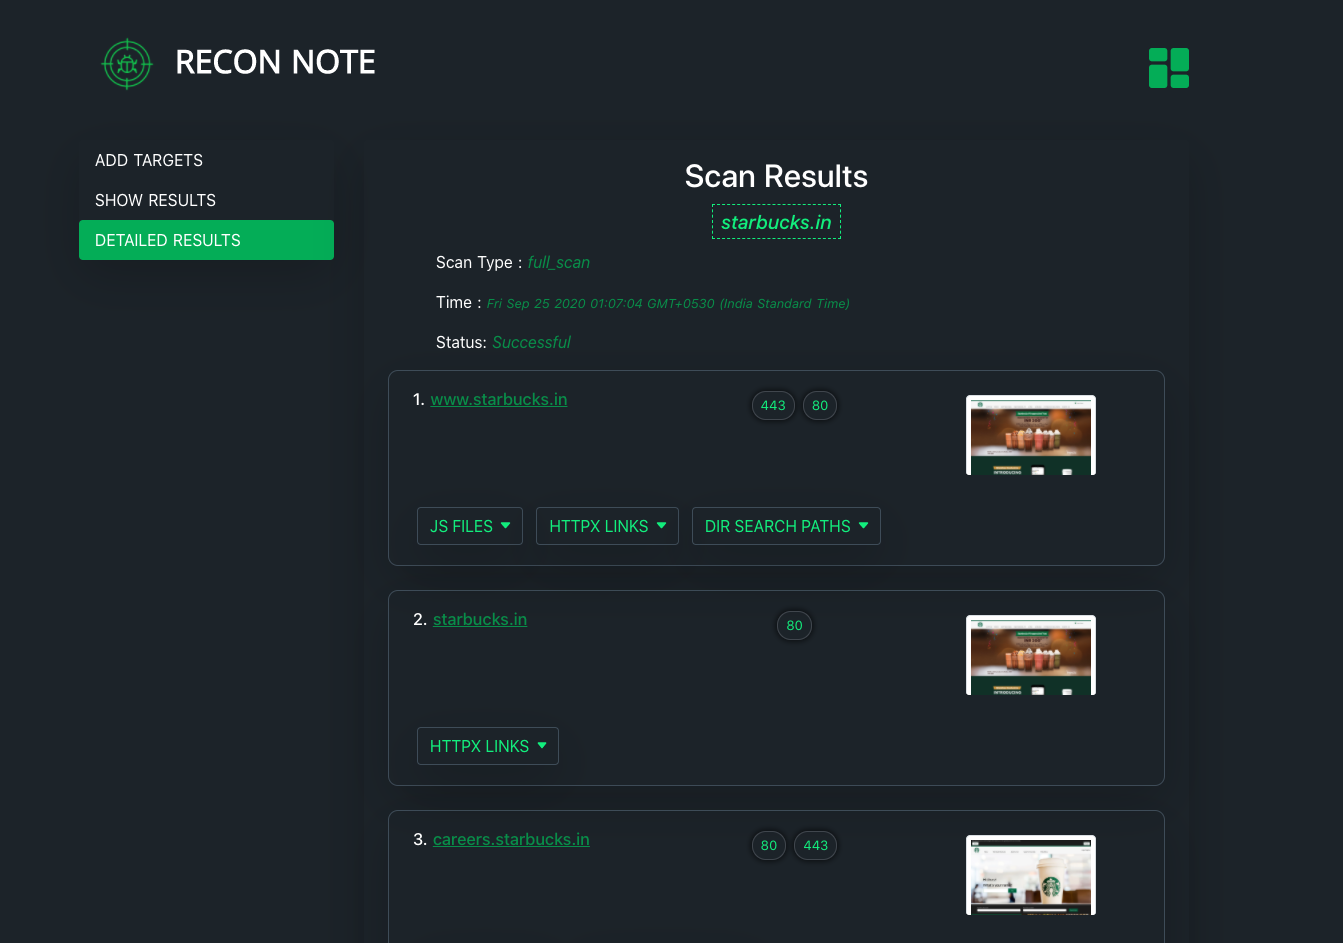 0xdekster/reconnote
Web Application Security Automation Framework which recons the target for various assets to maximize the attack surface for security professionals &…
 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
 sobri3195/pegasus-pentest-arsenal
A comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.
 cappricio-securities/burpflow
BurpFlow is one of the best Burp Suite automation tools for bug bounty hunters and penetration testers, widely used to load recon data via proxy and…
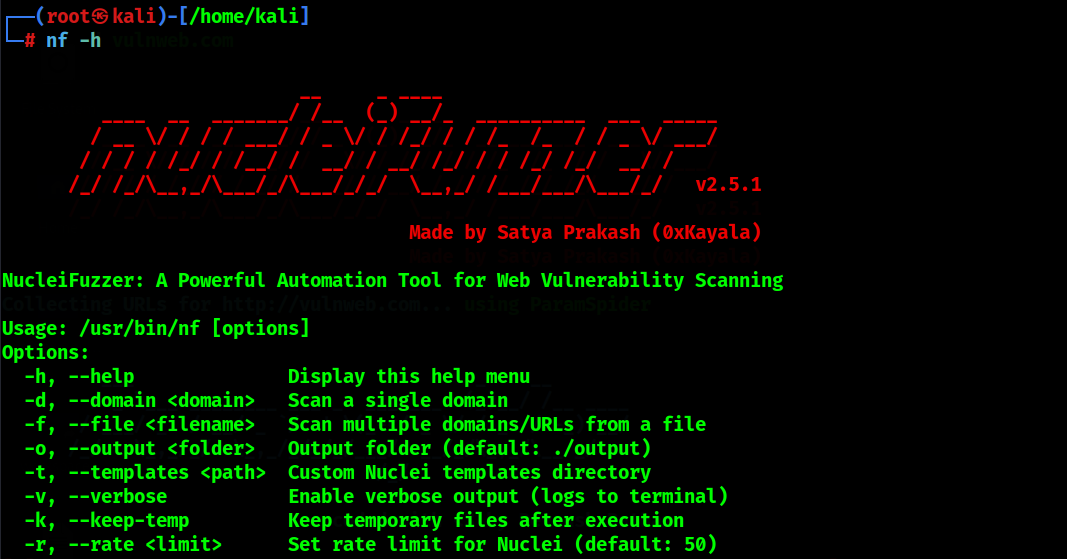 0xkayala/nucleifuzzer
Automated web vulnerability scanner combining URL discovery tools (ParamSpider, waybackurls, gauplus, hakrawler, katana) with Nuclei fuzzing…

 delvelabs/tachyon
Fast http dead file finder.
 overgrowncarrot1/cve-2023-0297
Proof-of-concept exploit for CVE-2023-0297, demonstrating a specific vulnerability in a web application for security testing and validation purposes.
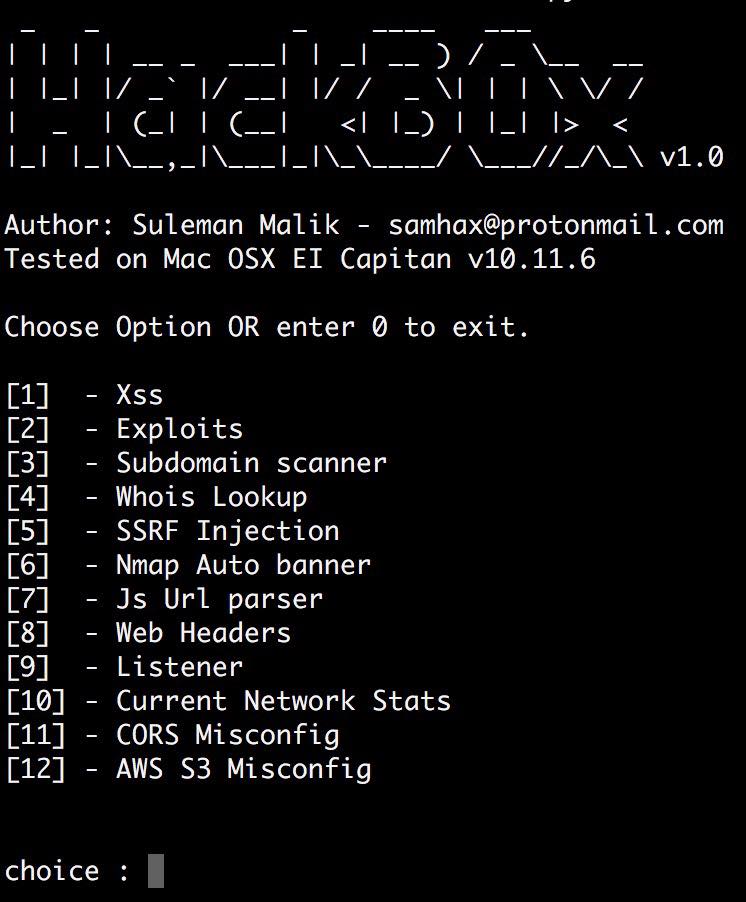 samhaxr/hackbox
HackBox is a powerful and comprehensive tool that combines a variety of techniques for web application and network security assessments, including…
 r3xbugbounty/cve-2025-53770
Proof-of-concept exploit for CVE-2025-53770, demonstrating exploitation of a web application vulnerability for security testing and validation.
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 artemcyberlab/project-project-chimera-exploiting-a-modern-wordpress-xxe-to-pillage-secrets-
The objective is to conduct a full-scale security assessment of a WordPress-based web application, culminating in a complete server compromise. The…
 bigherocenter/cve-2024-7029-exploit
Exploit code for CVE-2024-7029, a web application vulnerability, providing proof-of-concept implementation for security testing and research.
 m4fiab0y/cve-2022-30075
Proof-of-concept exploit for CVE-2022-30075, demonstrating a remote code execution vulnerability in a web application. Includes Python-based payload…