
KittyStager
 enelg52/kittystager
KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…
command-and-controleducationencryption-decryption-tools+6
226
enelg52/kittystagerKittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…
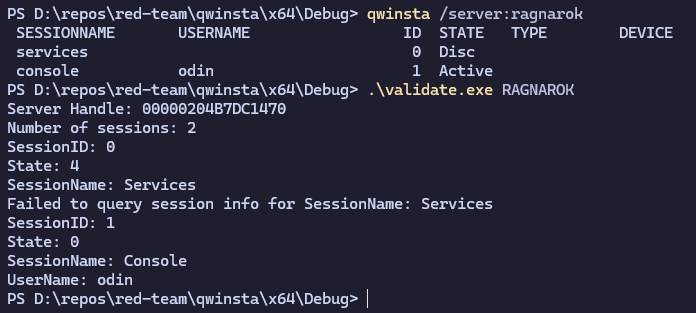 0xv1n/remotesessionenum
Remotely Enumerate sessions using undocumented Windows Station APIs
 macmod/flashingestor
TUI-based Active Directory data collector that ingests LDAP objects, performs remote RPC/SMB/HTTP collection, and generates BloodHound CE-compatible…
 technion/erlvulnscan
Concurrent network scanner for CVE-2015-1635
 jip-0-0-0-0-0/cve-2024-38063-scanner
A Python tool leveraging Shodan and Scapy to identify and exploit Windows systems vulnerable to CVE-2024-38063, enabling targeted Denial of Service…
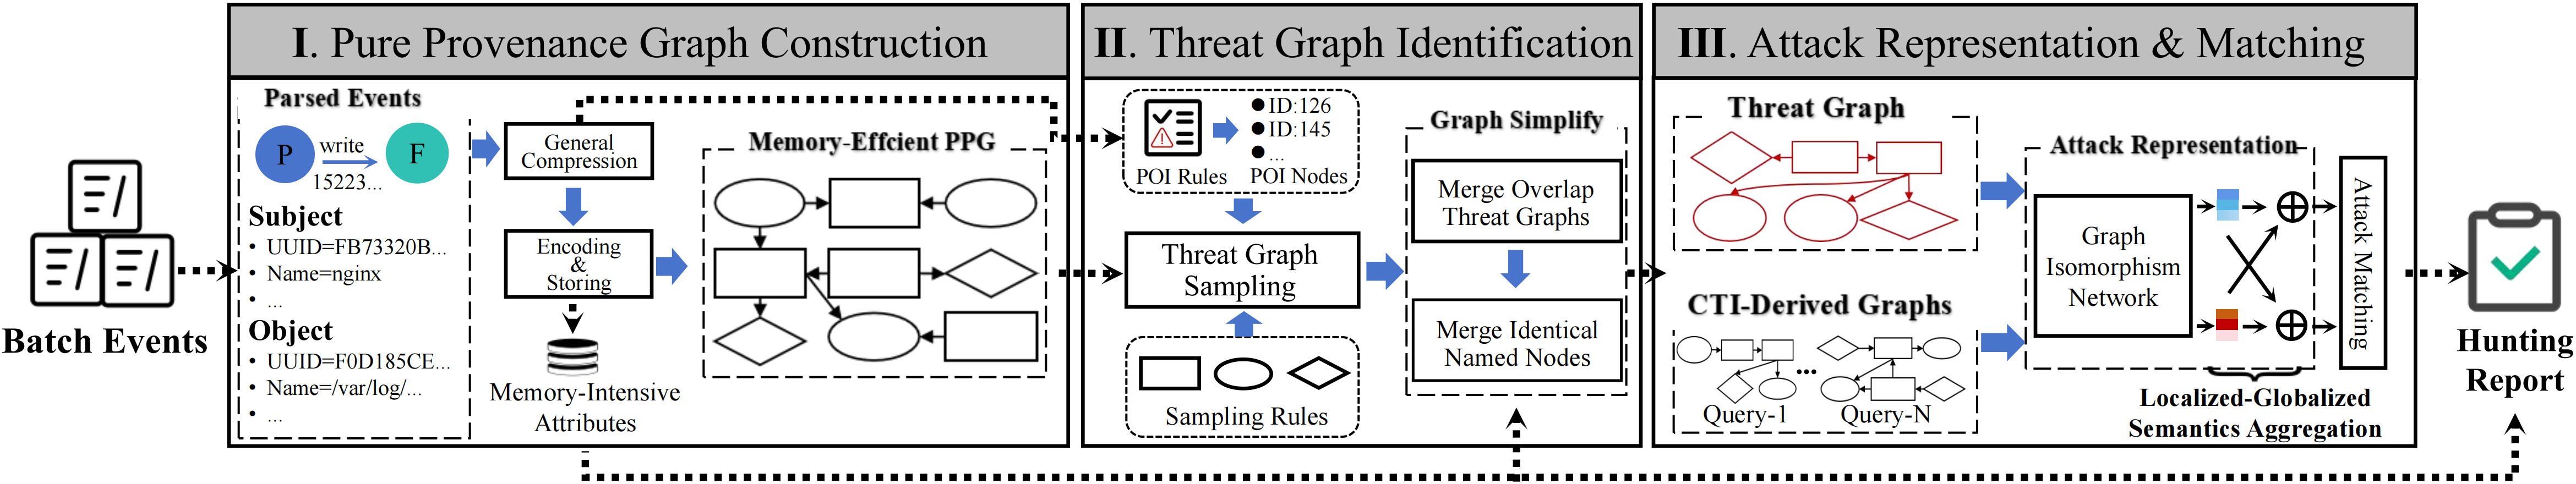 xueboqiu/prohunter
Graph-based threat detection system using inexact graph vector matching to compare threat graphs with CTI-derived attack query graphs for automated…
 justin-p/geoexplorer
Mass vulnerability scanner targeting CVE-2024-36401 in GeoServer, using WFS requests to discover feature types and deliver payloads for automated…
 you-ssef9/cve-2026-21440
Detection-only PoC for CVE-2026-21440 in AdonisJS BodyParser. Fingerprints AdonisJS indicators, probes upload endpoints via GET, and outputs…
 google/gcp_scanner
GCP resource scanner that evaluates access levels of compromised credentials by enumerating cloud services, projects, and IAM permissions across…
 bloodhoundad/sharphound3
C# Data Collector for the BloodHound Project, Version 3
 specterops/azurehound
Collects Azure tenant data (users, groups, roles, resources) and exports it for BloodHound attack path analysis in cloud penetration testing and red…
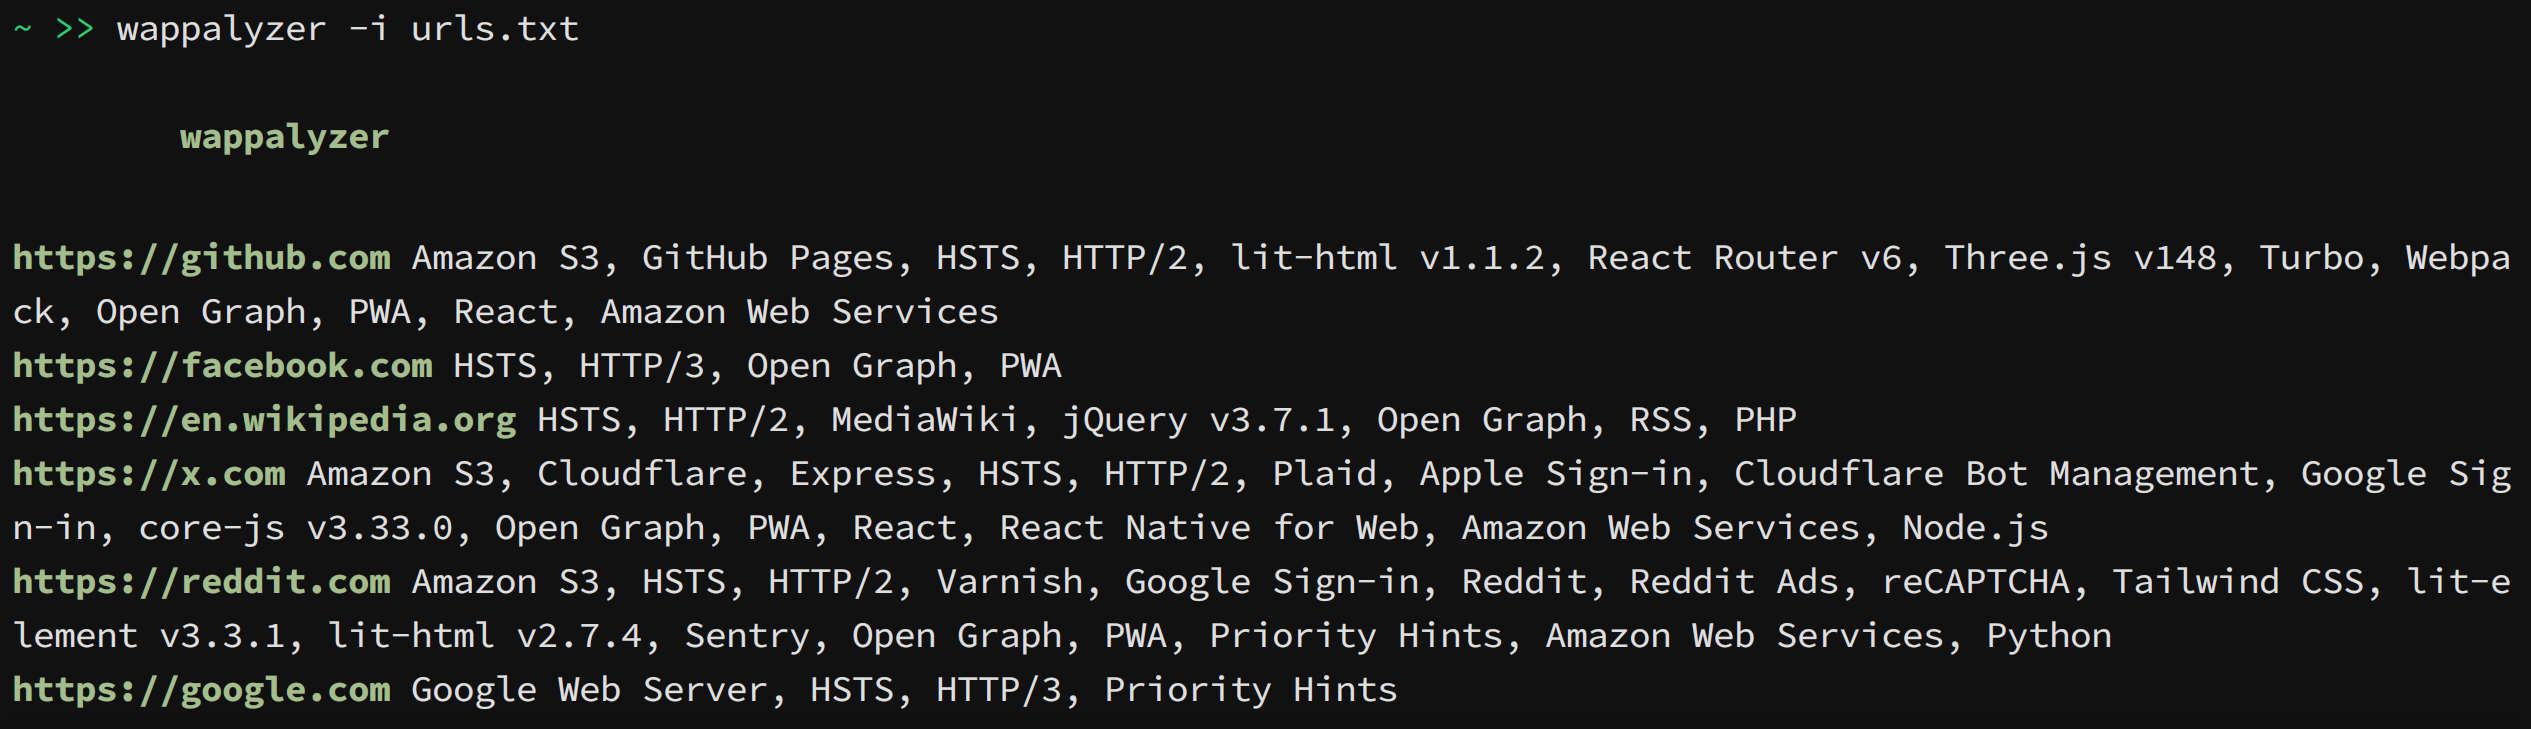 s0md3v/wappalyzer-next
detect technologies with wappalyzer alternative
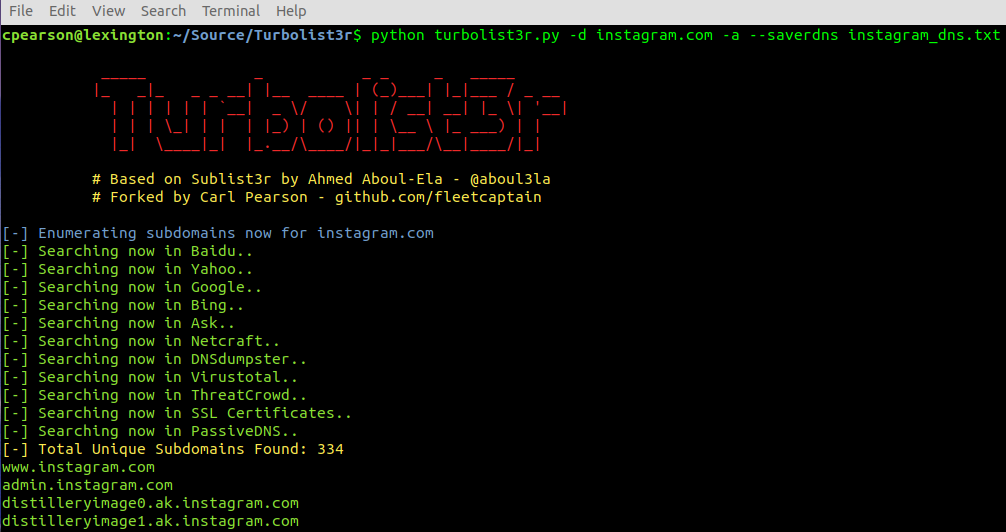 fleetcaptain/turbolist3r
Subdomain enumeration tool with analysis features for discovered domains
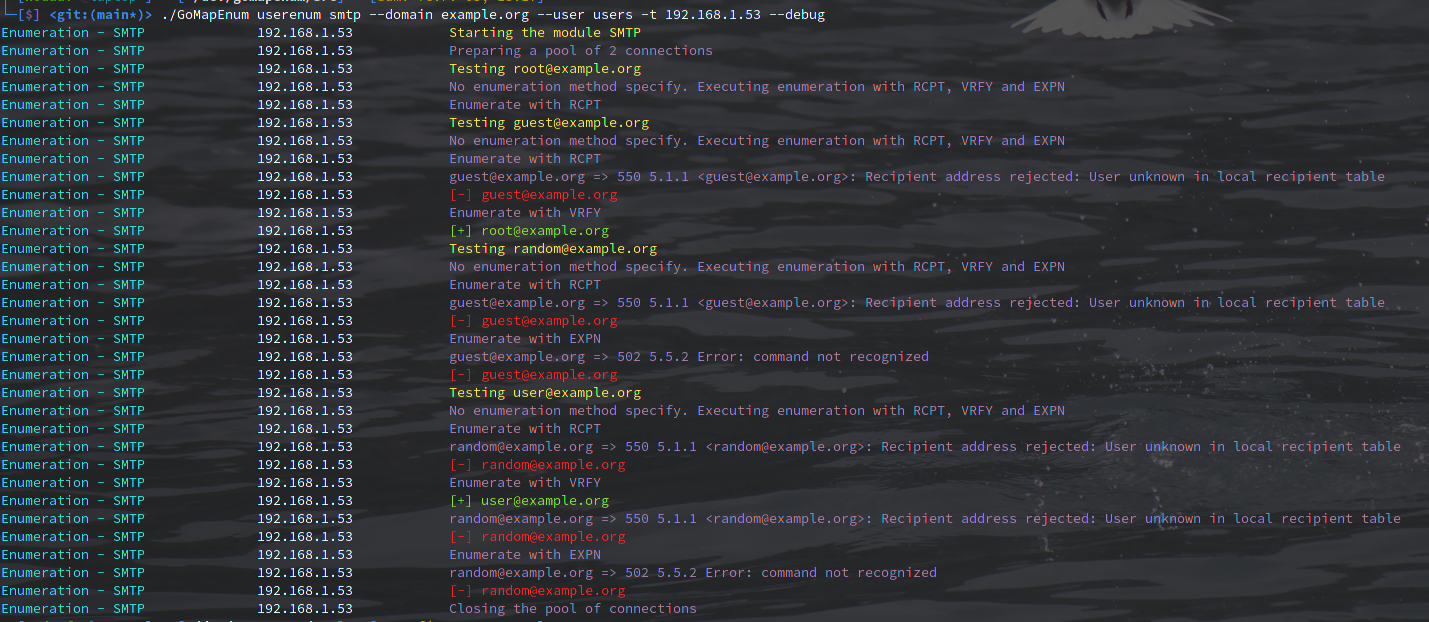 nodauf/gomapenum
User enumeration and password bruteforce on Azure, ADFS, OWA, O365, Teams and gather emails on Linkedin
 serain/bbrecon
Python library and CLI for the Bug Bounty Recon API
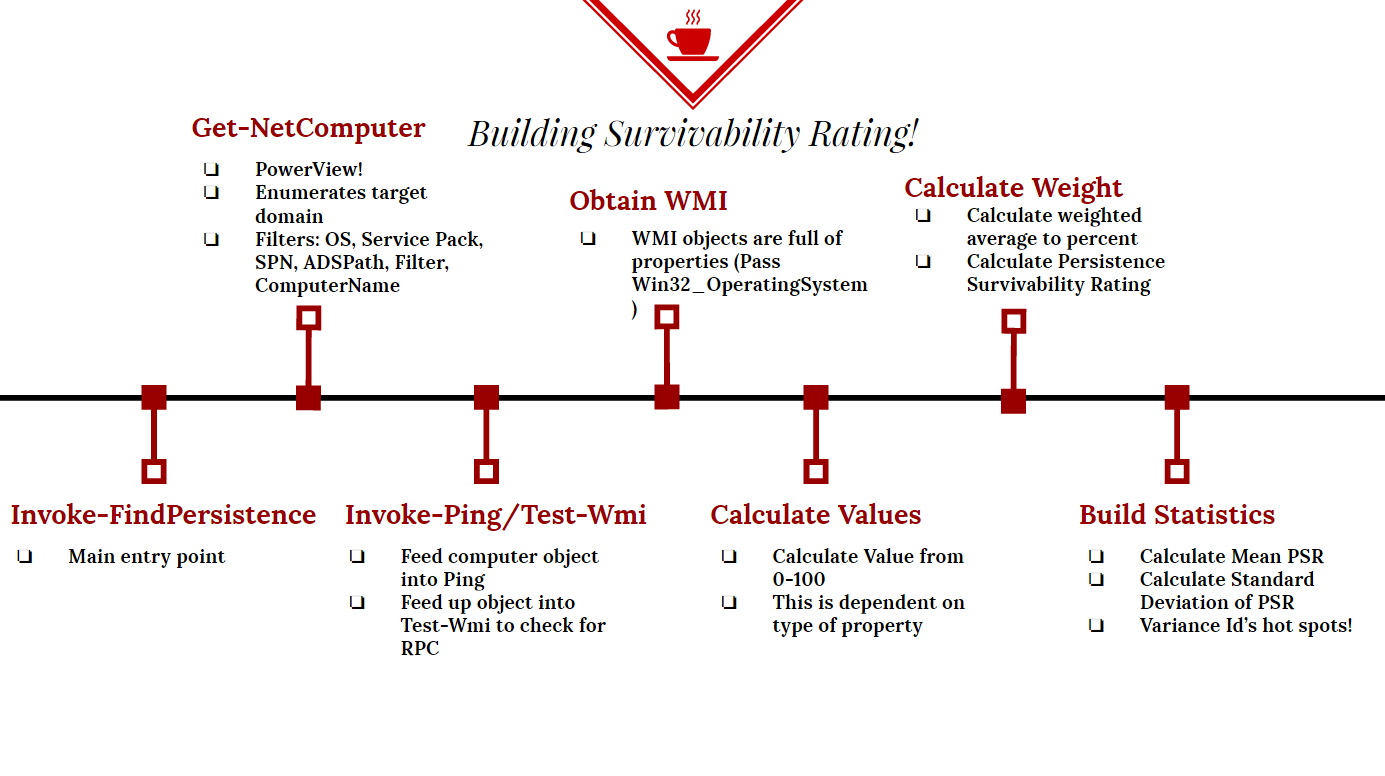 killswitch-gui/persistence-survivability
Powershell Persistence Locator
 subinacls/filibuster
Automated reconnaissance and information-gathering tool for penetration testing, designed to enumerate subdomains, endpoints, and network services.