
DefaultCreds-cheat-sheet
 ihebski/defaultcreds-cheat-sheet
One place for all the default credentials to assist the Blue/Red teamers identifying devices with default password 🛡️
curated-resourcesdefensive-toolseducation+6
6.8k
ihebski/defaultcreds-cheat-sheetOne place for all the default credentials to assist the Blue/Red teamers identifying devices with default password 🛡️
 nuc13us/pulse
Pulse Secure VPN CVE-2019-11510
 grupooruss/cve-2024-6387
Python script to scan and secure SSH configurations against the CVE-2024-6387 race condition vulnerability, with automated LoginGraceTime adjustment…
 seajaysec/ivanti-connect-around-scan
Mitigation validation utility for the Ivanti Connect Around attack chain. Runs multiple checks. CVE-2023-46805, CVE-2024-21887.
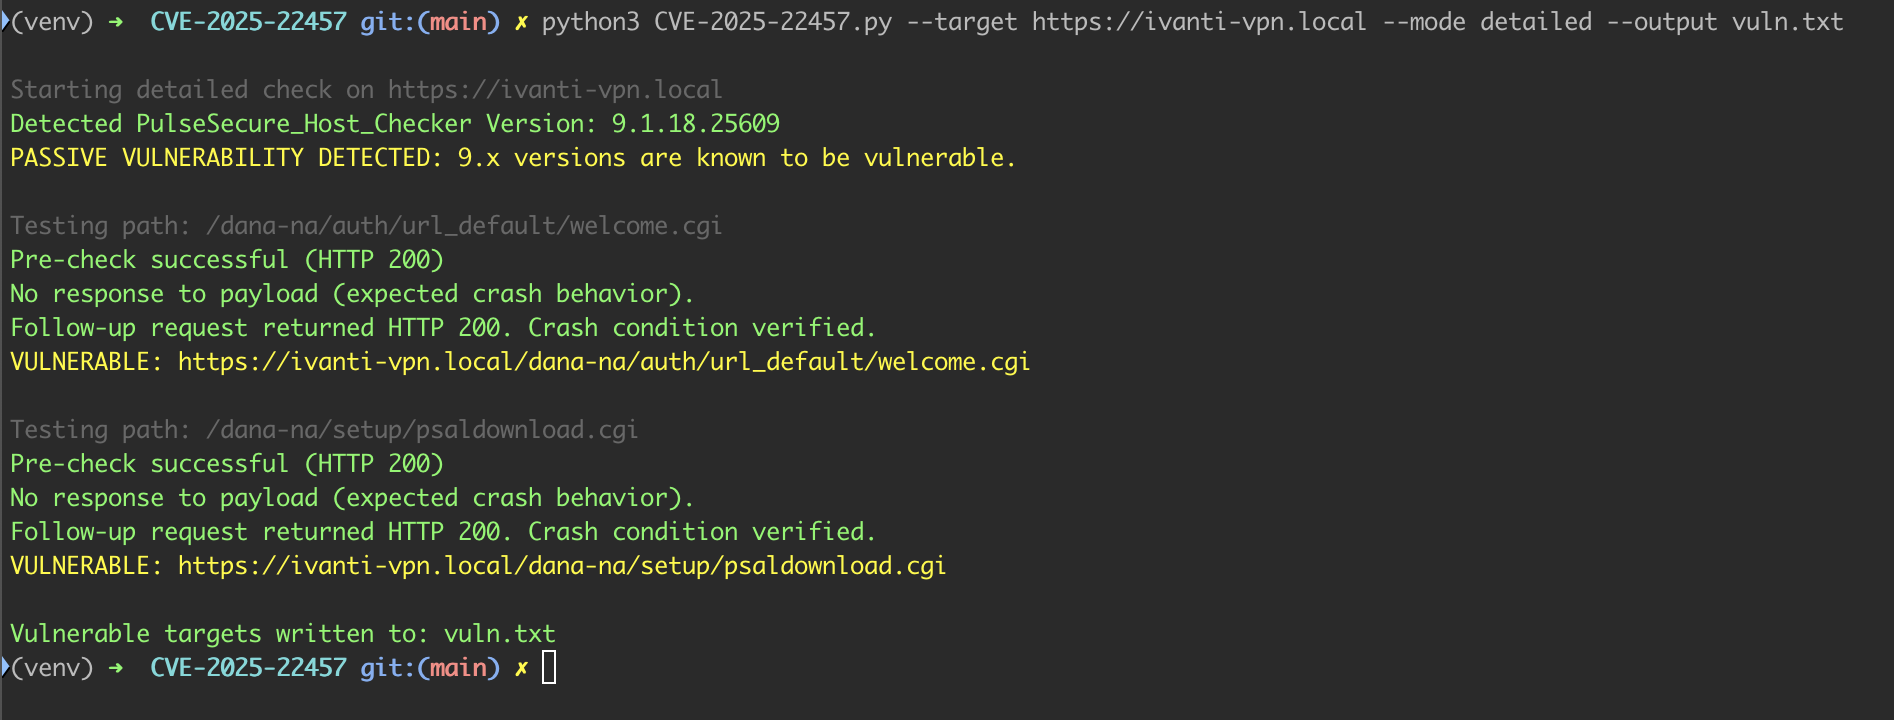 securekomodo/cve-2025-22457
CVE-2025-22457: Python Exploit POC Scanner to Detect Ivanti Connect Secure RCE
 cyberleelawat/cve-2025-20393
Cisco is aware of a potential vulnerability. Cisco is currently investigating and will update these details as appropriate as more…
 aerchy/cve-2024-7593
Exploit for CVE-2024-7593, a critical RCE in Pulse Secure VPN management interface, allowing authenticated attackers to execute arbitrary commands.…
 aqhmal/pulsexploit
Automated script for Pulse Secure SSL VPN exploit (CVE-2019-11510) using hosts retrieved from Shodan API. You must have a Shodan account to use this…
 xcoy0te/cve-2026-83548-checker
Non-intrusive detector for SonicWall SMA 1000 exposure to CVE-2026-83548/-83549 (version/patch-state check; no exploitation)
 eldraco/salamandra
Salamandra is a tool to find spy microphones that use radio freq to transmit. It uses SDR.
 yoryio/cve-2023-46805
Scanner for CVE-2023-46805 - Ivanti Connect Secure
 cbeek-r7/cve-2023-46805
Simple scanner for scanning a list of ip-addresses for vulnerable Ivanti Pulse Secure devices
 yozarseef95/cve-2023-31594
IC Realtime ICIP-P2012T 2.420 is vulnerable to Incorrect Access Control
 pwn3z/cve-2019-11510-pulsevpn
Exploit and detection scripts for CVE-2019-11510, enabling unauthenticated remote file reading on Pulse Secure VPN appliances, with IP scanning and…
 andripwn/pulse-exploit
Pulse Secure SSL VPN exploit (CVE-2019-11510) using hosts retrieved from Shodan API.
 cyberleelawat/cve-2025-40602
CVE-2025-40602 is a local privilege escalation vulnerability in the appliance management console (AMC) of SonicWall Secure Mobile Access (SMA) 1000…
 yozarseef95/cve-2023-31595
IC Realtime ICIP-P2012T is vulnerable to Incorrect Access Control via an open port
 mrlee123456/cve-2021-22893
Pulse Connect Secure RCE Vulnerability (CVE-2021-22893)