

peeko
 b3rito/peeko
peeko – Browser-based XSS C2 for stealthy internal network exploration via infected browser.
command-and-controldata-exfiltrationinformation-gathering+7
233
b3rito/peekopeeko – Browser-based XSS C2 for stealthy internal network exploration via infected browser.
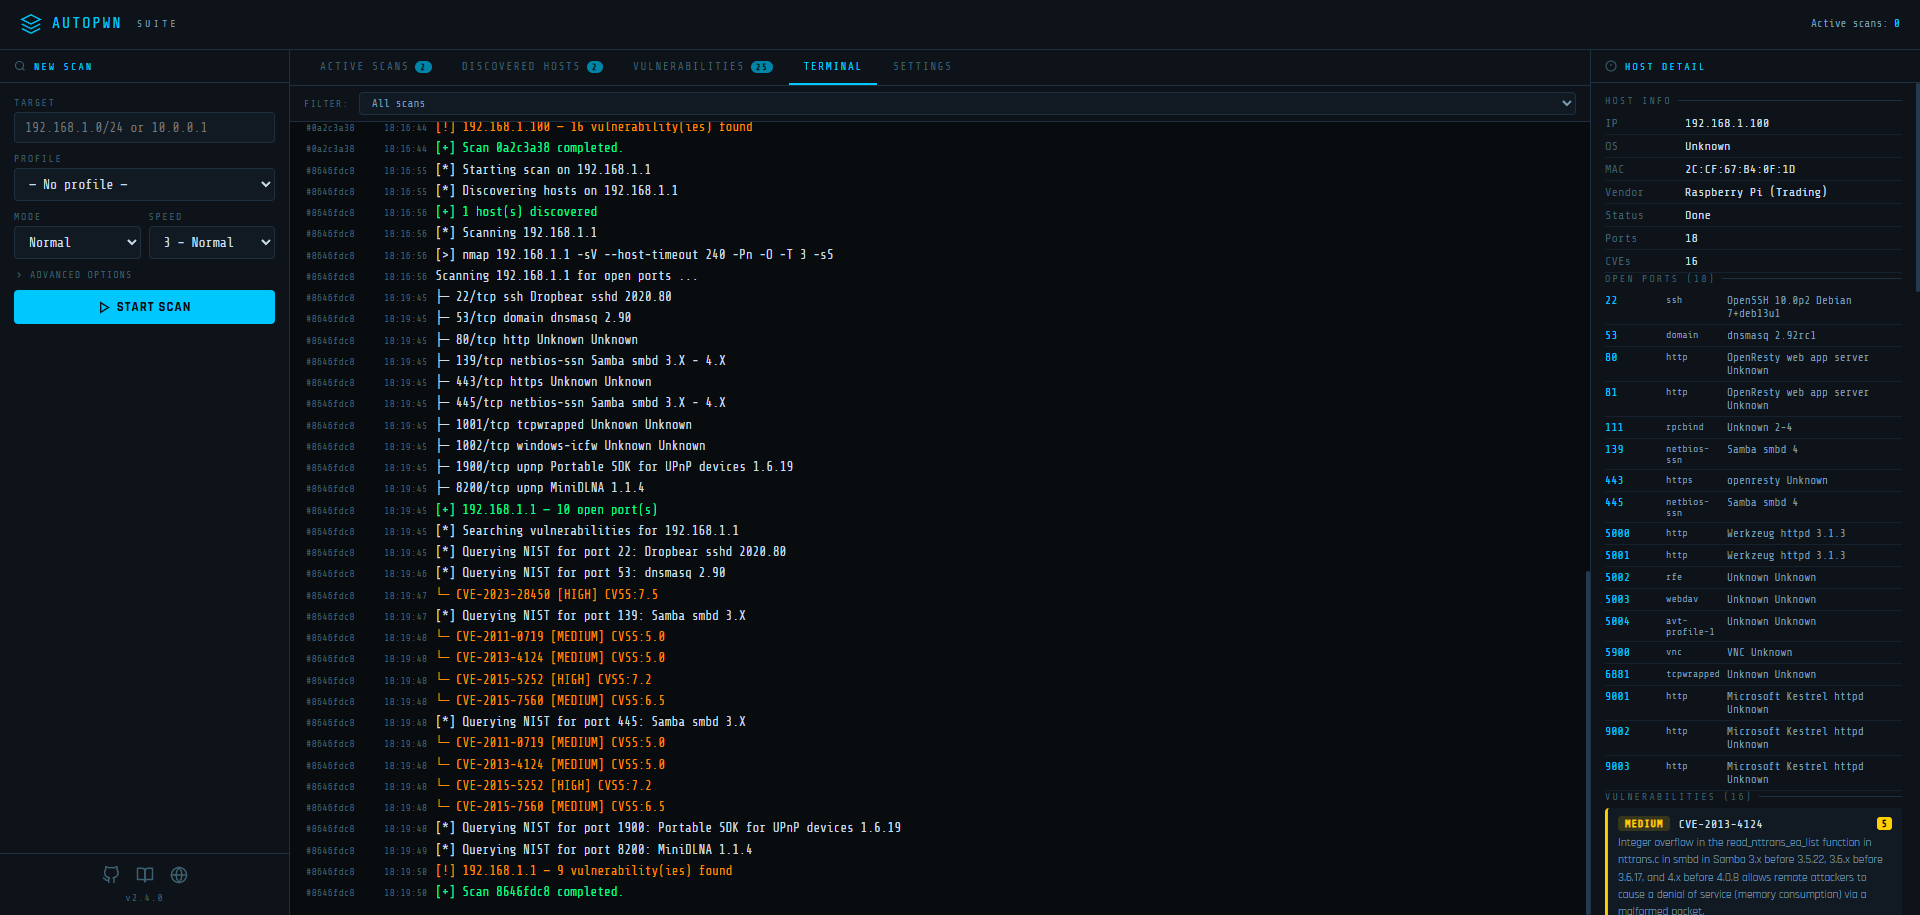 gamehunterkaan/autopwn-suite
AutoPWN Suite is a project for scanning vulnerabilities and exploiting systems automatically.
 inteleon404/cve-2025-0133
Reflected XSS vulnerability found in Palo Alto GlobalProtect Gateway & Portal. Attackers can inject malicious scripts via crafted requests.
 dirsoooo/recon
Recon is a script to perform a full recon on a target with the main tools to search for vulnerabilities. Created based on @ofjaaah and @Jhaddix…
 hood3drob1n/bingoo
BinGoo! A Linux bash based Bing and Google Dorking Tool
 w01fh4cker/cve-2023-1671-poc
CVE-2023-1671-POC, based on dnslog platform
 nhpt/weblogic-ssrf_cve-2014-4210
Weblogic SearchPublicRegistries SSRF(CVE-2014-4210) Exploit Script based on Python3
 d4rkmatt3r/kyoceracredsdump
Kyocera cred dumper based on CVE-2022-1026
 tjoulel/wordpress-6.9.1-blind-ssrf
Based on CVE-2022-3590, WordPress <= 6.9.1 - Unauthenticated Blind SSRF via XML-RPC Pingback Discovery proof of concept (PoC)
 mverschu/cve-2017-7921
HikVision Auth Bypass CVE, tool is able to extract credentials, and take snapshots based on magic cookie or supplied credentials.
 stanislav-web/opendoor
OWASP Web Recon & Directory Discovery Platform
 smaash/quasibot
complex webshell manager, quasi-http botnet.
 kn0x0x/cve-2025-32756-poc
Proof of Concept for CVE-2025-32756 - A critical stack-based buffer overflow vulnerability affecting multiple Fortinet products.
 shiva108/waes
CPH:SEC WAES: Web Auto Enum & Scanner - Auto enums website(s) and dumps files as result
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
 dmonst3r/wordpressmassexploiter
[discontinued] Mass exploiter of CVE-2015-1579 for WordPress CMS
 exfil0/cve-2024-55591-poc
A comprehensive all-in-one Python-based Proof of Concept script to discover and exploit a critical authentication bypass vulnerability…
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…