

AWSBucketDump
 jordanpotti/awsbucketdump
Security Tool to Look For Interesting Files in S3 Buckets
cloud-securityinformation-gatheringpenetration-testing+1
1.5k
jordanpotti/awsbucketdumpSecurity Tool to Look For Interesting Files in S3 Buckets
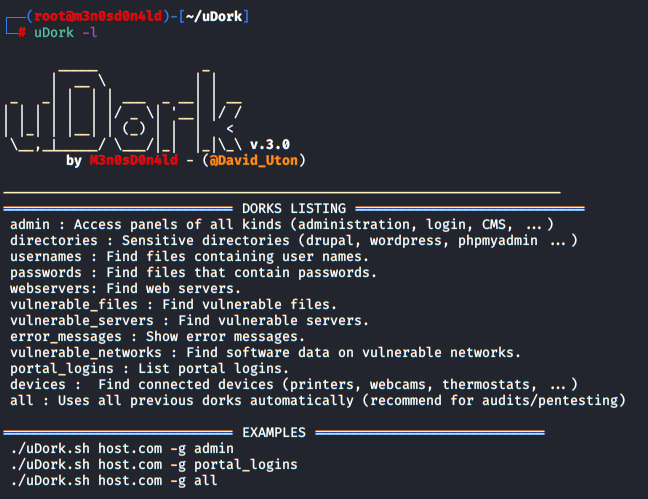 m3n0sd0n4ld/udork
uDork is a script written in Bash Scripting that uses advanced Google search techniques to obtain sensitive information in files or directories, find…
 t3l3machus/eviltree
A python3 remake of the classic "tree" command with the additional feature of searching for user provided keywords/regex in files, highlighting those…
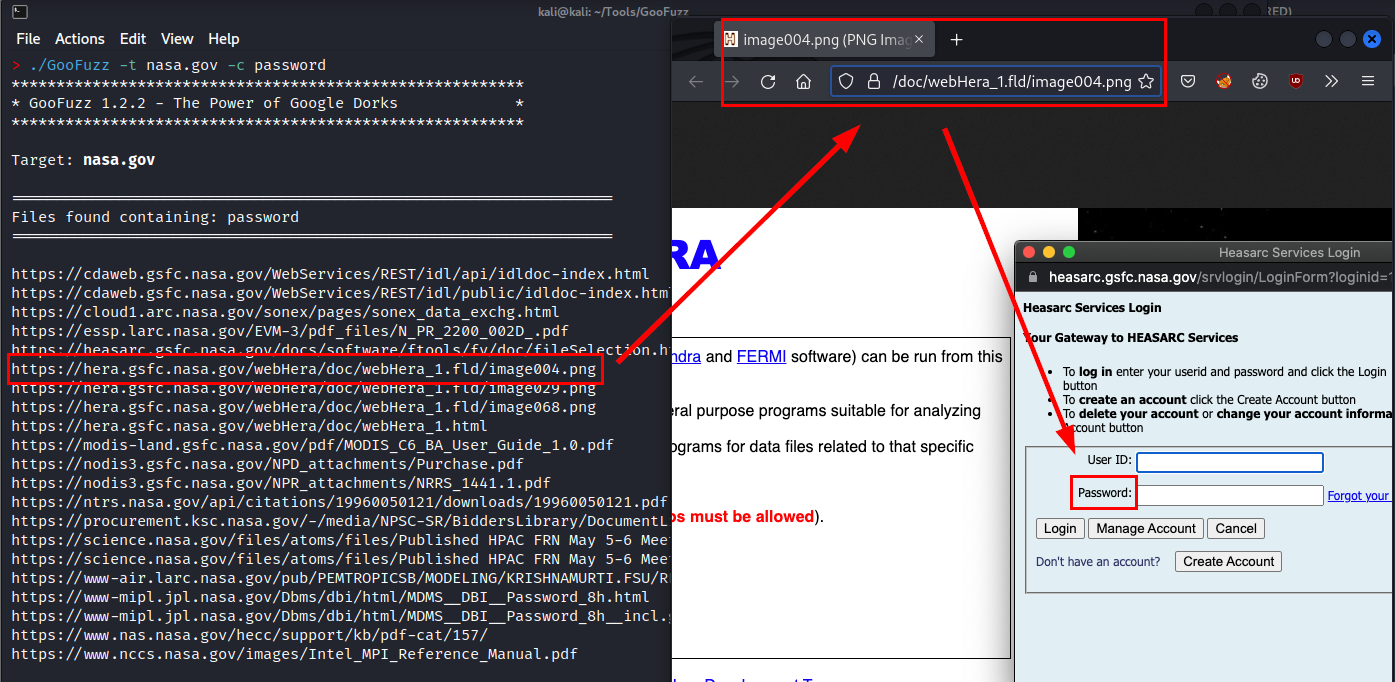 m3n0sd0n4ld/goofuzz
Bash-based fuzzing tool that leverages Google Dorking for stealthy enumeration of directories, files, subdomains, and parameters without direct…
 vulnmachines/grafana-unauth-file-read
Exploit for Grafana LFI vulnerability CVE-2021-43798 enabling unauthorized file reading via path traversal in plugin endpoints.
 kal1gh0st/mylog4shell
Simple Python 3 script to detect the "Log4j" Java library vulnerability (CVE-2021-44228) for a list of URLs with multithreading
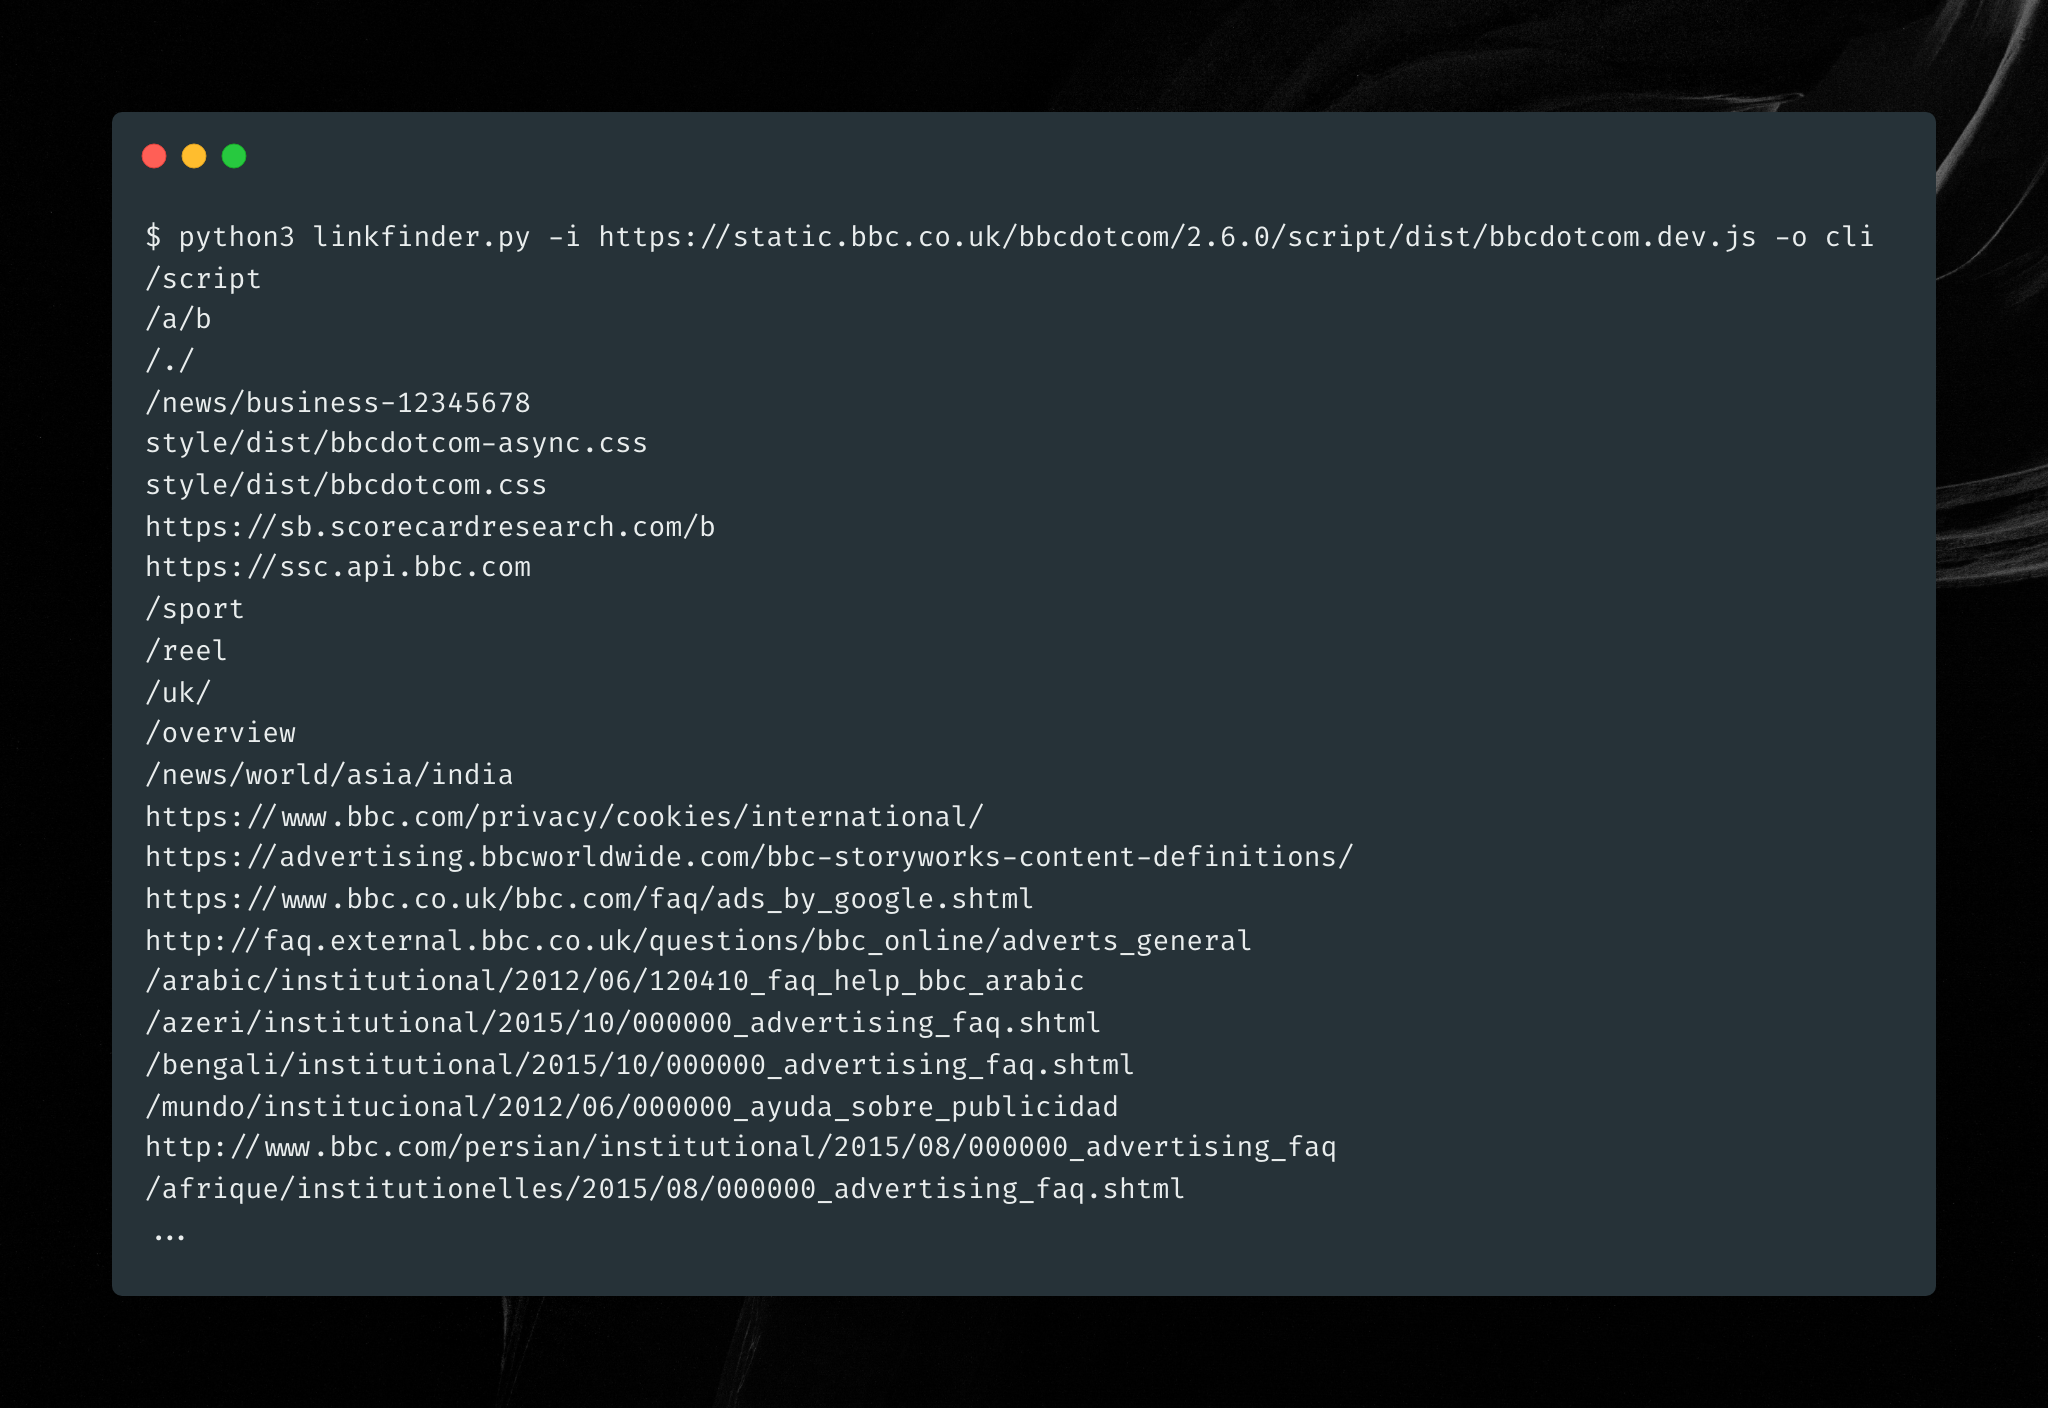 gerbenjavado/linkfinder
A python script that finds endpoints in JavaScript files
 byt3hx/jsleak
Concurrent CLI tool for discovering secrets, API keys, and links in JavaScript files during web reconnaissance, with custom regex pattern support and…
 m0n1x90/exif-gps-tracer
A python script which allows you to parse GeoLocation data from your Image files stored in a dataset.It also produces output in CSV file and also in…
 3ndg4me/cve-2020-3452-exploit
Just basic scanner abusing CVE-2020-3452 to enumerate the standard files accessible in the Web Directory of the CISCO ASA applicances.
 eslam3kl/3klcon
Automation Recon tool which works with Large & Medium scopes. It performs a lot of tasks and gets back all the results in separated files.
 0xteles/jsleak
a Go code to detect leaks in JS files via regex patterns
 badsectorlabs/sccm-http-looter
Find interesting files stored on (System Center) Configuration Manager (SCCM/CM) shares via HTTP(s)
 kacakb/jsfinder
Fetches JavaScript files quickly and comprehensively.
 redhuntlabs/bucketloot
BucketLoot is an automated S3-compatible bucket inspector that can help users extract assets, flag secret exposures and even search for custom…
 blackfan/bfscan
Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…
 nebian/cve-2024-23897
Scraping tool to ennumerate directories or files with the CVE-2024-23897 vulnerability in Jenkins.
 randomrobbiebf/loot-me
Collects files and commands post-exploitation, formats them into Markdown reports, and helps find sensitive information for red team reporting.