
GraphQLGrapper
 m19o/graphqlgrapper
Burp Suite extension to extract and collect GraphQL API endpoints from HTTP request history for security testing and reconnaissance.
api-security-testinginformation-gatheringpenetration-testing+3
21
m19o/graphqlgrapperBurp Suite extension to extract and collect GraphQL API endpoints from HTTP request history for security testing and reconnaissance.
 nu11secur1ty/burpsuite-grand-master-tools
Modular toolkit for pentesters that converts Burp Suite captured HTTP requests into browsable URLs and automates workflow actions with auditable…
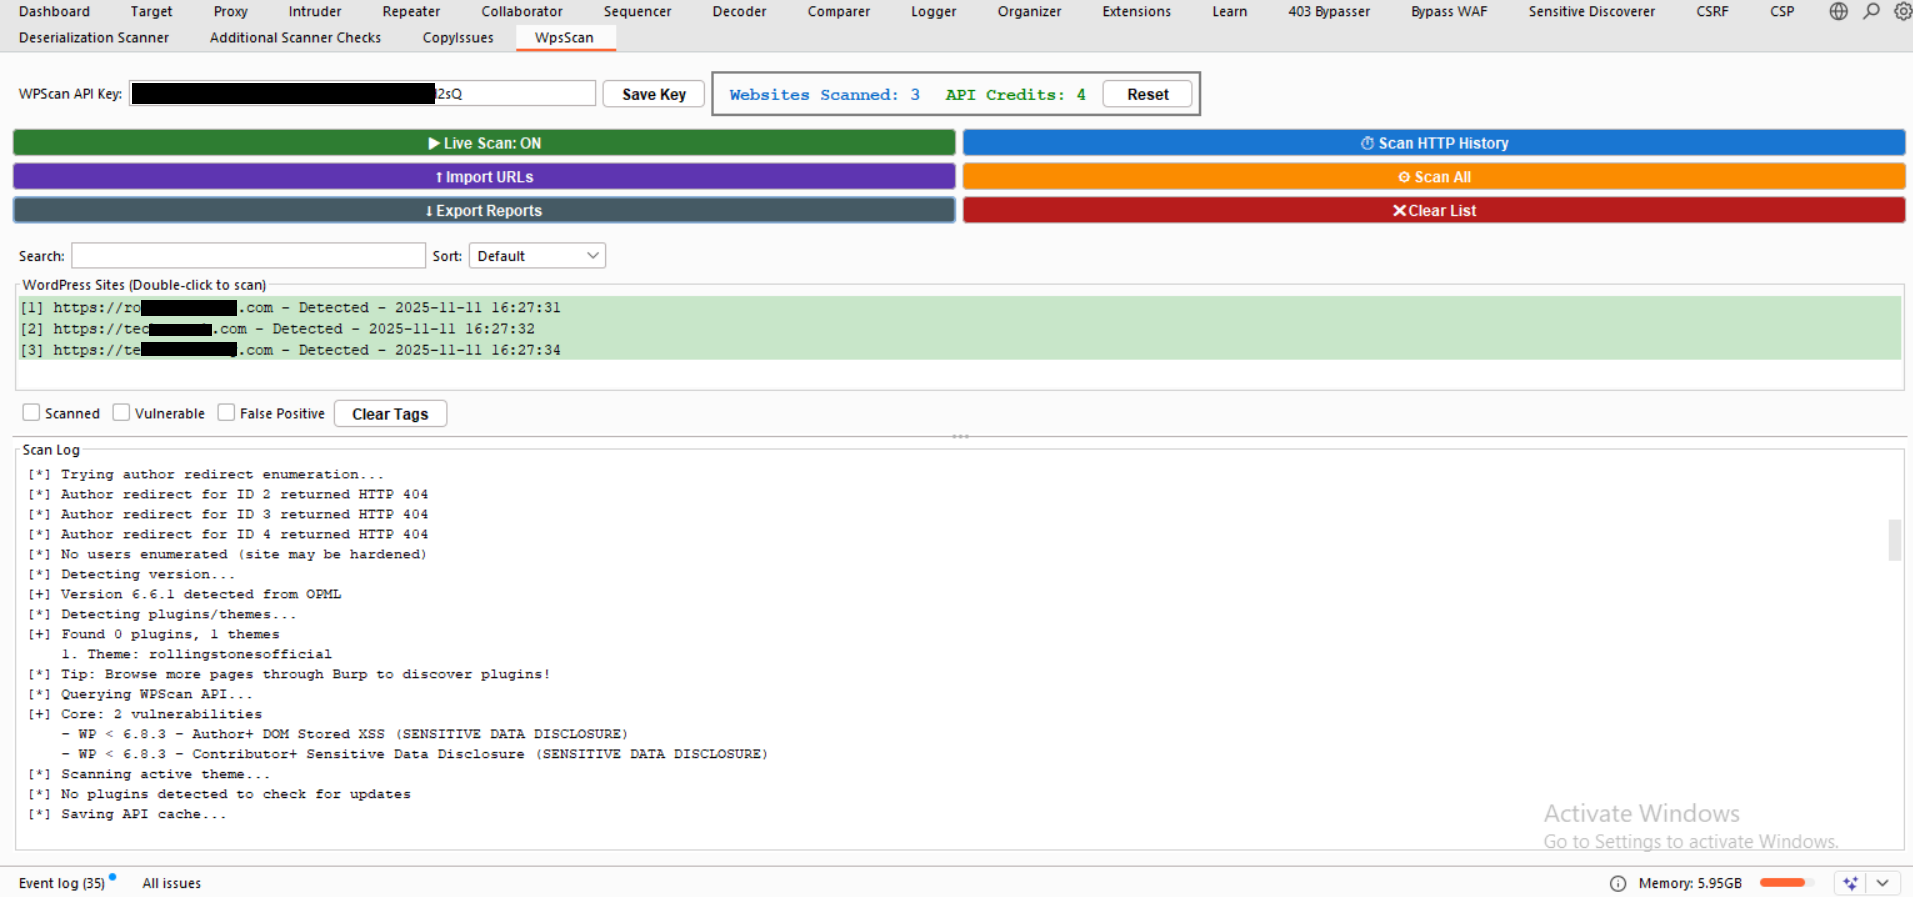 teycir/burpwpsscan
Burp extension for wordpress security scanning
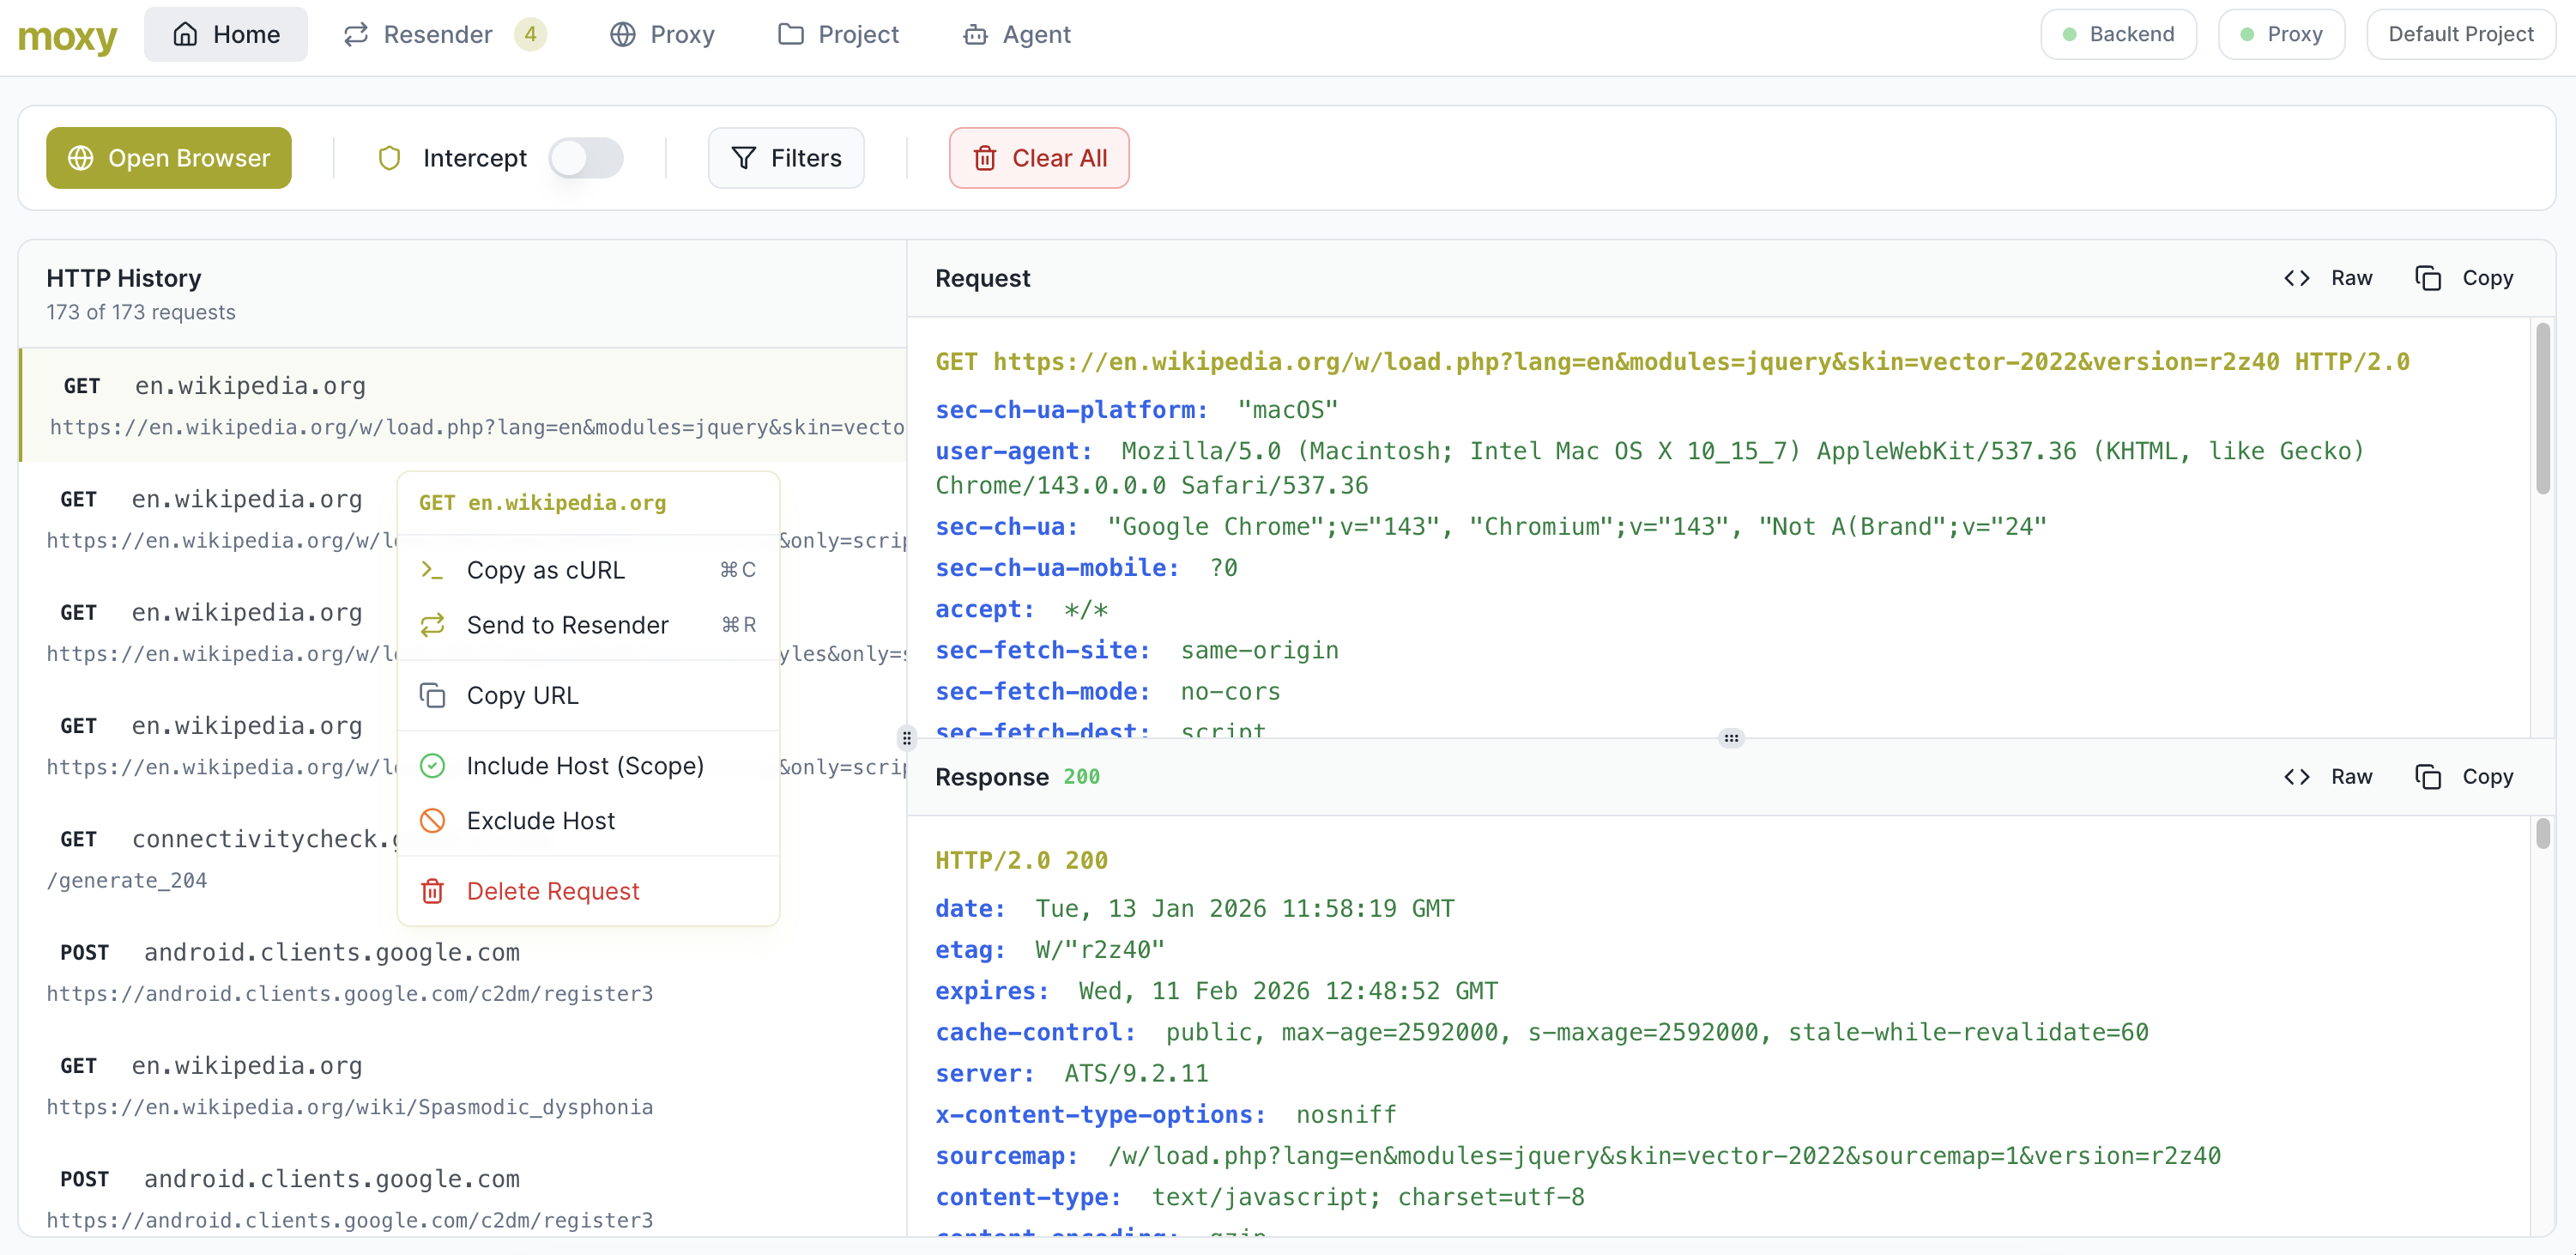 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
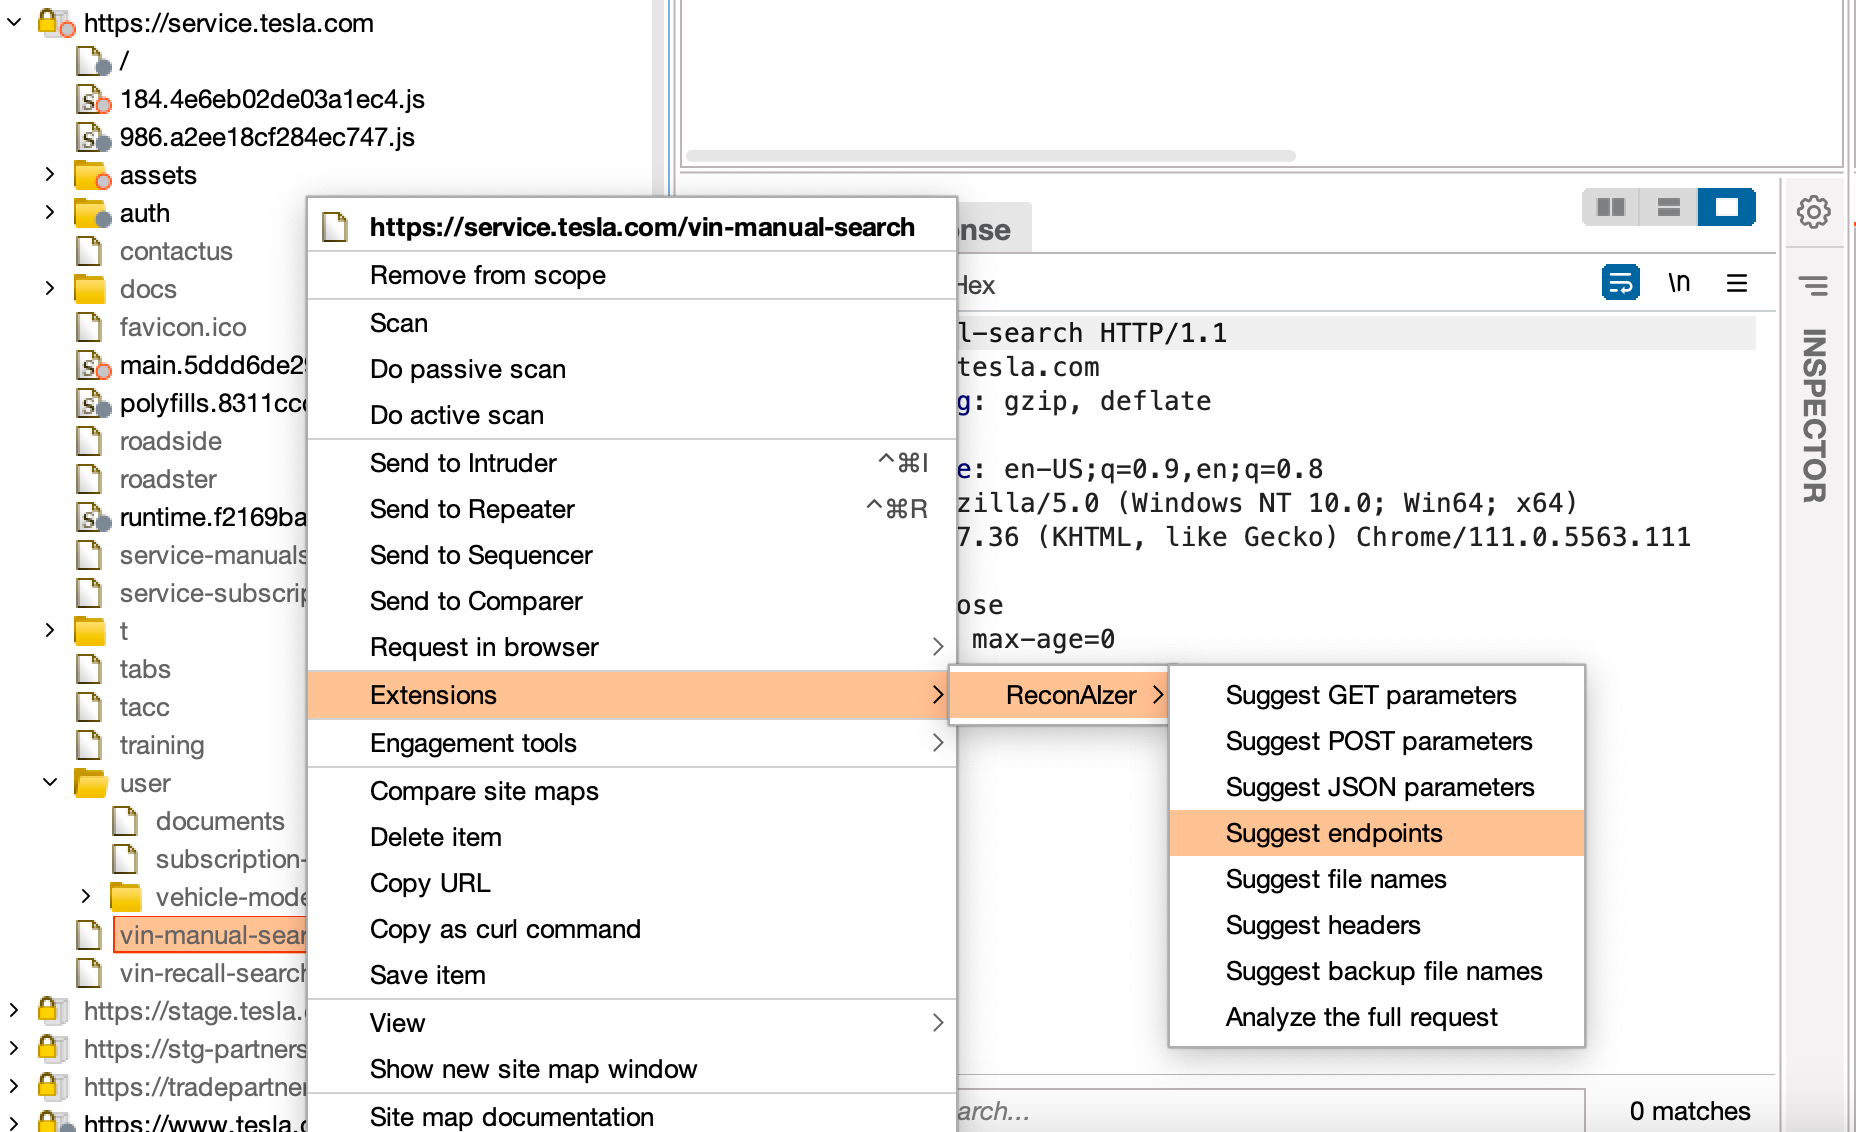 hisxo/reconaizer
A Burp Suite extension to add OpenAI (GPT) on Burp and help you with your Bug Bounty recon to discover endpoints, params, URLs, subdomains and more!
 moeinfatehi/admin-panel_finder
Burp Suite extension that finds exposed admin panels and login pages of web applications and infrastructure. 1,000+ payloads, OWASP WSTG-CONF-05.
 cappricio-securities/burpflow
BurpFlow is one of the best Burp Suite automation tools for bug bounty hunters and penetration testers, widely used to load recon data via proxy and…
 erman-bolukbasi/web-penetration-drupal
Penetration test of a Drupal web app — CVE-2018-7600 (Drupalgeddon 2) exploited using Nmap, Burp Suite & Metasploit | Internship @ BB CyberSec
 shieldersec/webtech
Identify technologies used on websites.