
CVE-2026-33715
 romain-deperne/cve-2026-33715
Unauthenticated SSRF and open email relay in Chamilo LMS — CVE-2026-33715 / CVSS 7.2
exploitationphishingreconnaissance+2
romain-deperne/cve-2026-33715Unauthenticated SSRF and open email relay in Chamilo LMS — CVE-2026-33715 / CVSS 7.2
 pog007/cve-2023-5561-poc
WordPress does not properly restrict which user fields are searchable via the REST API, allowing unauthenticated attackers to discern the email…
 kernel364/cve-2024-2876
Proof-of-concept exploit for a critical SQL injection vulnerability in WordPress Email Subscribers plugin. Includes exploitation details, HTTP…
 bhanunamikaze/cve-2024-42009
This Proof of Concept (PoC) demonstrates an exploit for CVE-2024-42009, leveraging a cross-site scripting (XSS) vulnerability to extract emails from…
 7h30th3r0n3/cve-2025-51586-prestashop-poc
PrestaShop AdminLogin Email Enumeration PoC - CVE-2025-51586. This repository provides an ethical Proof-of-Concept (PoC) for the PrestaShop…
 thewoodenbench/cve-2025-66956
Insecure Access Control in Contact Plan, E-Mail, SMS and Fax components in Asseco SEE Live 2.0 allows remote attackers to access and execute…
 ekultek/whatbreach
OSINT tool to find breached emails, databases, pastes, and relevant information
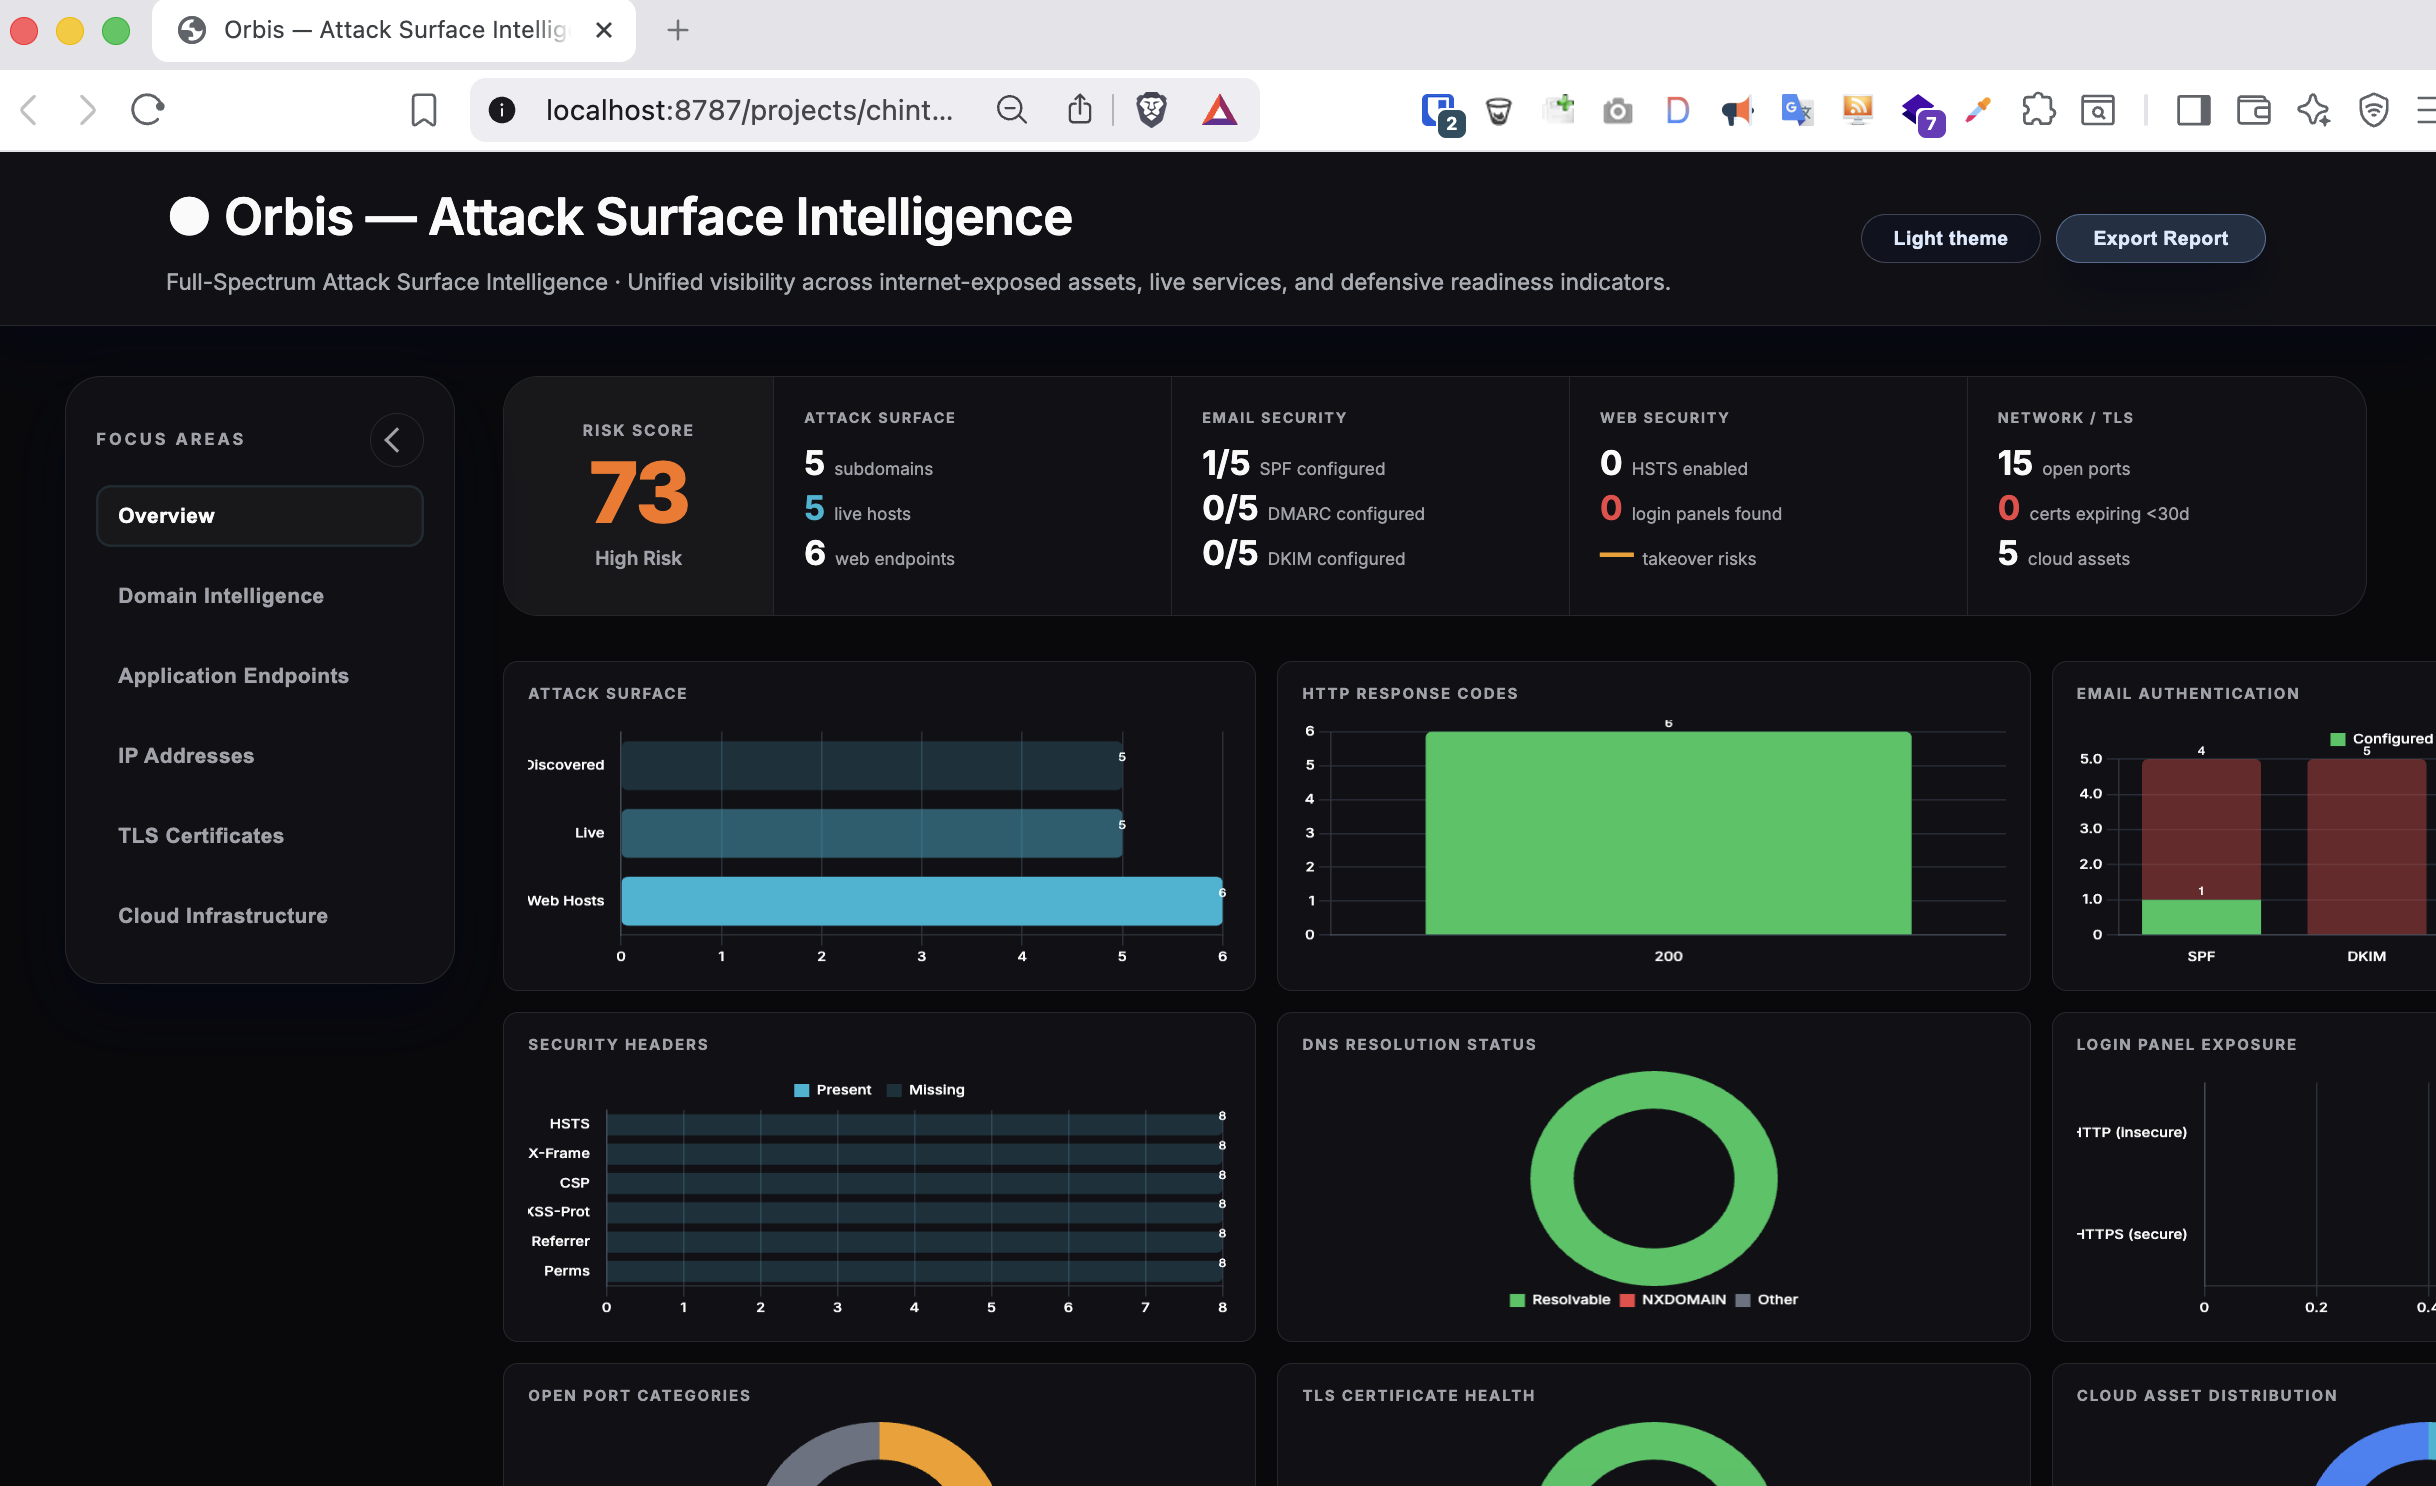 iamthefrogy/frogy2.0
Orbis is an full spectrum automated external attack surface intelligent toolkit.
 cisc0-gif/email-extract
Simple tool for extracting emails from websites

 osintnet/osintnet-public
OsintNET is a browser-based OSINT platform for domain intelligence, website risk scanning, SERP discovery, image intelligence and AI image detection.
 redbyte1337/credspy
Entra ID user enumeration and auth method discovery via the public GetCredentialType API
 cnotin/m365_groups_enum
Enumerate Microsoft 365 Groups in a tenant with their metadata
 artemy-ccrsky/cve-2024-39211
User Enumeration vulnerability in Kaiten (workflow management system)
 0ggp4r1s/osint-pattern-analyzer
Automated OSINT tool for phone number discovery, pattern detection, and cross-platform correlation.
 leakix/sentryexploit
CVE-2023-38035 Recon oriented exploit, extract company name contact information
 shinthink/cve-2026-54390
CVE-2026-54390 — JTL Shop Smarty SSTI RCE | Pre-Auth Template Injection via fetch('string:' . ) | 5.2.0-5.7.1
 cyberleelawat/cve-2025-20393
Cisco is aware of a potential vulnerability. Cisco is currently investigating and will update these details as appropriate as more…