Big-Ass-Data-Broker-Opt-Out-List

Curated, community-maintained directory of data broker opt-out instructions to help individuals remove personal information from people-search sites…

Curated, community-maintained directory of data broker opt-out instructions to help individuals remove personal information from people-search sites…

Checks all maintainers of all NPM and Pypi packages for hijackable packages through domain re-registration

Fast passive subdomain enumeration tool.

PoC exploits for CVE-2026-52824 (GHSA-jr9p-4h4j-6c58) — Kimai time-tracking default APP_SECRET authentication bypass affecting versions ≤ 2.57.0

Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…

Fast, accurate subdomain takeover scanner with zero false positives. Detects vulnerable subdomains, collects metadata (IP, CNAME, title, status…

Multithreaded reverse IP lookup tool for discovering domains hosted on the same IP address.

Just a silly recon tool that uses data from SSL Certificates to find potential host names

Wicked sick v2.0 script is intended to automate your reconnaissance process in an organized fashion.

PEGASUS-NEO is a comprehensive penetration testing framework designed for security professionals and ethical hackers. It combines multiple security…

Analysis of state-sponsored WhatsApp phishing infrastructure with real-time QR hijacking and device surveillance

A proof of concept demonstrating how to use the Hinge dating app as a C2.

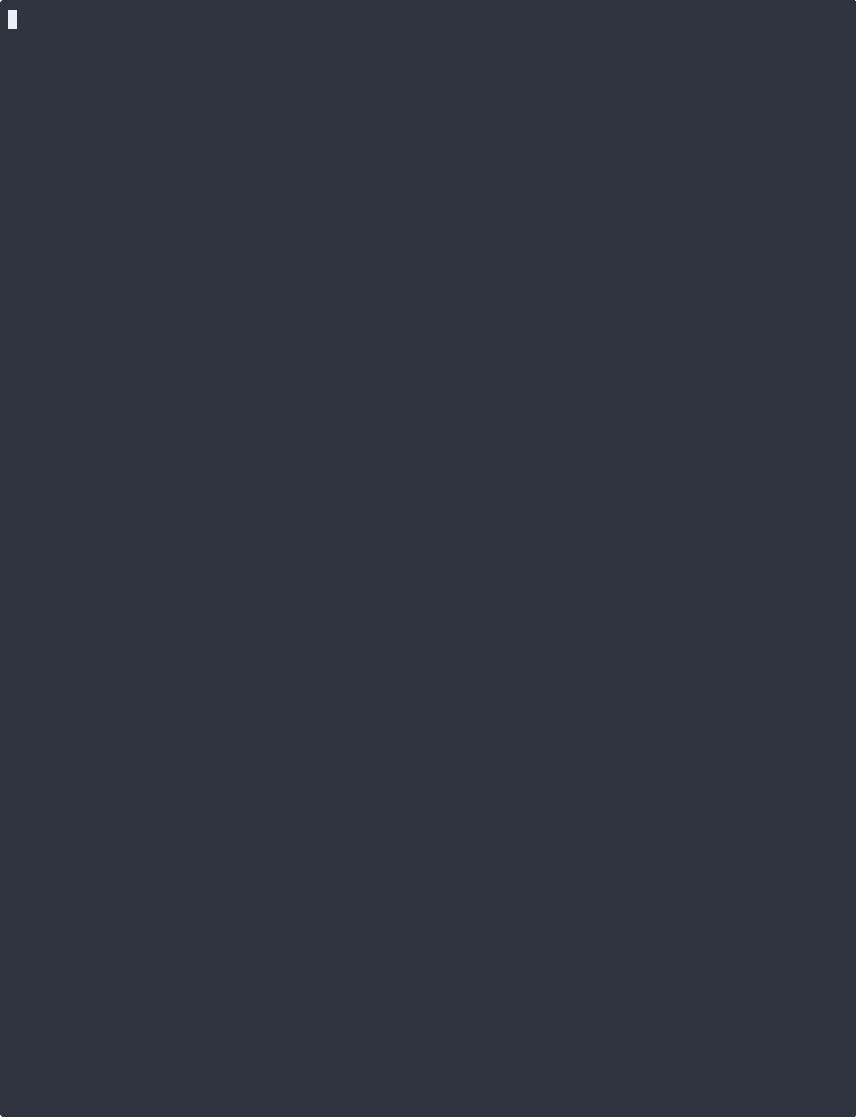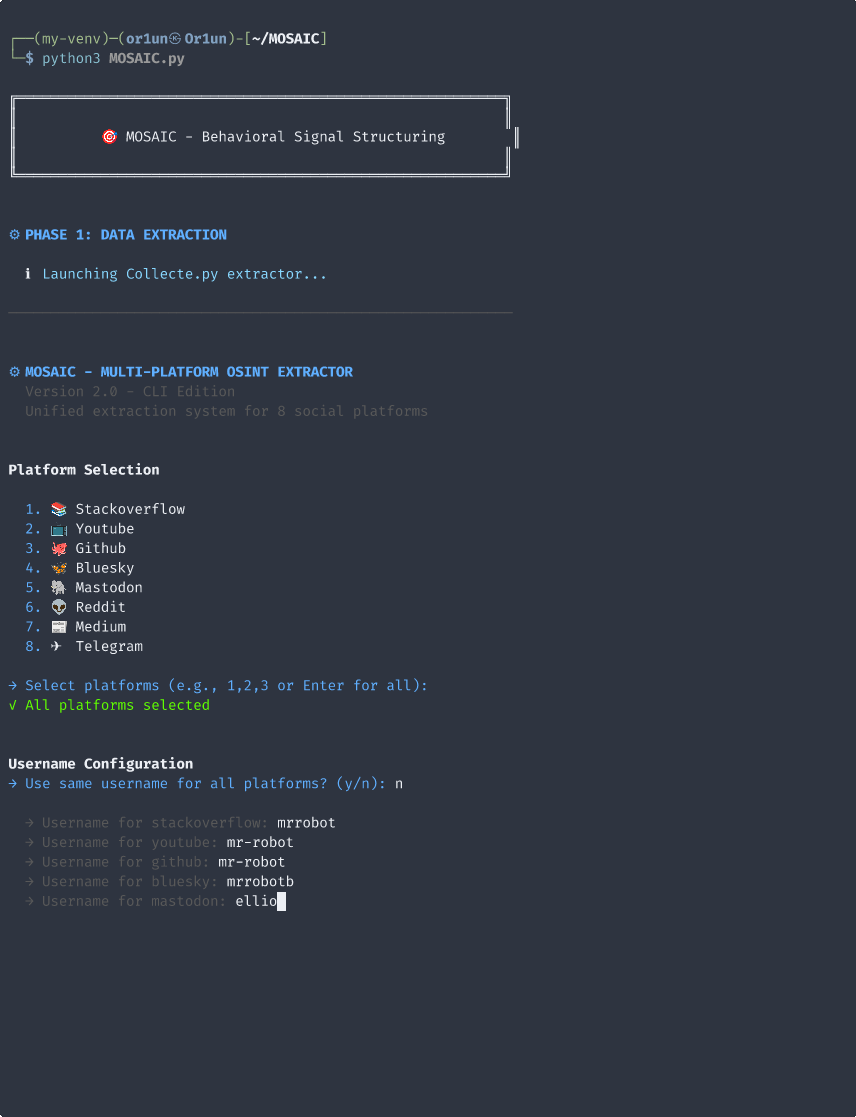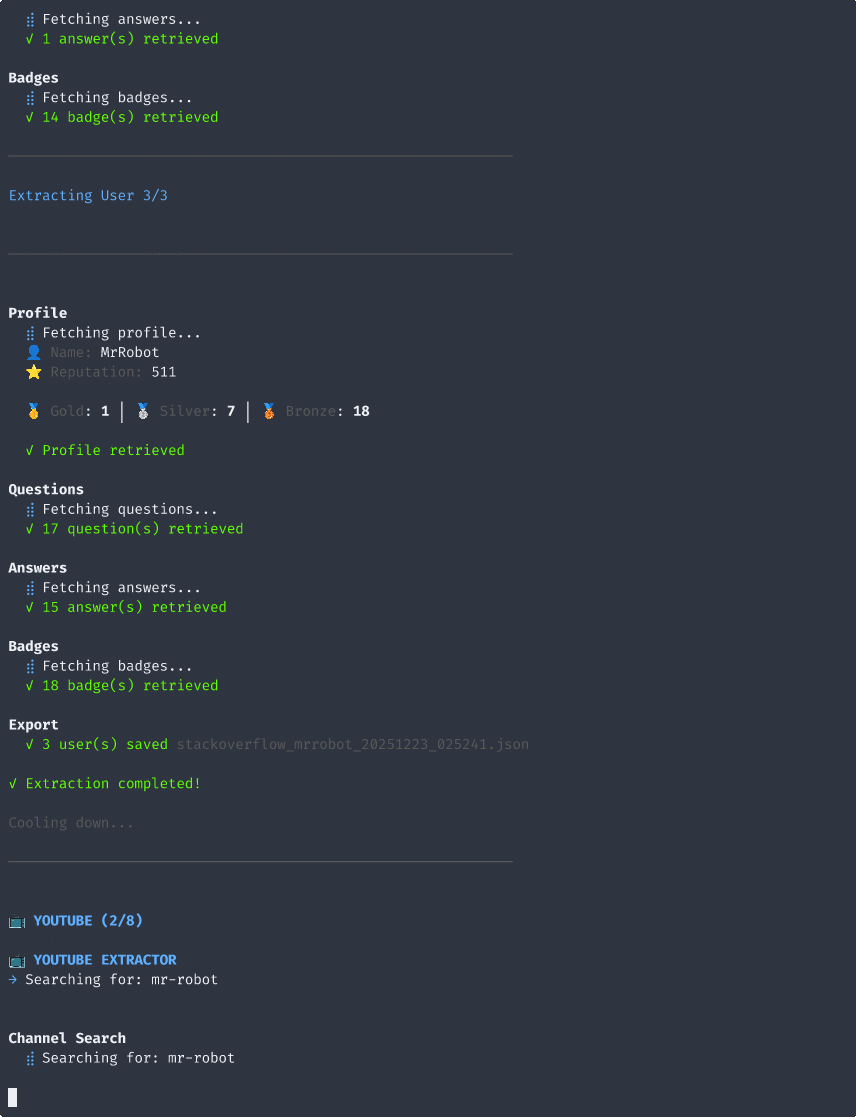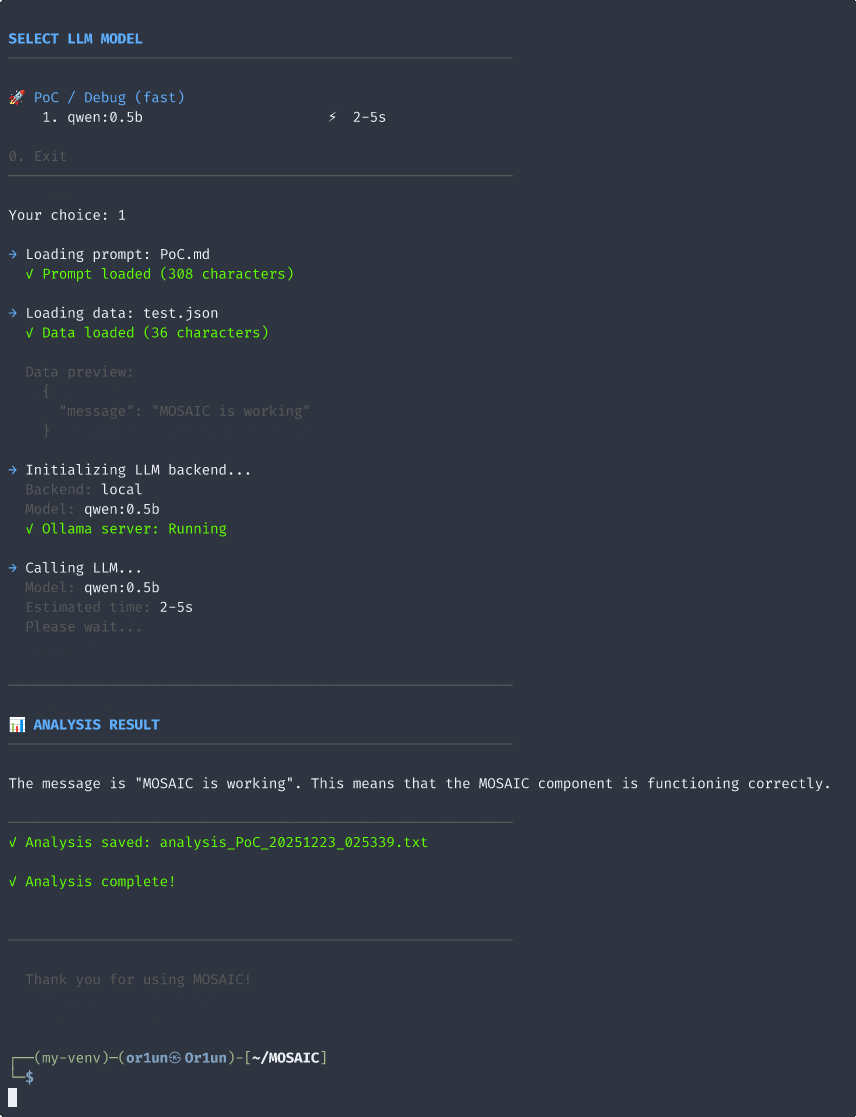
Privacy-first behavioral intelligence framework for multi-platform analysis and sociodynamic research.

Reproducible incident micro-postmortem for on-prem Microsoft SharePoint “ToolShell” (CVE-2025-53770): ATT&CK snapshot, “logs that matter” table,…

Scans project dependencies for dependency confusion vulnerabilities and checks package owner email takeover risks across multiple registries (npm,…

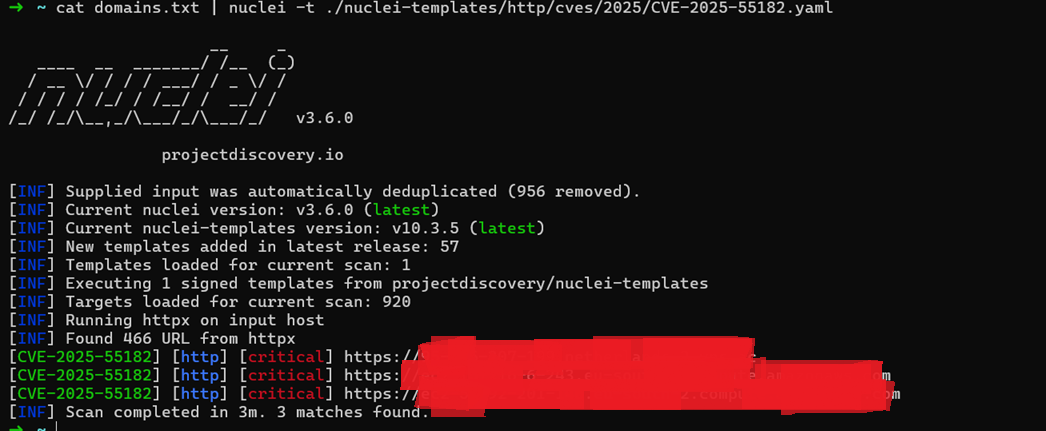
PoC, Hunting React2Shell about CVE-2025-55182

Passive subdomain discovery tool that aggregates results from multiple online sources via CLI, supporting stdin/stdout, JSONL output, and API key…

crawls the website and finds broken social media links that can be hijacked