
toolbox
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
api-security-testingcrawlerdynamic-analysis-sandboxing+8
43
go-appsec/toolboxCollaborative application security testing between humans and agents via CLI and MCP
 stanislav-web/opendoor
OWASP Web Recon & Directory Discovery Platform
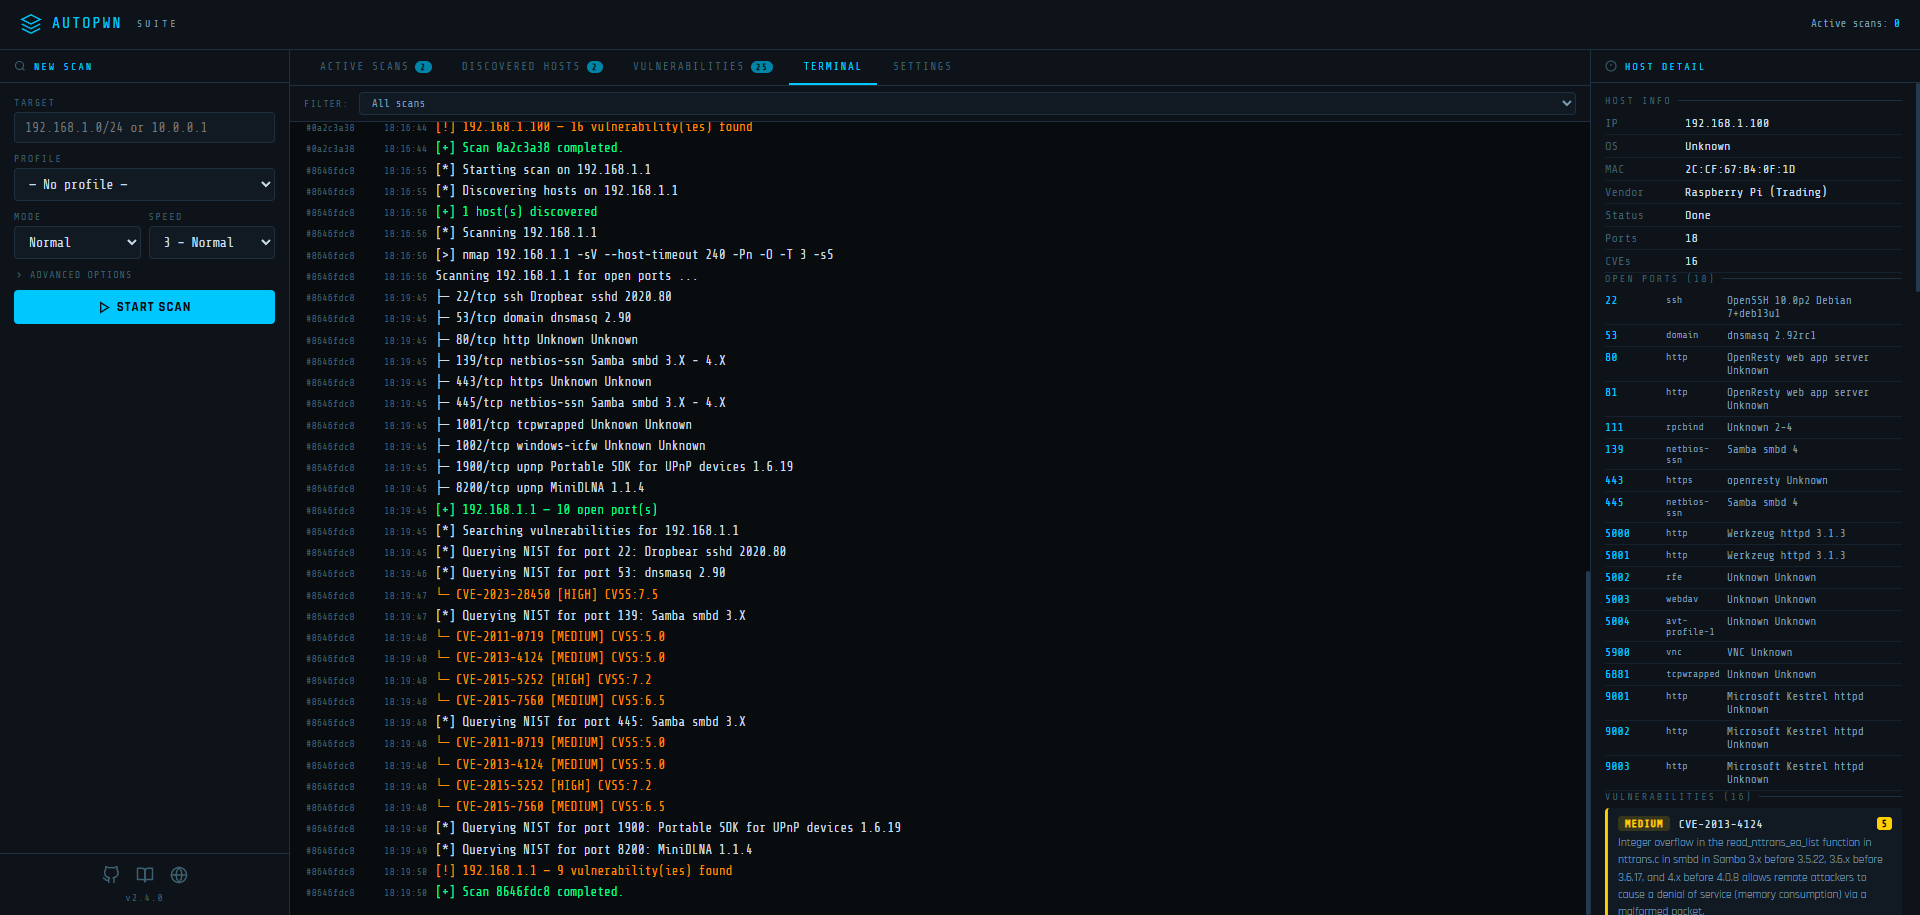 gamehunterkaan/autopwn-suite
AutoPWN Suite is a project for scanning vulnerabilities and exploiting systems automatically.
 sh4den/cve-2025-49493
This is a Python-based exploit for CVE-2025-49493, which affects Akamai CloudTest versions before 60 2025.06.02 (12988). The vulnerability allows for…
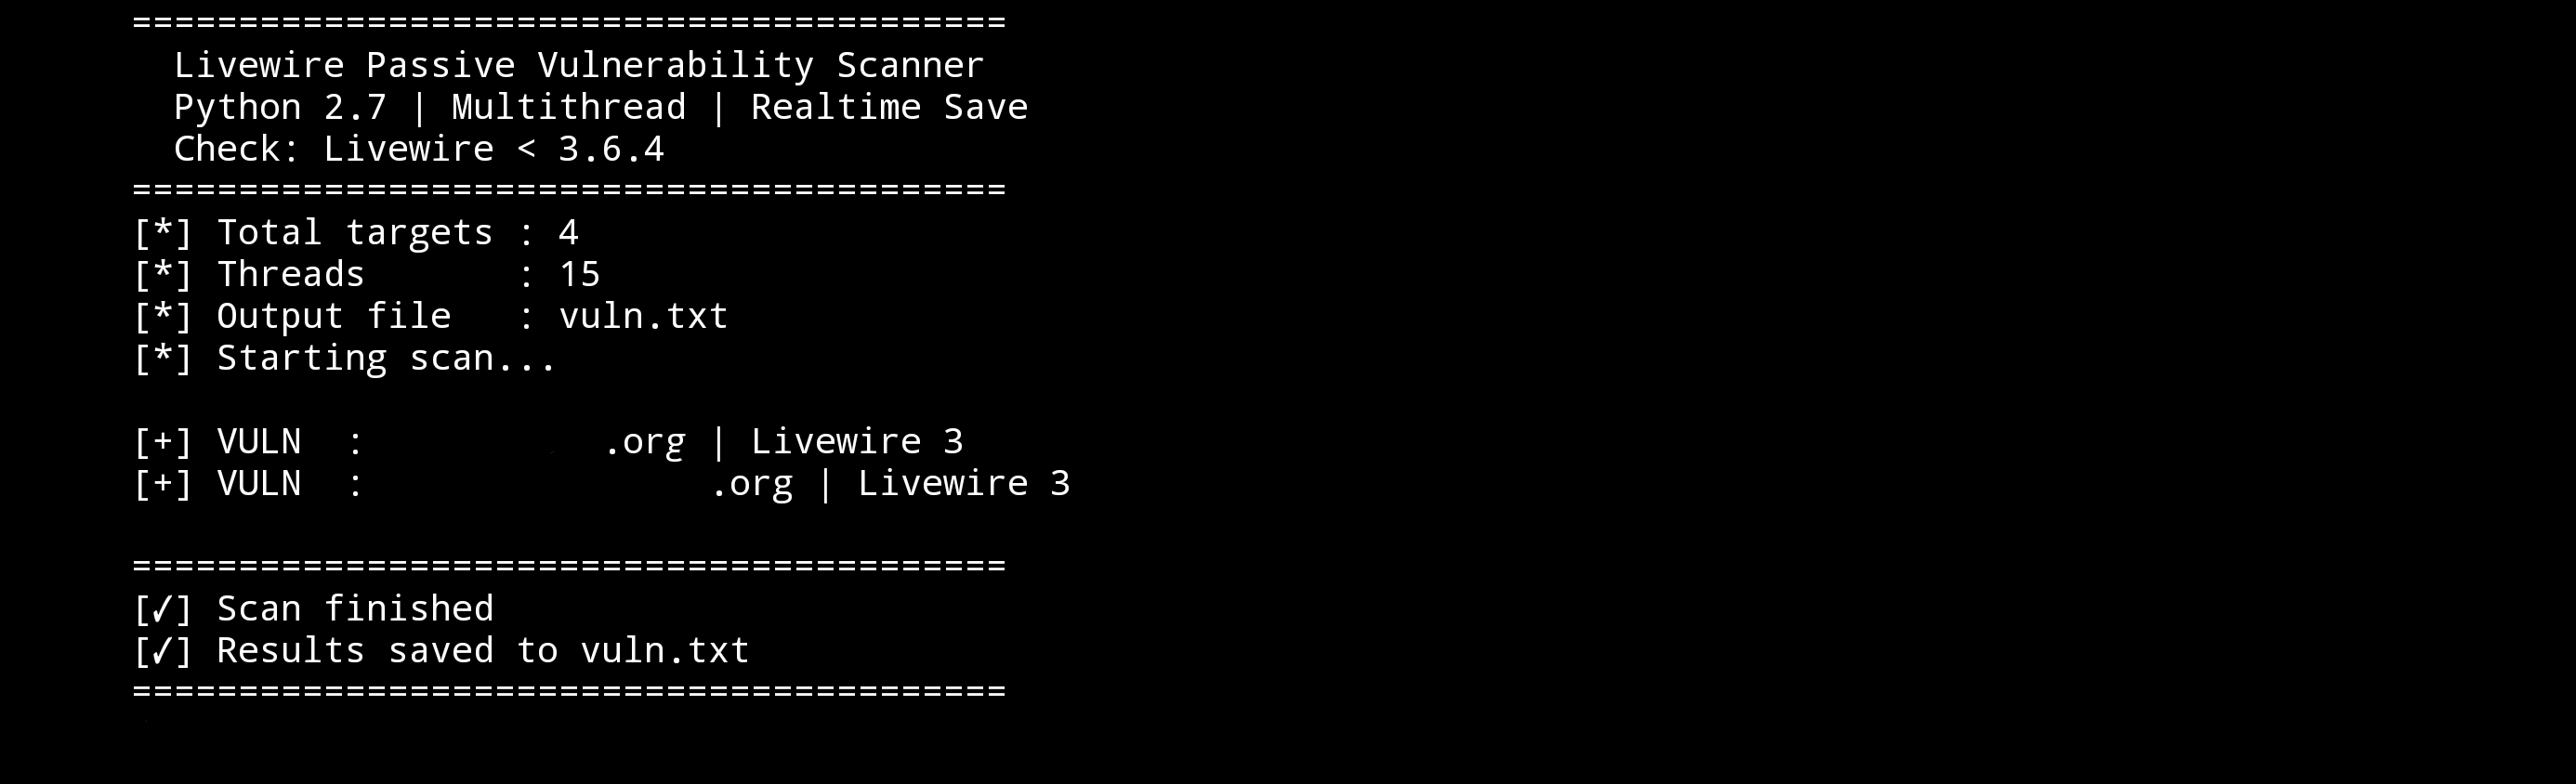 jenderal92/livewire-vuln-scanner
Simple scanner to detect vulnerable Livewire installations.
 hann1bl3l3ct3r/fuxapwn
POC exploit for CVE-2026-25895 FUXA Unauthenticated Path Traversal -> Arbitrary File Write -> RCE
 kouf320/docker-lab-cve-2017-5638-cve-2021-41773
Docker-based multi-stage attack emulation lab demonstrating CVE-2017-5638 and CVE-2021-41773 exploitation, lateral movement, and Suricata IDS…
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 d4rkmatt3r/kyoceracredsdump
Kyocera cred dumper based on CVE-2022-1026
 tjoulel/wordpress-6.9.1-blind-ssrf
Based on CVE-2022-3590, WordPress <= 6.9.1 - Unauthenticated Blind SSRF via XML-RPC Pingback Discovery proof of concept (PoC)
 oscar-mine/cve-2026-23980-exploit
Exploit for CVE-2026-23980 — Authenticated error-based SQL injection in Apache Superset < 6.0.0 via sqlExpression bypass
 inferiorak/cve-2025-55182-react2shell-async-scanner
Async RCE scanner for CVE-2025-55182 / CVE-2025-66478 — prototype-pollution → code execution via React Server Actions.
 l33tdawg/phantomrecon
PhantomRecon is a CLI-based, modular, agent-driven red team automation tool designed to demonstrate autonomous offensive security workflows powered…
 mverschu/cve-2017-7921
HikVision Auth Bypass CVE, tool is able to extract credentials, and take snapshots based on magic cookie or supplied credentials.
 shiva108/waes
CPH:SEC WAES: Web Auto Enum & Scanner - Auto enums website(s) and dumps files as result
 rxerium/cve-2024-12084
A heap-based buffer overflow flaw was found in the rsync daemon. This issue is due to improper handling of attacker-controlled checksum lengths…
 0nsec/cve-2023-35078
CVE-2023-35078 - Ivanti MobileIron Core Remote Unauthenticated API Access Exploit tool
 yucaerin/cve-2024-55555
Laravel Crypto Killer Mass Scanner (CVE-2024-55555)