

dddd
 sleepingbag945/dddd
Batch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…
fingerprint-spoofinginformation-gatheringnetwork-mapping+9
1.9k
sleepingbag945/ddddBatch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…
 saqibnet/blackbox-pentesting-infsecos
Full black-box penetration test against SecOS:1 (VulnHub) — CSRF exploitation, privilege escalation via CVE-2015-1328 (OverlayFS), post-exploitation

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 cyeezy08/kimai-cve-2026-52824-poc
PoC exploits for CVE-2026-52824 (GHSA-jr9p-4h4j-6c58) — Kimai time-tracking default APP_SECRET authentication bypass affecting versions ≤ 2.57.0
 qyvora/qyvora-anansi
Terminal-first attack surface intelligence engine. Built for speed, portability, and raw technical signal.
 ferpalma21/nextjs-scanner
This script scans a list of URLs to detect if they are using **Next.js** and determines whether they are vulnerable to **CVE-2025-29927**. It…
 piratesshield/apiharvester
The one shot API attacker tool - finds the API url from the given root simulate the automated attacks
 murrez/cve-2026-102425
Python PoC for CVE-2026-102425: unauthenticated RCE in Joomla Balbooa Forms (com_baforms) via field shortcode injection in post-submission PHP…
 murrez/cve-2026-101894
Python PoC for CVE-2026-101894: symlink-chain path traversal in @xhmikosr/decompress. Includes local Node lab, lockfile version scan, and mass…
 murrez/cve-2026-101110
Python 3 PoC and mass exploit for CVE-2026-101110, an unauthenticated ORDER BY SQL injection in OrdaSoft Joomla Book Library <=6.4.6 via…
 murrez/cve-2026-101108
Python 3 PoC and mass scanner for CVE-2026-101108, an unauthenticated ORDER BY SQL injection in OrdaSoft Joomla Vehicle Manager <=6.5.7…
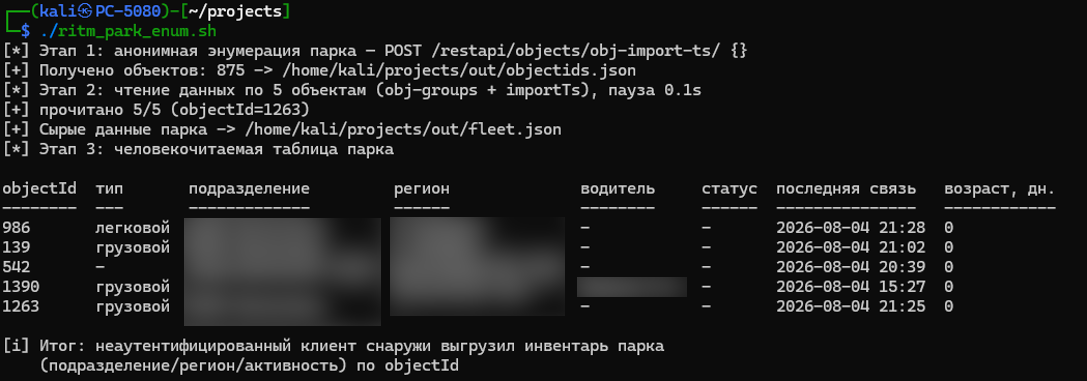 4ybrick/cve-2026-100903
PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.
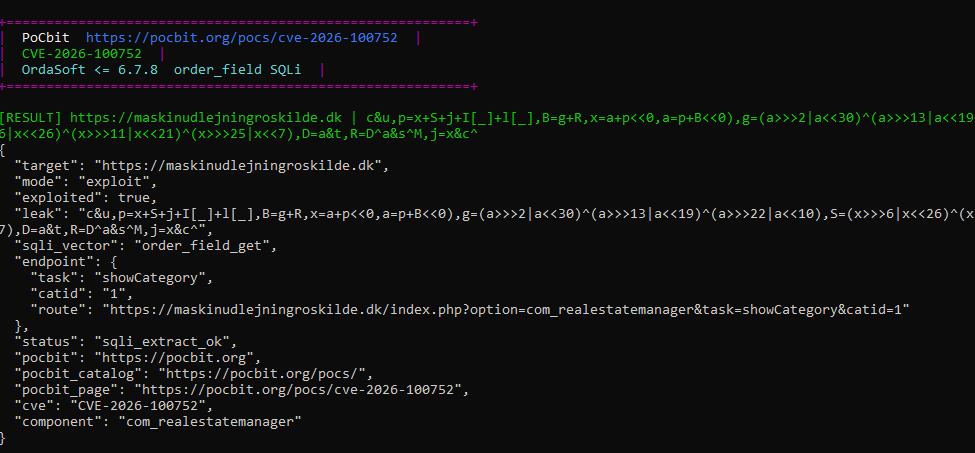 murrez/cve-2026-100752
Python 3 PoC and mass exploit for CVE-2026-100752, an unauthenticated SQL injection in OrdaSoft Joomla Real Estate Manager <=6.7.8 via the…
 murrez/cve-2026-100721
Python PoC for CVE-2026-100721: detects and exploits vm2 <3.12.2 NodeVM external allowlist bypass, achieving sandbox escape and host RCE via local…
 murrez/cve-2026-14378
Python PoC scanner and exploit helper for CVE-2026-14378, an unauthenticated admin session takeover in the DevKit Pro WordPress plugin via forged…
 langz337/cve-2026-14281
Mass scanner and single-target exploit for CVE-2026-14281, an unauthenticated privilege escalation in the WordPress Automation Web Platform plugin…
 abatsakidis/cve-2026-14281-check
A Windows-friendly, non-destructive Python checker for detecting WordPress installations potentially affected by CVE-2026-14281.
 murrez/cve-2026-13249
Unauthenticated arbitrary file upload on Honeywell PD45 web admin (firmware F10.19.010040–before F10.22.030745) leading to RCE. Python check/exploit…