
findcdn
 cisagov/findcdn
Scans domains to identify which Content Delivery Network (CDN) they use by fingerprinting HTTPS headers, CNAME records, and WHOIS data, with JSON…
dns-analysisfingerprint-spoofinginformation-gathering+4
123
cisagov/findcdnScans domains to identify which Content Delivery Network (CDN) they use by fingerprinting HTTPS headers, CNAME records, and WHOIS data, with JSON…
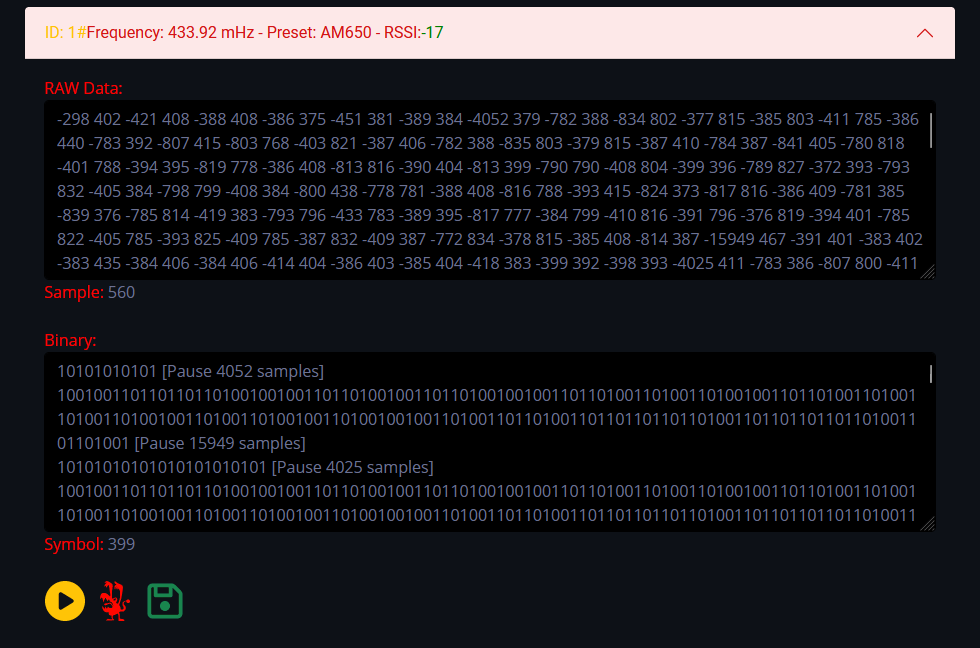 h-rat/evilcrowrf_custom_firmware_cc1101_flipperzero
This firmware is an alternative to the EvilCrowRF default firmware. Module: CC1101 - Compatible Flipper Zero file.
 btnz-k/emby_ssrf
Metasploit auxiliary module that identifies Emby Media Server version and exploits CVE-2020-26948 SSRF vulnerability to scan internal network…
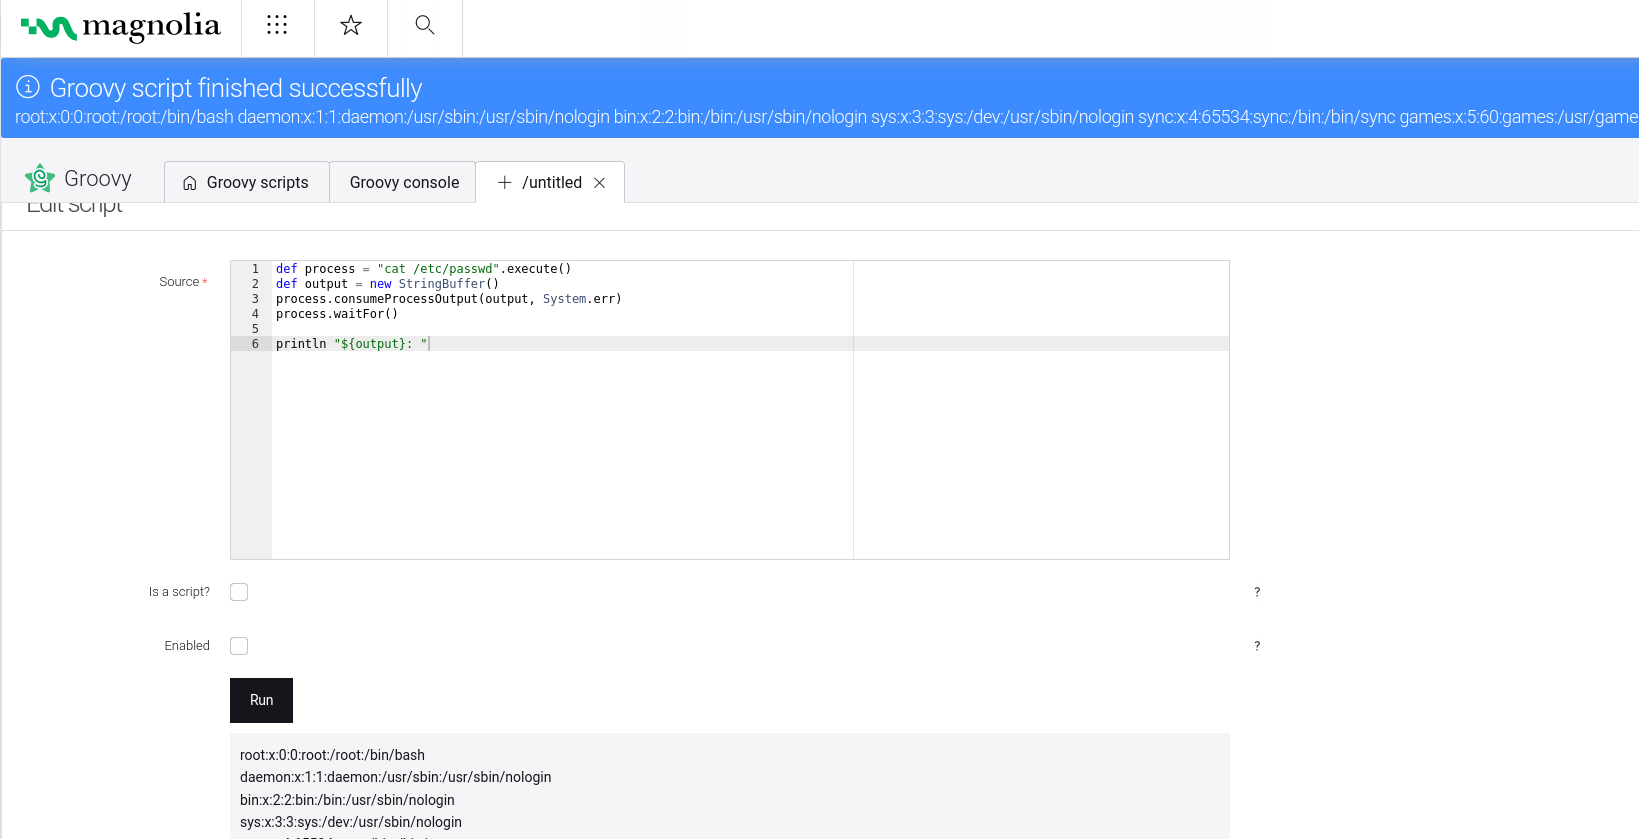 capture0x/magnolia-rce
AdminCentral Groovy module (magnolia-groovy module) in Magnolia DX Core 6.3.8.
 moften/cve-2022-41741-742-nginx-vulnerability-scanner
CVE-2022-41741/742 Nginx Vulnerability Scanner
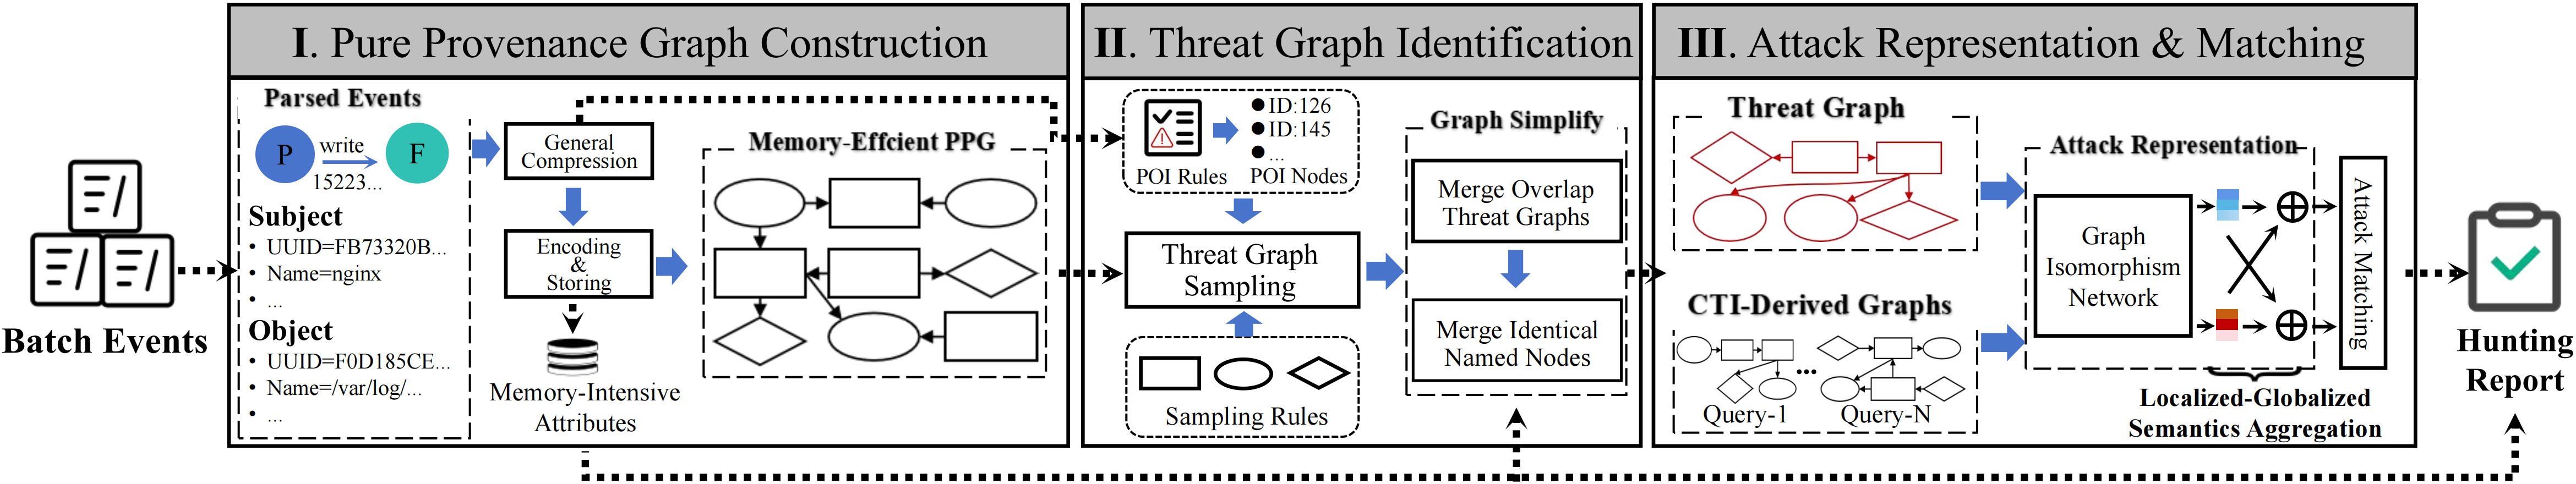 xueboqiu/prohunter
Graph-based threat detection system using inexact graph vector matching to compare threat graphs with CTI-derived attack query graphs for automated…
 jgalego/hiddensteps
HiddenSteps — a local-first personal workflow intelligence platform
 emilliewatson96/sprycve-2026-10520
Python-based exploit module targeting CVE-2026-10520 with automated payload delivery and vulnerability verification for penetration testing…
 nullt3r/rapiddns
Rapidly enumerate subdomains and domains using rapiddns.io.
 nuc13us/pulse
Pulse Secure VPN CVE-2019-11510
 hynekpetrak/detect_bluekeep.py
Python script to detect bluekeep vulnerability (CVE-2019-0708) with TLS/SSL and x509 support
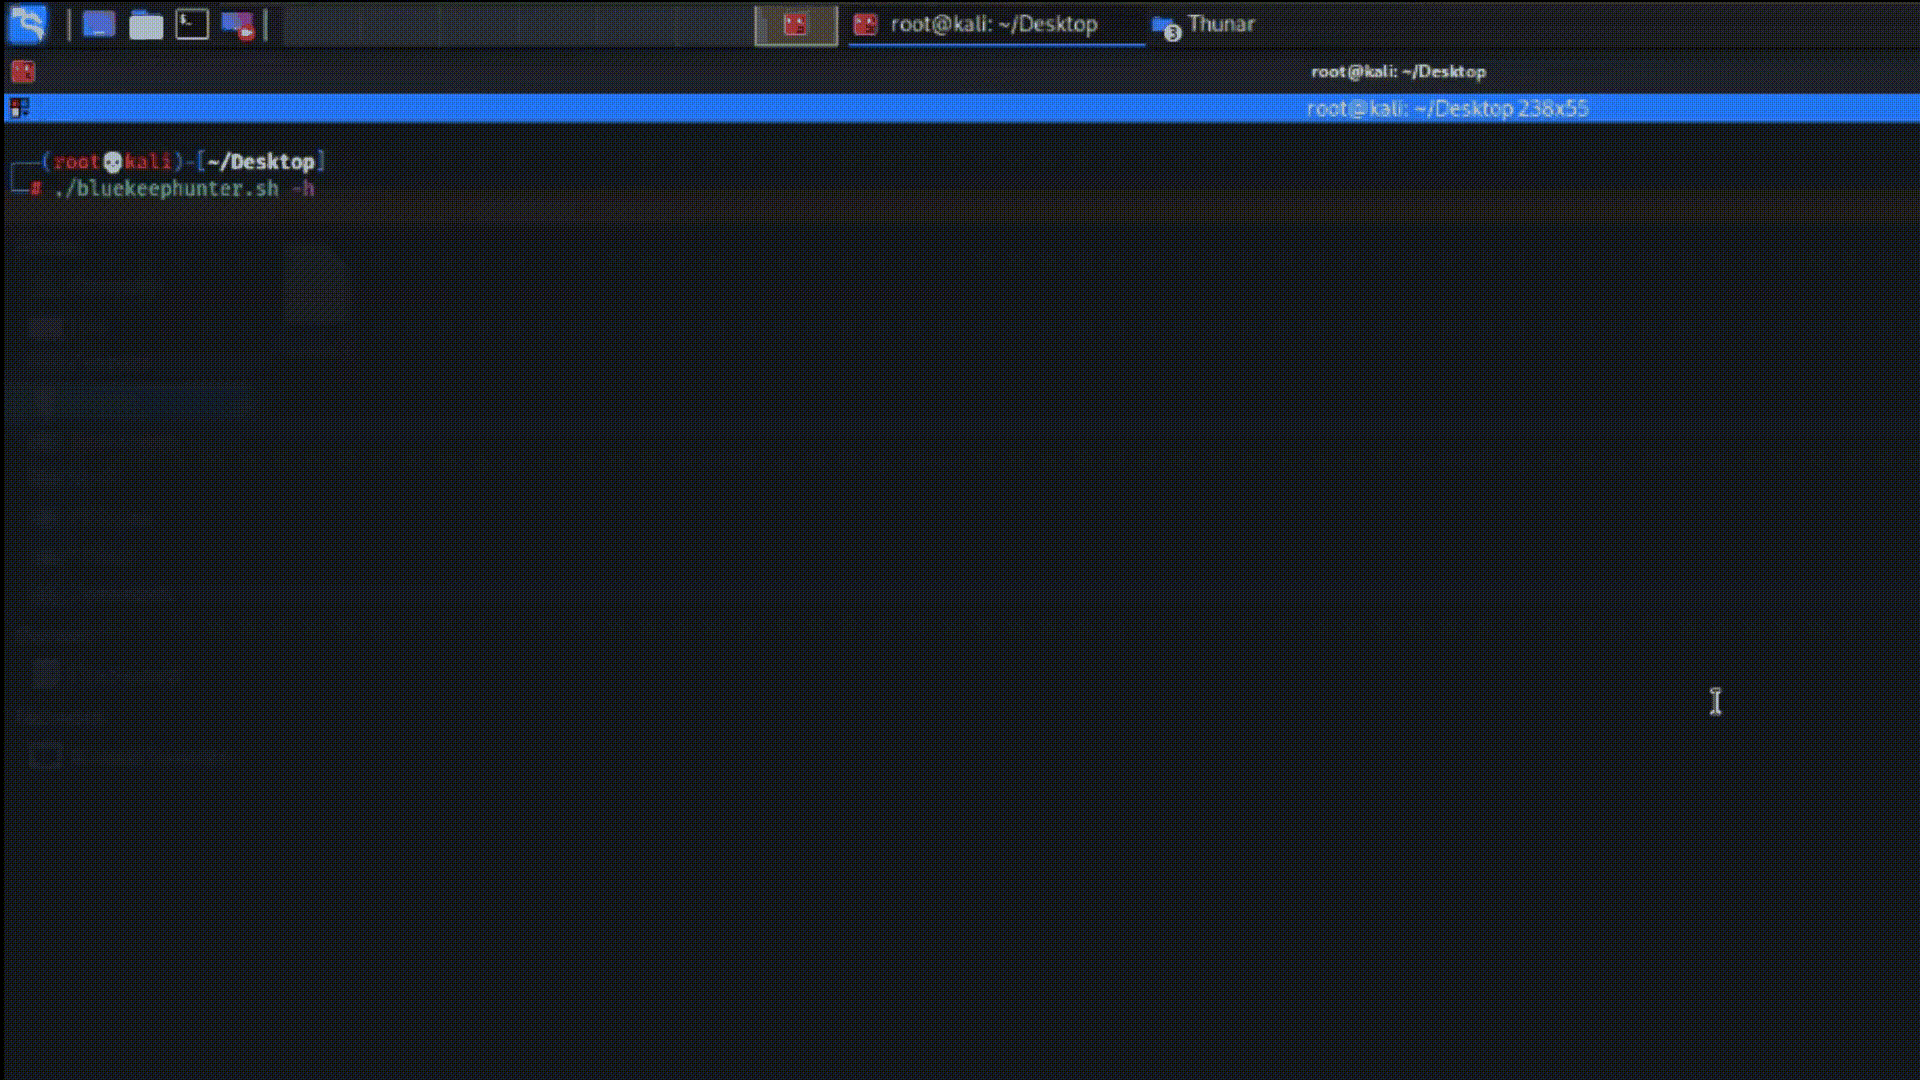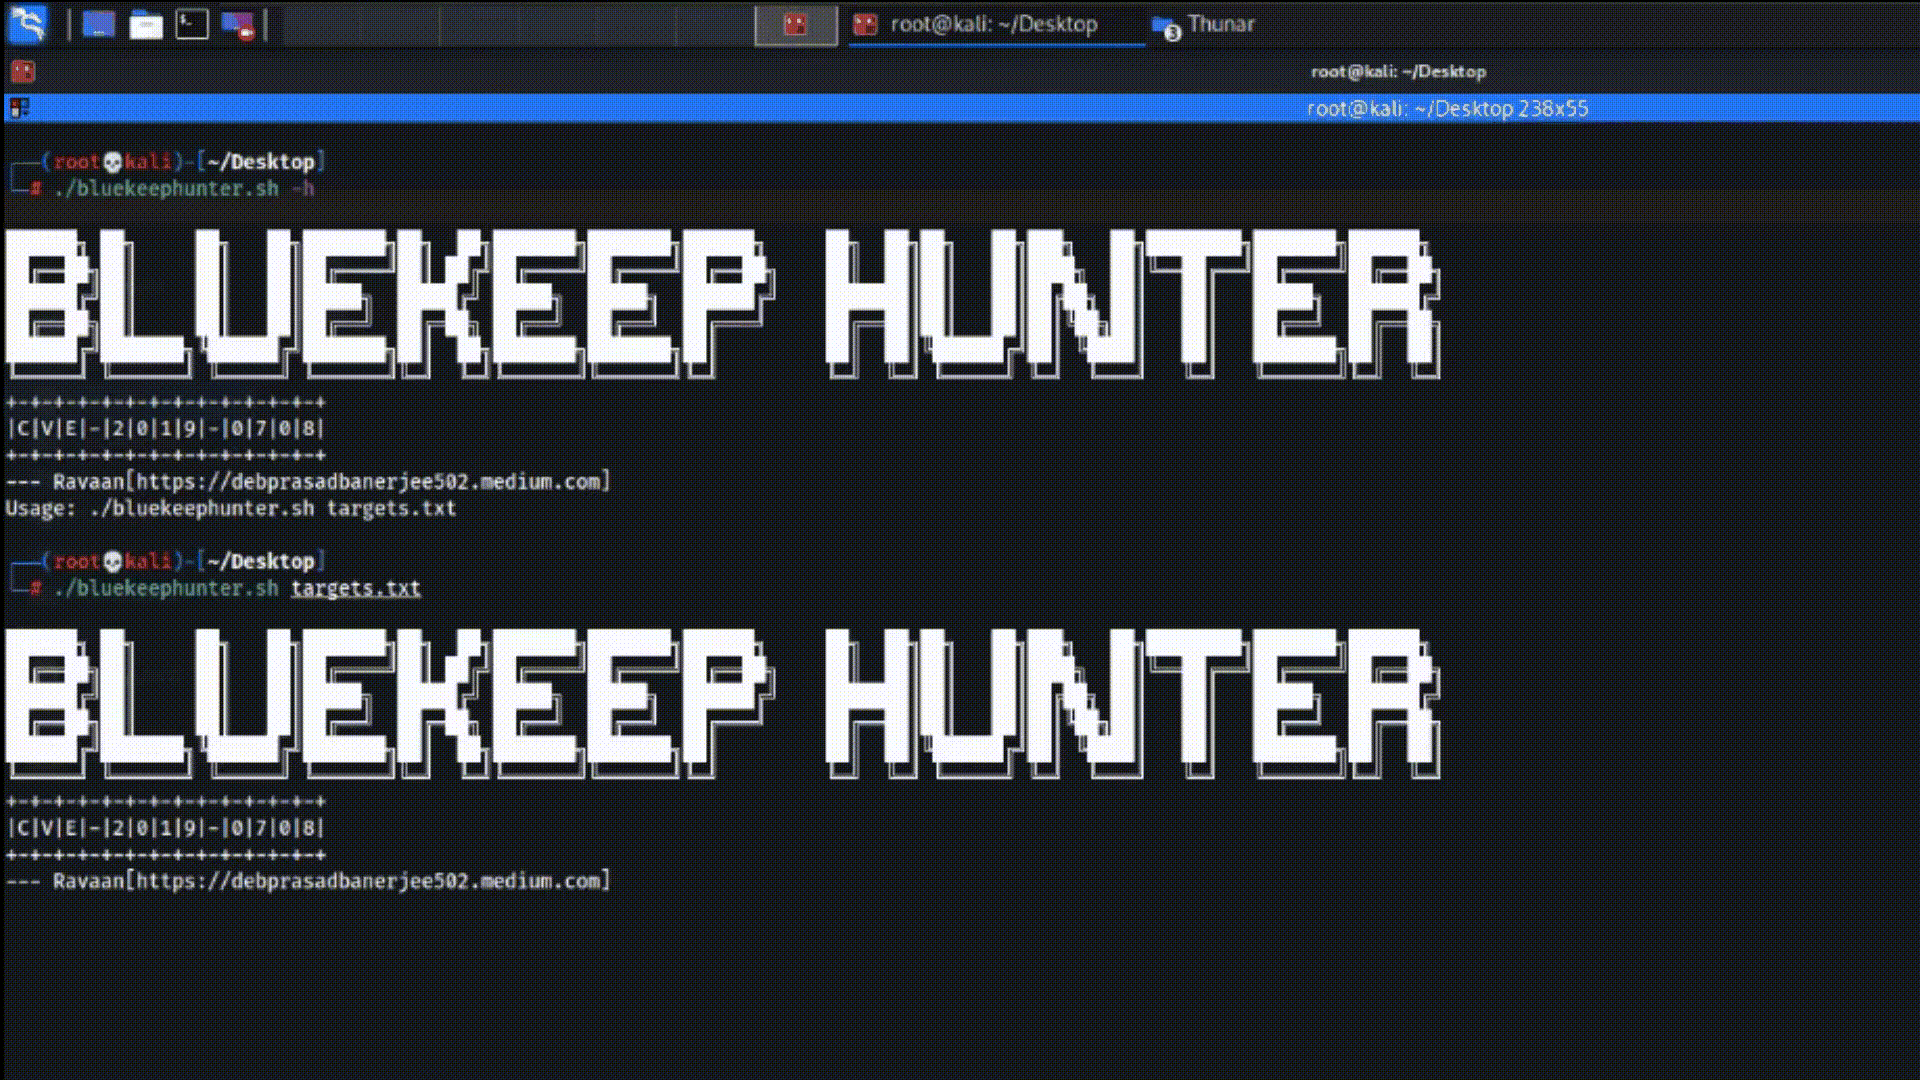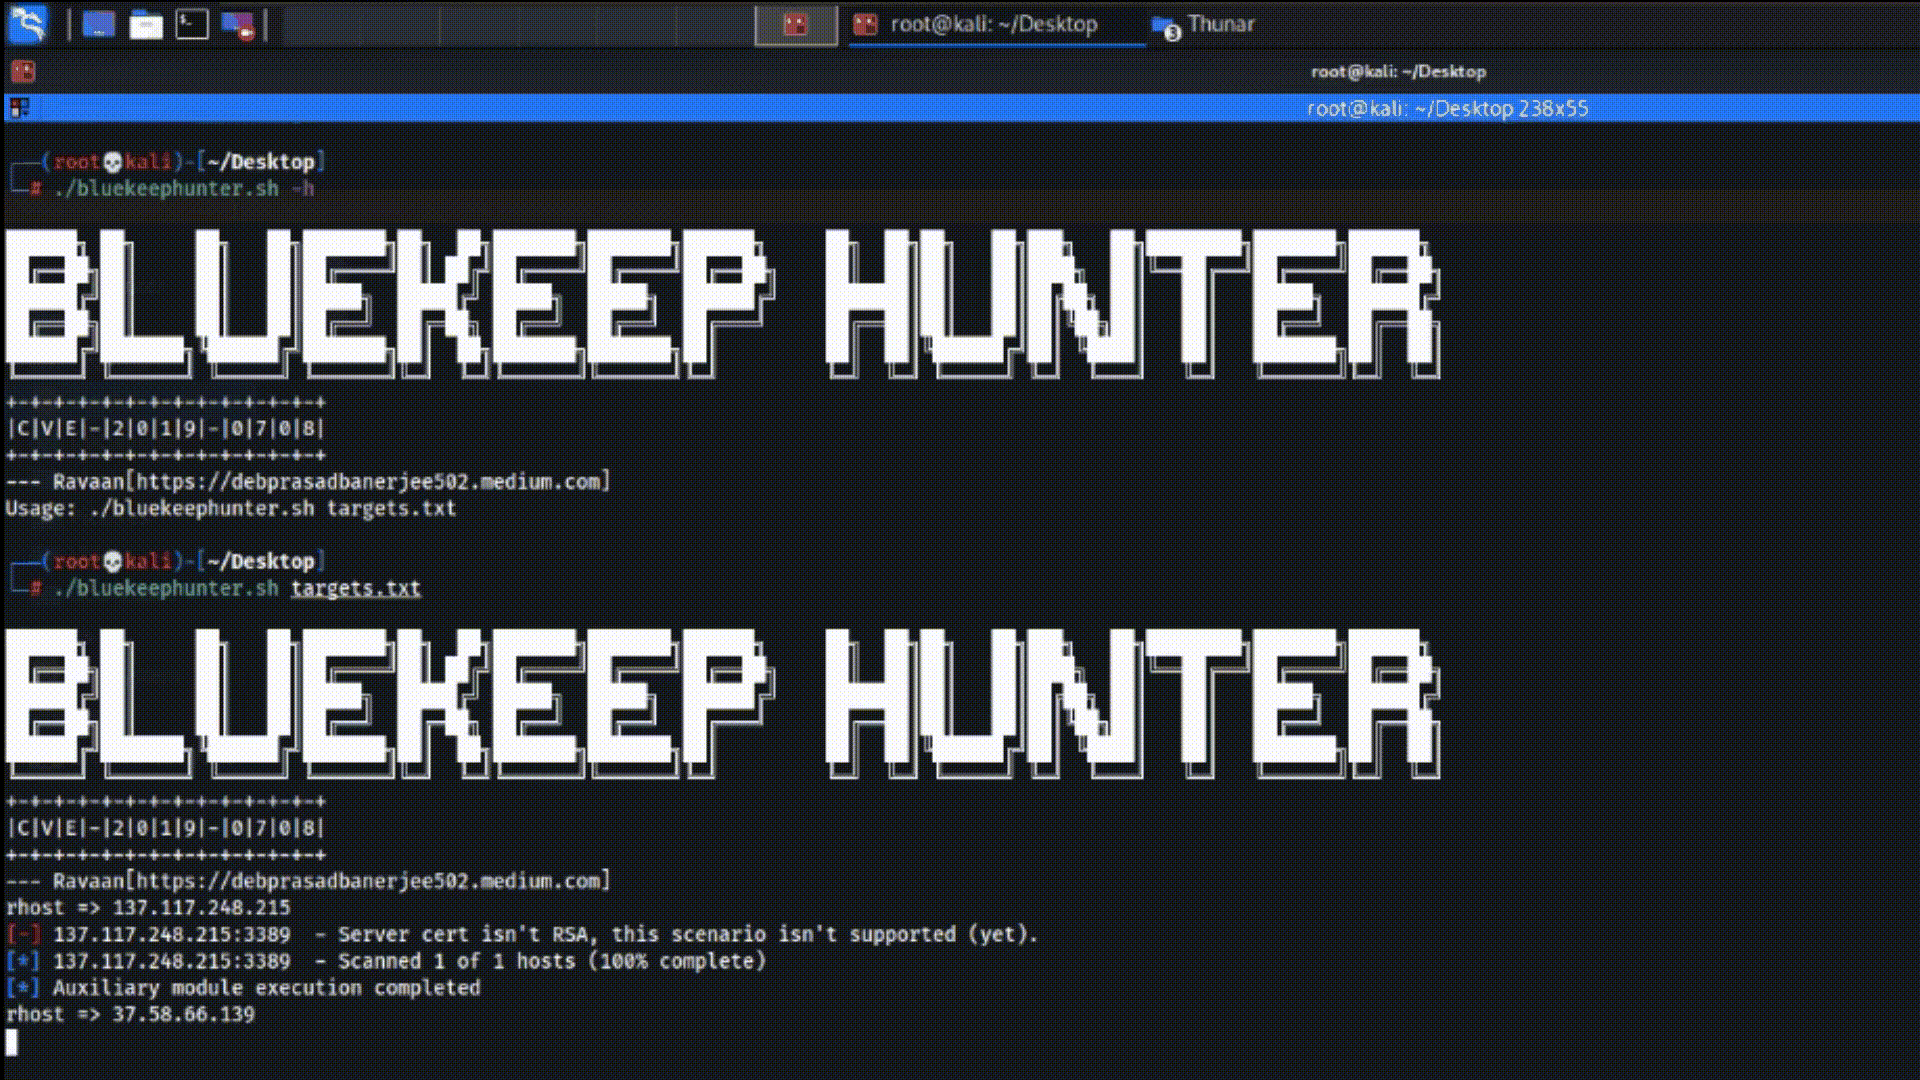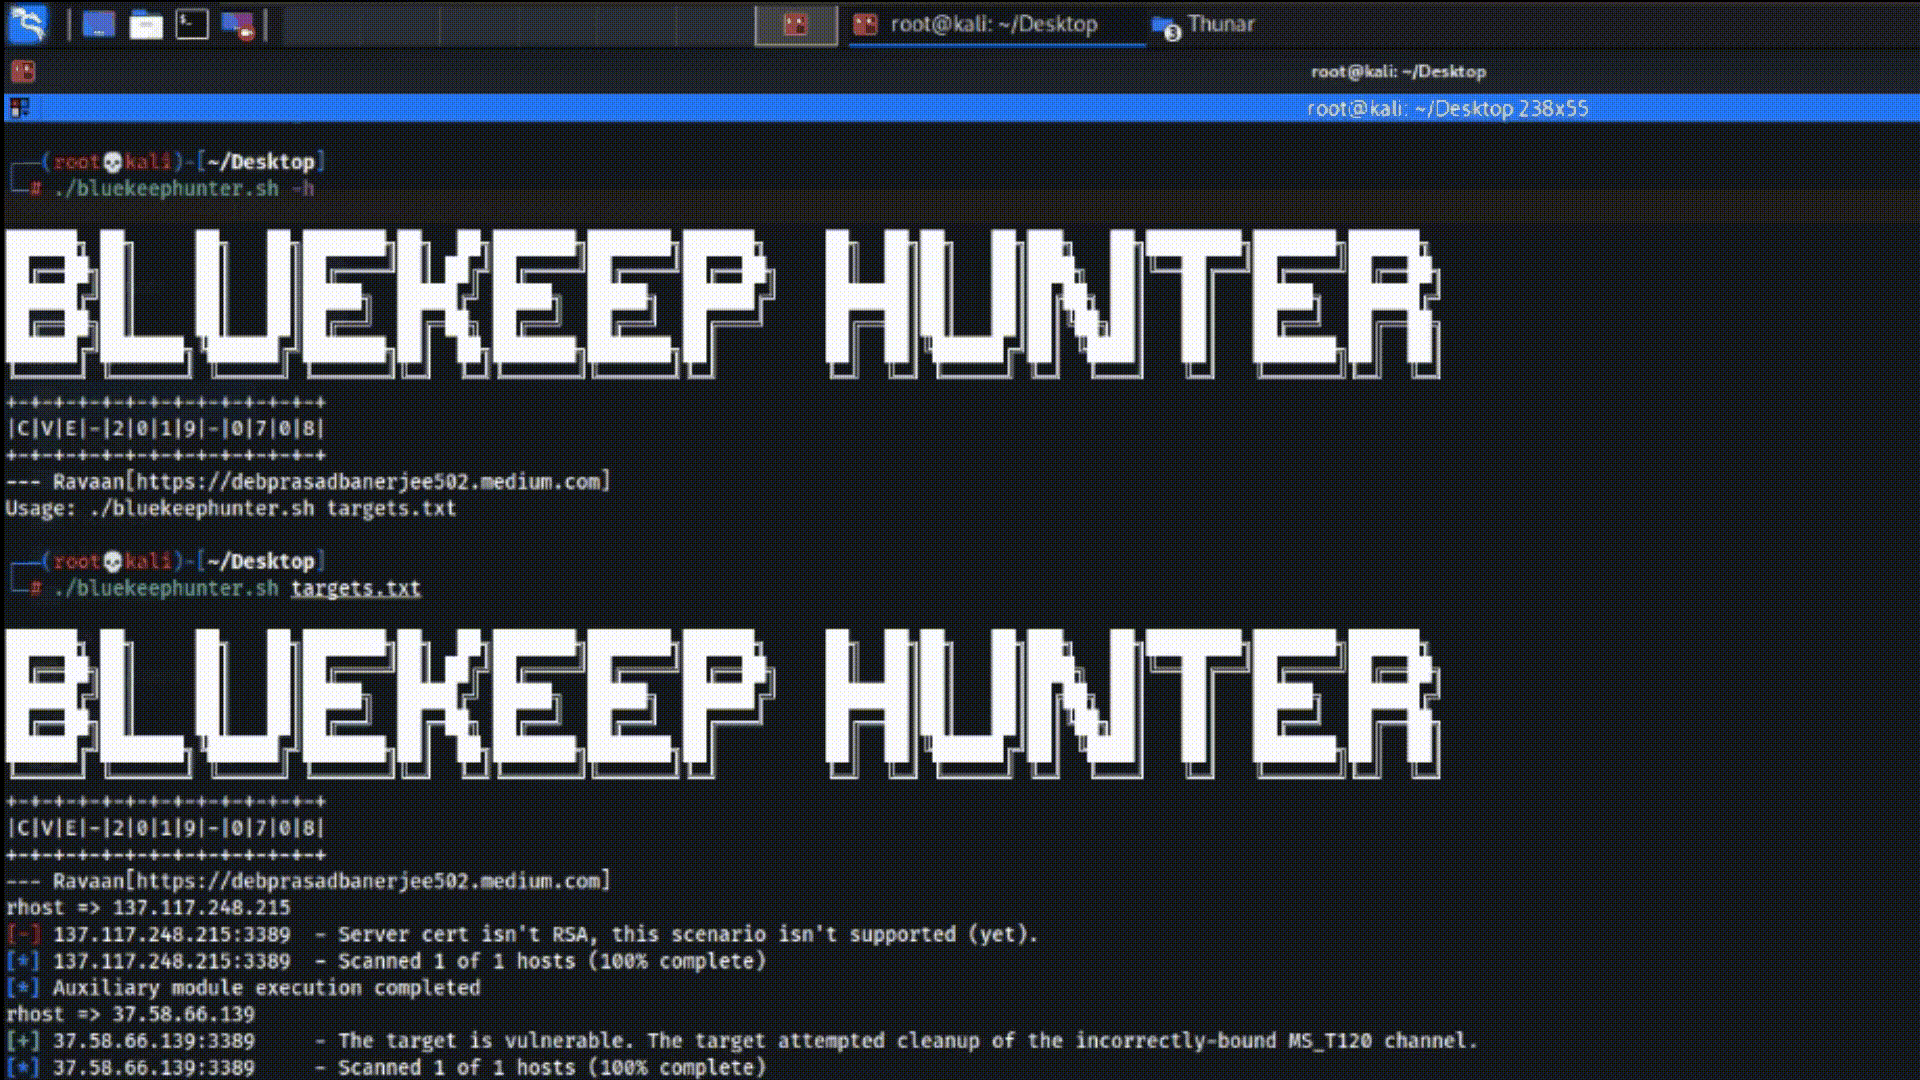 ravaan21/bluekeep-hunter
CVE-2019-0708, A tool which mass hunts for bluekeep vulnerability for exploitation.
 hynekpetrak/cve-2019-5544_cve-2020-3992
Python / scapy module implementing SRVLOC/SLP protocol and scans for enabled OpenSLP services.
 yukar1z0e/cve-2019-19781
Exploit module for CVE-2019-19781 targeting Citrix ADC, integrated with Router Scan for automated vulnerability scanning and exploitation.
 yukar1z0e/cve-2017-15944
Python-based exploit module for CVE-2017-15944 targeting routers, with automated scanning and API integration for Router Scan Project.
 mauricelambert/passwordssniffer
This module sniff username and password of unprotected protocols.
 devoteam-cybertrust/cve-2013-3319
metasploit module for CVE-2013-3319 / SAP Security Note 1816536
 bl4ck574r/cve-2019-17662
Exploit for CVE-2019-17662, a path traversal vulnerability in ThinVNC, demonstrating URL normalization bypass to access arbitrary files on the target…