

unwaf
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
dns-subdomain-enumerationinformation-gatheringnetwork-mapping+7
192
mmarting/unwafGo tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
 0xshe/fuck-cdn
Automated CDN origin-IP discovery skill for Claude Code that runs 40+ prioritized OSINT methods, cross-validates candidates via SSL and HTTP…
 murrez/hp-hplip-mass-cve-checker-2026-09-
Mass check/research exploit for HP HPLIP CVE-2026-91097–91106 (<3.26.6), PAPPL :8000 IPP probes + hpssd templates
 boydhacks/ntlmscout
Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
 luel-4013/misfortune-cookie
Interactive PoC suite for CVE-2014-9222 (Misfortune Cookie) and related router exploits, featuring detection, auth bypass, DoS, and RCE modules with…
 e4zyy/project-cve-2026-45833
Exploit tool for CVE-2026-45833 in ChromaDB, enabling malicious model generation, reconnaissance, and data exfiltration from target collections via…
 e4zyy/project-cve-2026-33017
CVE-2026-33017 - Langflow Unauthenticated RCE Exploit
 mad12wader/cve-2026-22812
Nuclei template for detecting and exploiting unauthenticated remote code execution in OpenCode via crafted HTTP requests.
 sachinart/cve-2025-61882
Multi-threaded scanner for CVE-2025-61882 in Oracle E-Business Suite, exploiting HTTP request smuggling to achieve unauthenticated remote code…
 kashkovsky/cve-2021-40438
Proof-of-concept exploit for CVE-2021-40438, an Apache HTTP Server mod_proxy vulnerability allowing request forwarding to arbitrary origins, with a…
 randomrobbiebf/subdomain-tko
Detects subdomain takeover vulnerabilities by analyzing DNS records and HTTP responses. Automatically identifies takeover-prone subdomains for…
 wattocyber/vegadns
Rust-based DNS enumeration and subdomain discovery tool for reconnaissance and penetration testing security assessments.
 wattocyber/cantina
OSCP-legal network recon orchestrator for port discovery, service classification, and enum-only plugin dispatch across HTTP, SMB, FTP, SNMP, SSH, and…
 tomnomnom/httprobe
Take a list of domains and probe for working HTTP and HTTPS servers
 sadprocessor/cypherdog
PoSh BloodHound Dog Whisperer
 pratham220/cve-2026-17543-php-exposure-validator
Safe PowerShell validator for PHP CVE-2026-17543 exposure via HTTP headers and non-destructive login-form probes.
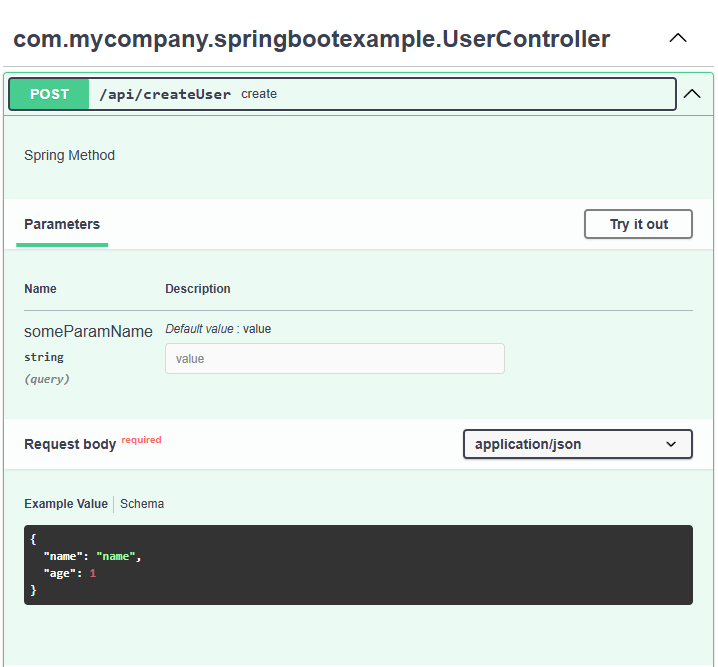 blackfan/bfscan
Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…
 btnz-k/emby_ssrf
Metasploit auxiliary module that identifies Emby Media Server version and exploits CVE-2020-26948 SSRF vulnerability to scan internal network…