azure-pentesting-suite

Go toolkit for authorized Azure security assessments: enumerates subscriptions and resources, audits misconfigurations, and attacks public Blob…

Go toolkit for authorized Azure security assessments: enumerates subscriptions and resources, audits misconfigurations, and attacks public Blob…

Enumerate Microsoft 365 Groups in a tenant with their metadata

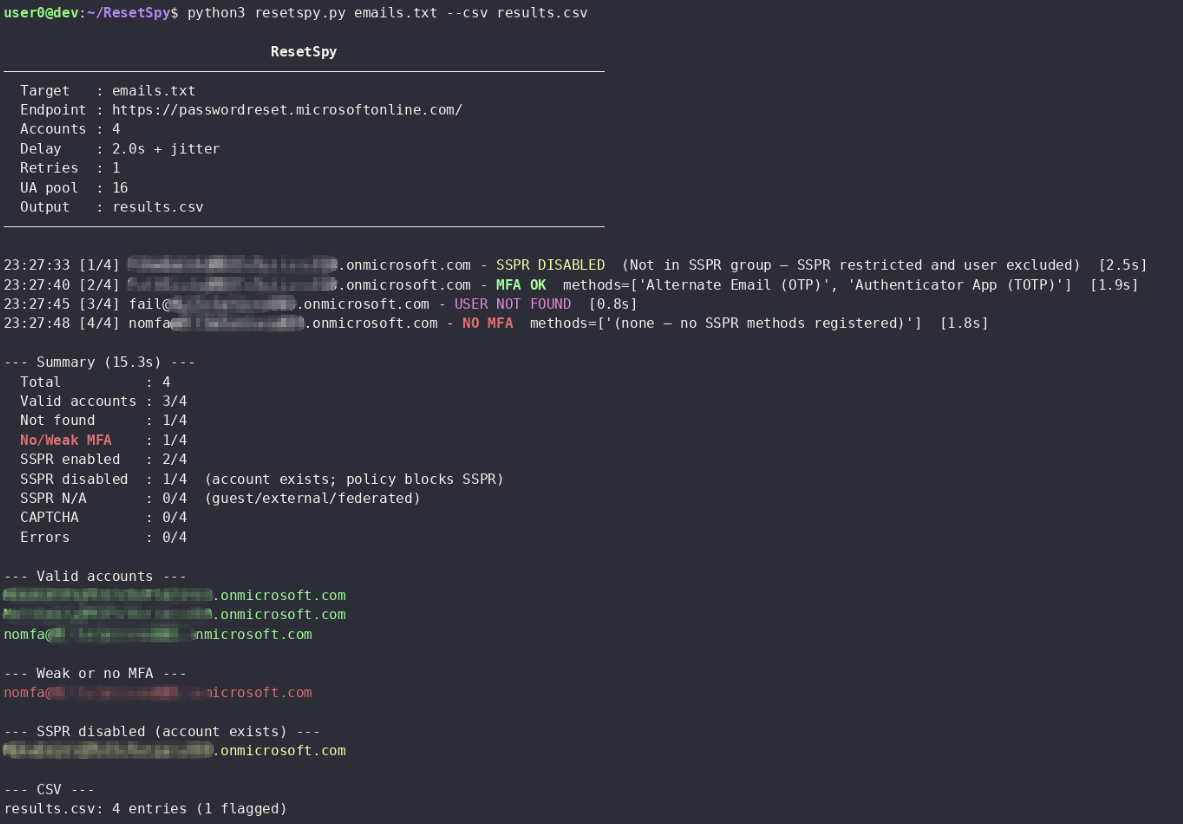
Enumerate user accounts and registered authentication methods via the Microsoft Self-Service Password Reset (SSPR) portal

PXEThief is a set of tooling that can extract passwords from the Operating System Deployment functionality in Microsoft Endpoint Configuration Manager

Curated collection of threat hunting and detection queries for CrowdStrike Falcon (CQL) and Microsoft Defender XDR (KQL), mapped to MITRE ATT&CK…

Microsoft Entra ID (Azure AD) Unauthenticated Enumeration

A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.

Microsoft-Outlook-Remote-Code-Execution-Vulnerability

Microsoft Network Service Fingerprinting Tool

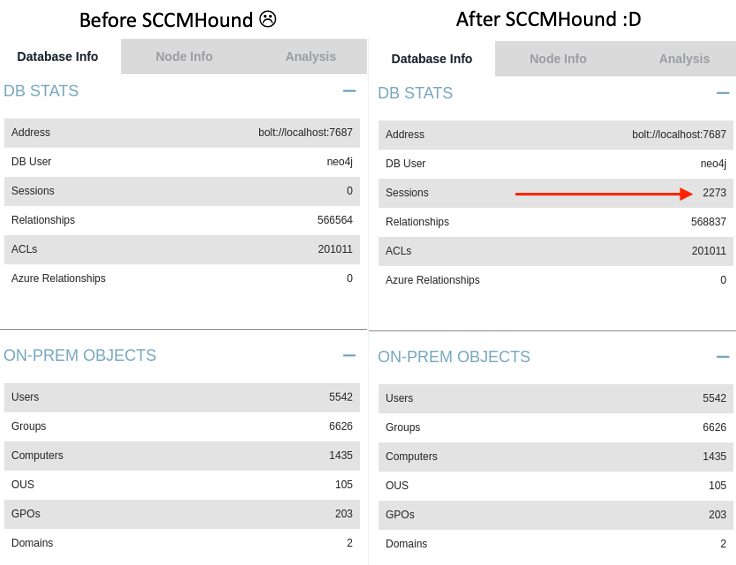
A BloodHound collector for Microsoft Configuration Manager

Automated scanner and exploit tool for CVE-2021-26855 targeting Microsoft Exchange servers, enabling remote code execution on vulnerable instances…

基于asyncio(协程)的CVE-2020-0796 速度还是十分可观的,方便运维师傅们对内网做下快速检测。

Enumerate valid users within Microsoft Teams and OneDrive with clean output.

A password spraying tool for Microsoft Online accounts (Azure/O365). The script logs if a user cred is valid, if MFA is enabled on the account, if a…

Misconfiguration Manager is a central knowledge base for all known Microsoft Configuration Manager tradecraft and associated defensive and hardening…

Proof-of-concept exploit for Microsoft SharePoint CVE-2026-55040 that forges JWT tokens, bypasses authentication, auto-discovers metadata, and…

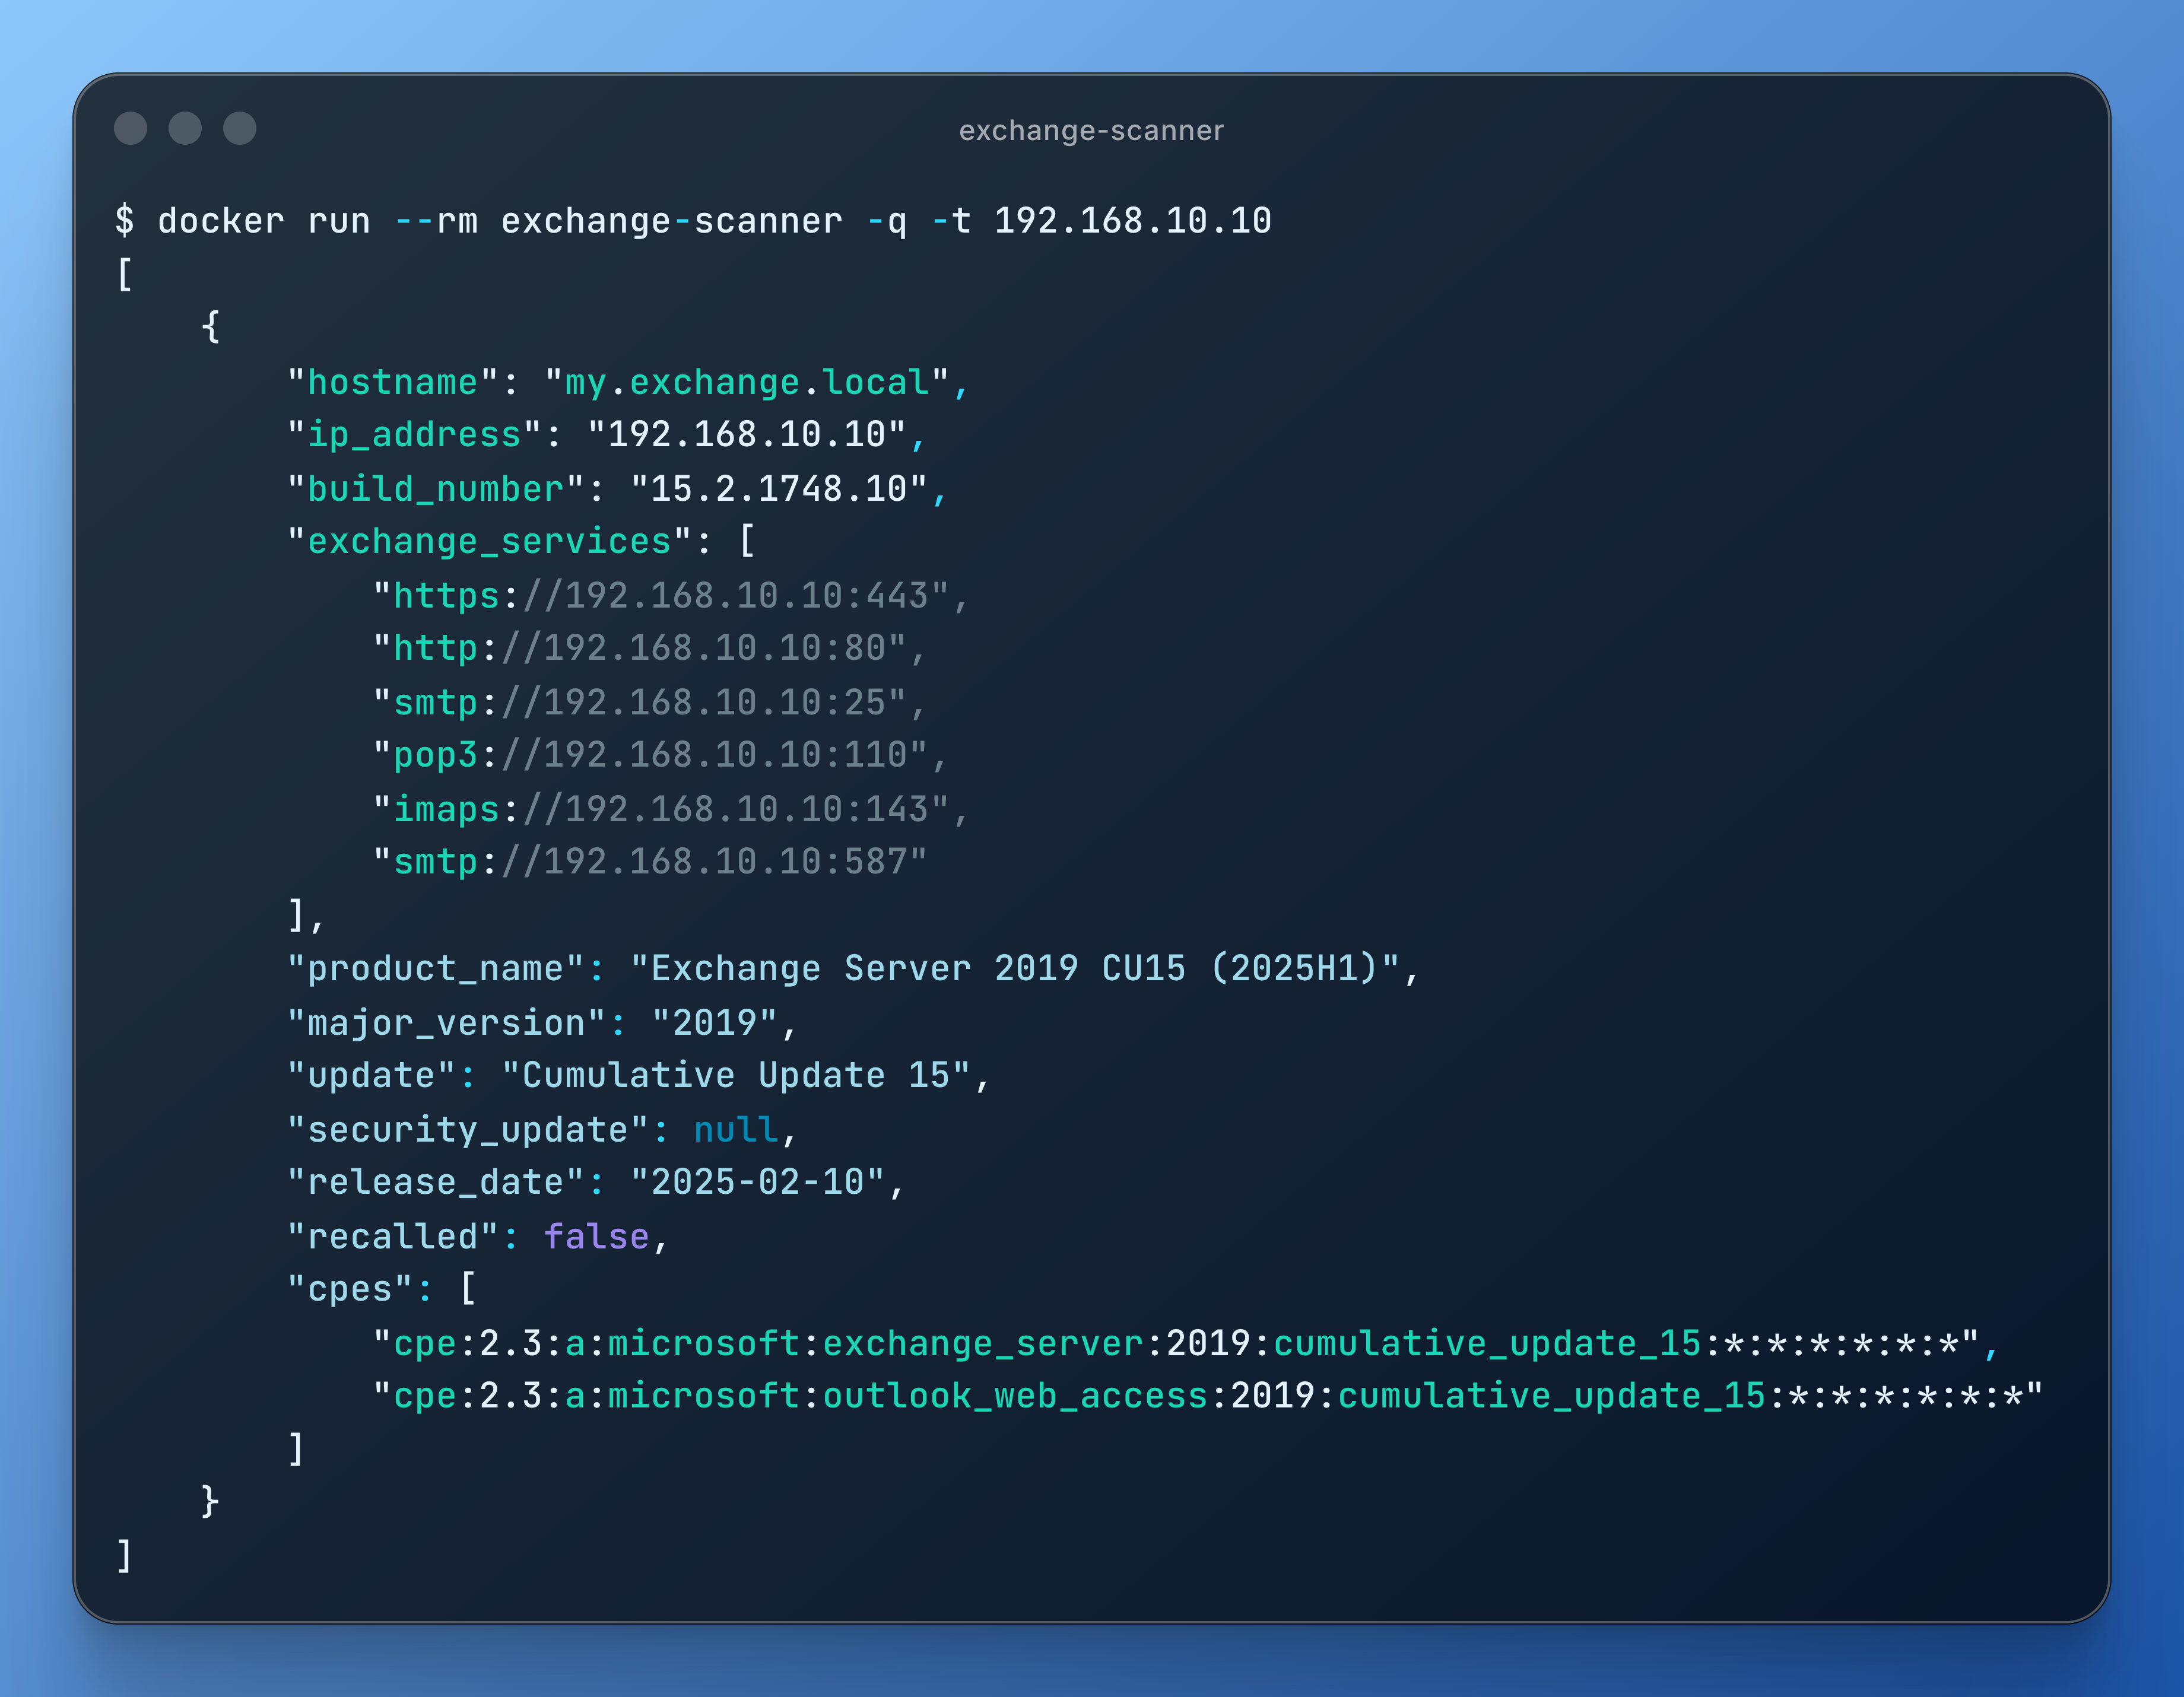
Identify public-facing Microsoft Exchange servers and determine their software versions

Powershell script to do domain auditing automation