

Awesome-Pentest
 kc57/awesome-pentest
A list of awesome penetration testing tools and resources.
cloud-securitycurated-resourceseducation+9
kc57/awesome-pentestA list of awesome penetration testing tools and resources.
 tamatahyt/cve-2026-53576
Kestra Unauthenticated RCE Exploit (CVE-2026-53576)
 ridpath/terrminus-cve-2026-2406
AsyncIO Scanner & Exploitation Framework for CVE-2026-24061 (Telnet NEW_ENVIRON Auth Bypass). Features high-concurrency discovery, passive…
 jenderal92/cve-2026-5118
CVE-2026-5118 – Python2 mass exploit for Divi WordPress plugin Unauthenticated administrator registration via admin-ajax.php. Multi‑threaded scanner…
 toxy4ny/copy-fail
Copy Fail - CVE-2026-31431 - Hardened C implementation for redteam and authorized penetration testing operations. ⚠️ Legal Notice: This tool is…
 johenlastgen-jlg/cve-2025-6325_cve-2025-6327
Python PoC validating CVE-2025-6325 unauthenticated privilege escalation and CVE-2025-6327 arbitrary file upload RCE in King Addons for Elementor <=…
 samratashok/kautilya
Kautilya - Tool for easy use of Human Interface Devices for offensive security and penetration testing.
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 cerberusmrxi/langflow-cve-2026-33017-exploit
CVE-2026-33017 exploitation tool for Langflow <1.9.0. Features reverse shells, command execution, file operations, persistence, and automated…
 ez4rd1x1/cve-2026-8181
Proof-of-concept exploit for CVE-2026-8181, an authentication bypass in the Burst Statistics WordPress plugin. Demonstrates remote, unauthenticated…
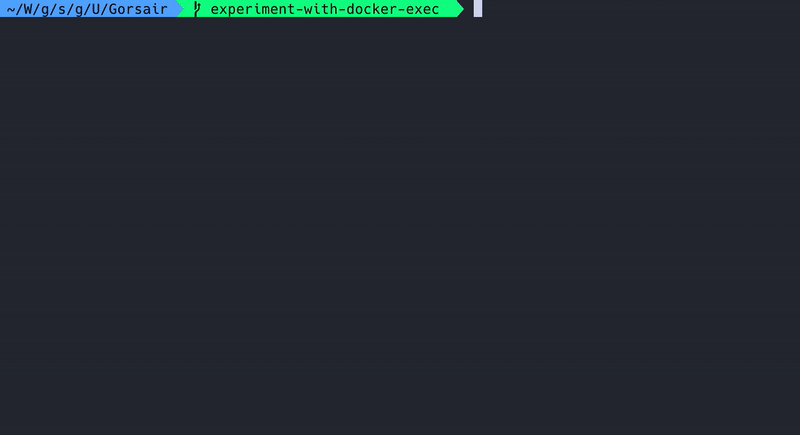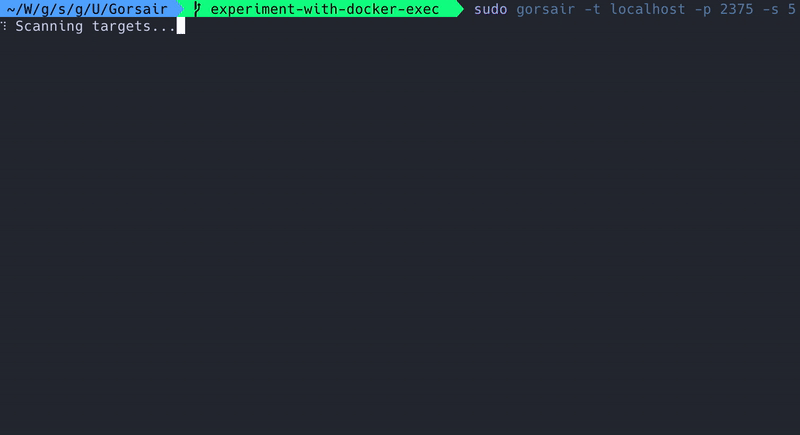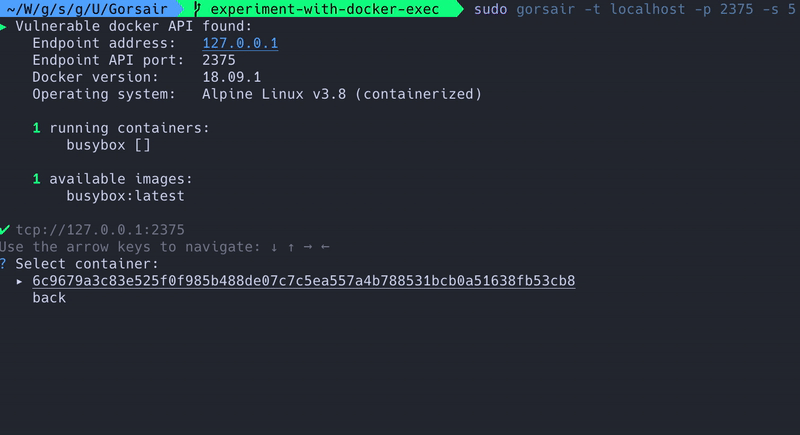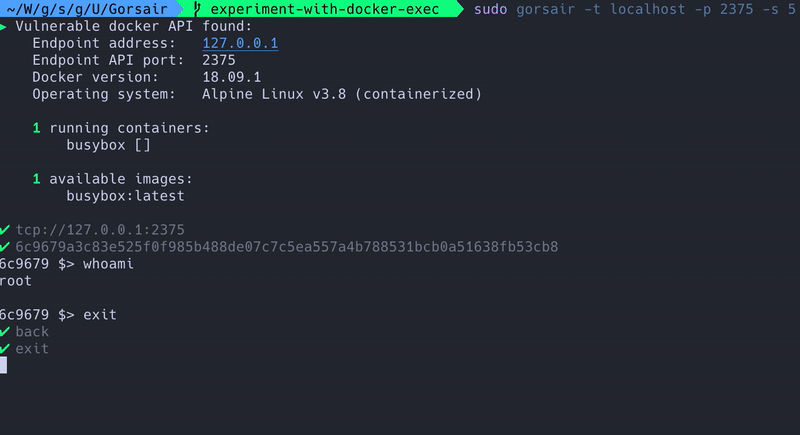 ullaakut/gorsair
Gorsair gives root access on remote docker containers that expose their APIs
 hackernese/sneakyexe
Automatic UAC-Bypassing for custom payloads during privilege escalation testing
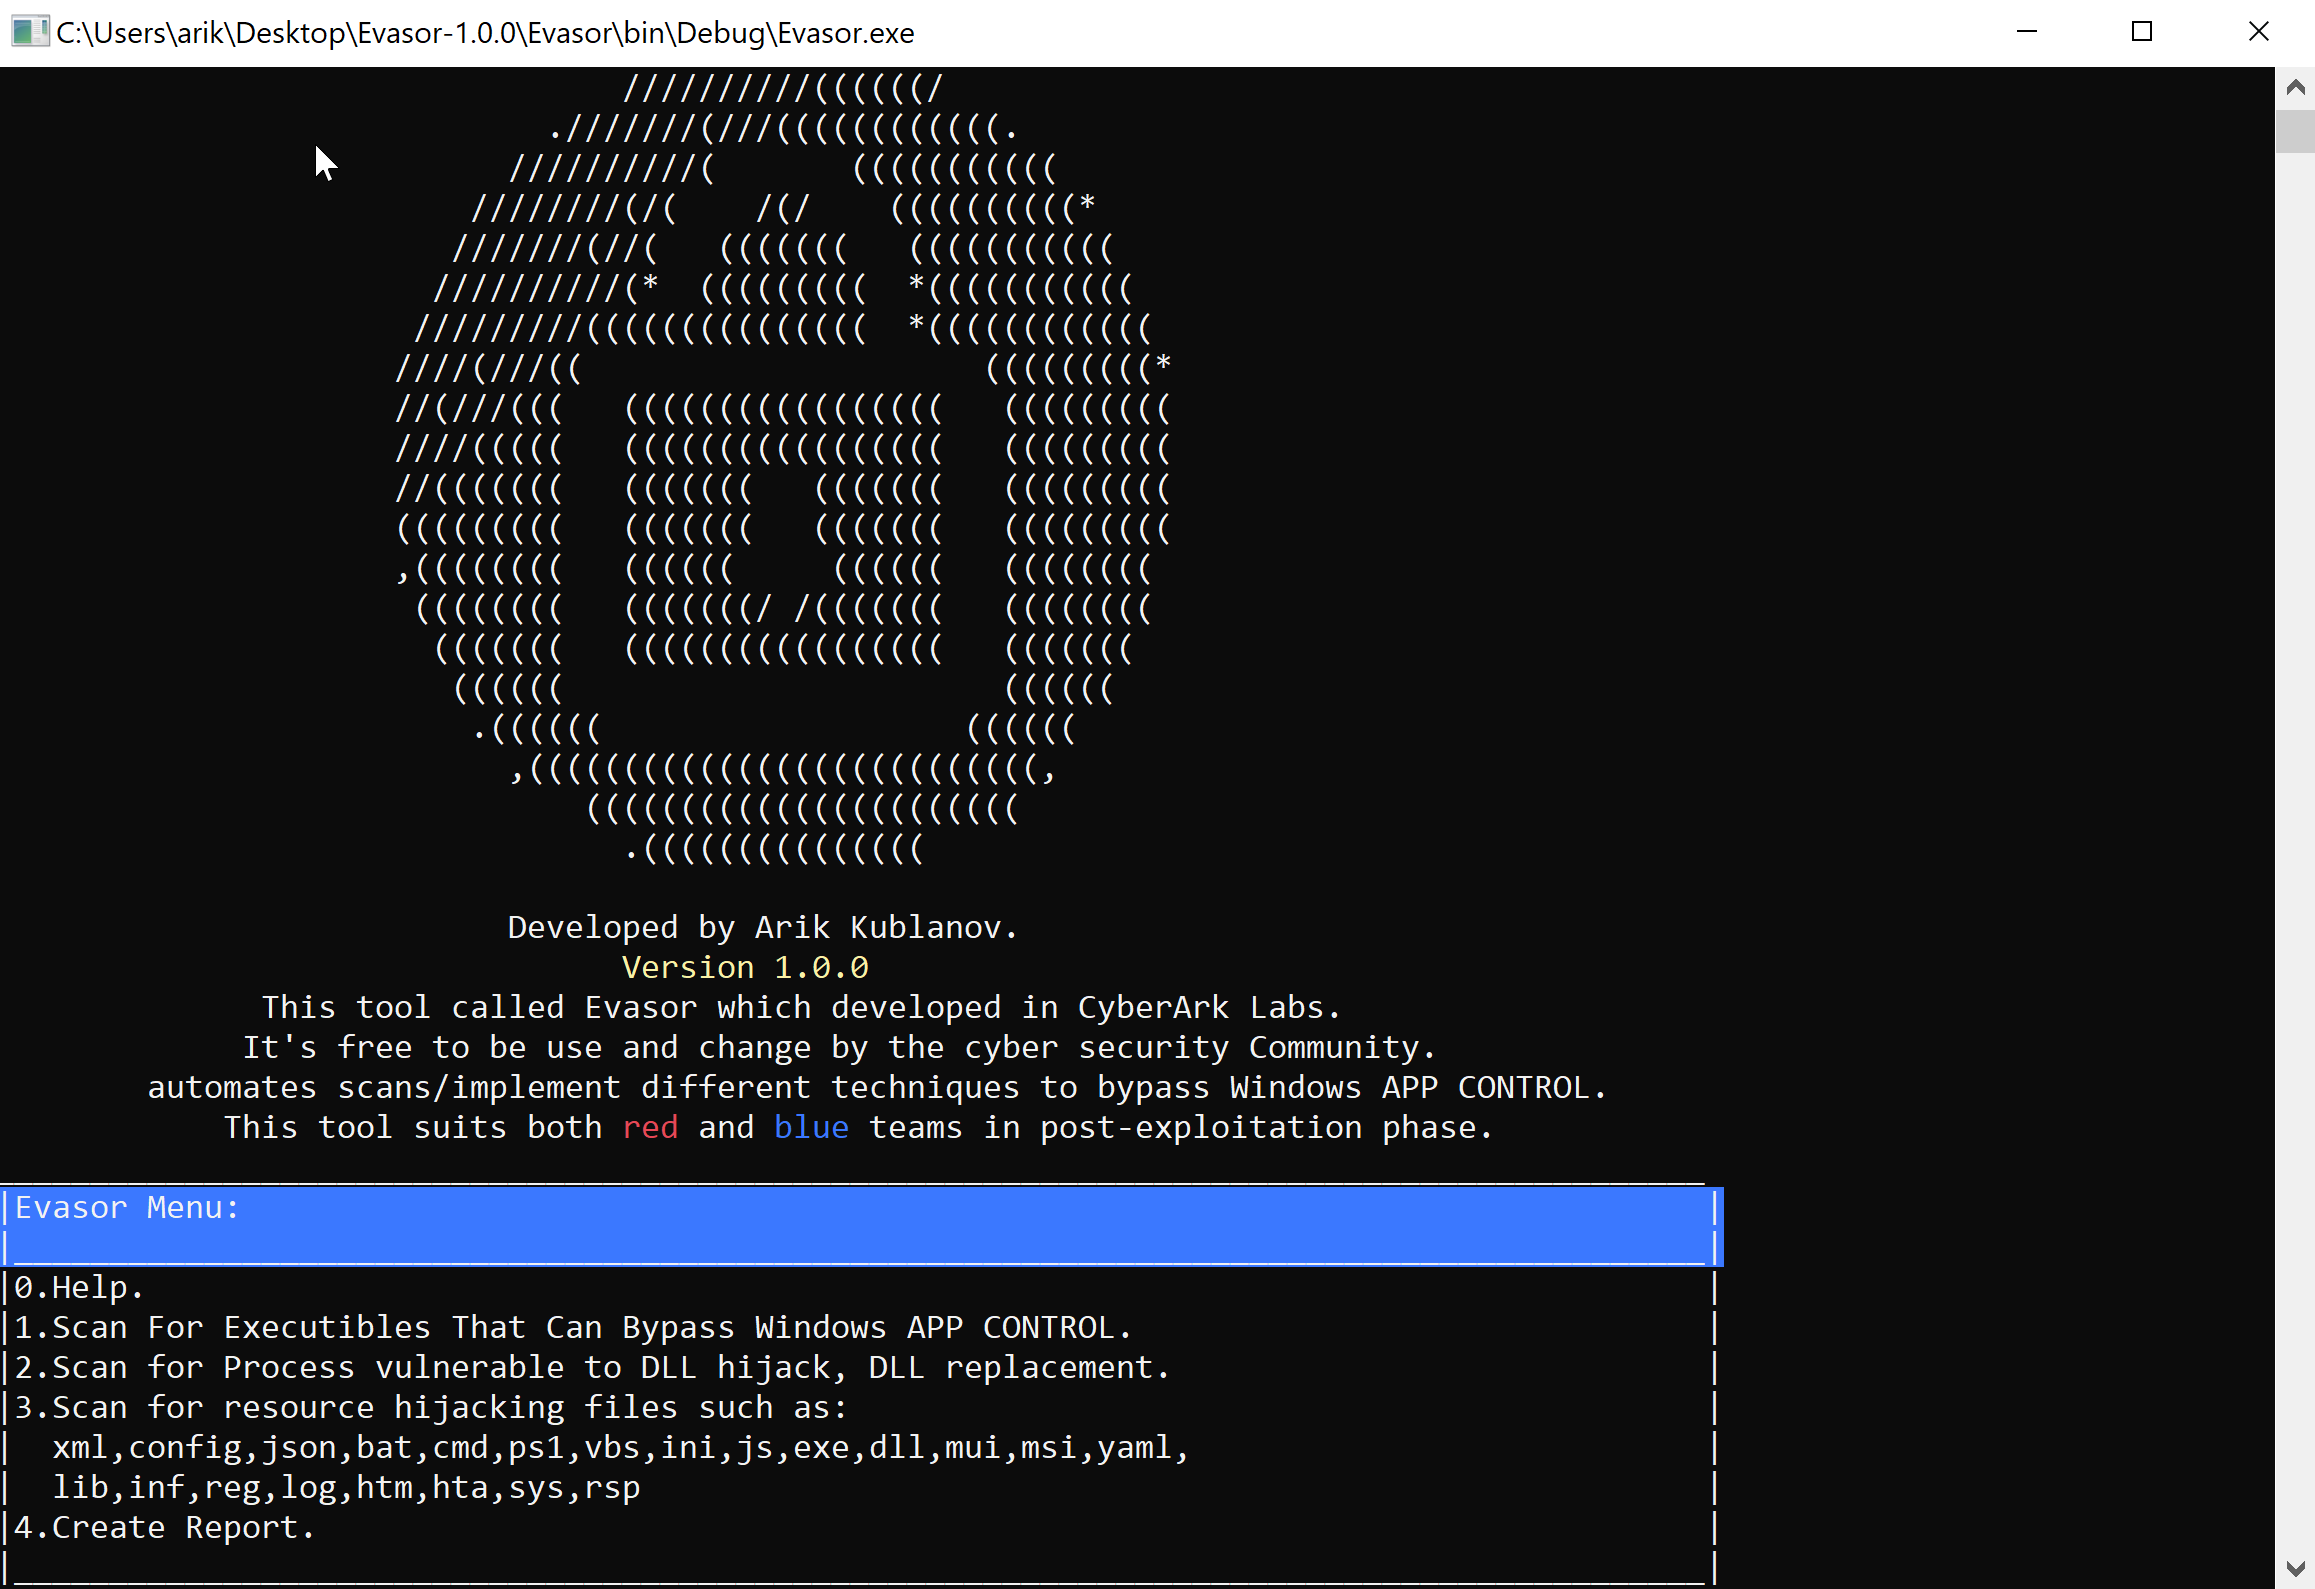 cyberark/evasor
A tool to be used in post exploitation phase for blue and red teams to bypass APPLICATIONCONTROL policies
 bishopfox/otto-support
An implementation of a vulnerable MCP server using mcp-go
 anthonyk2923/cve-2026-94609
Write-up and proof-of-concept for CVE-2026-94609, an authentik privilege-escalation flaw letting users with add_user_to_group join superuser groups…
 hakaioffsec/cve-2026-16764
Python exploit for CVE-2026-16764, a privilege escalation in OWASP DefectDojo where an is_staff REST API bypass lets a low-privileged user gain…
 proxydom/supahunter
Automated reconnaissance and exploitation framework for misconfigured Supabase instances. Features schema enumeration, Selenium-based key extraction,…
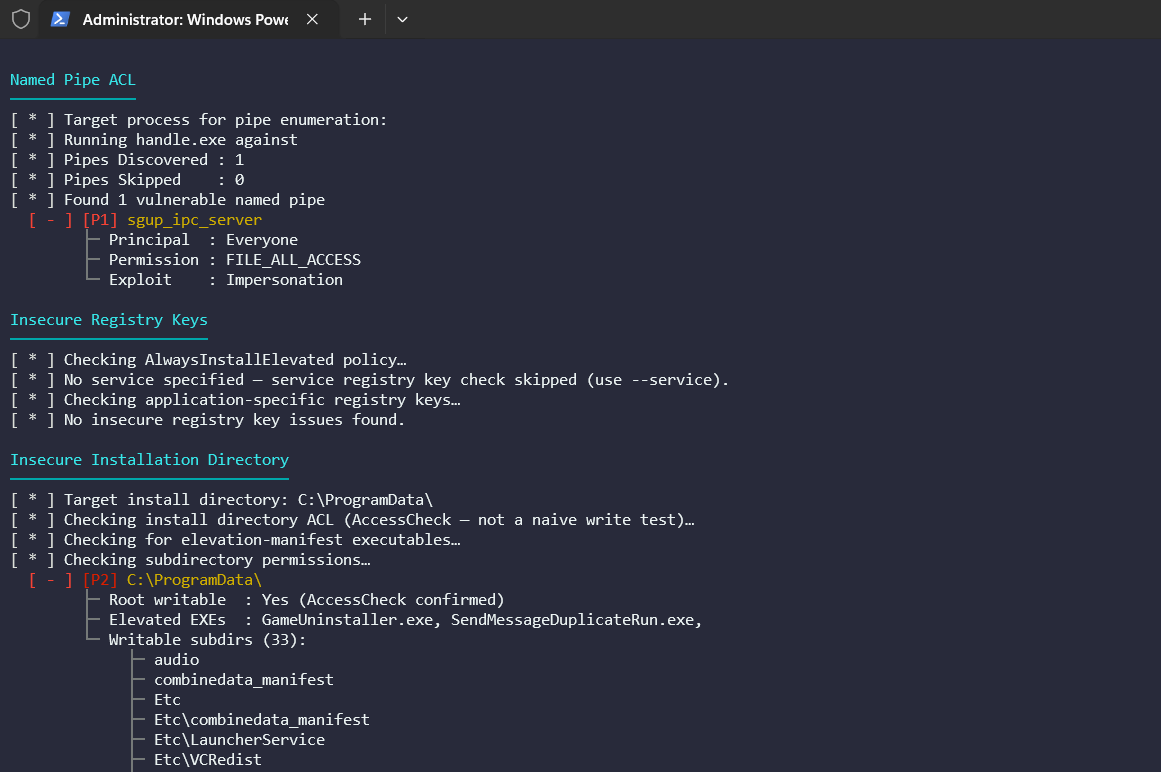 shellkraft/anvil
Anvil is a runtime-first attack surface assessment tool for Windows thick client applications, built for penetration testers and security researchers…