CVE-2024-31317-PoC-Deployer

Automated deployment tool for CVE-2024-31317 PoC on Android 9-13, enabling privilege escalation via Zygote injection and reverse shell execution.

Automated deployment tool for CVE-2024-31317 PoC on Android 9-13, enabling privilege escalation via Zygote injection and reverse shell execution.

Check UNIX/Linux systems for privilege escalation

Nerv0us r4bbit - Post Exploitation Windows Enumeration Tool

CVE-2026-33017 exploitation tool for Langflow <1.9.0. Features reverse shells, command execution, file operations, persistence, and automated…

Automated reconnaissance and exploitation framework for misconfigured Supabase instances. Features schema enumeration, Selenium-based key extraction,…

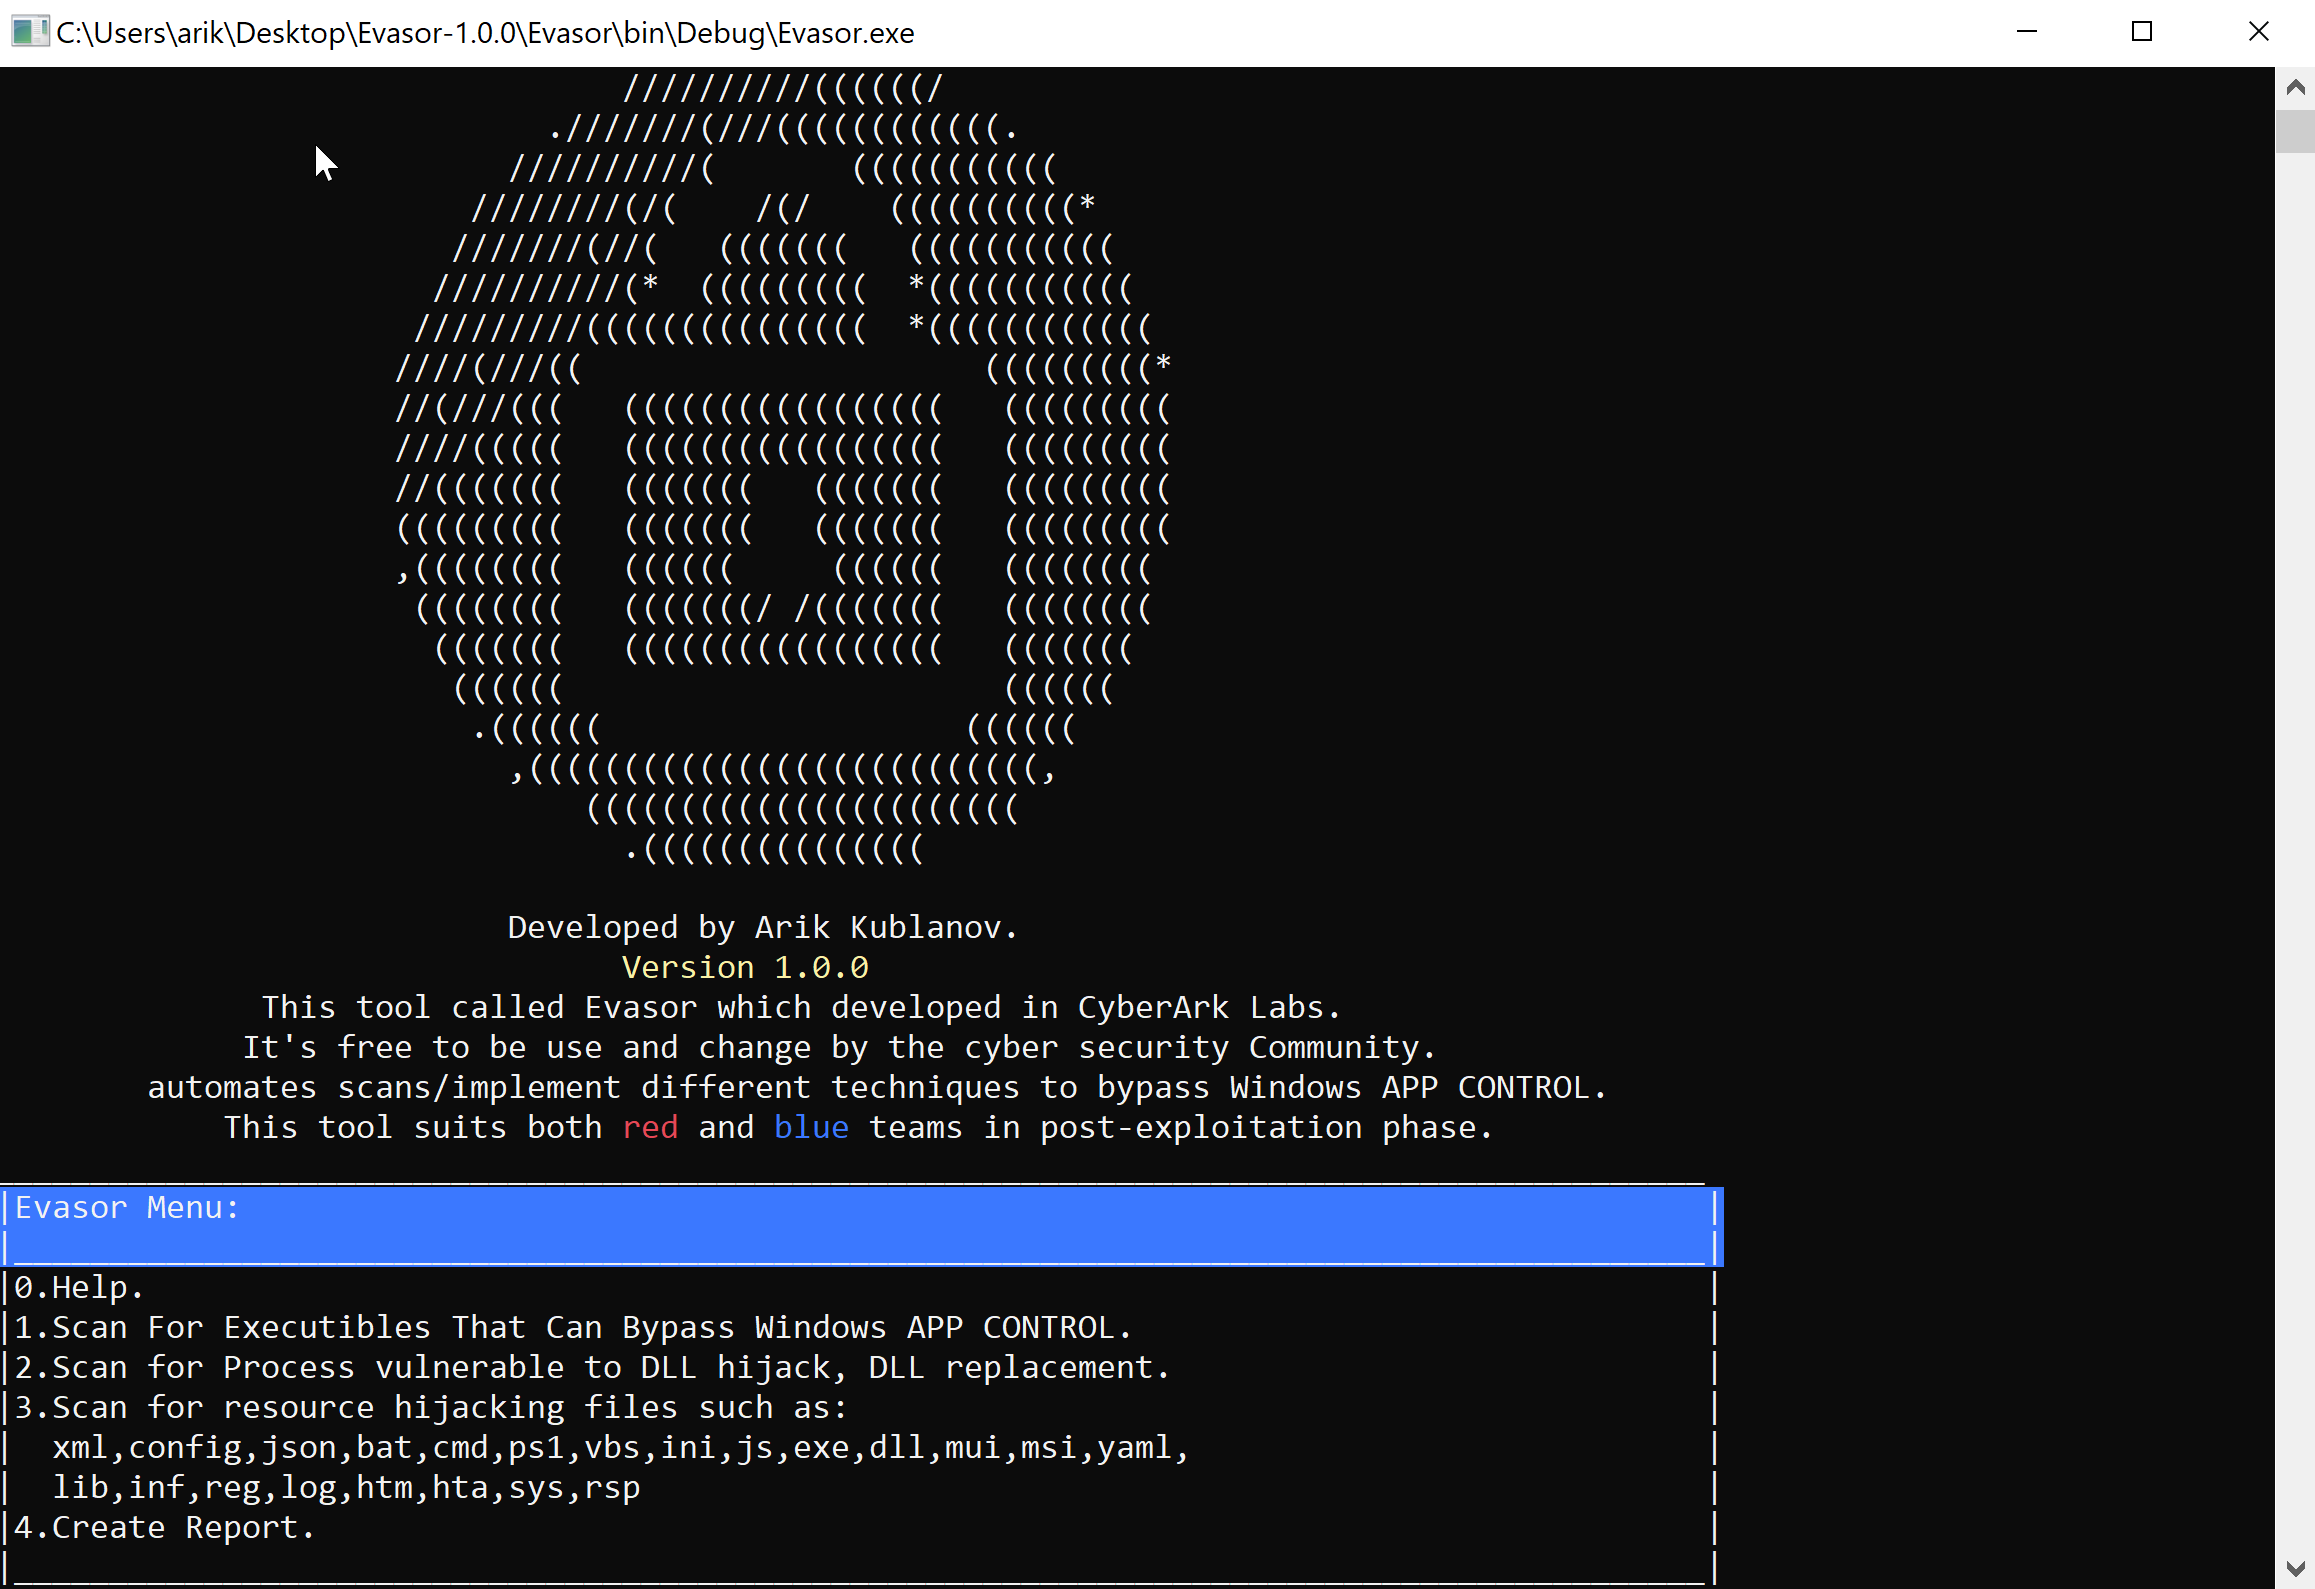
A tool to be used in post exploitation phase for blue and red teams to bypass APPLICATIONCONTROL policies

Automated local privilege escalation exploit for CVE-2024-48990 (needrestart v3.7), leveraging PYTHONPATH hijacking to gain root access.

Automated Tool That Generates The Perfect Meterpreter Powershell Payload

Python PoC validating CVE-2025-6325 unauthenticated privilege escalation and CVE-2025-6327 arbitrary file upload RCE in King Addons for Elementor <=…

Exploit script for CVE-2020-1472 (ZeroLogon) with automated privilege escalation, credential dumping via secretsdump, and lateral movement using…

Automated exploit script combining CVE-2020-1472 (ZeroLogon) with evil-winrm to gain a remote shell on vulnerable Windows Domain Controllers.

Automated Bash script to patch CVE-2023-22809 by installing the latest sudo version, mitigating a local privilege-escalation vulnerability on Linux…

Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…