

CVE-2022-0435-Poc
 spydomain/cve-2022-0435-poc
Stack overflow exploit for CVE-2022-0435 in the TIPC module, providing local privilege escalation to root on Ubuntu kernels.
binary-exploitationexploitationmemory-forensics+2
1
spydomain/cve-2022-0435-pocStack overflow exploit for CVE-2022-0435 in the TIPC module, providing local privilege escalation to root on Ubuntu kernels.
 topjohnwu/magisk
Android customization suite providing root access (MagiskSU), systemless module installation, boot image unpacking/repacking, and Zygisk runtime code…
 nurupo/rootkit
Linux kernel module that grants root privileges, hides processes/files, and protects itself from unloading, designed for educational purposes on…
 blacksnufkin/novaldr
Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)
 mgeeky/azurert
AzureRT - A Powershell module implementing various Azure Red Team tactics
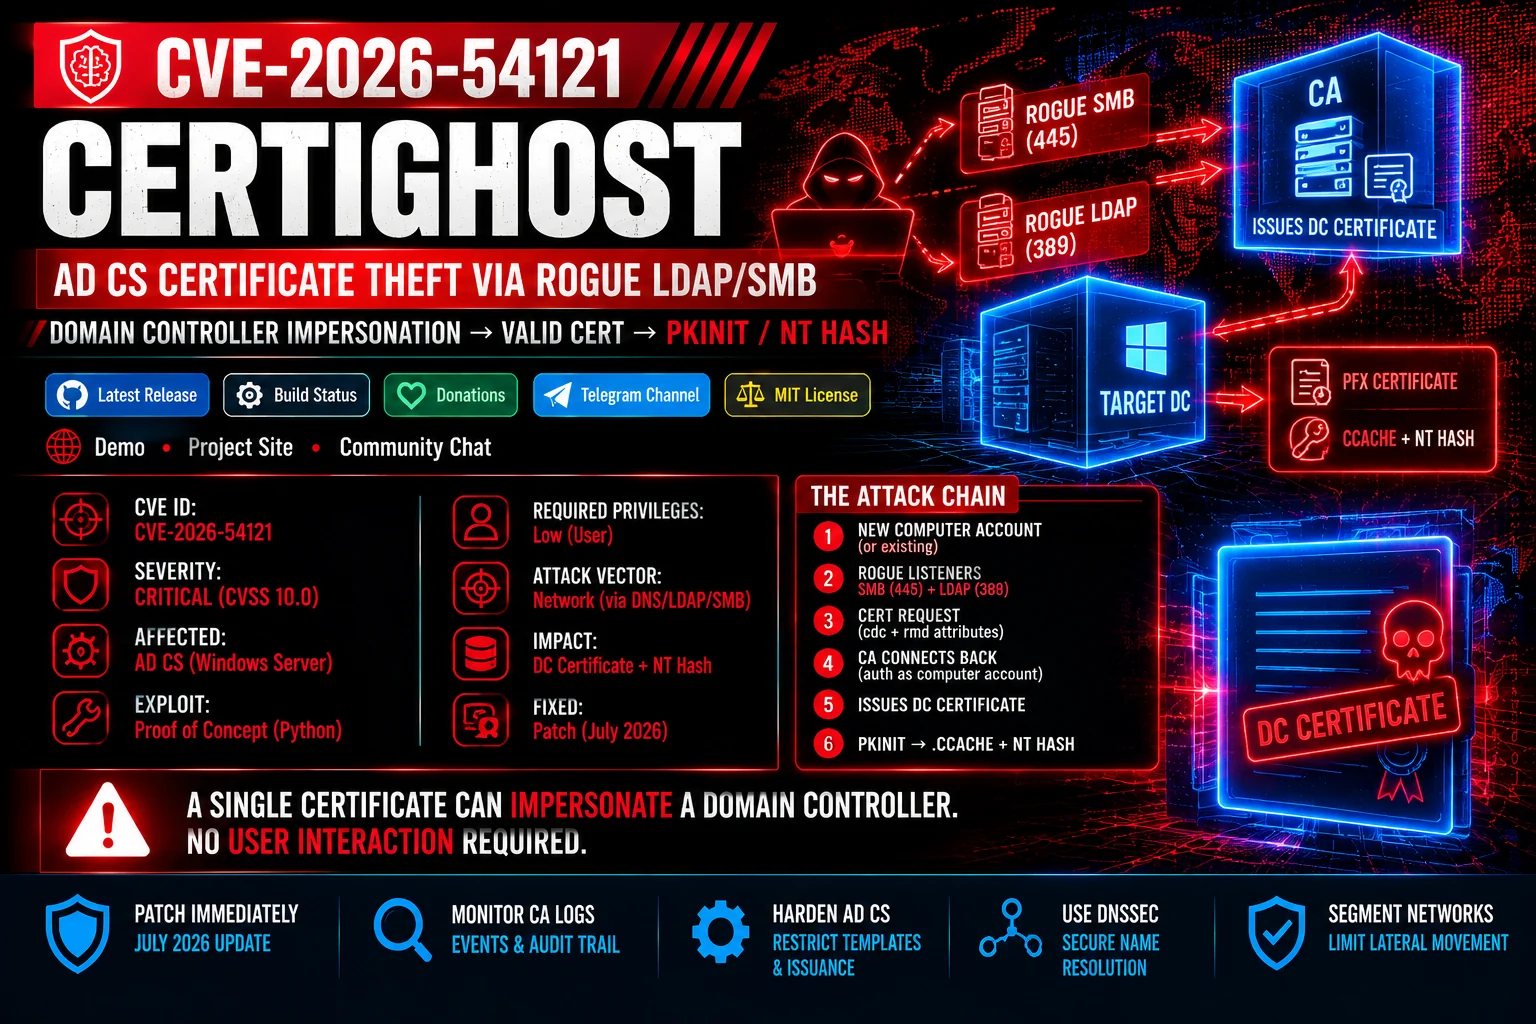 zerodayevil/cve-2026-54121-certighost
Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…
 mhaskar/fsquirtcplpoc
PoC for generating bthprops.cpl module designed to be loaded by Fsquirt.exe LOLBin
 hyd3sec/azur3alph4
PowerShell module for post-breach Azure red teaming, automating token extraction, resource enumeration, and lateral movement within managed identity…
 kungfulon/nf-tables-lpe
Linux kernel privilege escalation exploits targeting Netfilter's nf_table module, developed by Team Orca for multiple CVEs.
 yakidango-official/ghostlock-h80gt
Honor 80 GT privilege escalation PoC: GhostLock (CVE-2026-43499) + custom KernelSU module loading
 danaepp/pwncat_pwnkit
pwncat module that automatically exploits CVE-2021-4034 (pwnkit)
 syntaxmethod/cve-2026-42978-poc-research
CVE-2026-42978 Windows Push Notifications (WpnService) Use-After-Free & Race Condition PoC research, diagnostic scanner, and security audit module…
 strozfriedberg/badsamba
This module is used to exploit startup script execution through Windows Group Policy settings when configured to run off of a remote SMB share.
 kaandemir993/advanced-loader-reverse-engineering
"In-depth reverse engineering analysis of an advanced multi-phase loader targeting Shellhost.exe, amsi.dll, mstscax.dll, and clbcatq.dll using module…
 k8gege/cve-2021-1675
Exploit for CVE-2021-1675 (PrintNightmare) enabling local and remote SYSTEM-level privilege escalation on Windows via the Print Spooler service.…
 jeboo/bypasslkm
Using CVE-2013-6282 to bypass Samsung kernel module authentication
 ochebotar/copy-fail-cve-2026-31431-detection-probe
Safe detection tooling for CVE-2026-31431 "Copy Fail" and CVE-2026-43284 "Dirty Frag" — a local privilege escalation in the Linux kernel's algif_aead…
 depthsecurity/netmri-2014-3418
Metasploit module exploiting InfoBlox Network Automation CVE-2014-3418 command injection to create a sudo user and deliver a reverse Meterpreter…