CVE-2026-65643-PoC-Toolkit

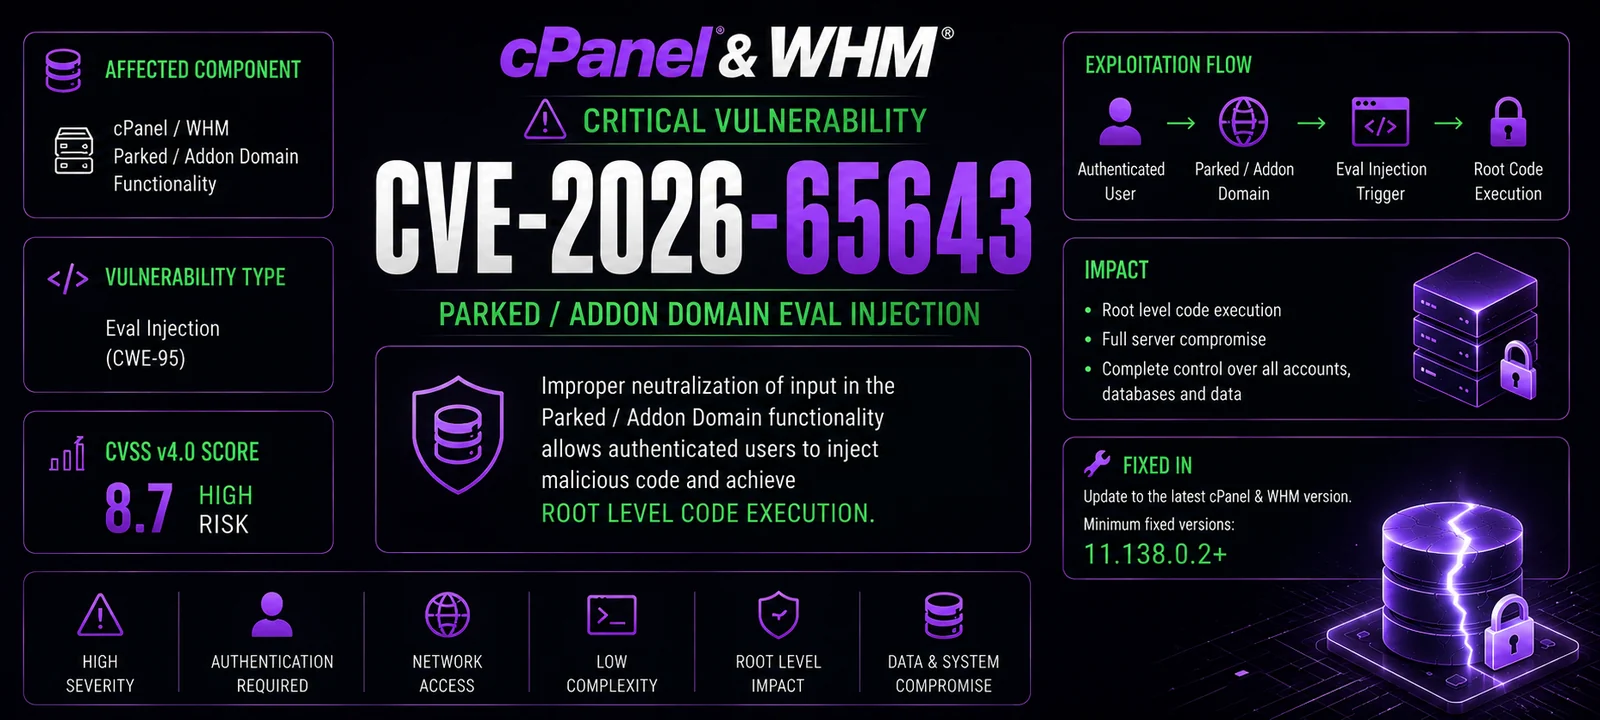
Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…

Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…

Proof of concept exploit for CVE-2026-3775/CVE-2026-3780 and CVE-2026-57239 which lets you obtain NT AUTHORITY\SYSTEM rights via the Foxit PDF Reader…

A PoC exploit for CVE-2022-41622 - a CSRF in F5 BIG-IP control plane that leads to remote root

0ldSQL_MySQL_RCE_exploit.py (ver. 1.0) (CVE-2016-6662) MySQL Remote Root Code Execution / Privesc PoC Exploit For testing purposes only. Do no…

Make CVE-2020-0668 exploit work for version < win10 v1903 and version >= win10 v1903

Exploit codes for rconfig <= 3.9.4

CVE-2021-1675 LPE PoC in Nim (PrintNightmare Local Privilege Escalation)

Authenticated exploit for Moodle 3.9 that escalates teacher privileges to manager role and achieves remote code execution via malicious plugin upload.

A Python-based DirtyPipe (CVE-2022-0847) POC to pop a root shell

C# PrintNightmare (CVE-2021-1675)

Use after free in Windows Common Log File System Driver allows an authorized attacker to elevate privileges locally.

CVE 2025 27237 Zabbix LPE proof of concept.

64-bit Windows kernel privilege escalation exploit for CVE-2016-0040 (WMI Receive Notification vulnerability) using GDI bitmap manipulation for token…

self cleaning CVE-2025-27591 Poc that grants a root reverse shell instead of modifying passwd files

CVE-2024-53691

POC exploit code for CVE-2020-1048(PrintDemon)

Proof-of-concept exploit for CVE-2020-8289 demonstrating remote code execution as SYSTEM/root via Backblaze backup client's SSL verification bypass…

CVE-2024-37032 (Probllama) PoC for Ollama ≤0.1.33: path traversal and arbitrary file write via model digest handling, leading to automated privilege…