

pyCobaltHound
 nvisosecurity/pycobalthound
pyCobaltHound is an Aggressor script extension for Cobalt Strike which aims to provide a deep integration between Cobalt Strike and Bloodhound.
exploit-frameworksinformation-gatheringlateral-movement+5
135
nvisosecurity/pycobalthoundpyCobaltHound is an Aggressor script extension for Cobalt Strike which aims to provide a deep integration between Cobalt Strike and Bloodhound.
 octoberfest7/kdstab
BOF combination of KillDefender and Backstab
 licitrasimone/crystalsliver
Crystal Palace Evasion kit for Sliver
 mstxq17/cve-2021-1675_rdl_lpe
PrintNightMare LPE提权漏洞的CS 反射加载插件。开箱即用、通过内存加载、混淆加载的驱动名称来ByPass Defender/EDR。
 gushmazuko/winbypass
Windows UAC Bypass

 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
 taroballzchen/cve-2022-41040-metasploit-proxynotshell
the metasploit script(POC) about CVE-2022-41040. Microsoft Exchange are vulnerable to a server-side request forgery (SSRF) attack. An authenticated…
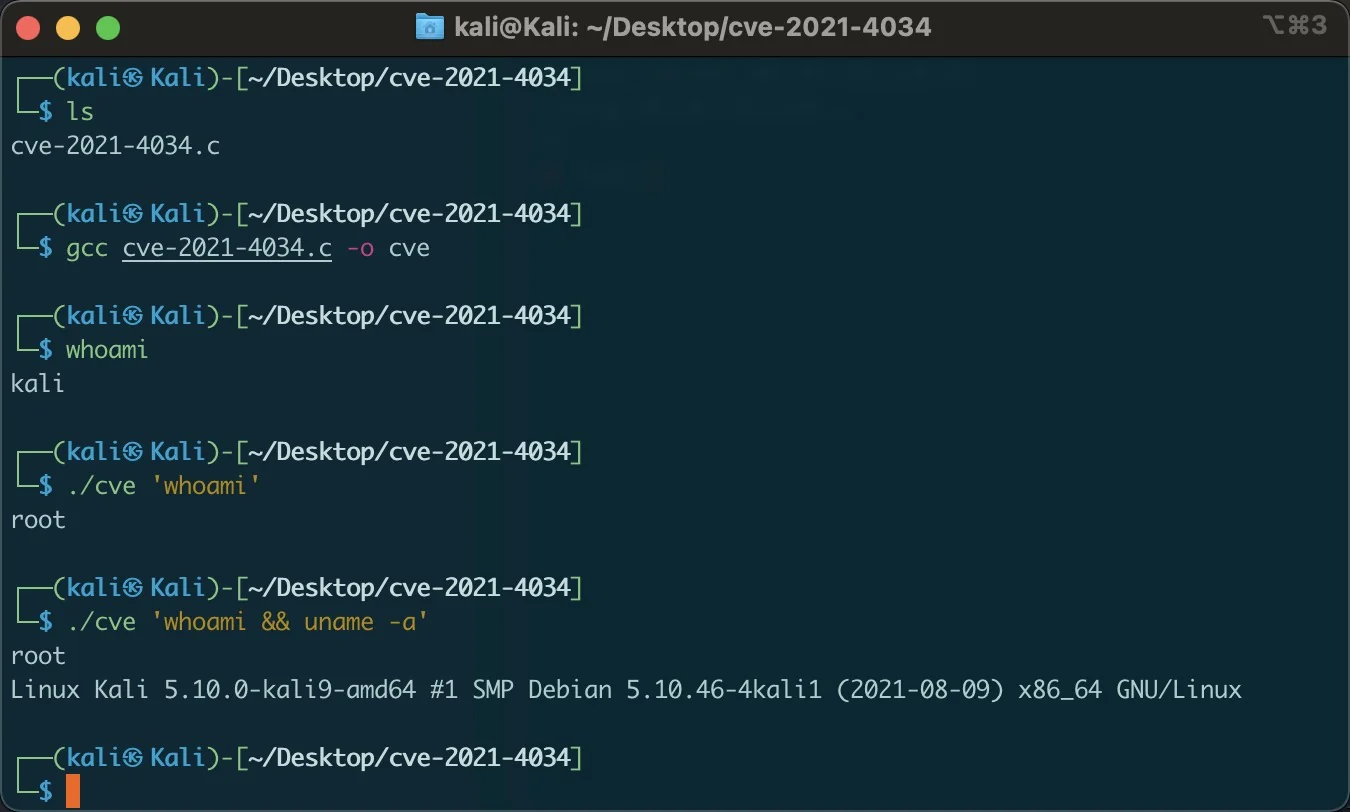 zhzyker/cve-2021-4034
polkit pkexec Local Privilege Vulnerability to Add custom commands

 jgoyd/glass-cage-ios18-cve-2025-24085-cve-2025-24201
Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, bypassing LockDown mode protection by exploiting ImageIO (CVE-2025-43300), then…
 xiao-zhu-zhu/pig_cs4.4
Cobalt Strike 4.4 猪猪版 去暗桩 去流量特征 beacon仿造真实API服务 修补CVE-2022-39197补丁
 h00die/msf-testing-scripts
Metasploit modules in testing
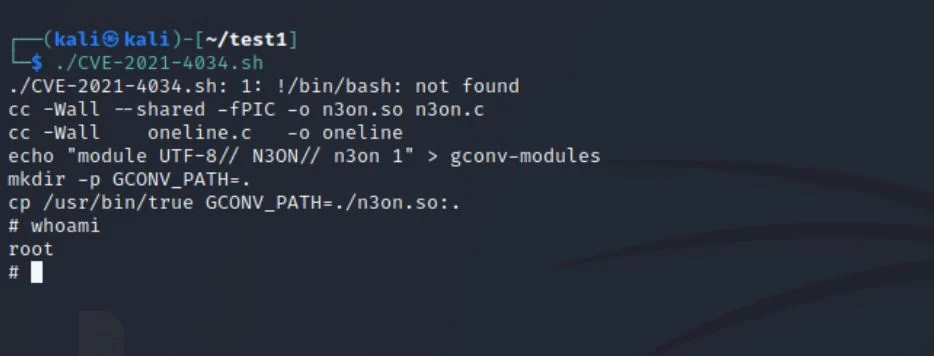 neonwhiterabbit/cve-2021-4034
Bash script exploiting CVE-2021-4034 (Pwnkit) for local privilege escalation on vulnerable Linux systems. Copy-paste execution for quick testing.
 esskumar/phantomevasion
Python-based antivirus evasion tool generating undetectable executables from msfvenom payloads with advanced techniques like junkcode injection,…
 nafiez/metasploit-cve-2026-54121-certighost
A Metasploit auxiliary module that escalates from any low-privileged domain user to full domain compromise by abusing the AD CS enrollment "chase"…
 depthsecurity/netmri-2014-3418
Metasploit module exploiting InfoBlox Network Automation CVE-2014-3418 command injection to create a sudo user and deliver a reverse Meterpreter…
 waterrr/nopac
Exploiting CVE-2021-42278 and CVE-2021-42287