
CVE-2021-4034
 joeammond/cve-2021-4034
Python exploit for CVE-2021-4034 (PwnKit) that escalates privileges to root via pkexec, generating a root shell with msfvenom payloads.
binary-exploitationexploitationpayload-generation+2
180
joeammond/cve-2021-4034Python exploit for CVE-2021-4034 (PwnKit) that escalates privileges to root via pkexec, generating a root shell with msfvenom payloads.
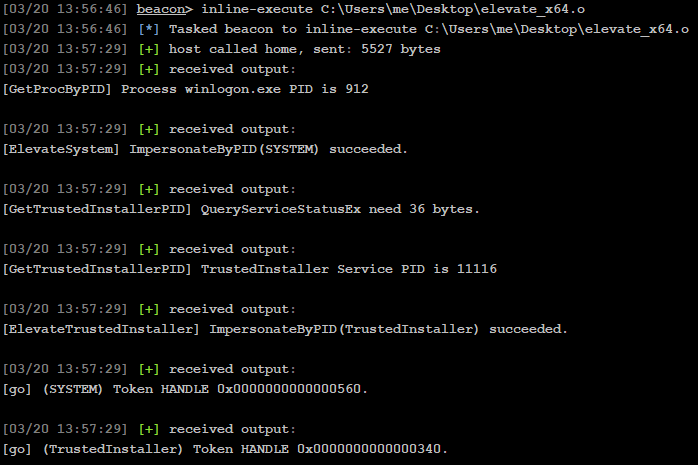 mr-un1k0d3r/elevate-system-trusted-bof
Cobalt Strike Beacon Object File that elevates an active beacon to SYSTEM and grants TrustedInstaller privileges through SetThreadToken token…
 ustayready/wnfexec
WNF Code Execution Library Using C#
 octoberfest7/eventvieweruac_bof
Beacon Object File implementation of Event Viewer deserialization UAC bypass

 je5442804/wptaskscheduler_cve-2024-49039
WPTaskScheduler RPC Persistence & CVE-2024-49039 via Task Scheduler
 rek7/postshell
PostShell - Post Exploitation Bind/Backconnect Shell
 cbwang505/cve-2020-1066-exp
Local privilege escalation exploit for CVE-2020-1066 targeting Windows 7 and Server 2008 R2. Leverages arbitrary file replacement via Windows…
 csenox/semanagevolumeexploit
Windows local privilege escalation exploit abusing SeManageVolumePrivilege to grant full C:\ drive access and gain a SYSTEM shell via PrintConfig.dll…
 checkpointsw/vectoredoverloading
Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…
 blacksnufkin/rusty-playground
Some Rust program I wrote while learning Malware Development
 exodusintel/cve-2019-0808
Win32k Exploit by Grant Willcox
 0xeb-bp/cve-2020-1054
Rust implementation of a Windows 7 x64 local privilege escalation exploit for CVE-2020-1054; compiles via Cargo and executes to elevate privileges.
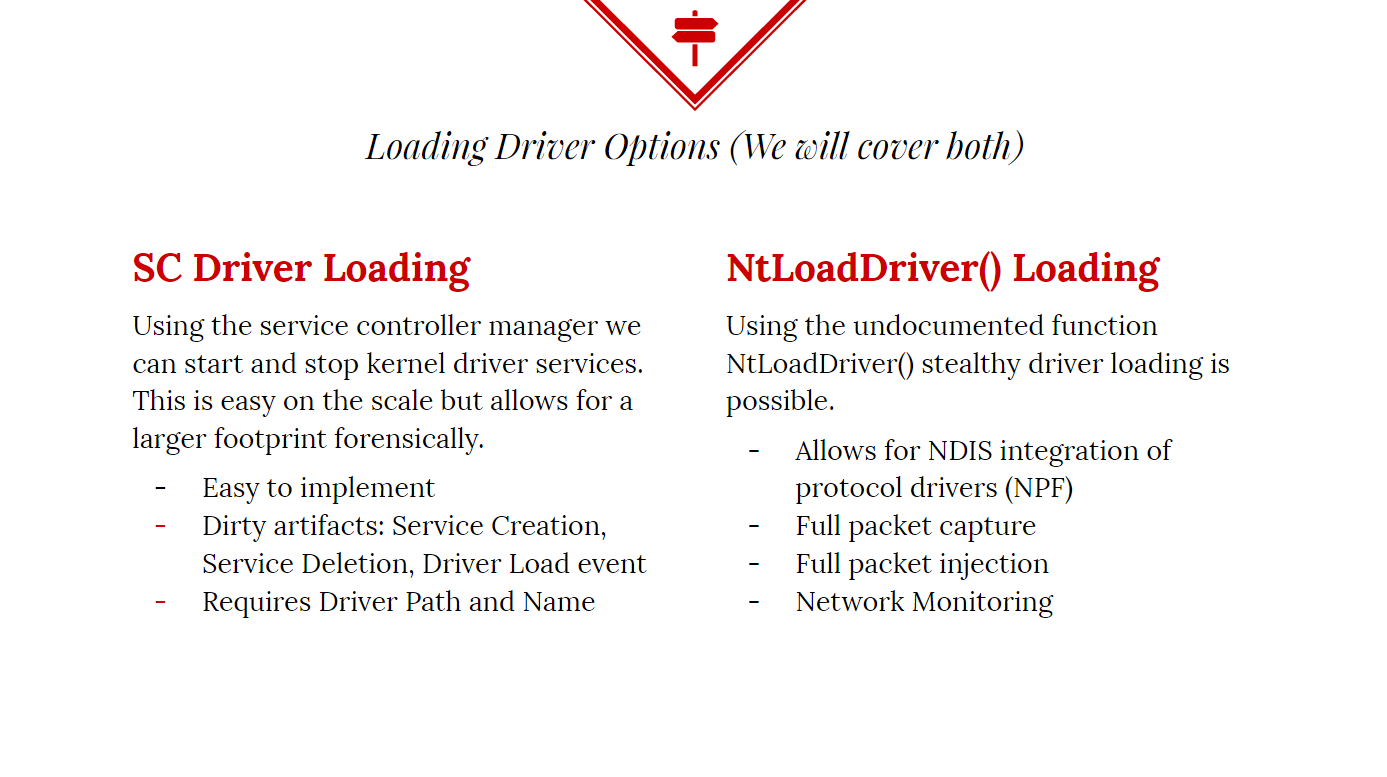 killswitch-gui/hotload-driver
C++
 forrest-orr/exploits
A personal collection of Windows CVE I have turned in to exploit source, as well as a collection of payloads I've written to be used in conjunction…
 fsecurelabs/cve-2016-7255
An exploit for CVE-2016-7255 on Windows 7/8/8.1/10(pre-anniversary) 64 bit
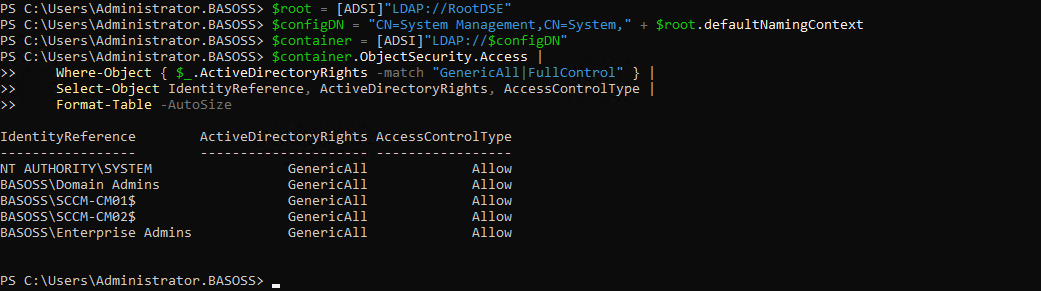 omribaso/sccm-cve-2026-47301-remote-code-execution-exploit
Proof-of-concept exploit chain (CVE-2026-47301) for Microsoft Configuration Manager (SCCM), combining a broken access, CAB arbitrary-write path…
 forrest-orr/doublestar
A personalized/enhanced re-creation of the Darkhotel "Double Star" APT exploit chain with a focus on Windows 8.1 and mixed with some of my own…