
RPC-Backdoor
 eladshamir/rpc-backdoor
A basic emulation of an "RPC Backdoor"
command-and-controllateral-movementpost-exploitation+3
2414 years ago
eladshamir/rpc-backdoorA basic emulation of an "RPC Backdoor"
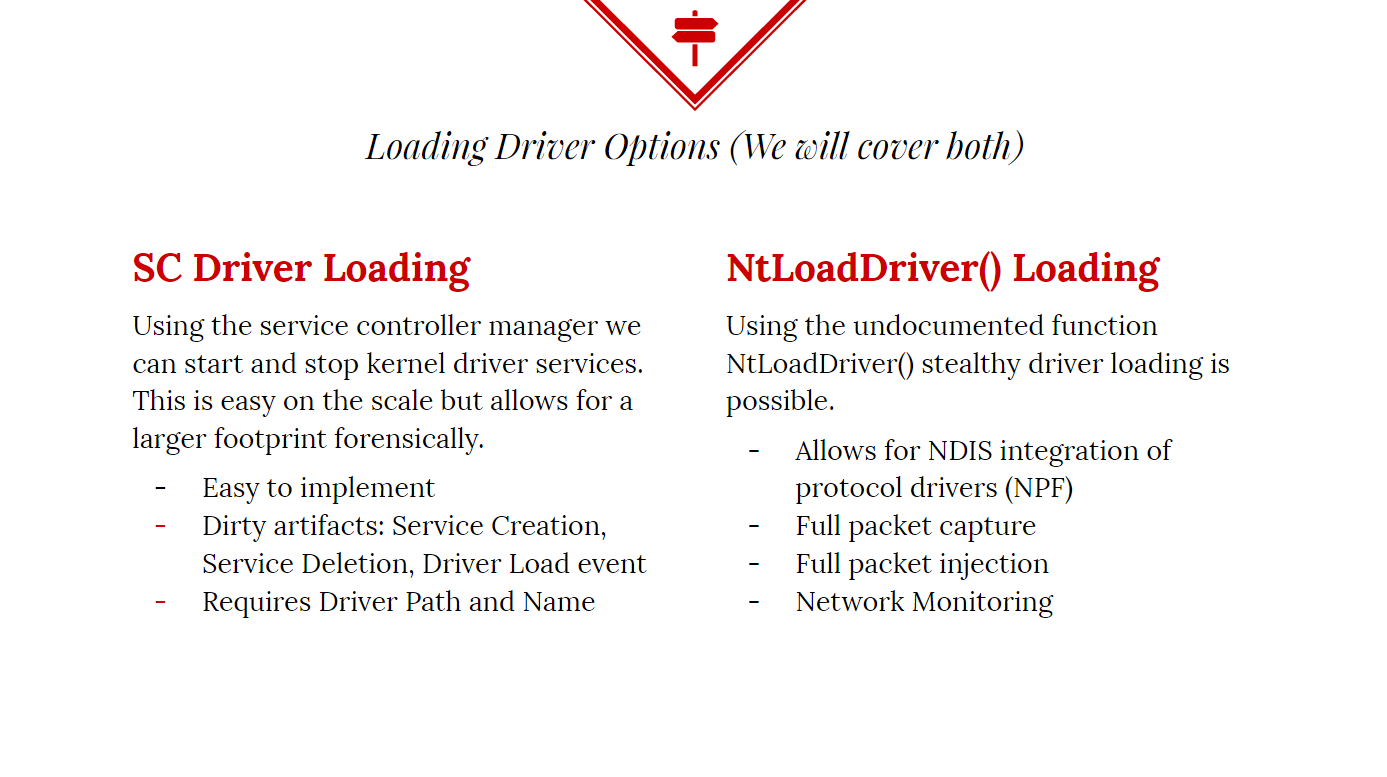 killswitch-gui/hotload-driver
C++
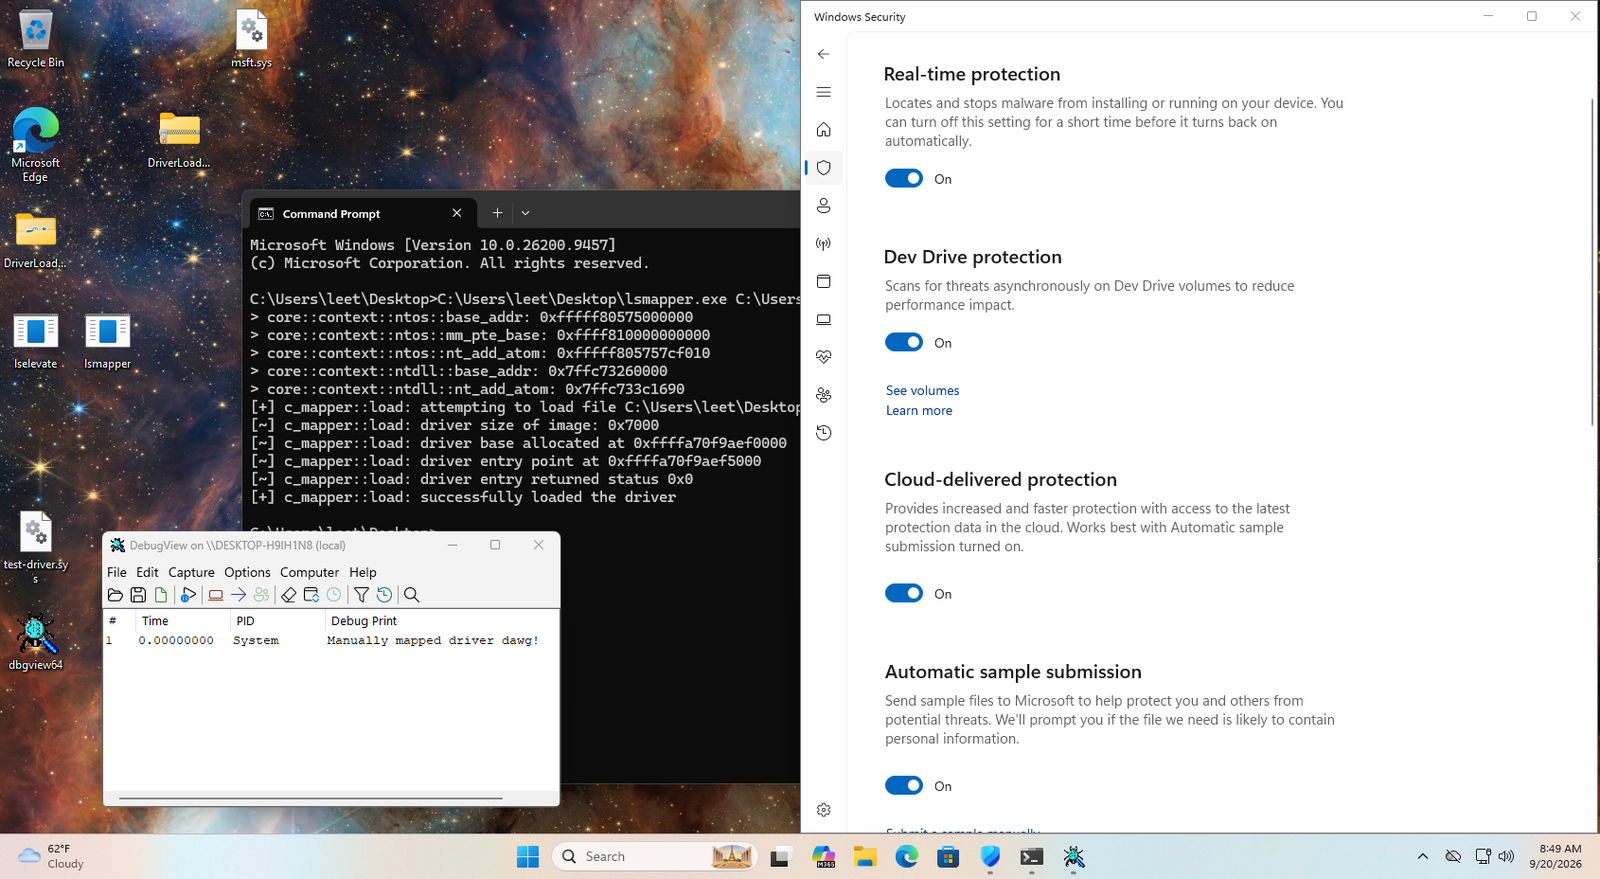 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
 synacktiv/windows_kernel_shadow_stack
Proof of concepts demonstrating some aspects of the Windows kernel shadow stack mitigation.
 buter-chkalova/project-rvbbit
Educational Linux kernel rootkit PoC exploring DKOM, syscall hooking, stealth, observability and defensive detection
 cisc0-gif/kitt
Python-Based Pentesting Framework
 the-snek-initiative/snek_equinox
Repository hosting a hypothetical EDR Spoofer, as discovered originally by Nightmare-Eclipse
 melardev/xeytanwin32-rat
WORK IN PROGRESS. RAT written in C++ using Win32 API
 kpwn/ps4-5.05-kernel-exploit
A fully implemented kernel exploit for the PS4 on 5.05FW
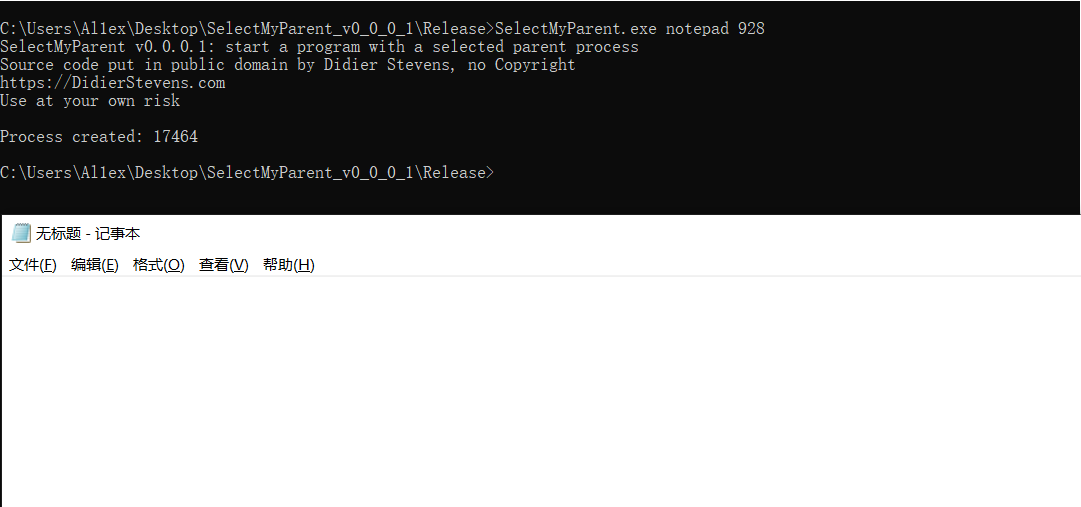 al1ex/selectmyparent
PPID Spoofing
 eonrickity/cve-2017-0213
Fixed No Virus Manual Automatic Loader exe no zip because zip picks up the anti virus detector.
 kurtulusakyuz/ionstack_s21
Exploit chain research targeting CVE-2026-43499 on Samsung Galaxy S21
 de7ec7ed/cve-2016-0040
64-bit Windows kernel privilege escalation exploit for CVE-2016-0040 (WMI Receive Notification vulnerability) using GDI bitmap manipulation for token…
 amrhuss/throttlestop-exploit-rw
Arbitrary physical memory read/write exploitation using ThrottleStop.sys (CVE-2025-7771) with superfetch address translation - Windows kernel…
 d4rkks/cve-2025-7771-vulnerability-exploration
Escalating privilege in the system from unsigned driver using throttlestop vulnerability
 cplusplus17/deco-filepush-disclosure
Disclosure and PoC for a root file read/write flaw in the TP-Link Deco XE75 Pro V3 debug channel (tmpsvr opcodes 0xC456/0xF0), with CVSS analysis and…
 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
 gagaltotal/cve-2026-68376-ubuntu-7.0.0-30-poc
Proof-of-concept exploit for CVE-2026-68376 in Ubuntu kernel 7.0.0-30, leveraging SCTP chunk handling and PTE manipulation to escalate privileges to…