
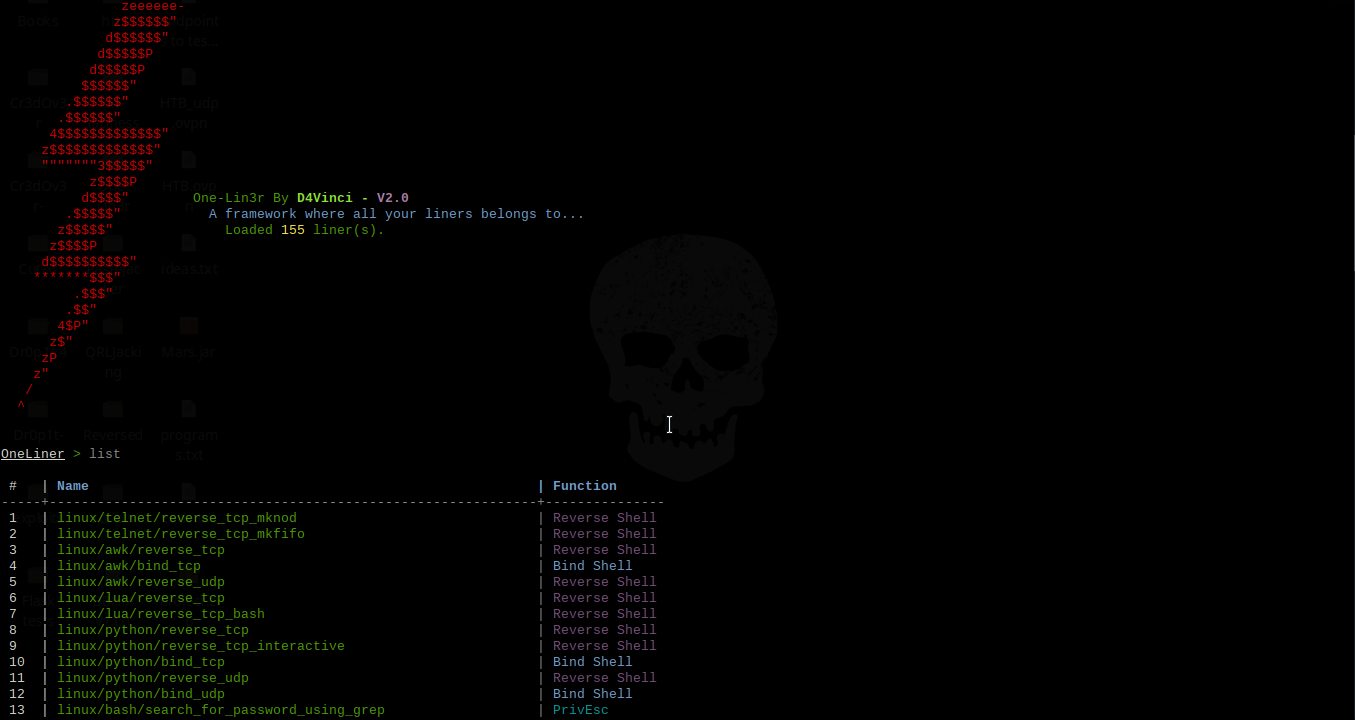
One-Lin3r
 d4vinci/one-lin3r
Gives you one-liners that aids in penetration testing operations, privilege escalation and more
exploitationinformation-gatheringpayload-generation+4
1.8k10 months ago
d4vinci/one-lin3rGives you one-liners that aids in penetration testing operations, privilege escalation and more
 cr4sh/smmbackdoor
First open source and publicly available System Management Mode backdoor for UEFI based platforms. Good as general purpose playground for various SMM…
 mgeeky/stracciatella
OpSec-safe Powershell runspace from within C# (aka SharpPick) with AMSI, Constrained Language Mode and Script Block Logging disabled at startup
 justicerage/ffm
Freedom Fighting Mode: open source hacking harness
 skiller9090/lucifer
A Powerful Penetration Tool For Automating Penetration Tasks Such As Local Privilege Escalation, Enumeration, Exfiltration and More... Use Or Build…
 xaitax/totalrecall
This tool extracts and displays data from the Recall feature in Windows 11, providing an easy way to access information about your PC's activity…
 octoberfest7/enumprotections_bof
A BOF to enumerate system process, their protection levels, and more.
 nickguitar/yaps
Yet Another PHP Shell - The most complete PHP reverse shell
 aeroot/wp-gdpr-compliance-plugin-exploit
Exploit of the privilege escalation vulnerability of the WordPress plugin "WP GDPR Compliance" by "Van Ons"…
 thejoyofhacking/berdav-cve-2021-4034
Exploit for CVE-2021-4034 (PwnKit) that provides a root shell via polkit pkexec. Includes a dry-run mode to test vulnerability and a one-liner script…
 4n4s4zi/copyfail-alpine
More portable PoC of copyfail LPE (CVE-2026-31431) that works on Alpine Linux
 dr4xp/pwnkit-helper
For CTF's and Safe Environments.... CVE-2021-4034 Local PrivEsc.
 h3xduck/umbra
A LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.
 hoangkien1020/cve-2020-14321
Course enrolments allowed privilege escalation from teacher role into manager role to RCE
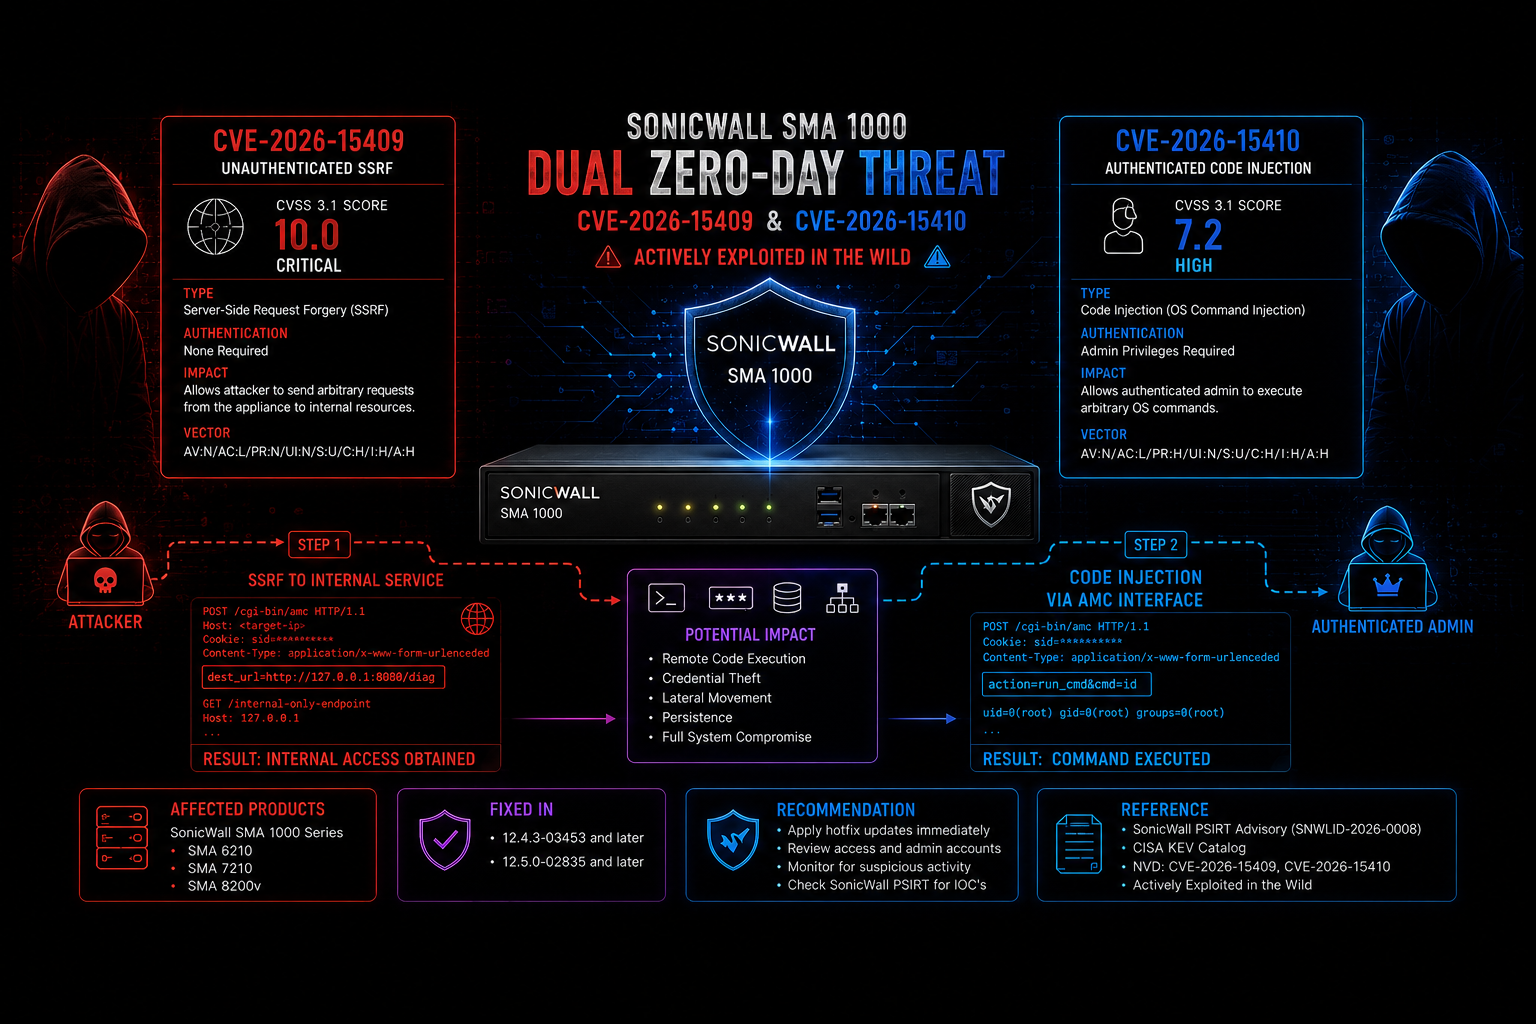 tc4dy/cve-2026-15409-15410-framework
Multi-exploit framework for SonicWall SMA1000 chaining SSRF (CVE-2026-15409) to Erlang RCE and root privilege escalation (CVE-2026-15410). Features…
 sangsenimanwartefak/cve-2026-80467
Python detection tool that fingerprints ACF Extended forms on WordPress and checks for publicly exposed role fields indicating CVE-2026-80467…
 albocoder/cve-2022-27666-exploits
There are 2 exploitation methods that exploit CVE-2022-27666. For more info on how to use these code bases please check my blog.
 sakilahamed/linux-kernel-exploit-lab
More specific : Dirty COW (CVE-2016-5195)